Secure Multi-Tenant AI Agent on Microsoft Agent Framework
تفاصيل العمل
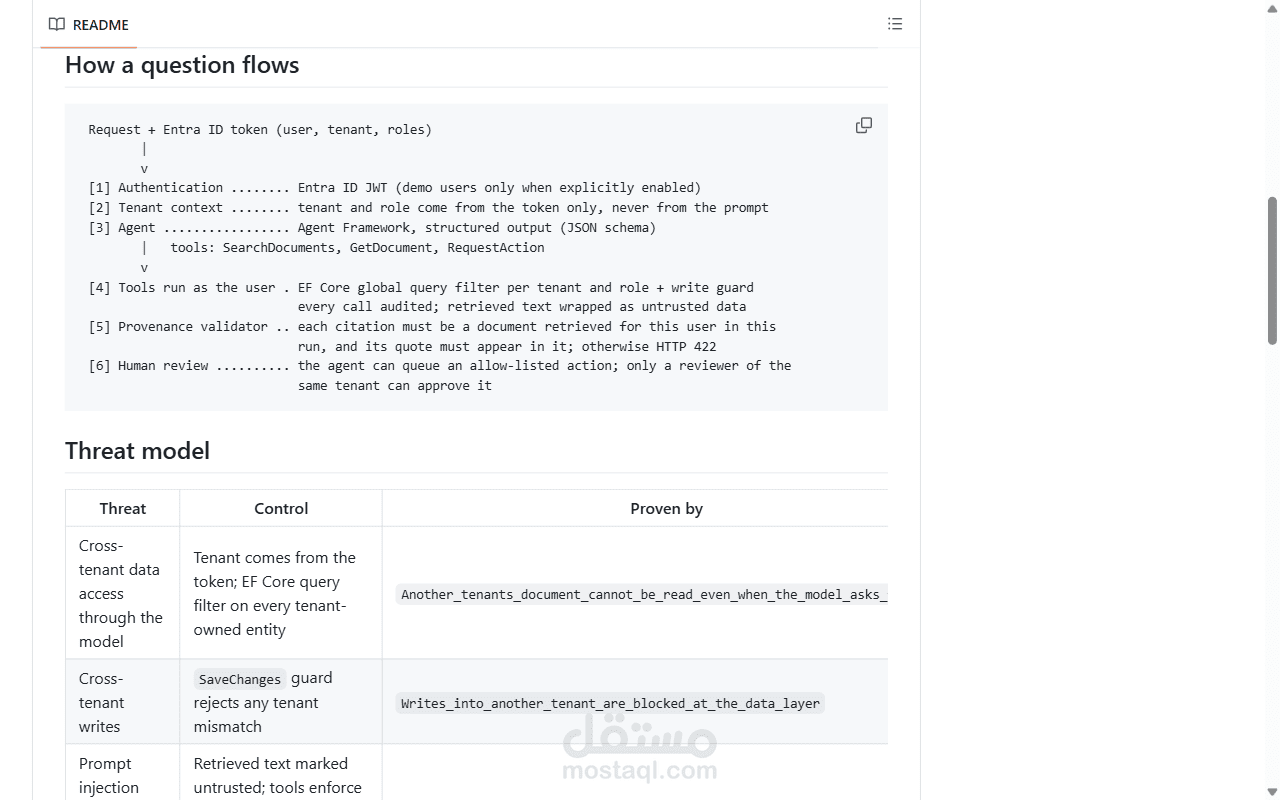
An open-source reference showing how to add an AI agent to a multi-tenant SaaS application without trusting the model.
- Microsoft Agent Framework with Azure OpenAI, signed in through managed identity (no secrets in code)
- Tools run as the signed-in user; EF Core filters isolate every tenant and a write guard blocks cross-tenant changes
- Provenance validation: answers must cite documents retrieved for that user, or they are rejected
- Human-review queue: the agent can only propose actions; a reviewer of the same tenant approves them
- Entra ID authentication, per-user rate limiting and OpenTelemetry tracing
- Security tests that script a malicious model (prompt injection, cross-tenant reads, fabricated quotes) and prove the system still holds