BladeRecon – Python-Based Reconnaissance & Attack Surface
تفاصيل العمل
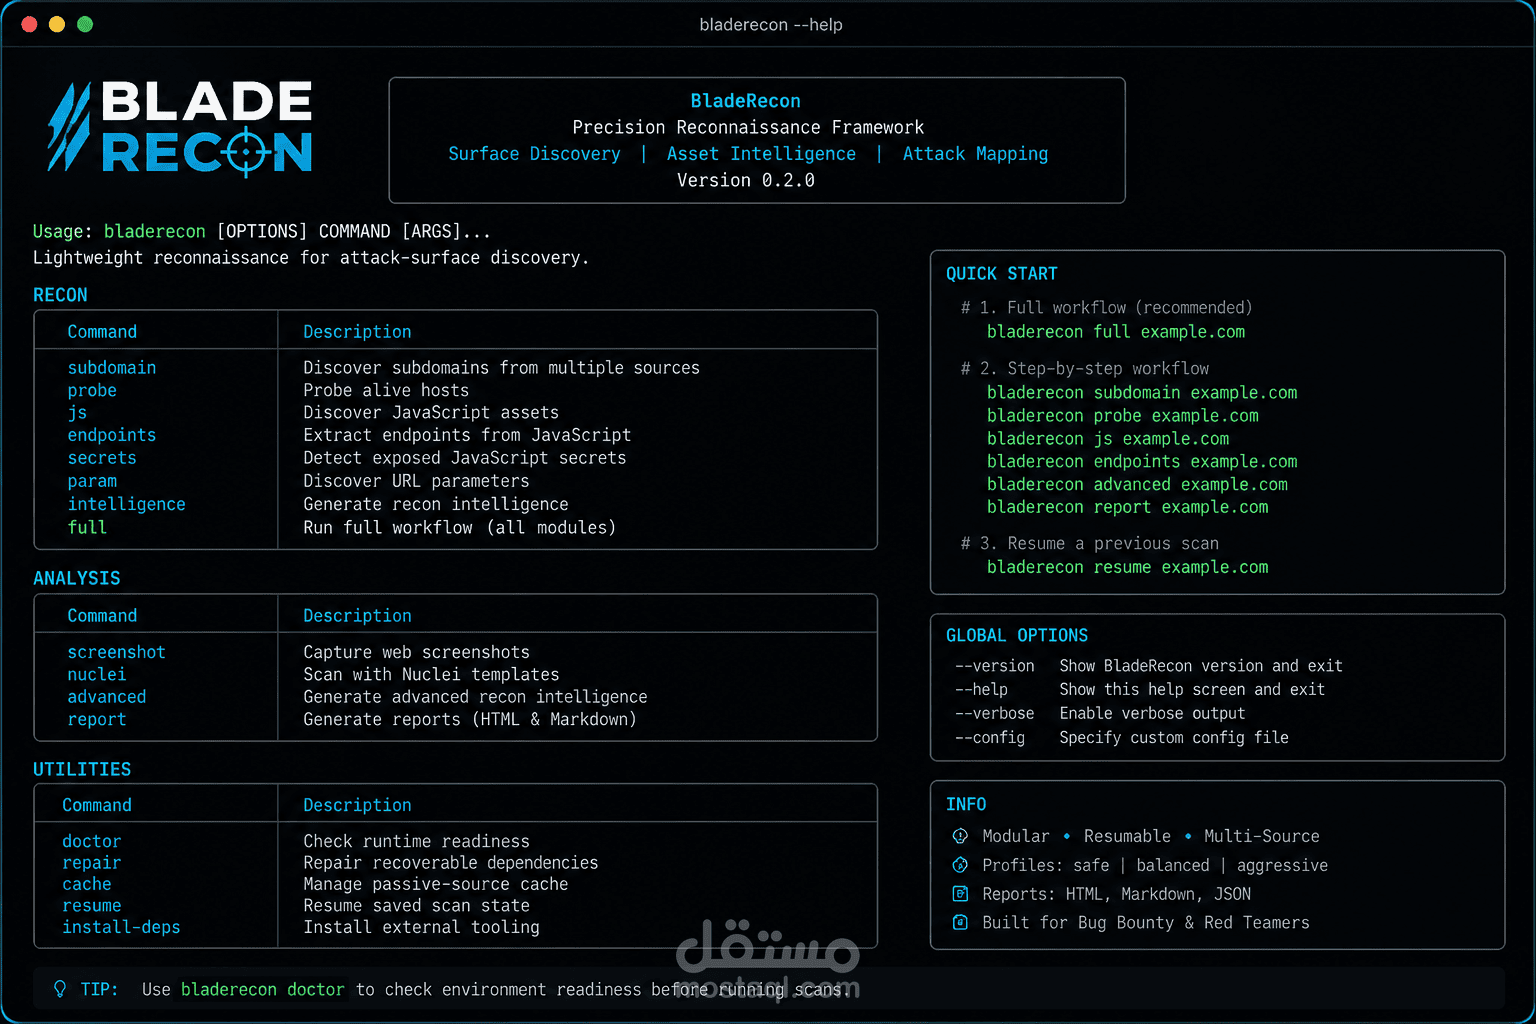
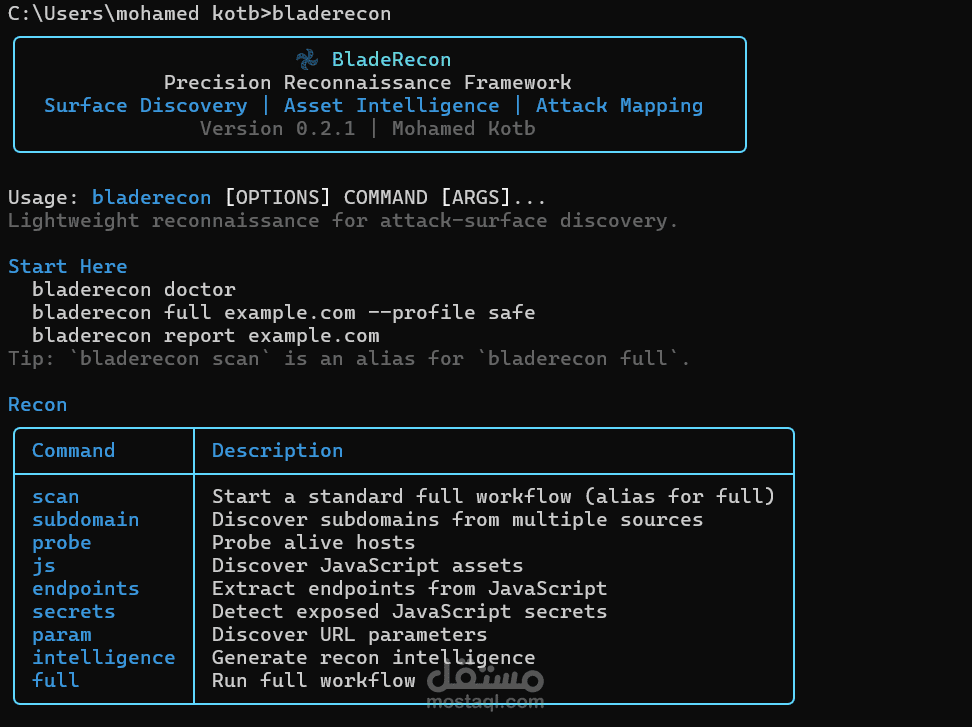
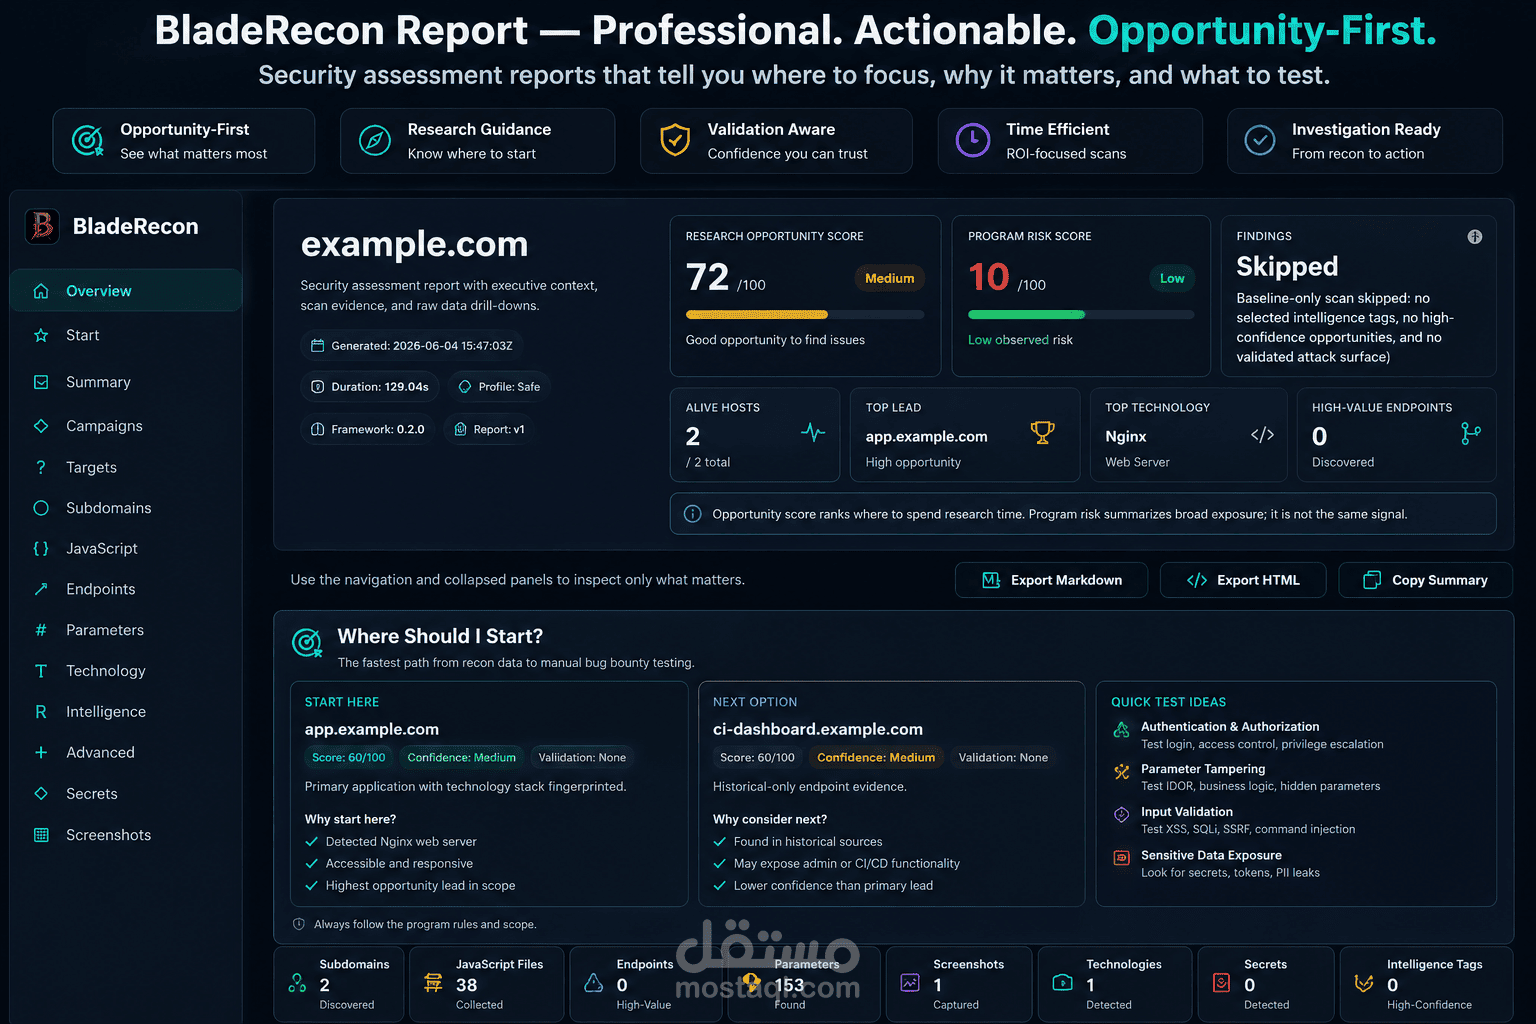
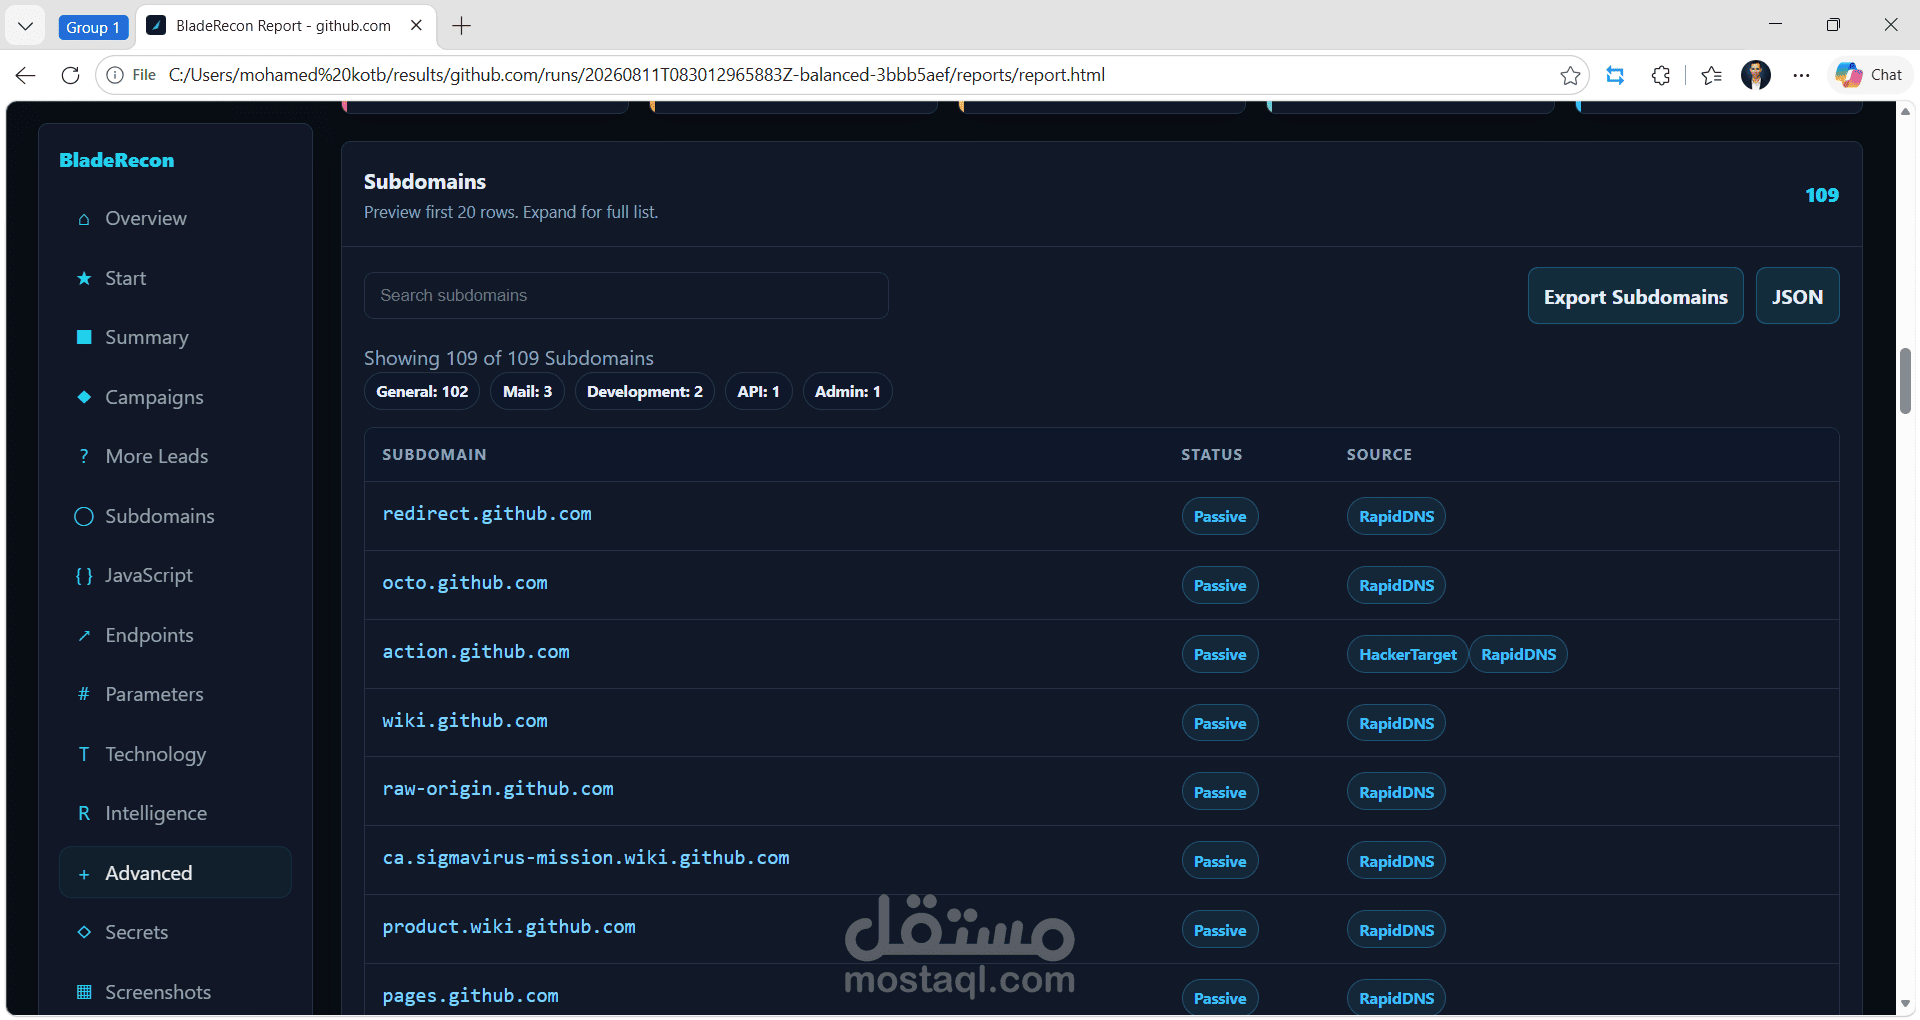
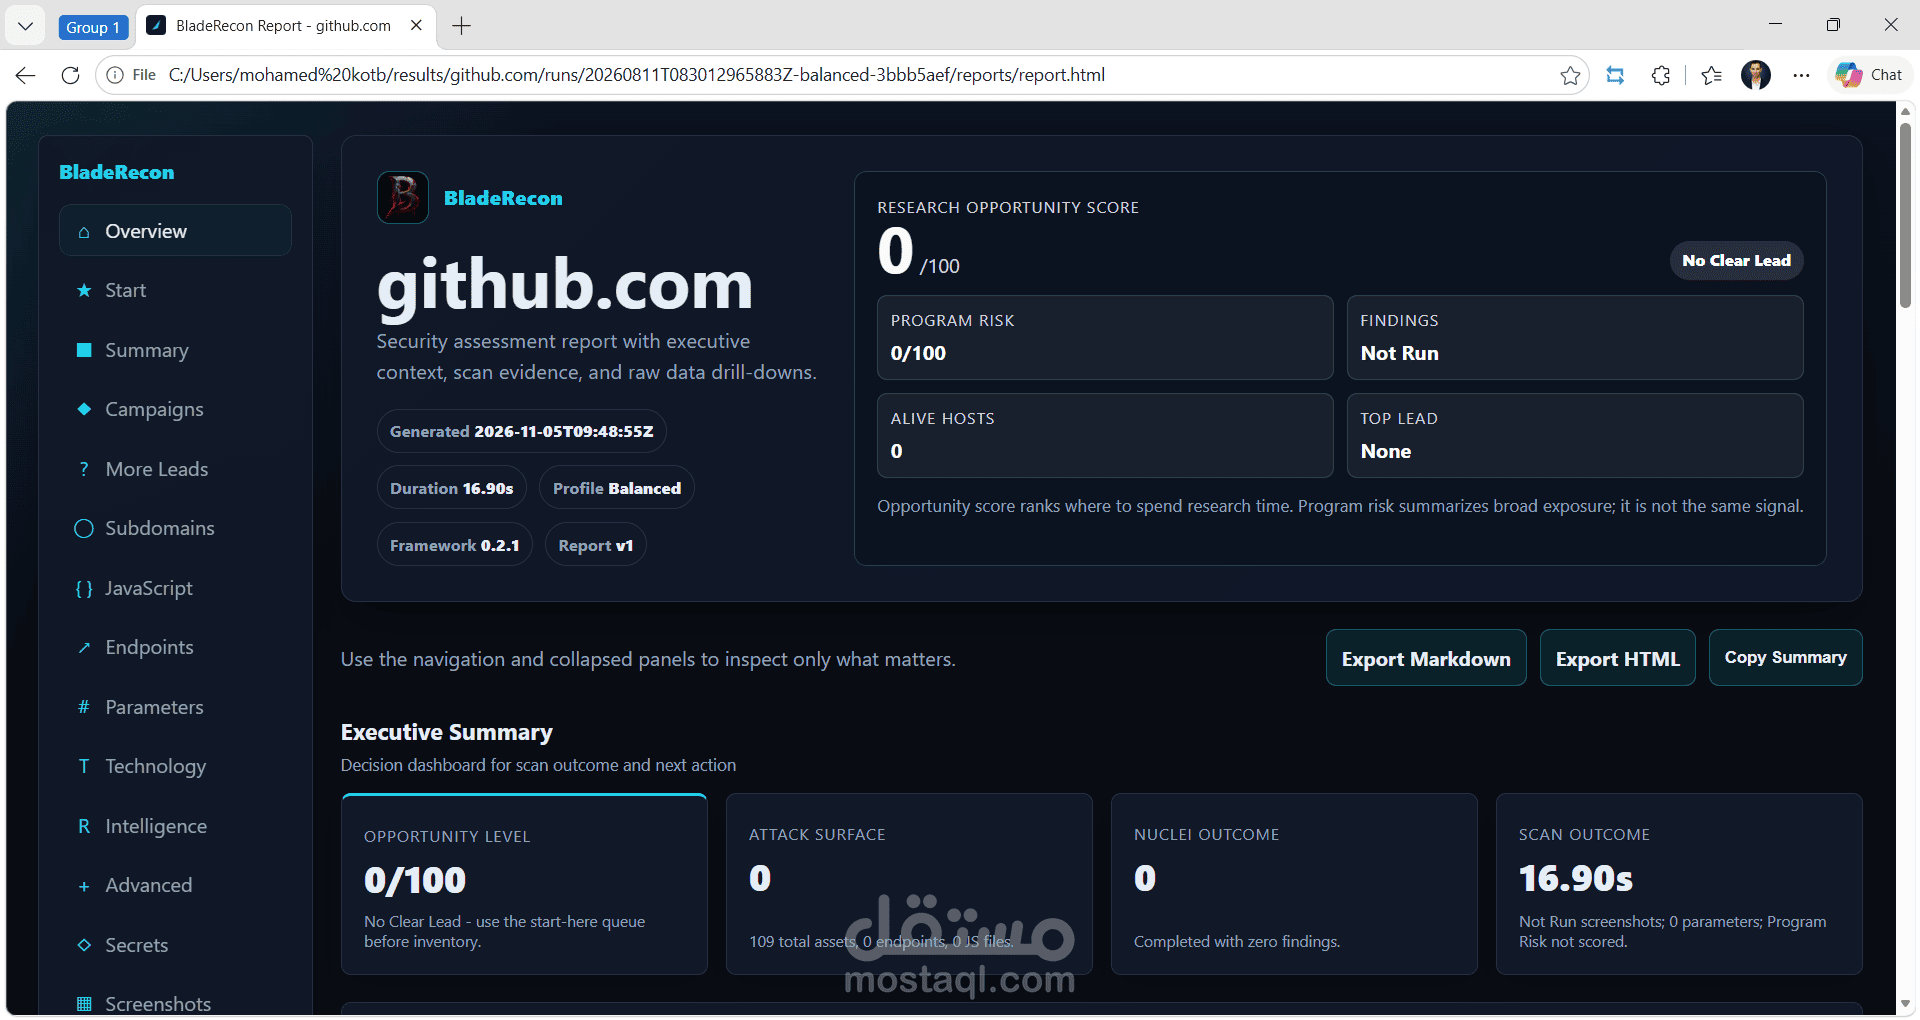
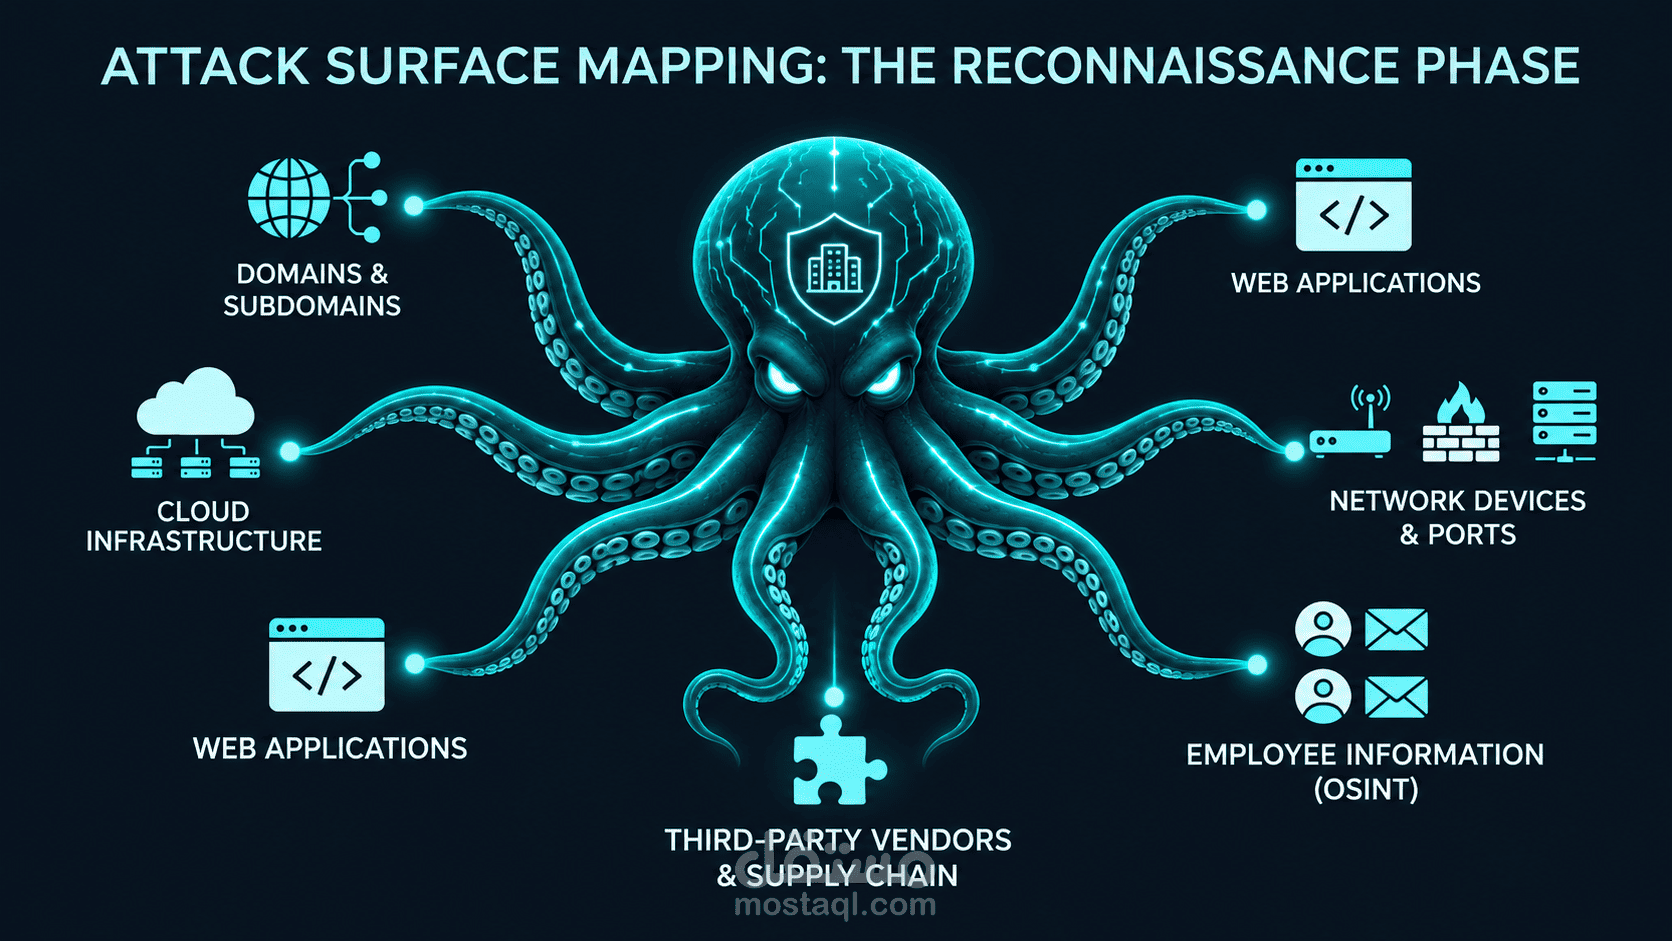
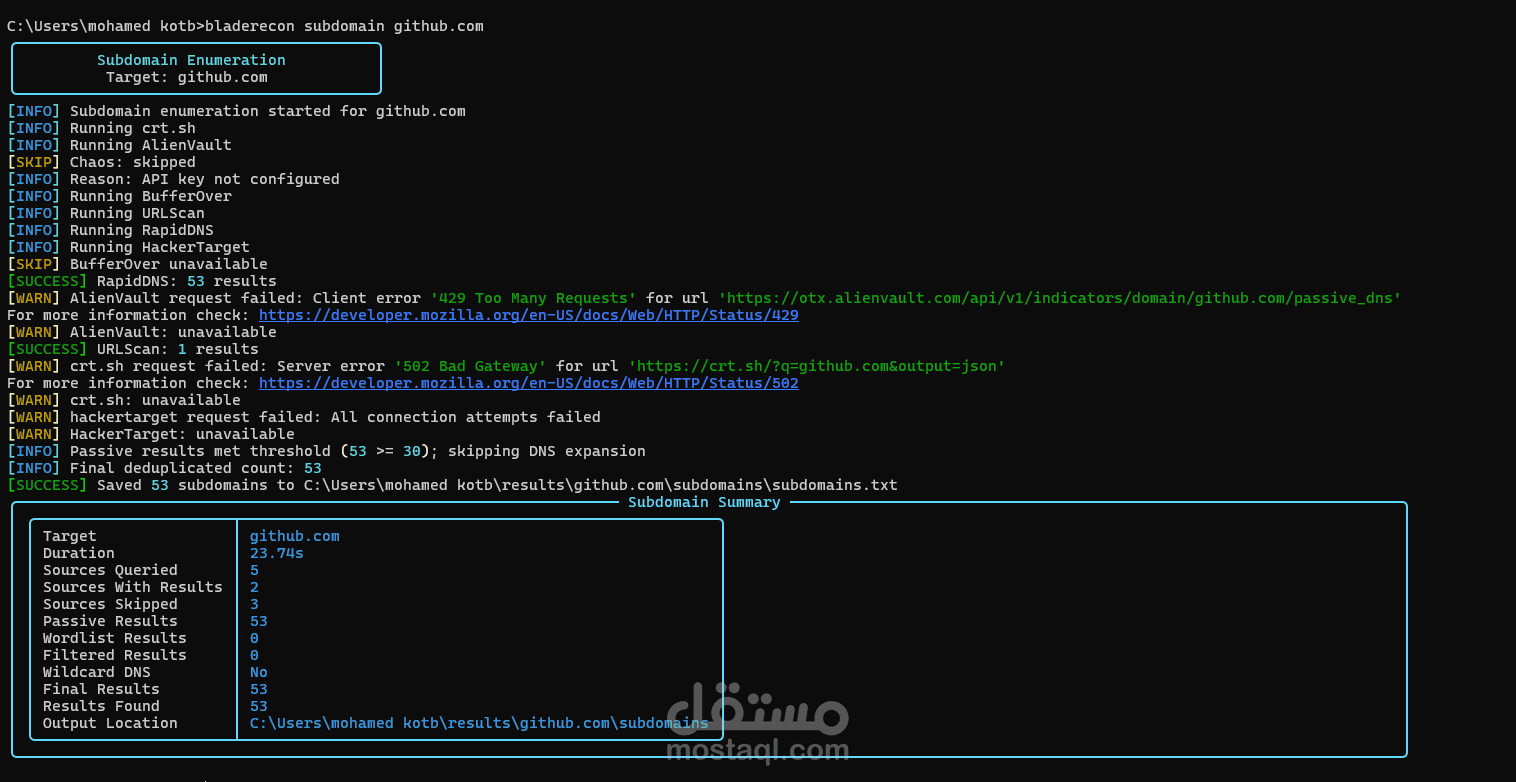
BladeRecon is a modular Python framework for reconnaissance and attack surface analysis, built for bug bounty hunters, penetration testers, and security researchers. It automates the recon stages and turns the collected data into correlated, prioritized findings. Instead of leaving you with hundreds of subdomains and endpoints to sort through by hand, it cuts the noise and shows which assets deserve a closer look.
What it does
Subdomain enumeration from passive sources such as crt.sh and AlienVault OTX.
Live host detection, with HTTP responses, headers, and technology fingerprints.
JavaScript analysis to extract endpoints, URLs, and exposed secrets.
Endpoint discovery: APIs, hidden routes, and interesting paths.
Secret discovery: possible credentials, API keys, tokens, and sensitive references.
Parameter discovery from historical sources.
Attack surface intelligence: correlates evidence, scores confidence, and ranks assets for follow-up.
Advanced recon: historical analysis and infrastructure correlation.
Screenshots of discovered web assets.
Nuclei integration for vulnerability scanning and validation.
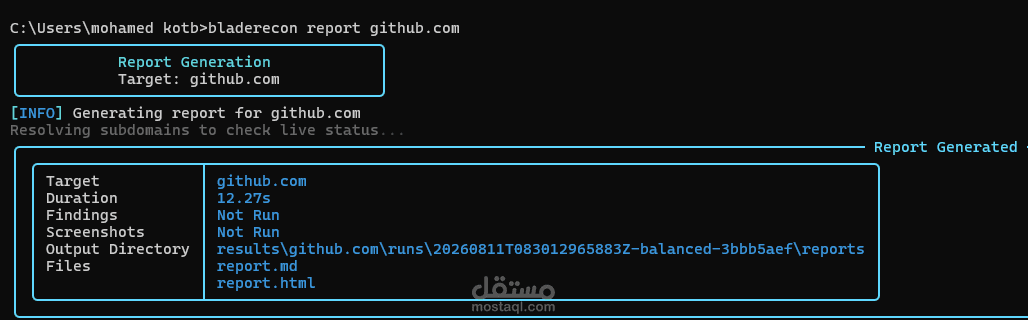
HTML and Markdown reports.
Stack: Python, Typer, Playwright, Nuclei, Jinja2, JSON, YAML, HTTPX, DNS.
Status: v0.2 release candidate, in active development and private testing.