Building a Production-Grade, Secure Multi-Tier AWS Architecture!
تفاصيل العمل
I just wrapped up my 2nd AWS cloud engineering project, moving beyond single-instance setups to design and deploy a complete Multi-Tier Network Architecture following industry best practices for network isolation and least-privilege security.
🏗️ Architectural Highlights:
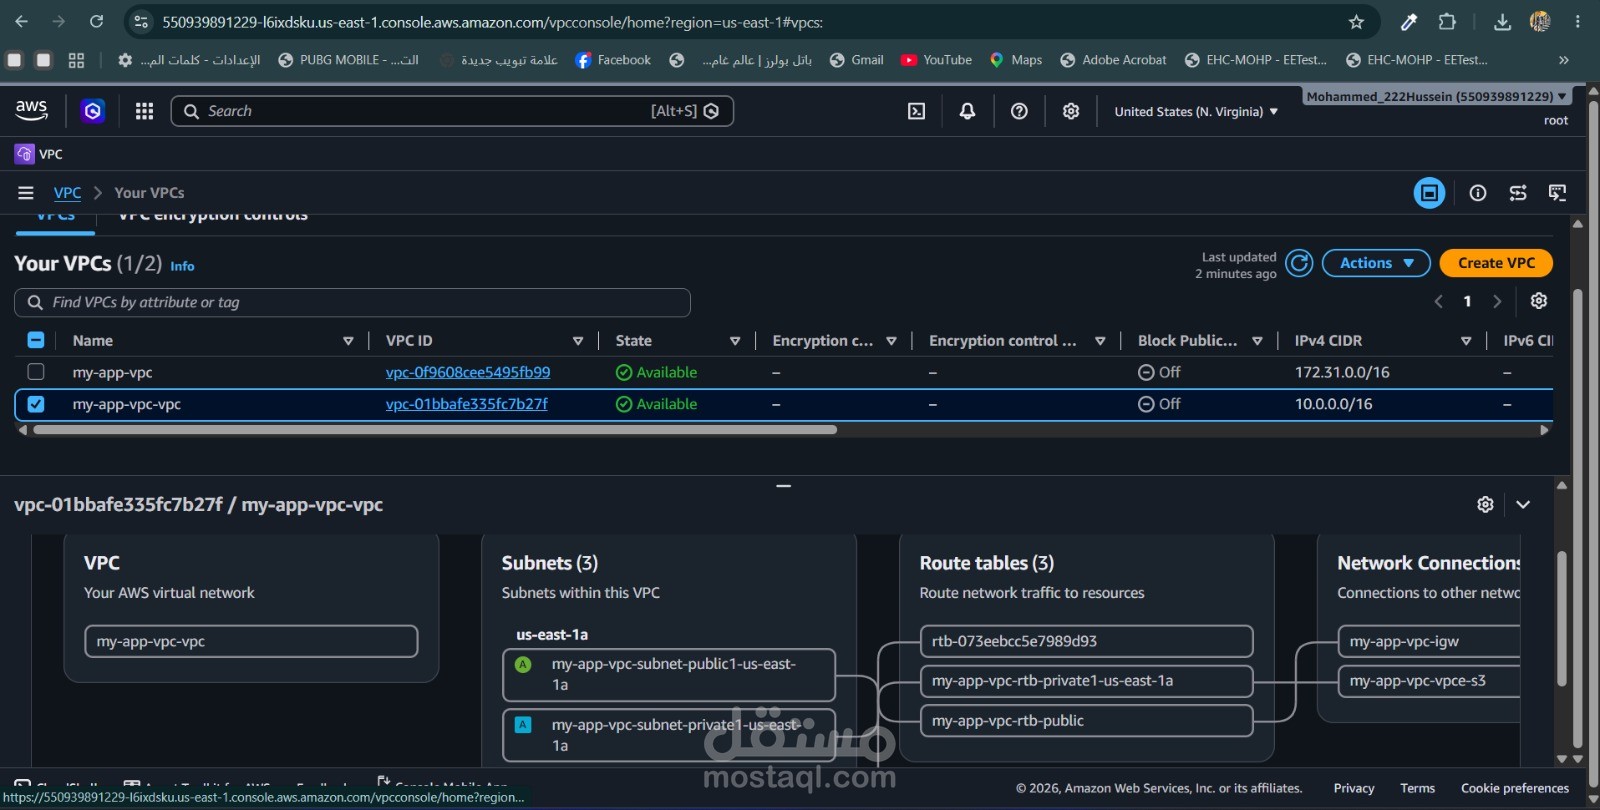
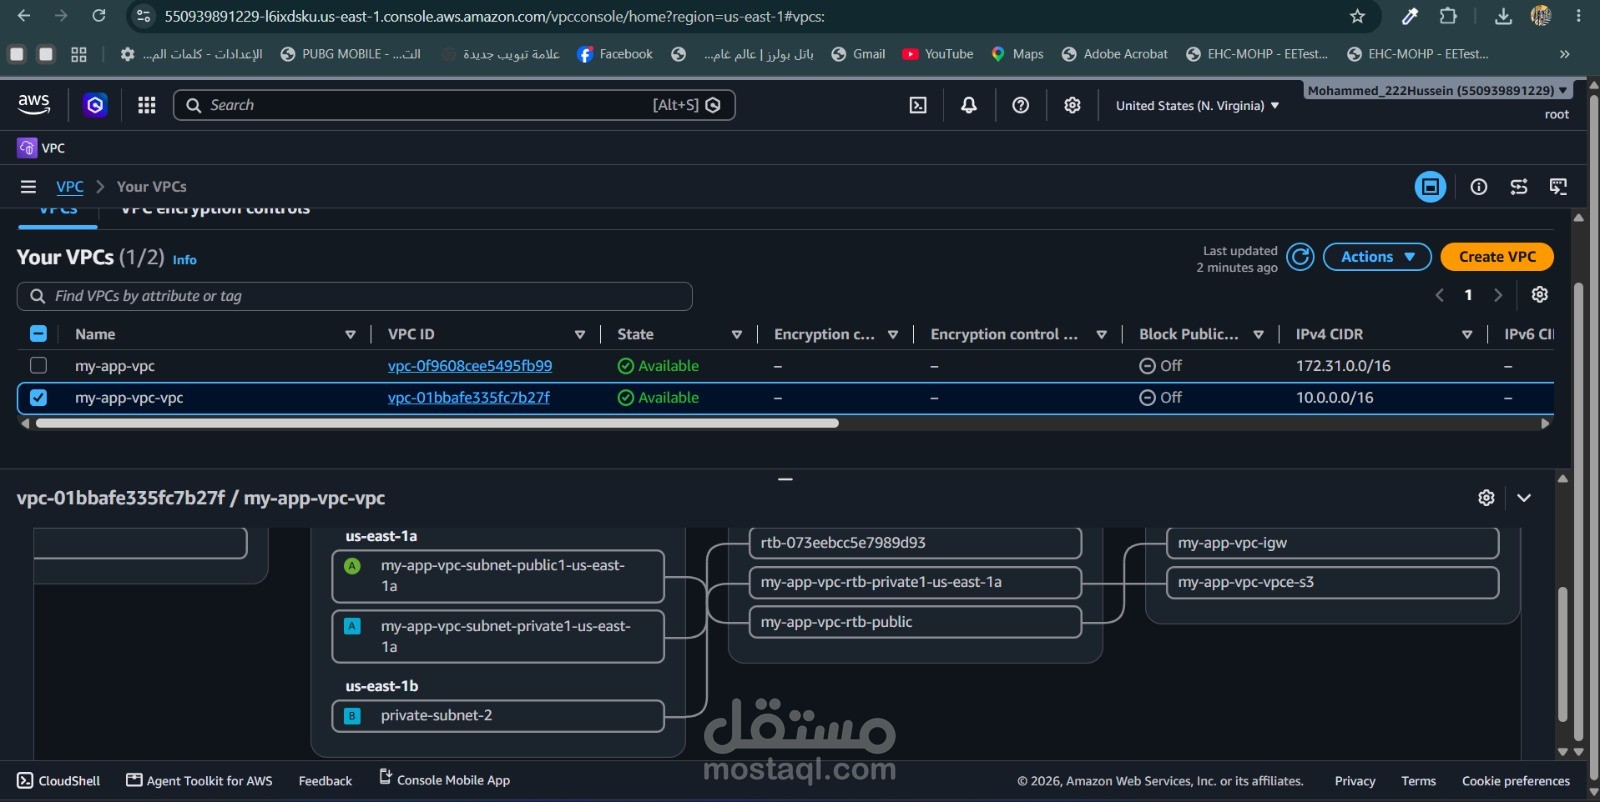
🔹 Networking (AWS VPC): Created a custom VPC (10.0.0.0/16) spanning multiple Availability Zones with custom Route Tables and an Internet Gateway (IGW).
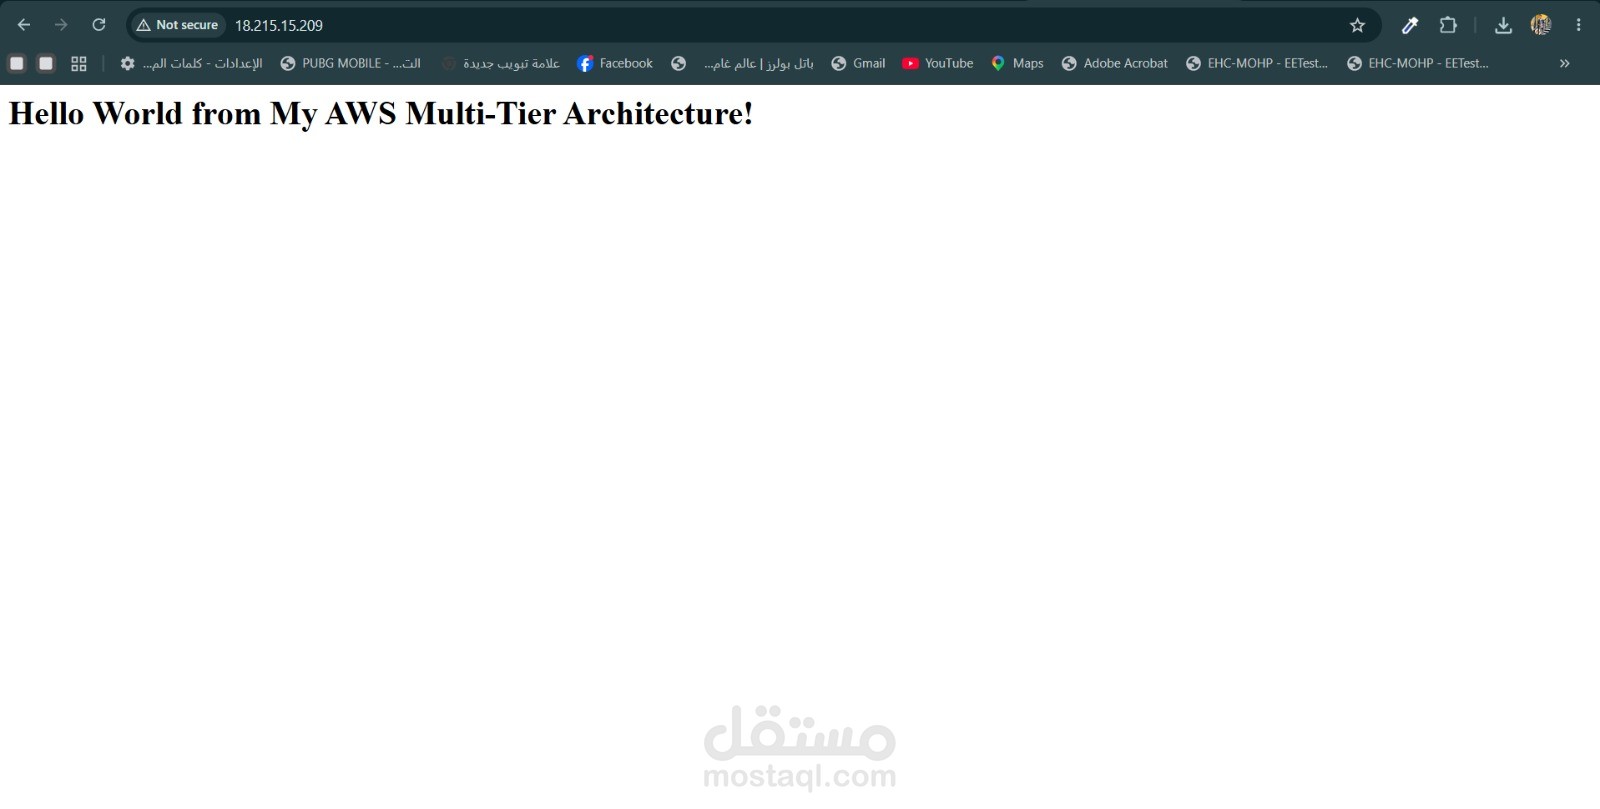
🔹 Public Tier (EC2): Deployed a public web server running Amazon Linux 2023, bootstrapped via User Data scripts to automatically run Apache.
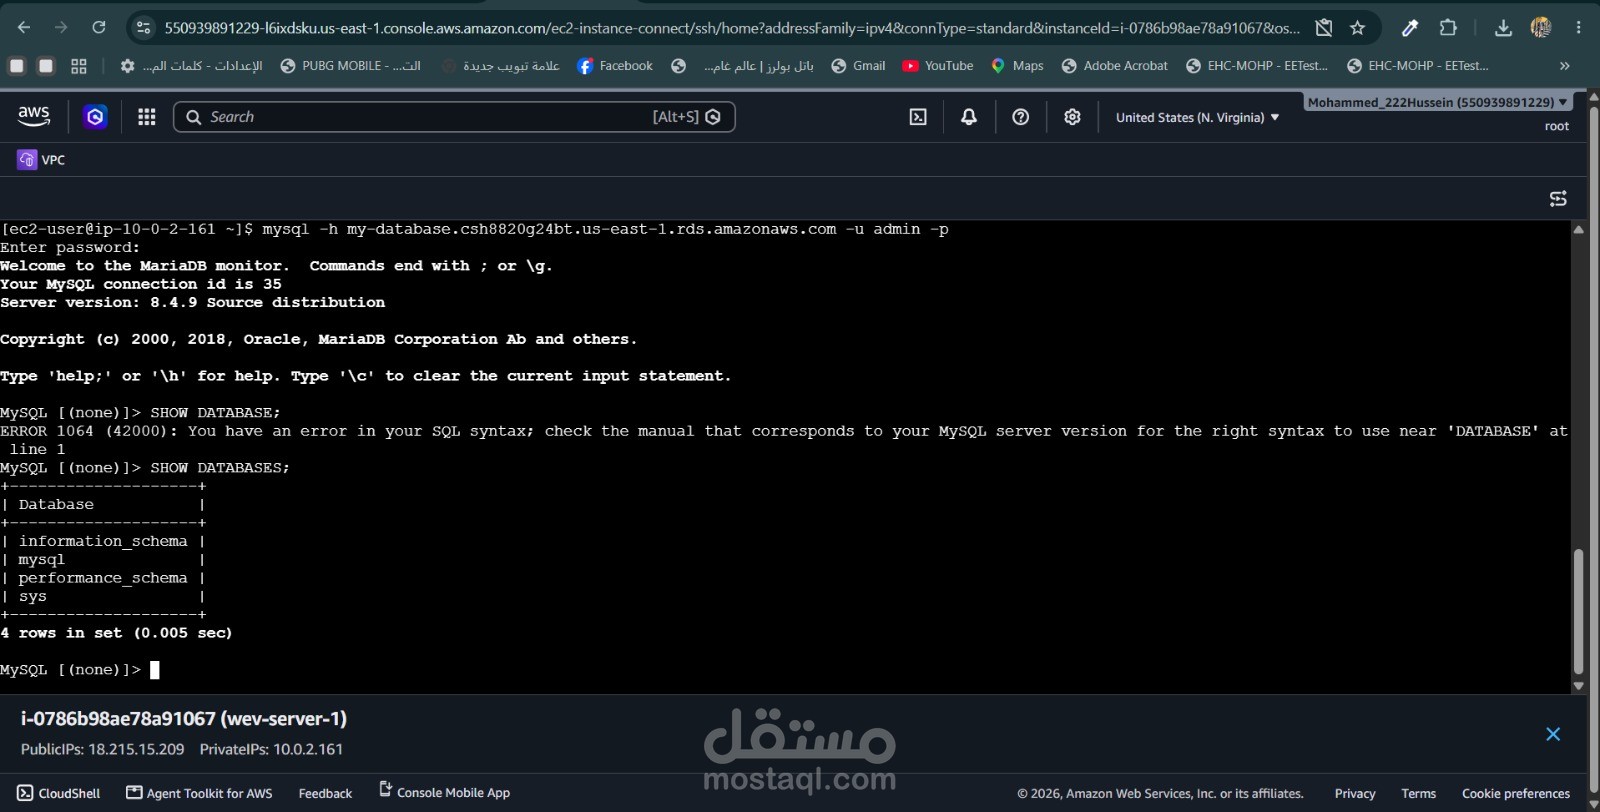
🔹 Private Tier (RDS MySQL): Provisioned a database instance completely isolated inside a Private DB Subnet Group with ZERO public internet access.
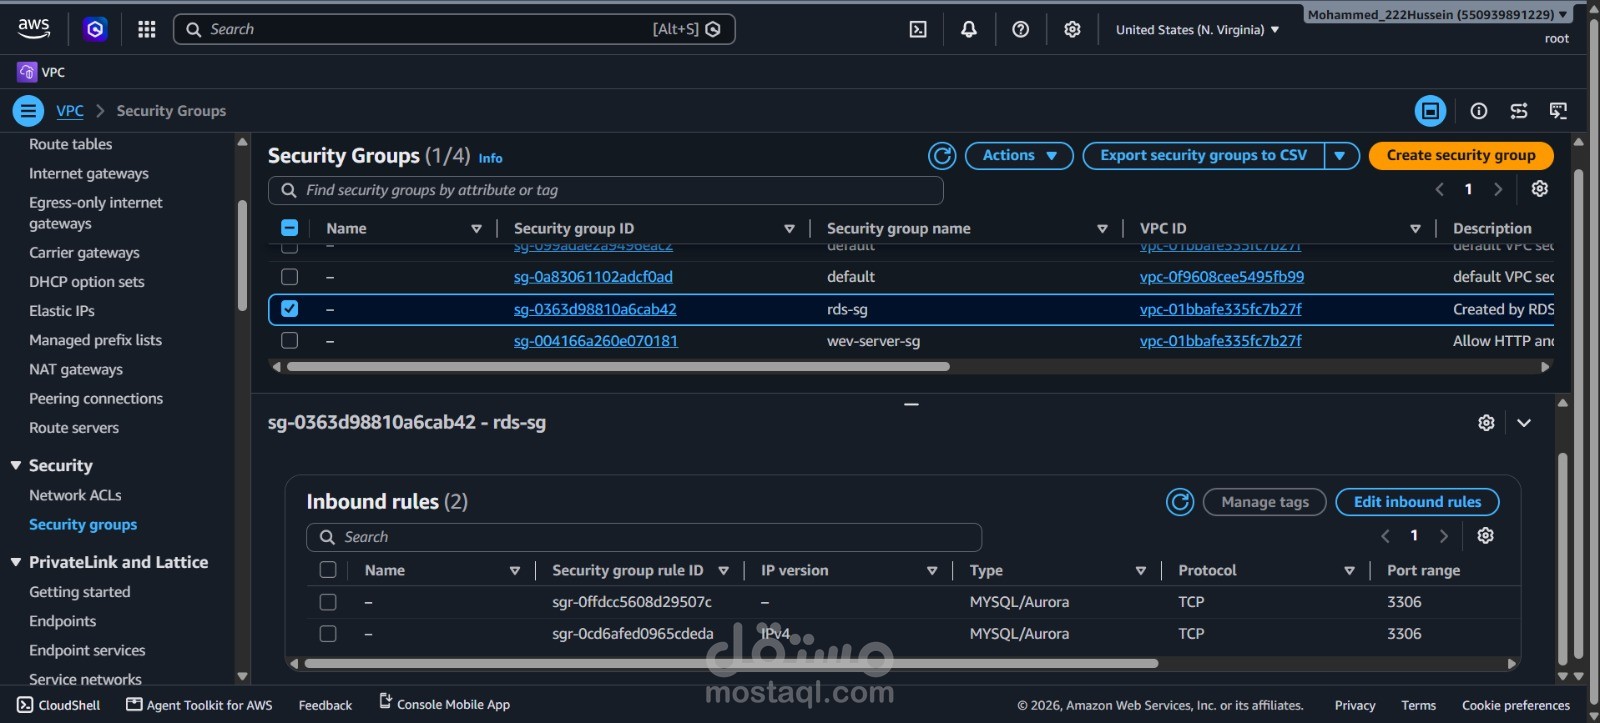
🔹 Least Privilege Security: Configured Security Groups (rds-sg) so that the RDS instance ONLY accepts MySQL traffic (Port 3306) coming directly from the Web Server's Security Group (web-server-sg).
🧪 Verification & Testing:
Verified cross-tier connectivity directly via SSH/Terminal by querying the isolated database directly from the web server instance.
💡 Key Takeaway: Real security isn't just about passwords—it's about controlling network pathways and ensuring database tiers remain entirely invisible to the public internet.