Network Design
تفاصيل العمل
How it works
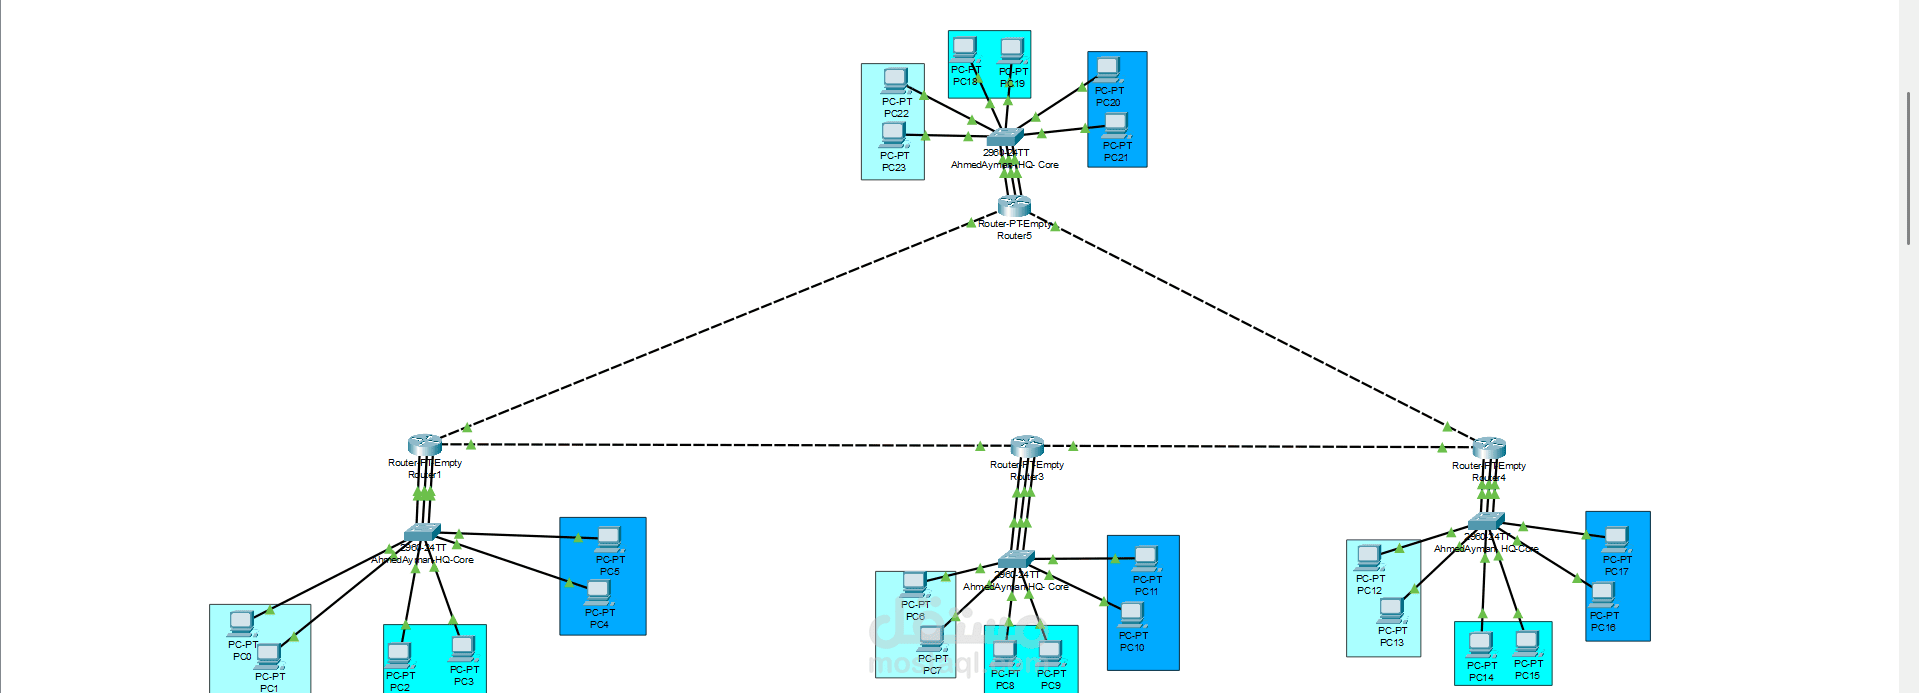
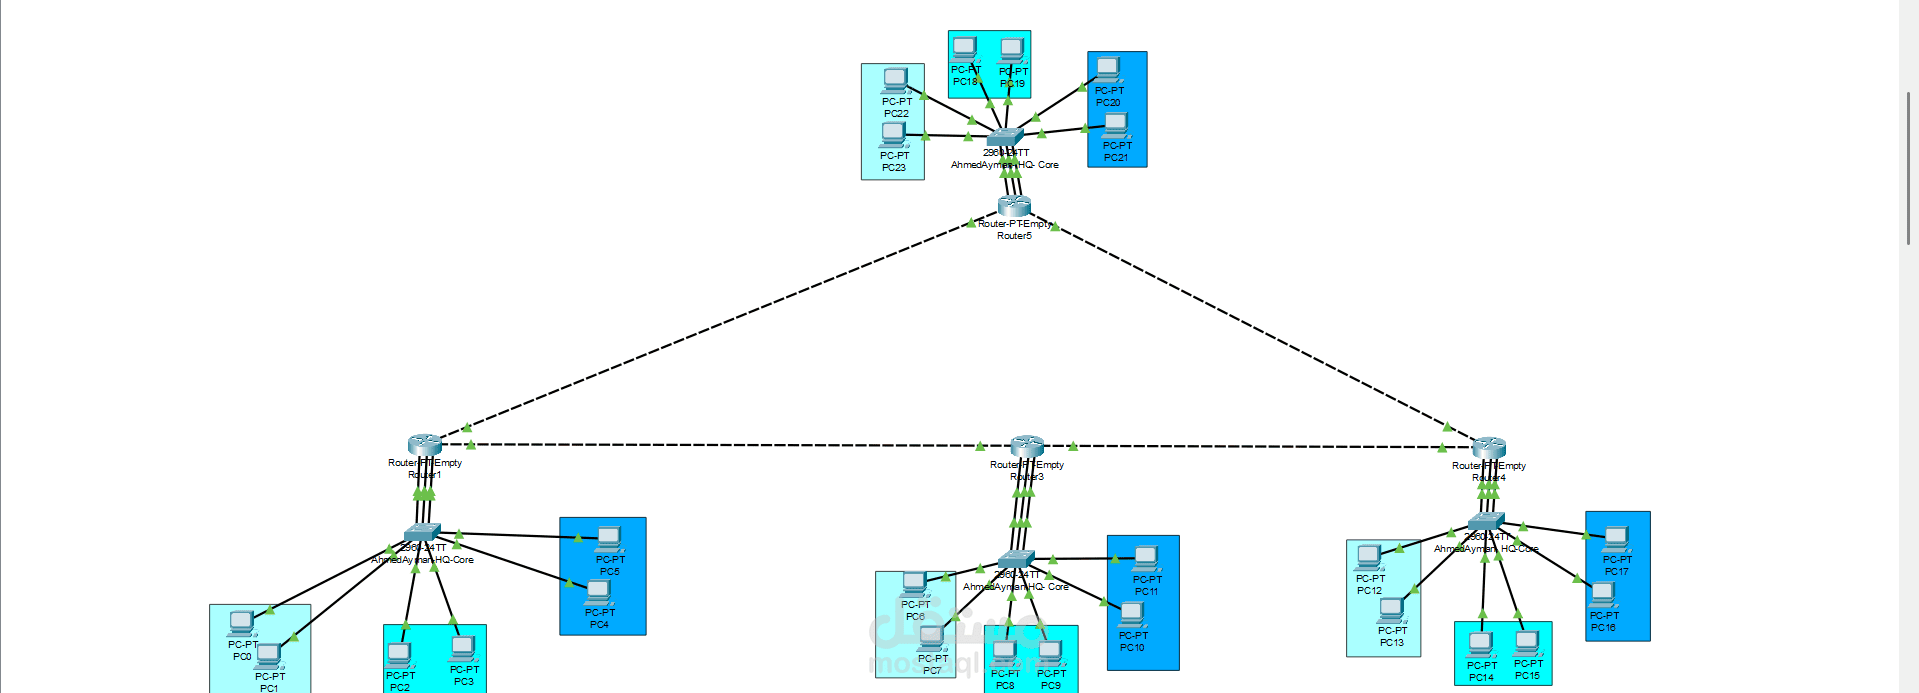
Planned the topology: one headquarters site and three branch sites, each with its own switches and PCs, linked through routers.
Divided the address space into smaller subnets using VLSM so no IP addresses are wasted.
Created VLANs to separate departments inside each site.
Configured DHCP so PCs get their IP settings automatically.
Configured RIP routing so routers learn all remote networks (the routing table shows RIP routes with metric 120/1).
Tested end to end: a ping from a PC in one site to a PC in another succeeded with 4/4 replies and 0% loss.
Next steps: VPN integration and extra security hardening.