..SQL-Injection-Hardening
تفاصيل العمل
SQL Injection Hardening — Lab 1 (Secure Software Development)
This README.md documents the hardened version of a Node.js + SQLite demo app. The goal was to find and fix critical security issues (especially SQL injection), add server-side input validation, and secure password storage. Copy & paste this file into your repo root.
Quick summary
✅ Fixed: SQL injection by using parameterized/prepared queries.
✅ Added: Server-side input validation & sanitization (express-validator).
✅ Secured: Passwords hashed with bcrypt (no plaintext passwords).
✅ Improved: Error handling/logging to avoid leaking internal details.
Changes implemented (technical details)
Login endpoint hardened
Replaced string-concatenated SQL with parameterized queries (e.g. db.get("SELECT ... WHERE username = ?", [username])).
All user input is passed as query parameters, so it cannot be executed as SQL.
Input validation & sanitization
Added server-side validation middleware using express-validator for endpoints that accept user input (e.g., /login, /register).
Example rules used: username = alphanumeric, 3–30 chars; password = minimum length (configurable).
Inputs are sanitized where appropriate (.trim(), .escape()).
Secure password handling
Passwords are hashed (and salted) using bcrypt before being stored.
init-db.js seeds sample users with hashed passwords.
Login flow uses bcrypt.compare() to verify passwords.
Safer error handling and logs
Client-facing error messages do not include DB internals or stack traces.
Server logs contain enough info for debugging without leaking secrets.
Key files changed
routes/auth.js (or equivalent): login/register routes now use parameterized queries and bcrypt.
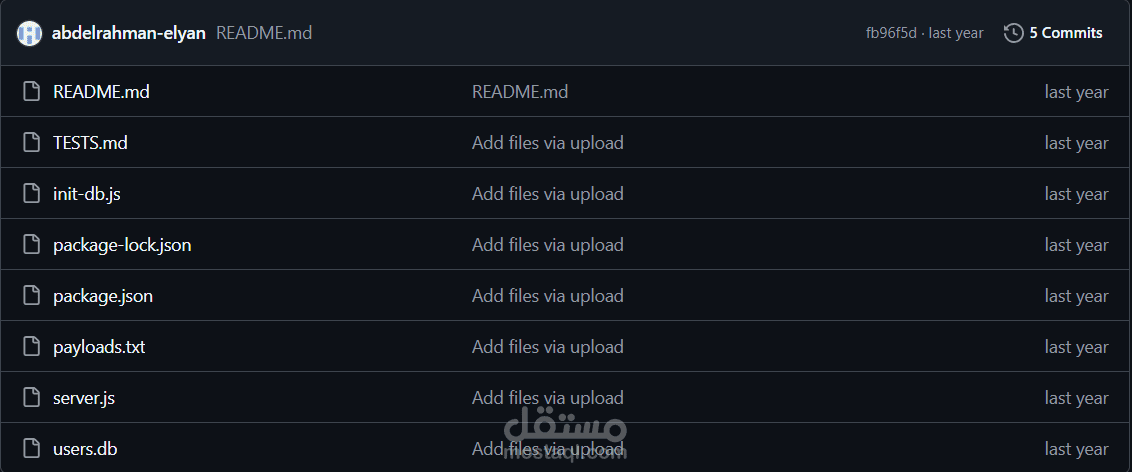
init-db.js: creates users.db and seeds test users with hashed passwords.
package.json: includes bcrypt and express-validator dependencies.
TESTS.md: separate file with quick curl test commands.
Prerequisites
Node.js 16+ and npm installed.