FortiGate firewall lab
تفاصيل العمل
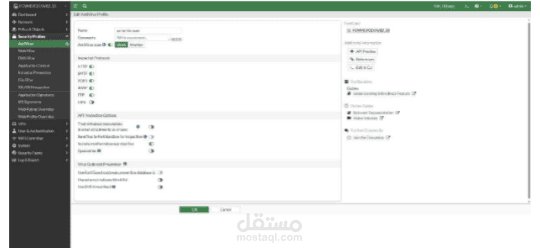
This project involved configuring a FortiGate next-generation firewall to secure a network environment. The work included creating a LAN-to-WAN policy to control outgoing traffic, setting up user accounts with administrator profiles, and installing certificates for secure communication. Security features were then layered on top, including an antivirus profile, web and URL filtering, and application control to block unwanted or risky traffic. The lab also covered a site-to-site VPN, which securely connects two separate networks over the internet. Together, these steps show how a firewall can be used to enforce access policies, filter threats, and protect data in transit.