محلل سجلات
تفاصيل العمل
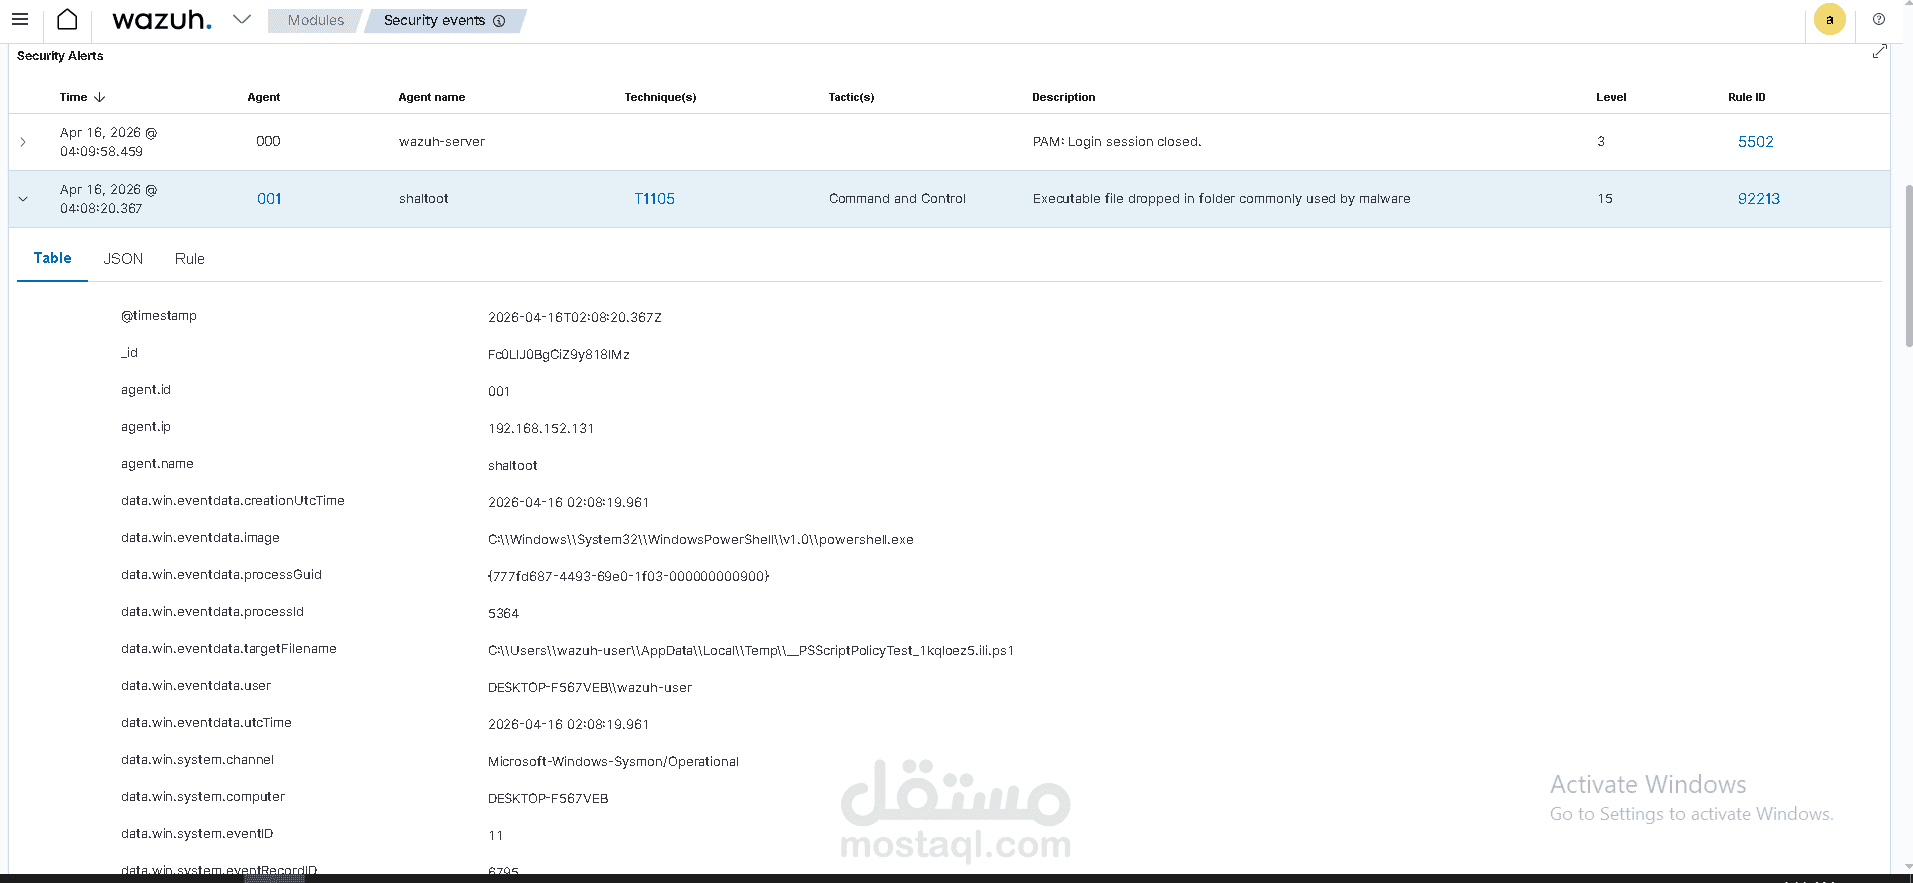
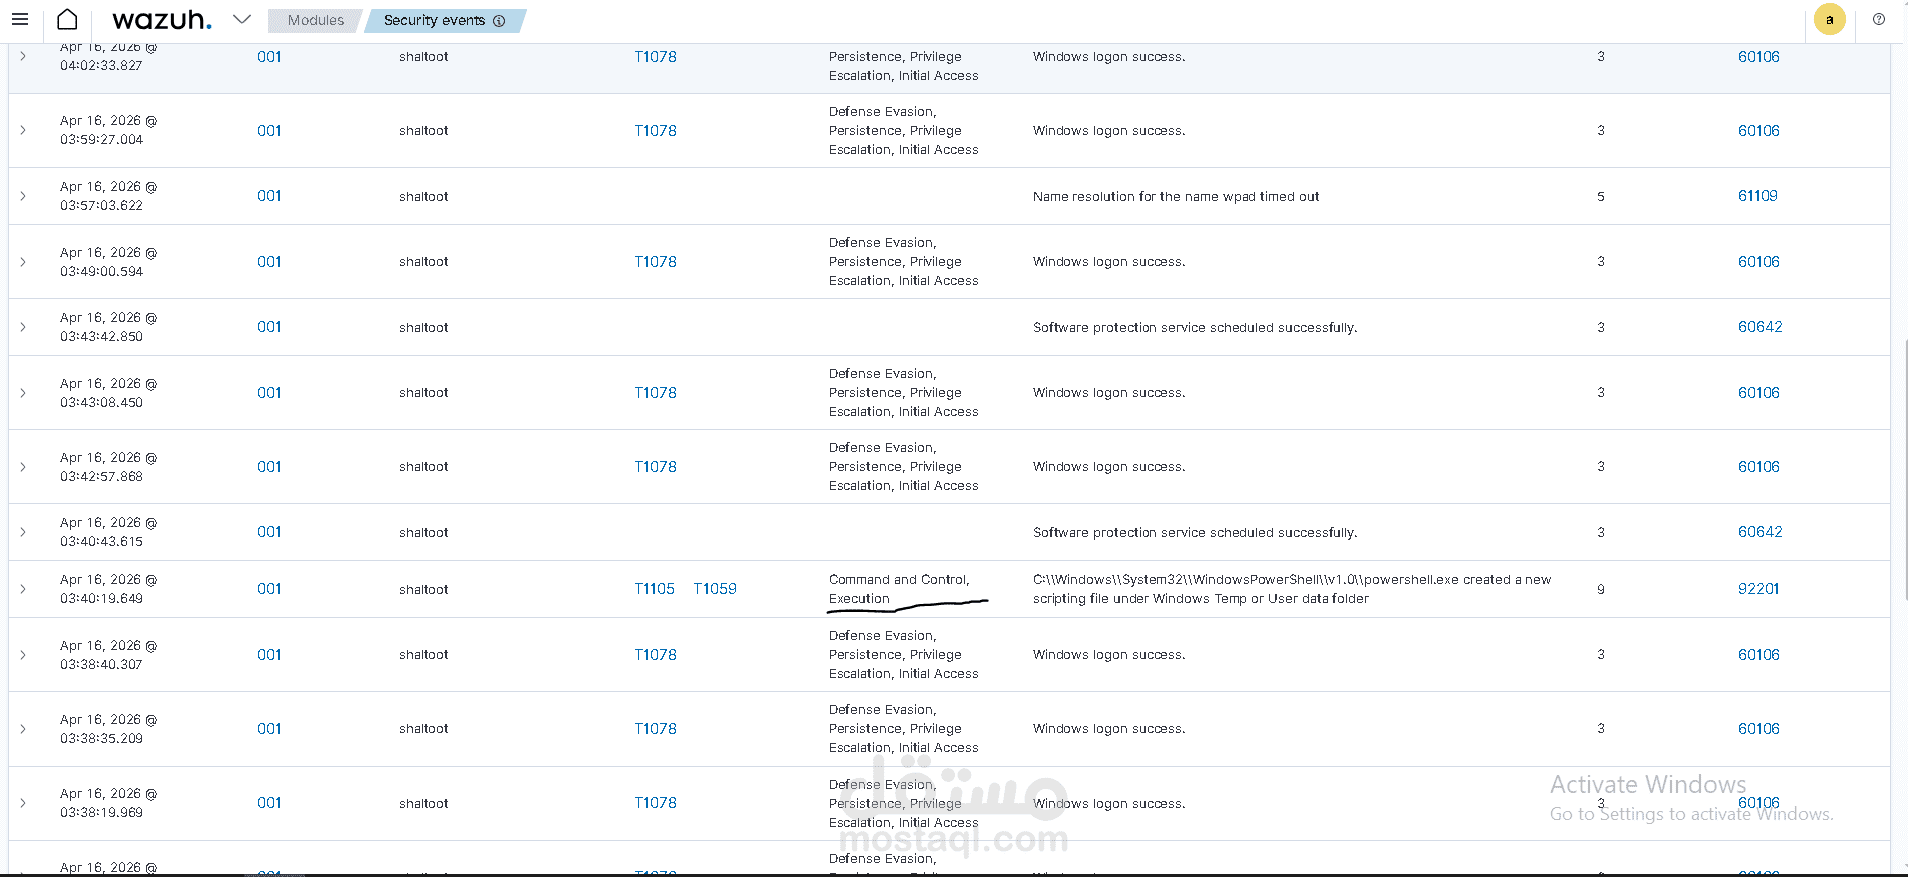
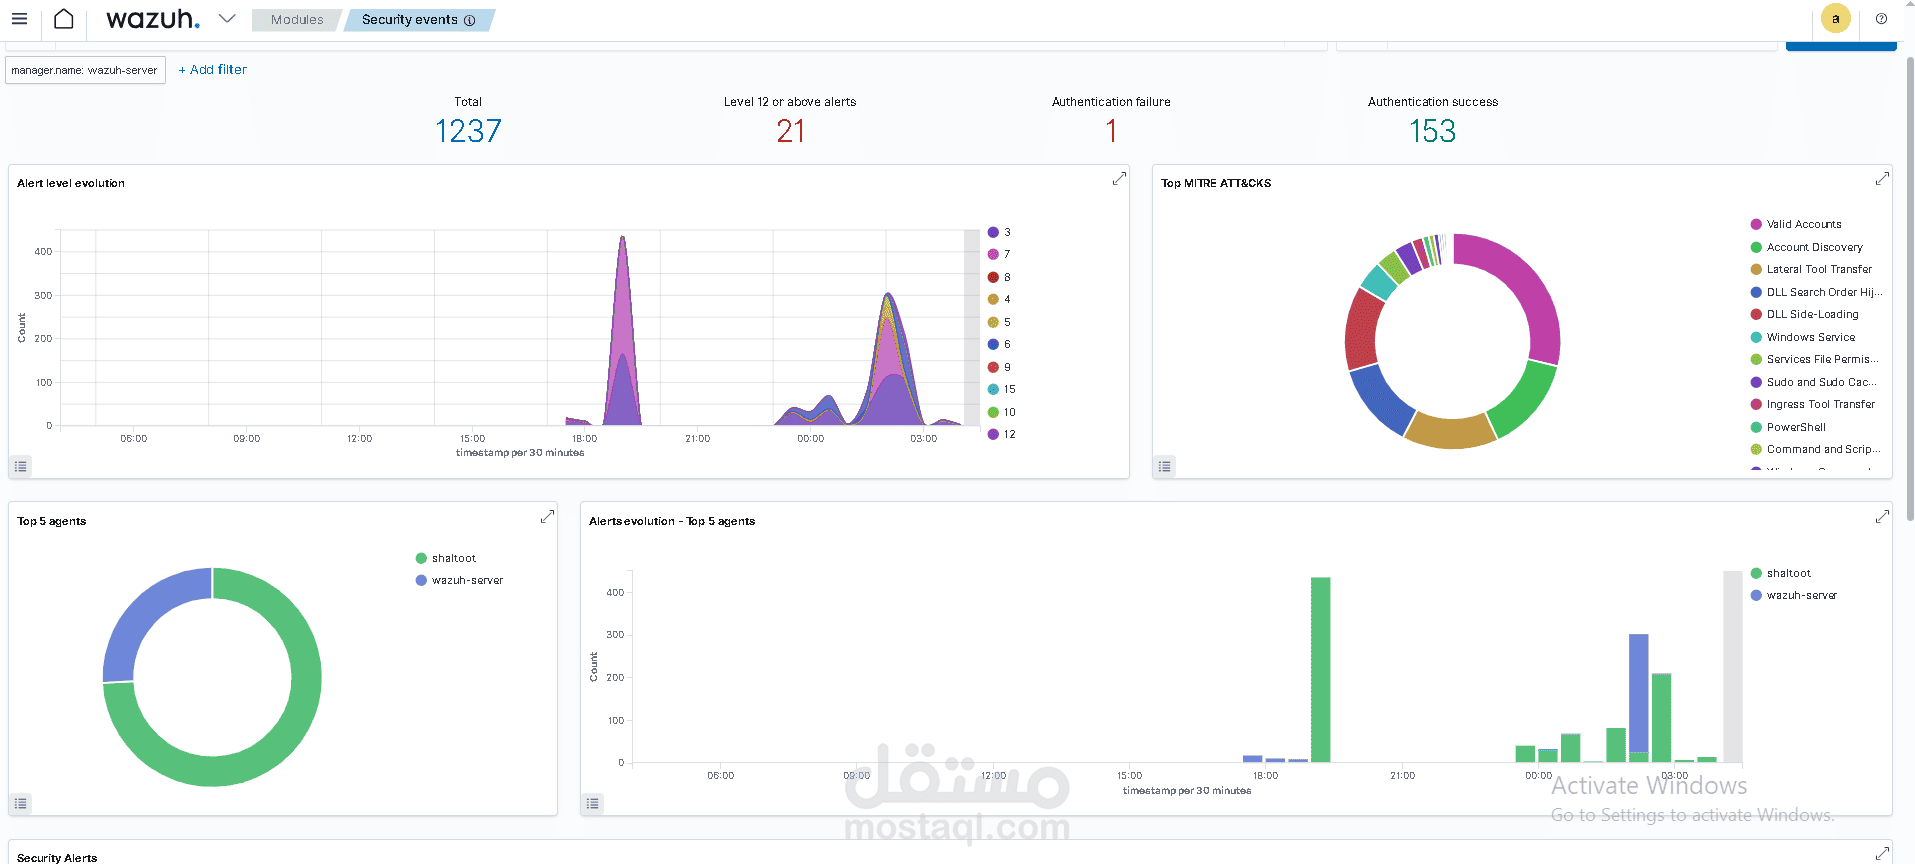
Log collection and analysis using Wazuh & Sysmon
Monitoring Windows Event Logs
Creating detection rules and alerts
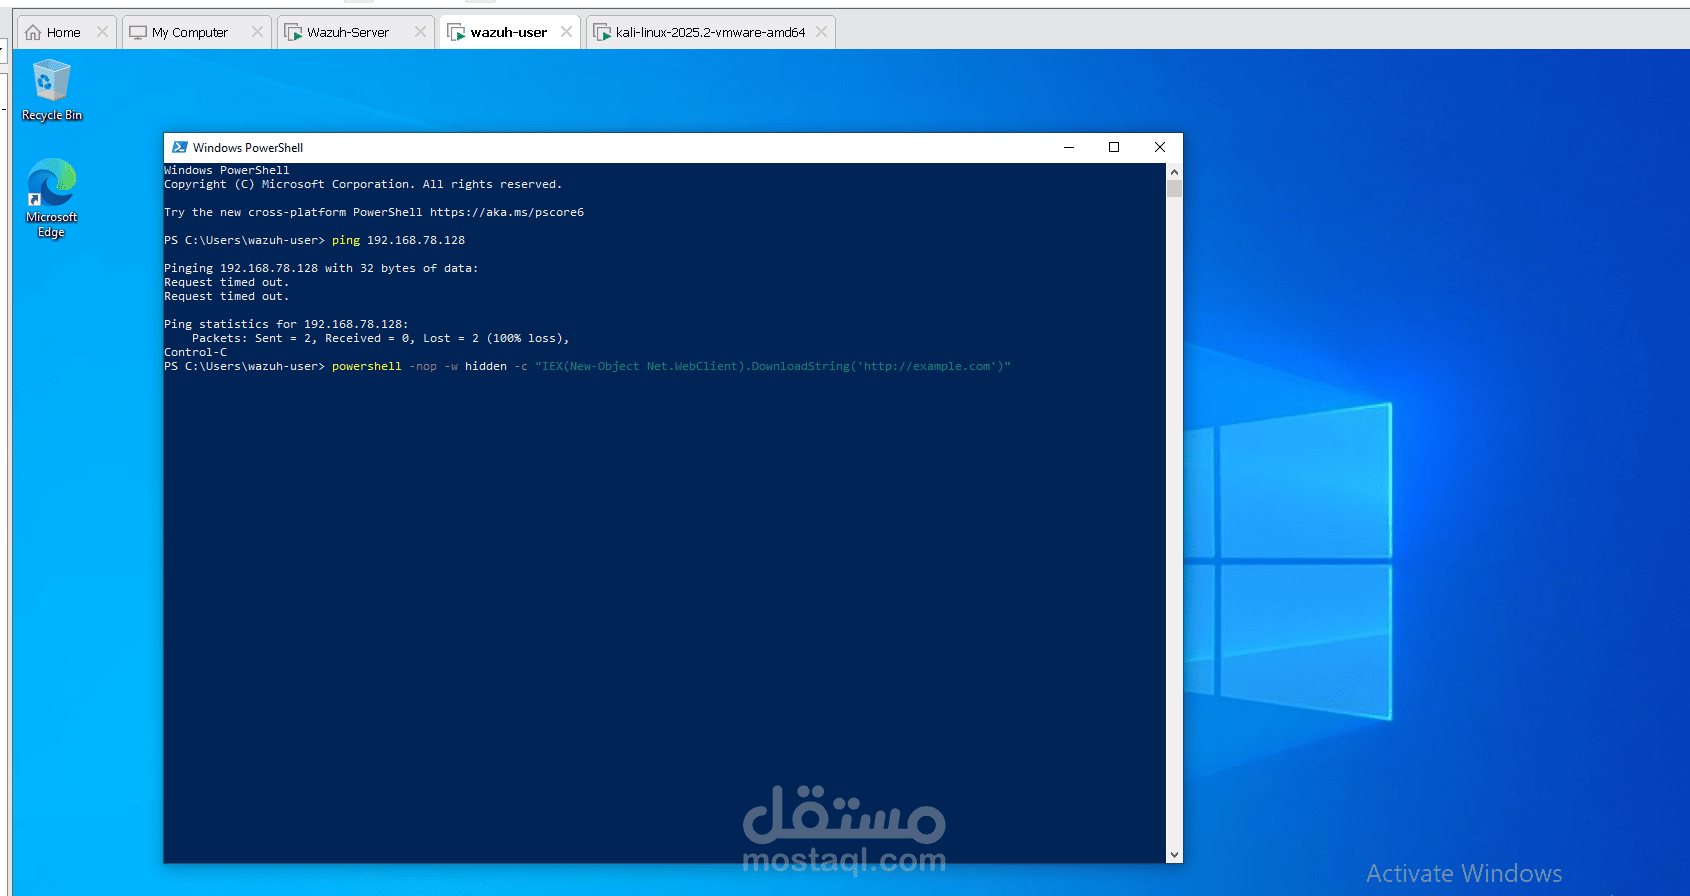
Simulating attacks to test detection capabilities
Basic threat hunting using MITRE ATT&CK techniques
🛠️ Tools & Technologies:
Wazuh | Sysmon | Snort | Windows Event Logs
This project helped me understand how SOC teams monitor, detect, and respond to security incidents in real environments.