Wireshark Malware Traffic Analysis & Network Forensics
تفاصيل العمل
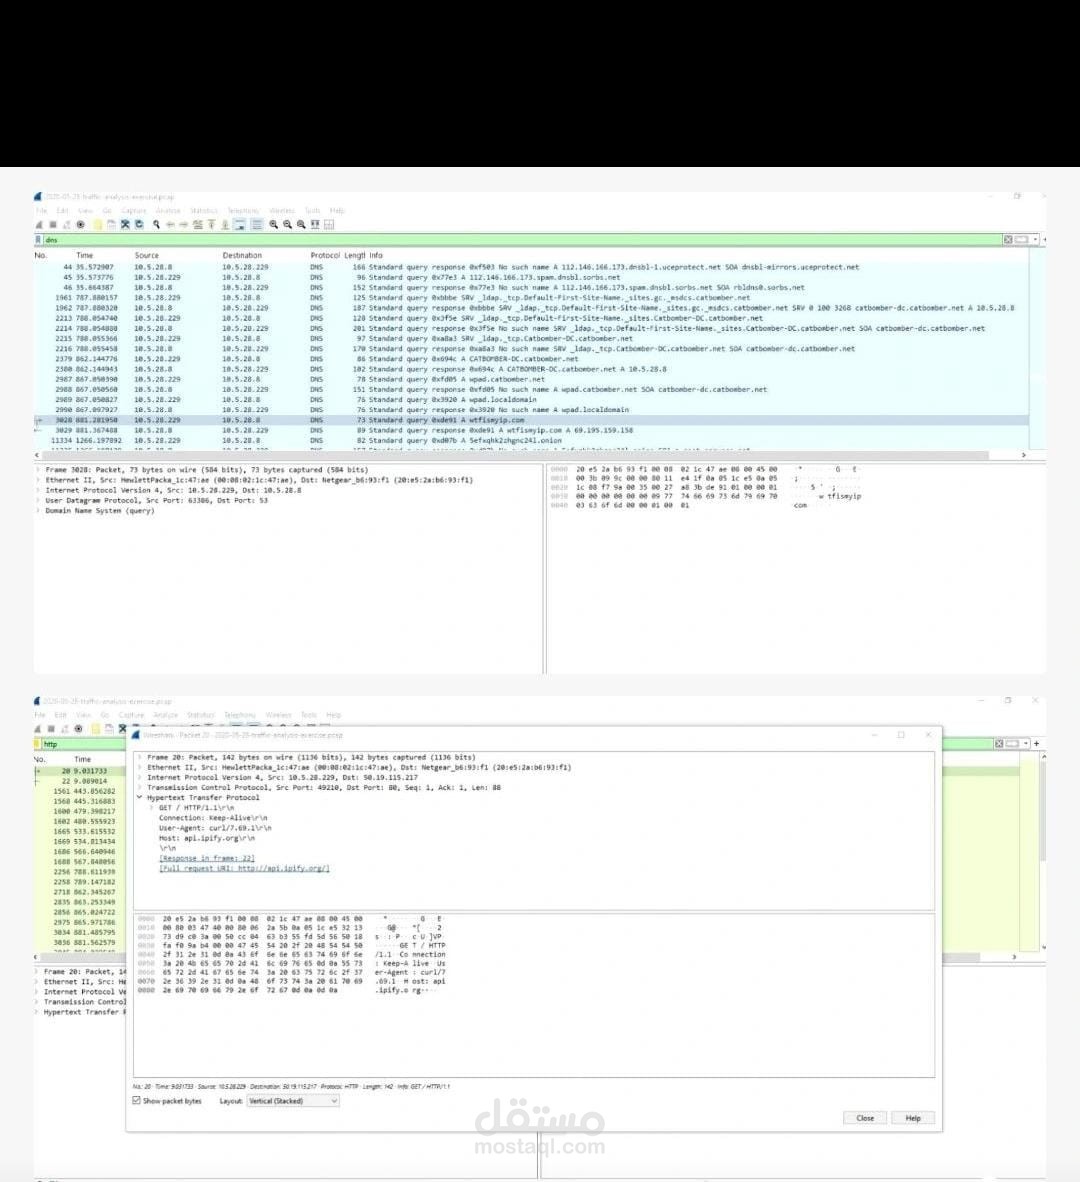
Wireshark Malware Traffic Analysis & Network Forensics
Project Overview
Hands-on cybersecurity investigation using Wireshark to analyze a PCAP file and investigate suspicious network traffic associated with malware activity.
The project focused on reconstructing the attack flow, analyzing HTTP and DNS communications, identifying attacker behavior, and extracting Indicators of Compromise (IOCs) relevant to threat detection and incident response.
What I Analyzed
- Analyzed suspicious HTTP GET/POST requests and network communications.
- Investigated malware delivery and identified a suspicious file disguised as an image.
- Reconstructed the malware communication flow with its Command & Control (C2) infrastructure.
- Analyzed system and network reconnaissance activities.
- Investigated process enumeration and information-gathering behavior.
- Identified attempts to access sensitive credentials and configuration data.
- Performed DNS traffic analysis to identify suspicious network activity.
- Extracted relevant IOCs including malicious IP addresses, domains, files, and network artifacts.
Skills & Tools
Wireshark | PCAP Analysis | Malware Traffic Analysis | HTTP Analysis | DNS Analysis | Network Forensics | Digital Forensics | Incident Response | IOC Identification | Threat Hunting
Project Outcome
This project strengthened my practical ability to investigate suspicious network traffic, understand malware communication patterns, reconstruct attack activity, and extract actionable indicators that can support SOC investigations and incident response.