Temporary Rate Limit Bypass – Responsible Disclosure Report
تفاصيل العمل
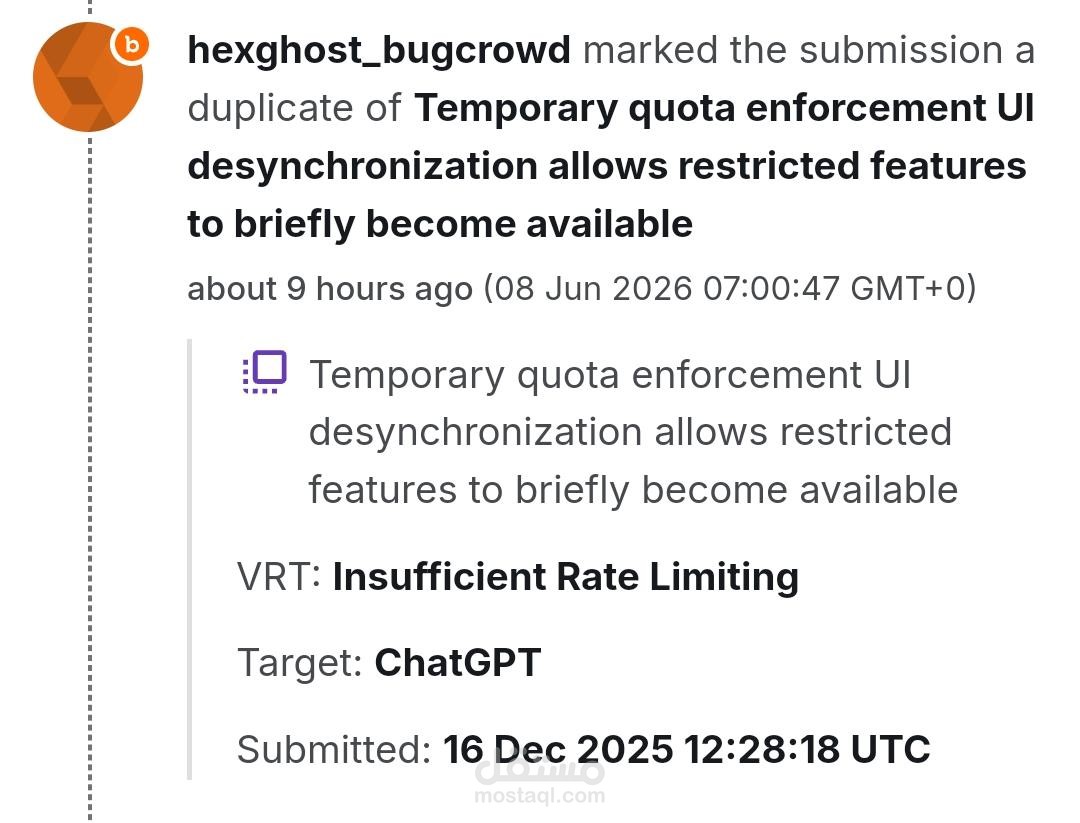
Identified and responsibly reported a temporary rate-limit bypass affecting a security-related workflow. The issue was submitted through Bugcrowd and reviewed by the program team.
The report was later marked as a duplicate of an existing submission and classified as Informational, with the customer team determining that it had no security impact.
This submission demonstrates practical experience in vulnerability research, responsible disclosure, security testing, and communicating findings through a bug bounty platform.