fortigate project
تفاصيل العمل
FortiGate Firewall Network Security Lab
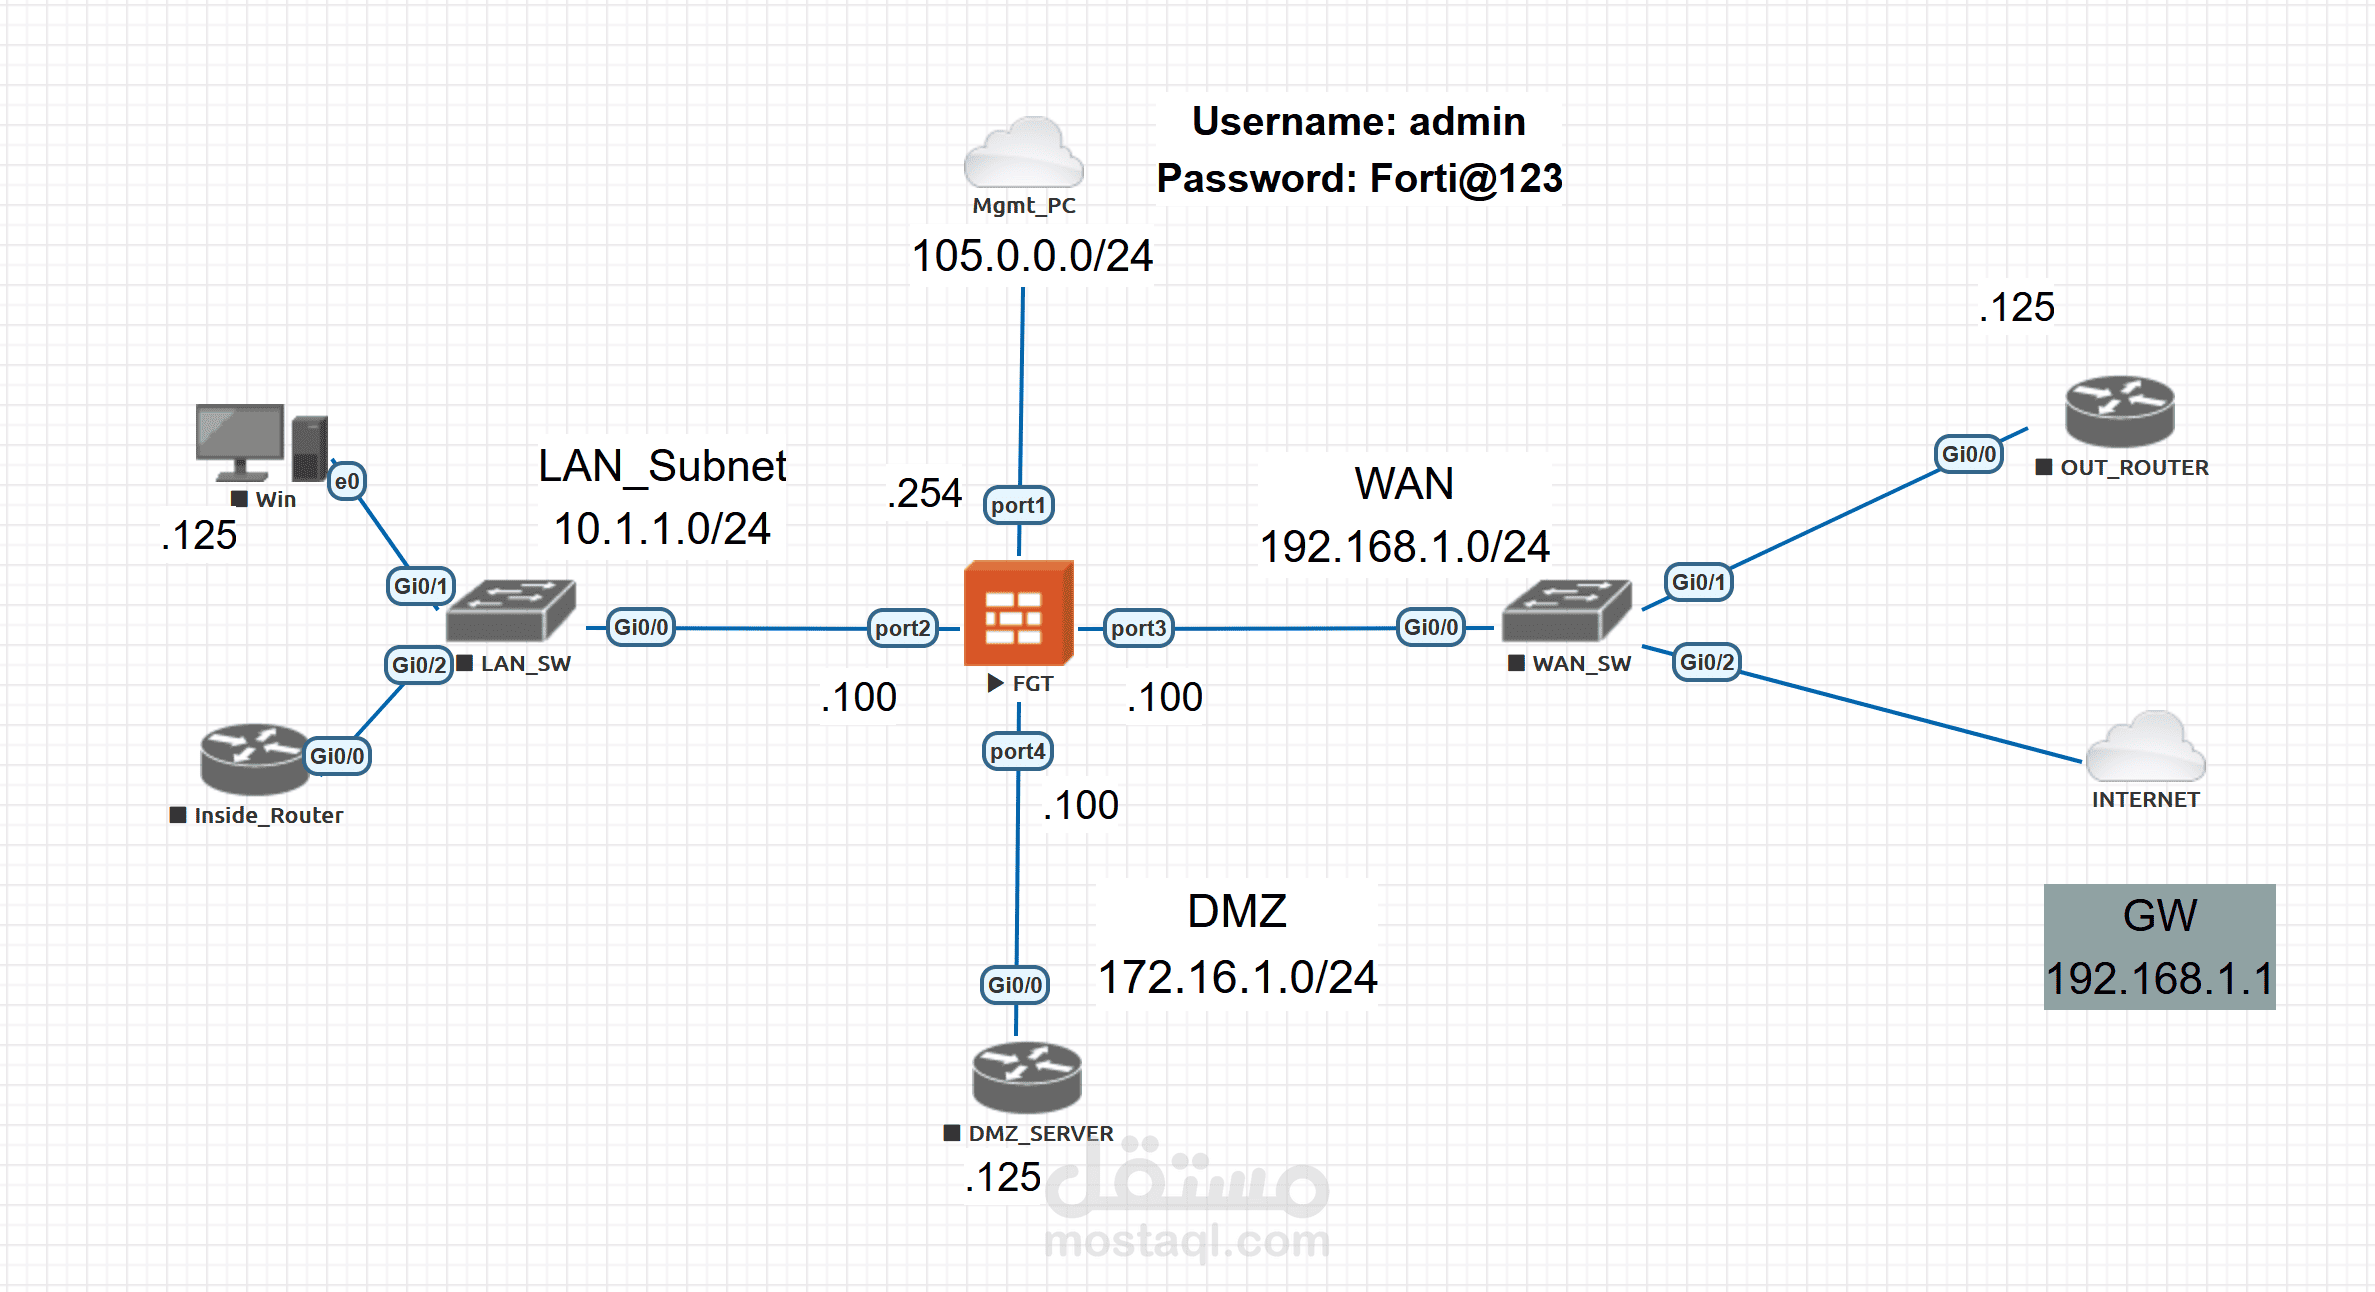
Designed and configured a network security topology using FortiGate Firewall, Cisco switches, routers, and multiple network segments. The topology demonstrates how a firewall can be positioned between the internal network, WAN, and DMZ to control and secure network traffic.
The internal LAN uses the 10.1.1.0/24 subnet and is connected to the FortiGate through a dedicated LAN switch. The WAN side uses 192.168.1.0/24 and connects the firewall to an external router and the Internet. A separate DMZ network (172.16.1.0/24) is configured for hosting services that need to be isolated from the internal LAN.
The project focuses on understanding network segmentation, firewall interfaces, IP addressing, WAN connectivity, DMZ architecture, and secure traffic management using FortiGate.
Key Concepts:
FortiGate Firewall Configuration
Network Segmentation
LAN / WAN / DMZ Architecture
IP Addressing & Subnetting
Firewall Interfaces
Default Gateway
Network Security & Traffic Control
Cisco Routers & Switches
Internet/WAN Connectivity
Tools: FortiGate | Cisco Routers & Switches | Network Simulation Lab