Network Security Assessment
تفاصيل العمل
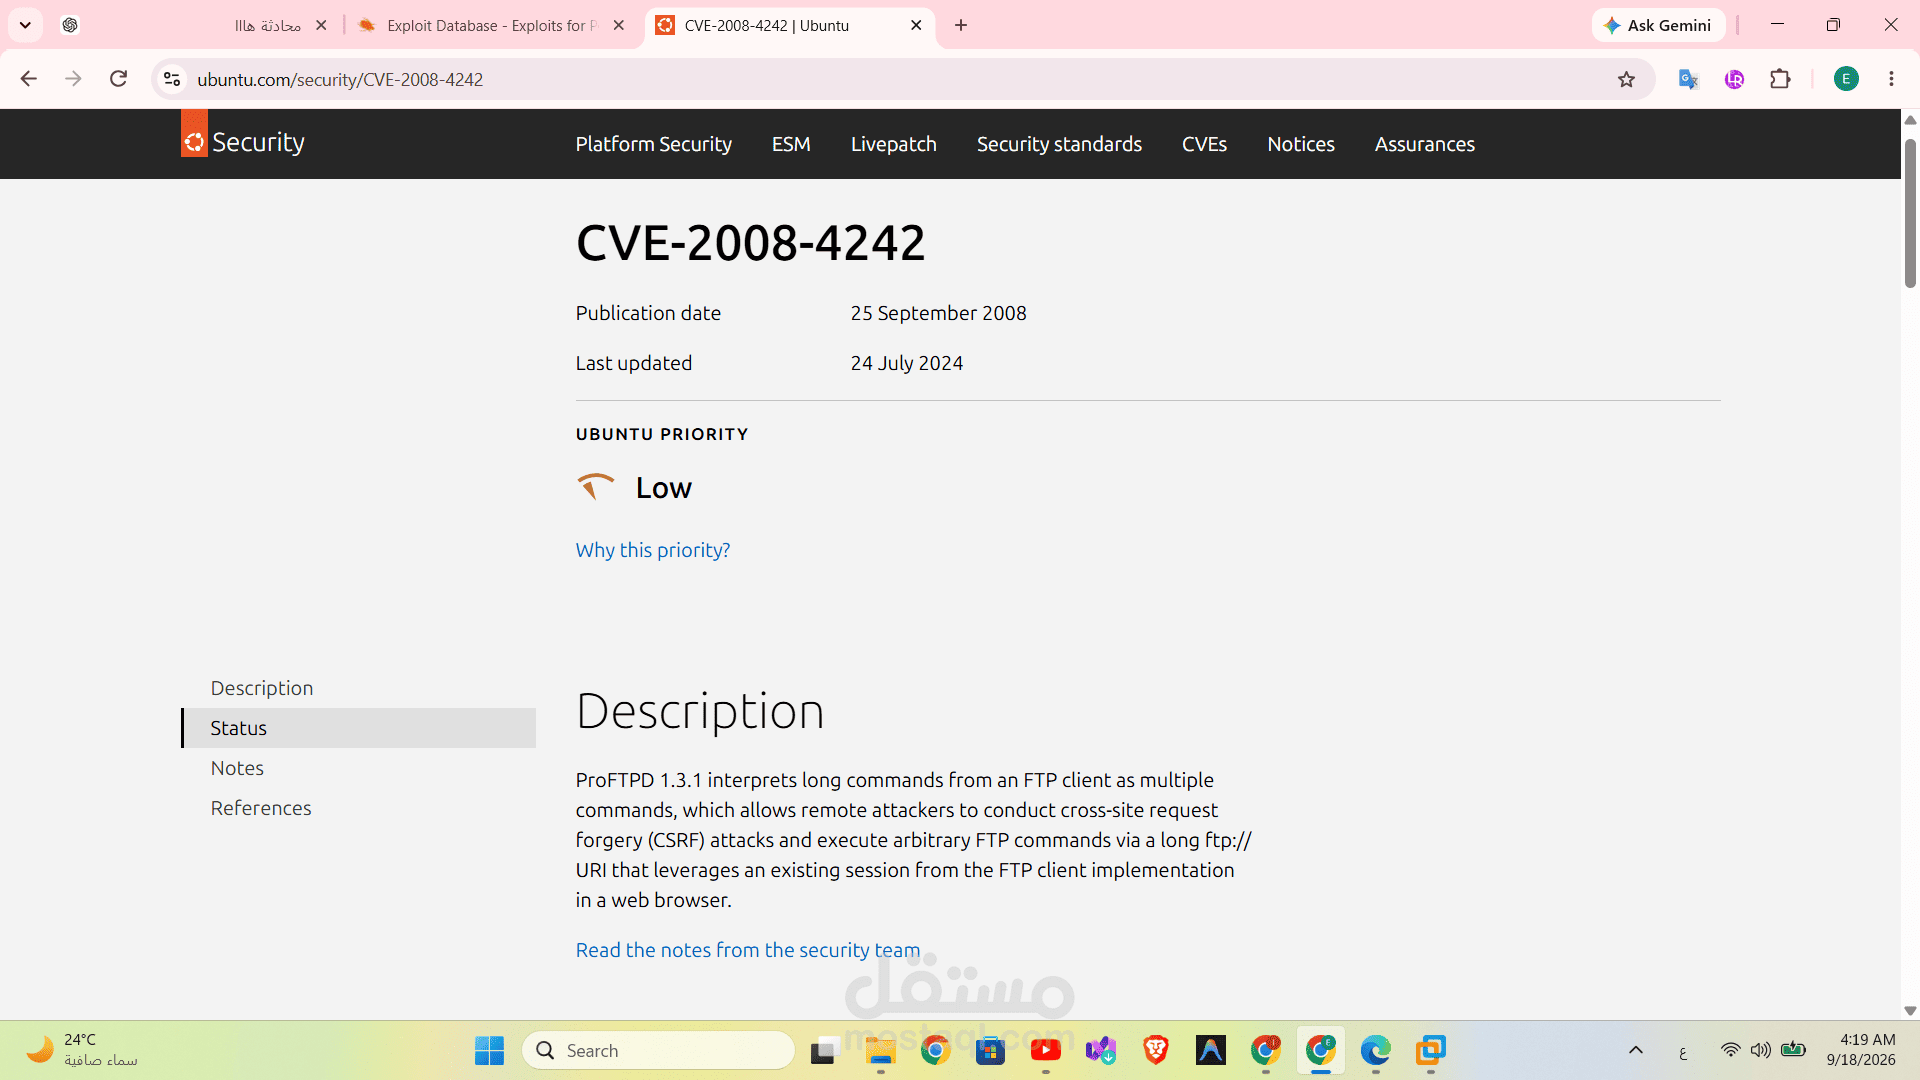
A hands-on cybersecurity lab focused on network reconnaissance, host discovery, service enumeration, and vulnerability research in an authorized controlled environment.
Scope of Work:
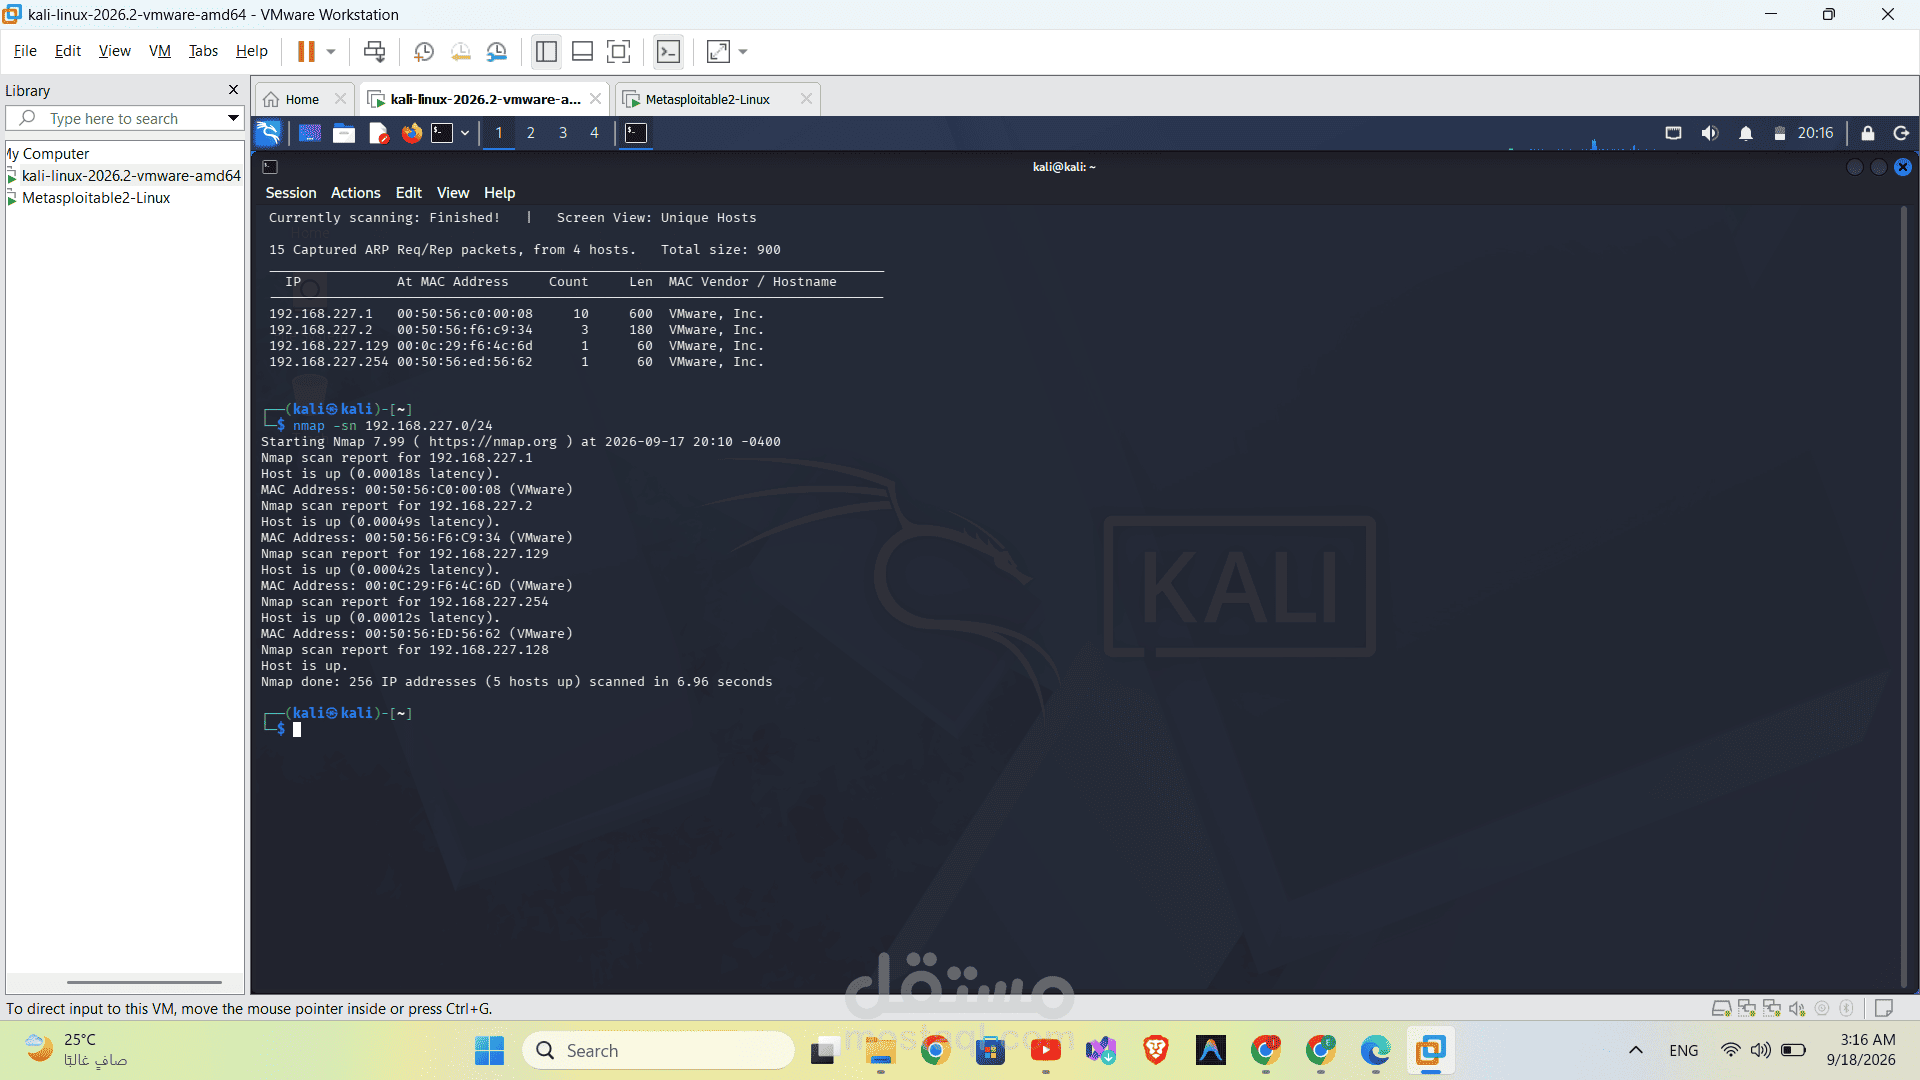
Network interface and connectivity analysis
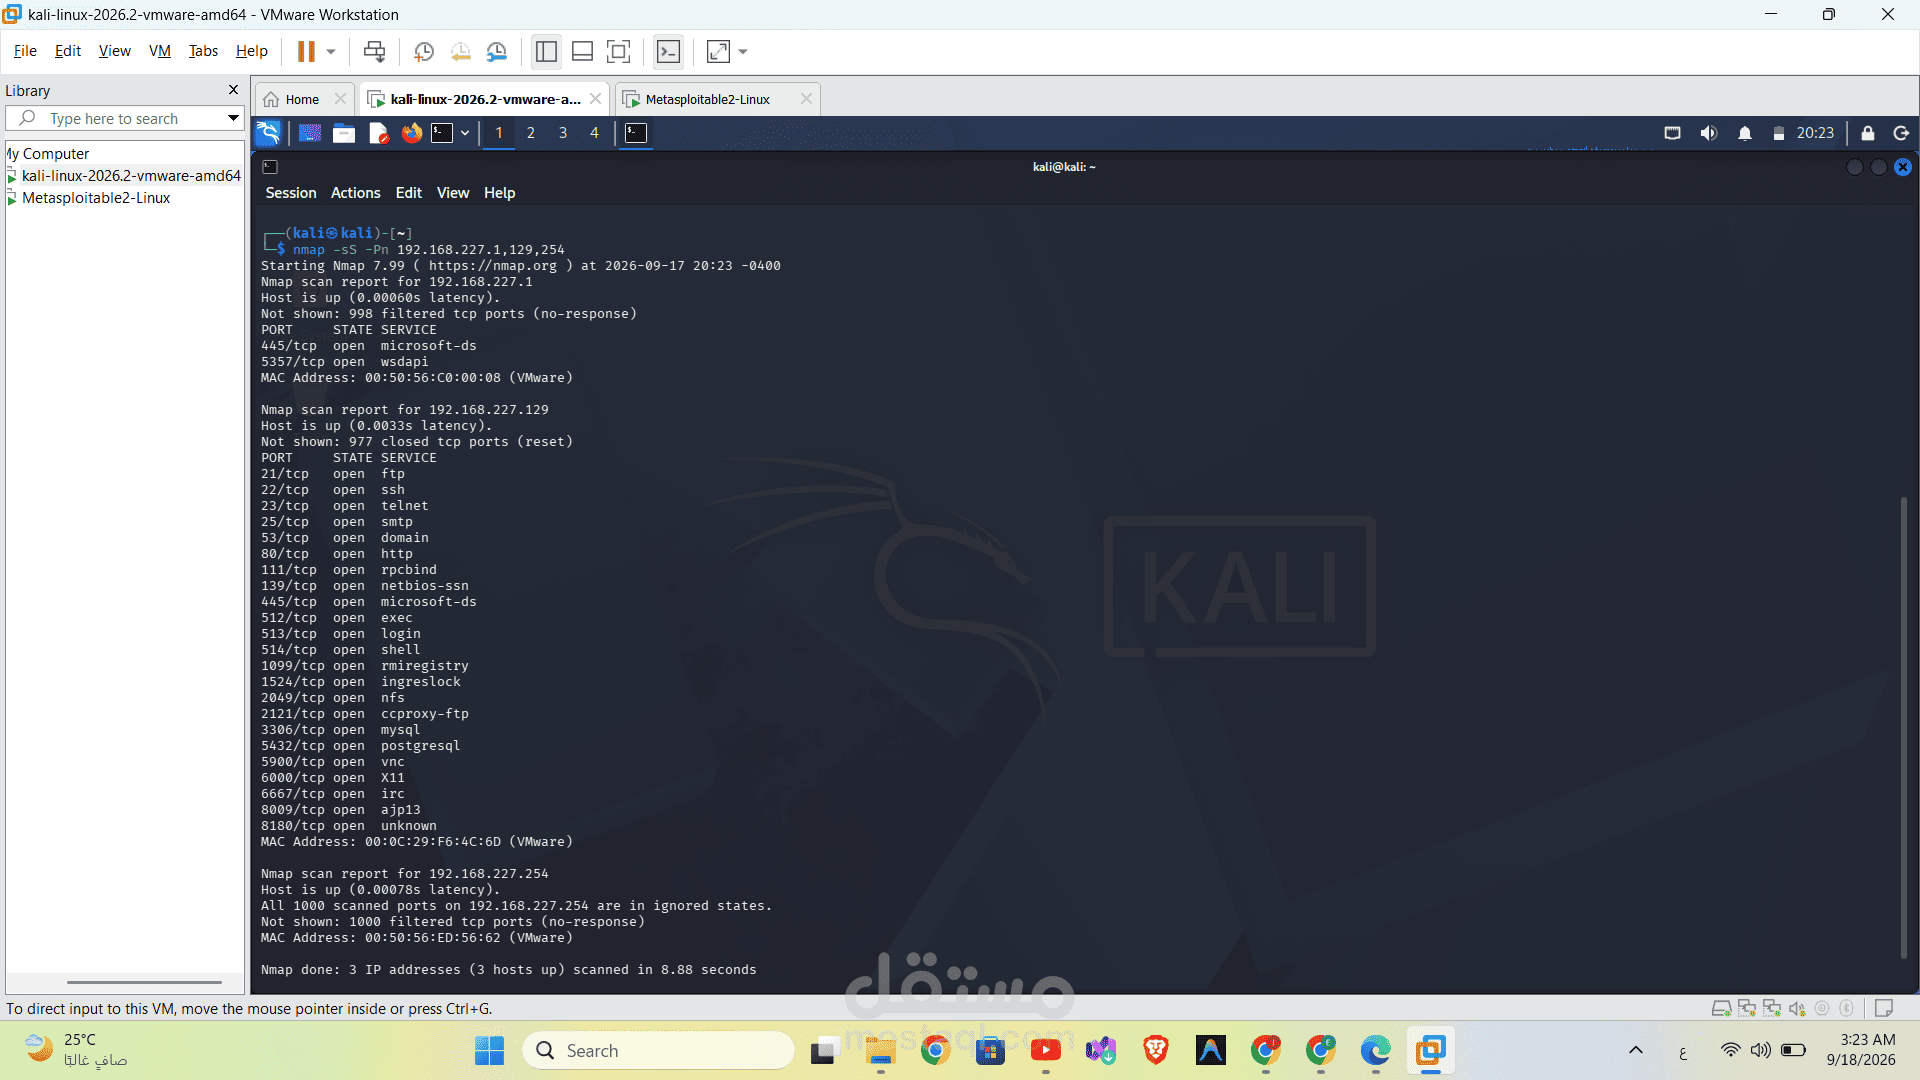
Live host discovery
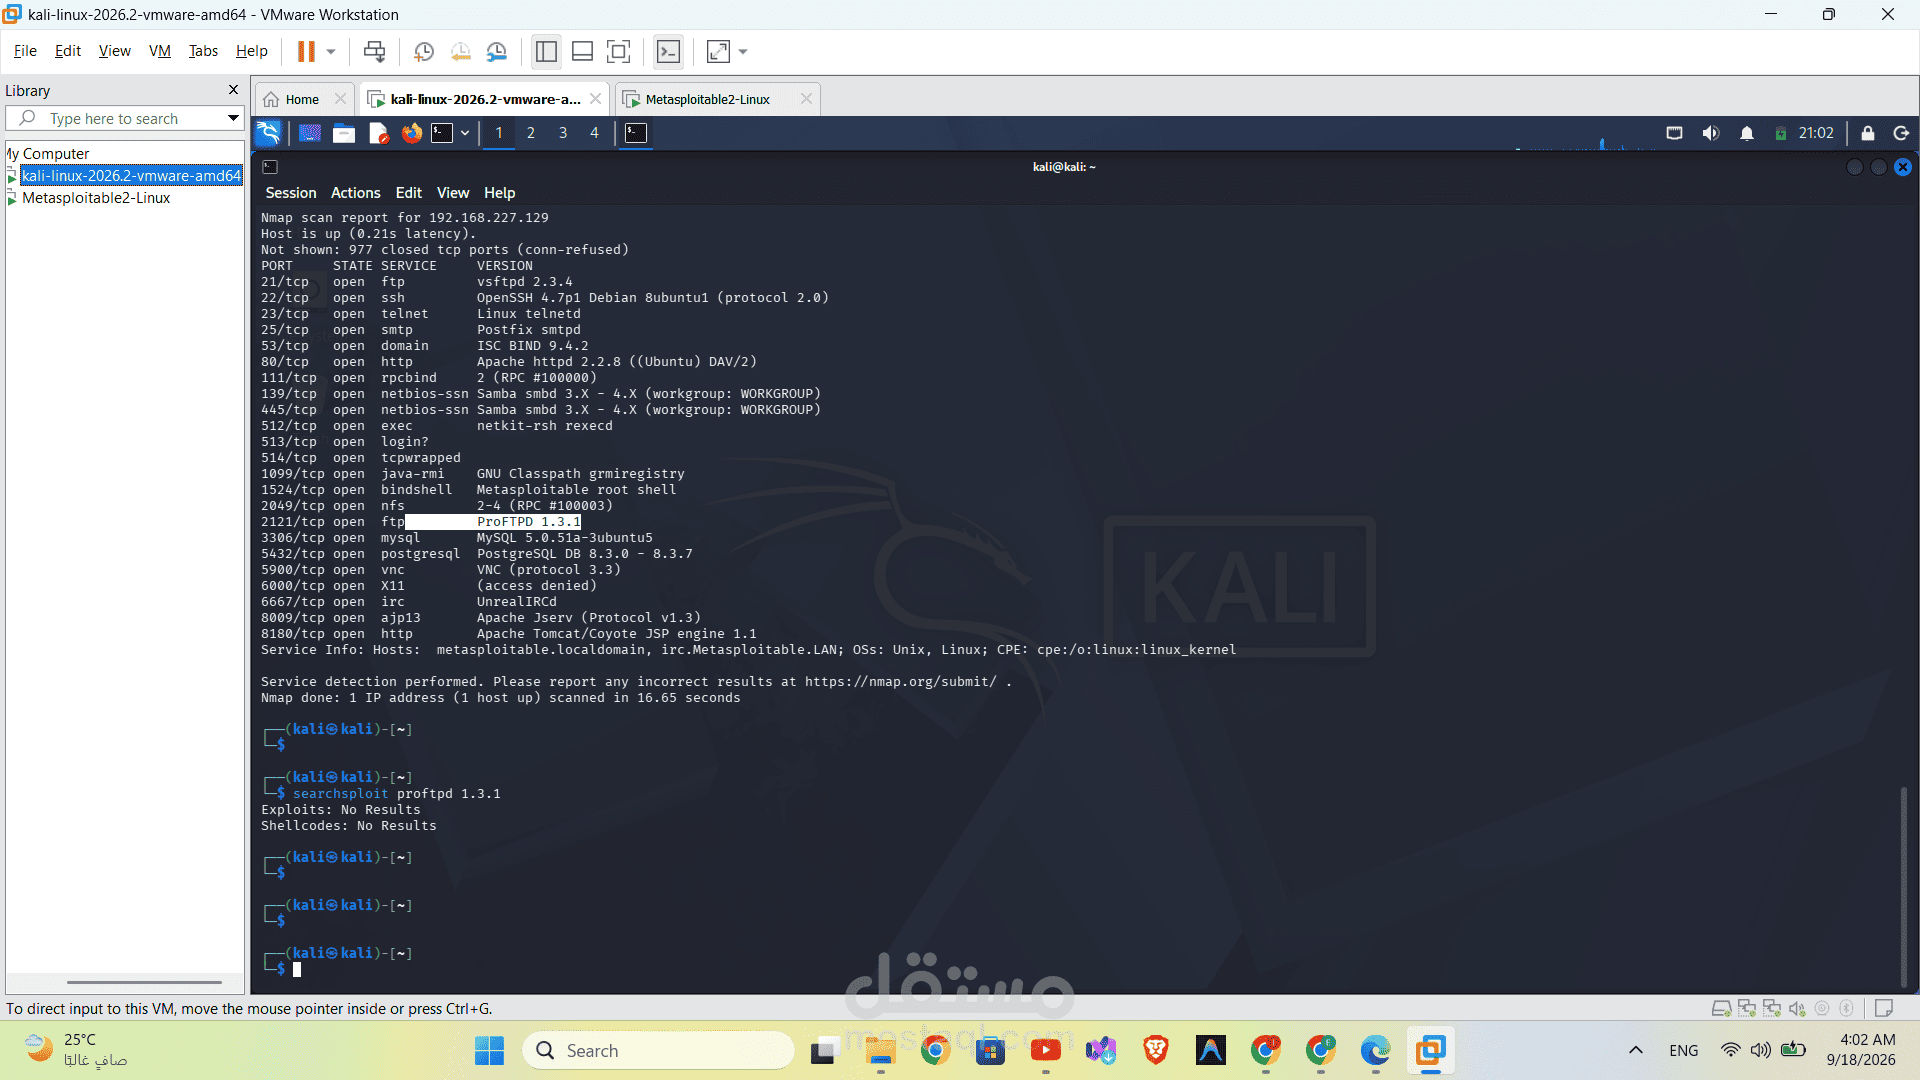
TCP port scanning using Nmap
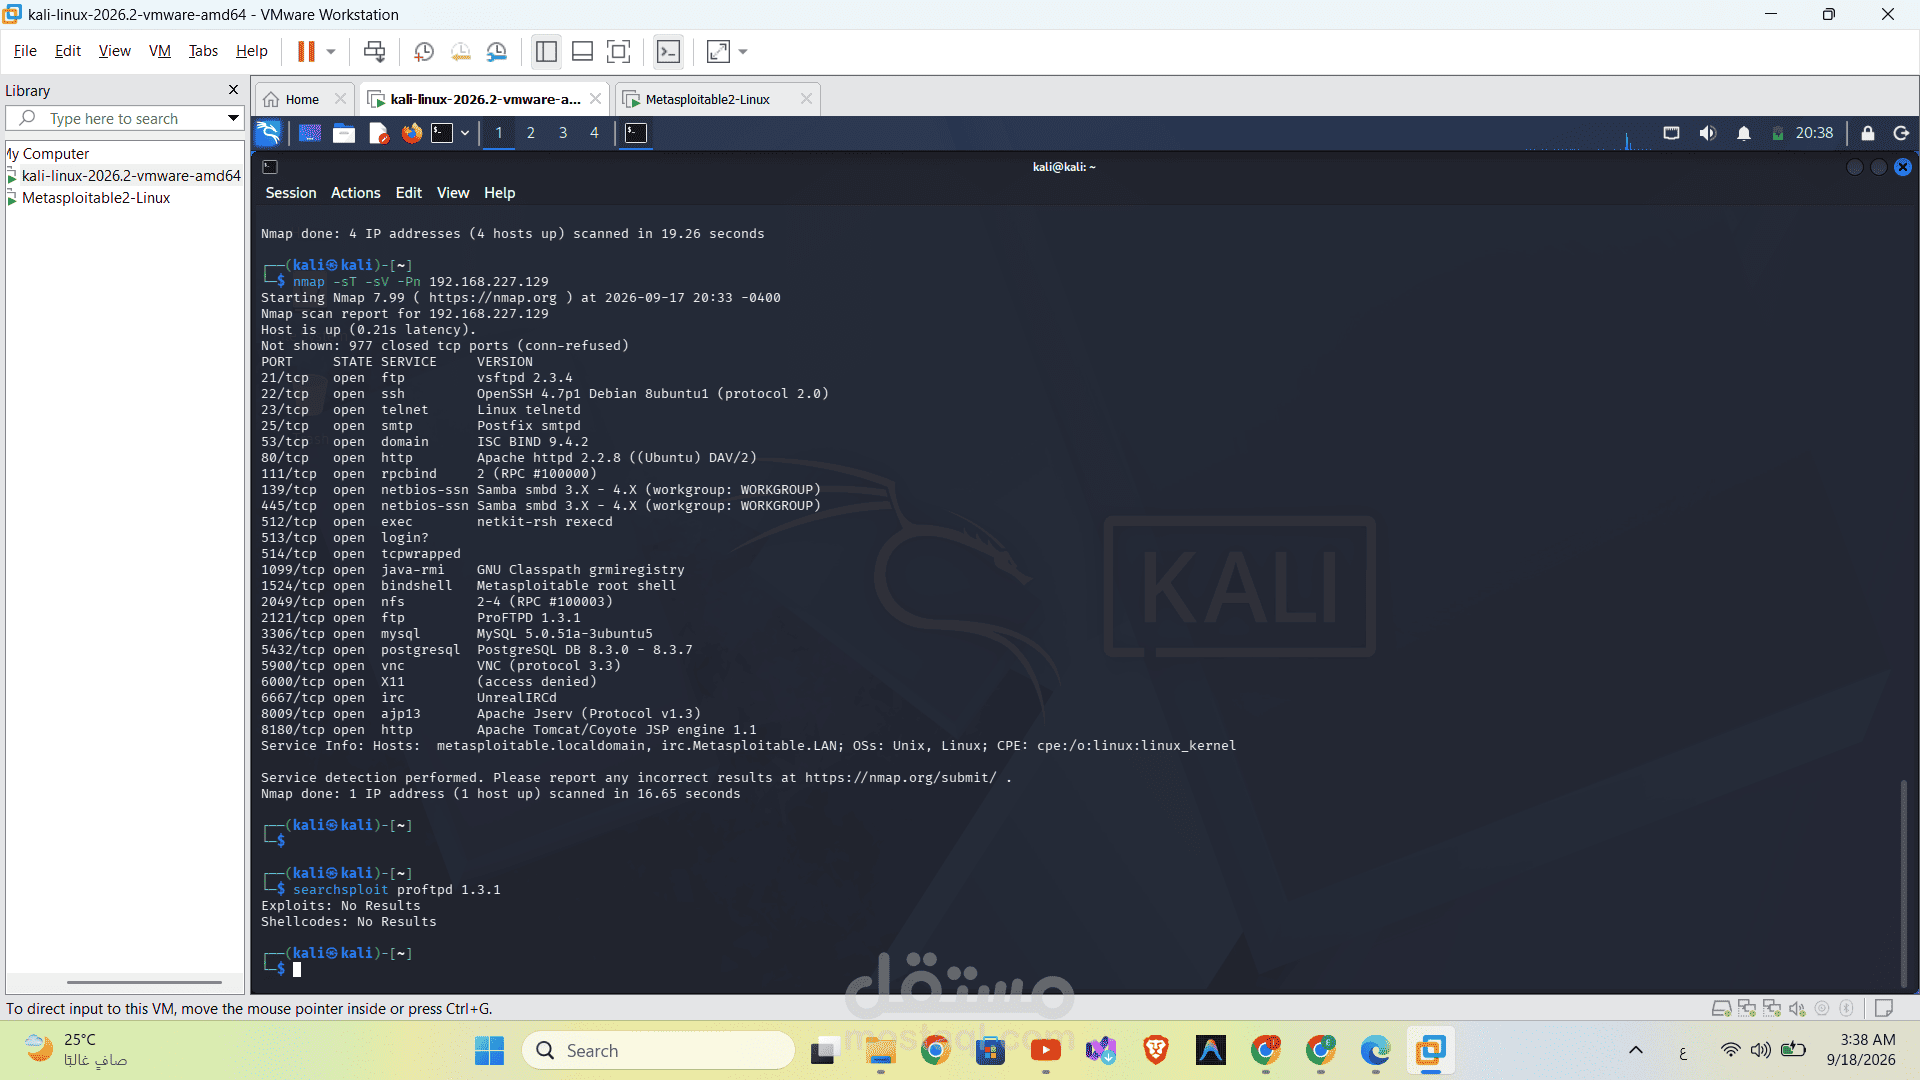
Service and version enumeration
Identification of exposed network services
ProFTPD service identification
Vulnerability research using public security references
Search for relevant exploit information
Documentation of reconnaissance findings
Key Results:
Identified multiple active hosts and exposed services, performed detailed service/version enumeration, and investigated an identified legacy FTP service for relevant vulnerability information.
Environment: Authorized cybersecurity training lab
Focus: Network Reconnaissance • Nmap • Service Enumeration • Vulnerability Research