Network Traffic Analysis Using Wireshark
تفاصيل العمل
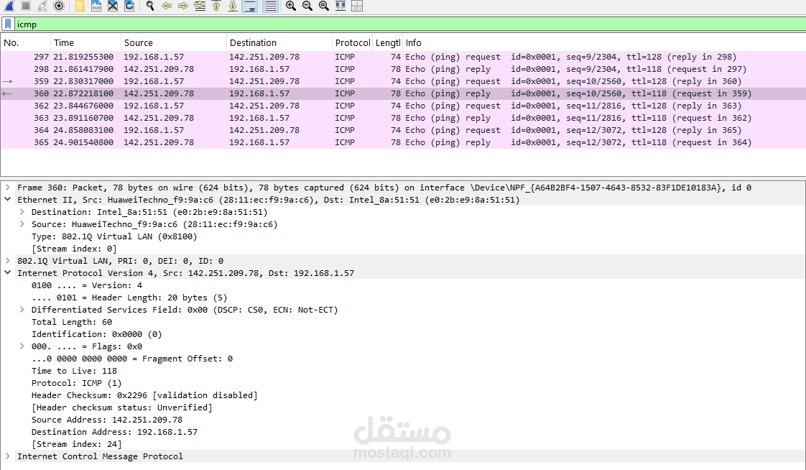
Analyzed real network traffic using Wireshark to understand how data is transmitted across different layers of a network.
- Analyzed Ethernet II frames and examined MAC addresses and protocol types.
- Analyzed IPv4 packet headers and their fields.
- Examined source and destination IP addresses, TTL, protocol, and header information.
- Analyzed TCP segments and studied TCP ports, sequence numbers, acknowledgment numbers, and control flags.
- Identified TCP SYN and SYN-ACK segments during connection establishment.
- Analyzed UDP headers and examined source port, destination port, length, and checksum.
- Used Wireshark filters such as ICMP and TCP to isolate and analyze specific network traffic.
- Worked with real captured packets to understand protocol operation and data encapsulation.