SupportHub Secure Edition — Remediation of 7 Web Vulnerabilities
تفاصيل العمل
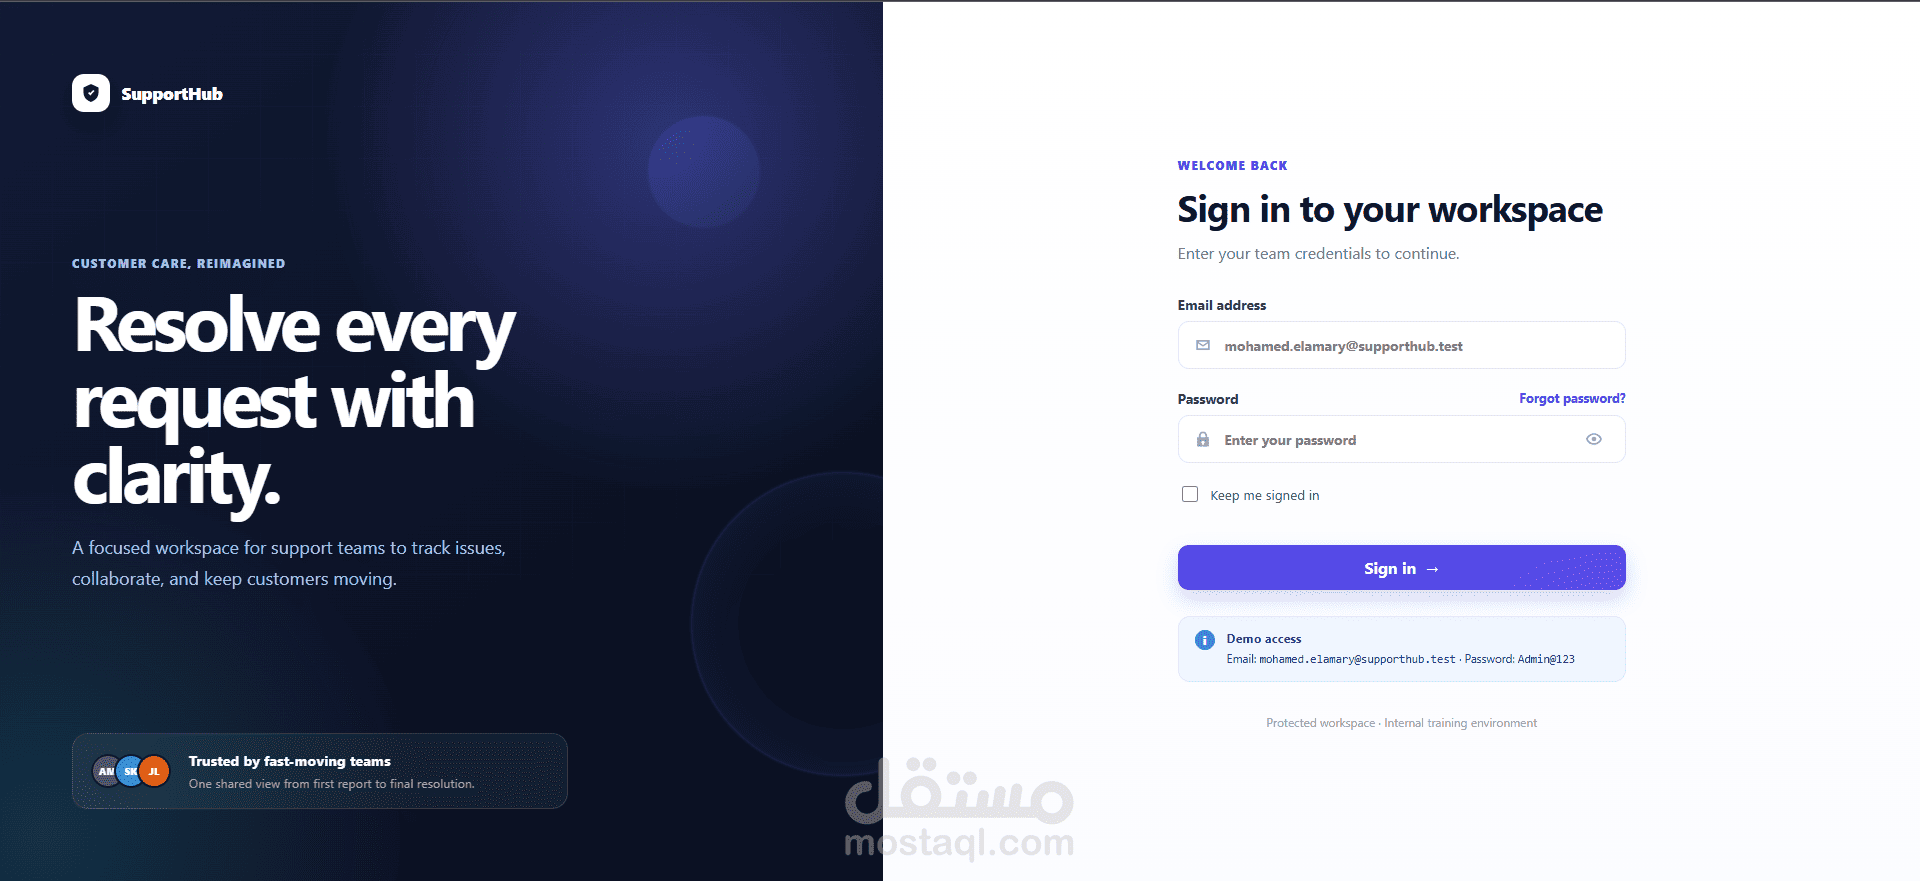
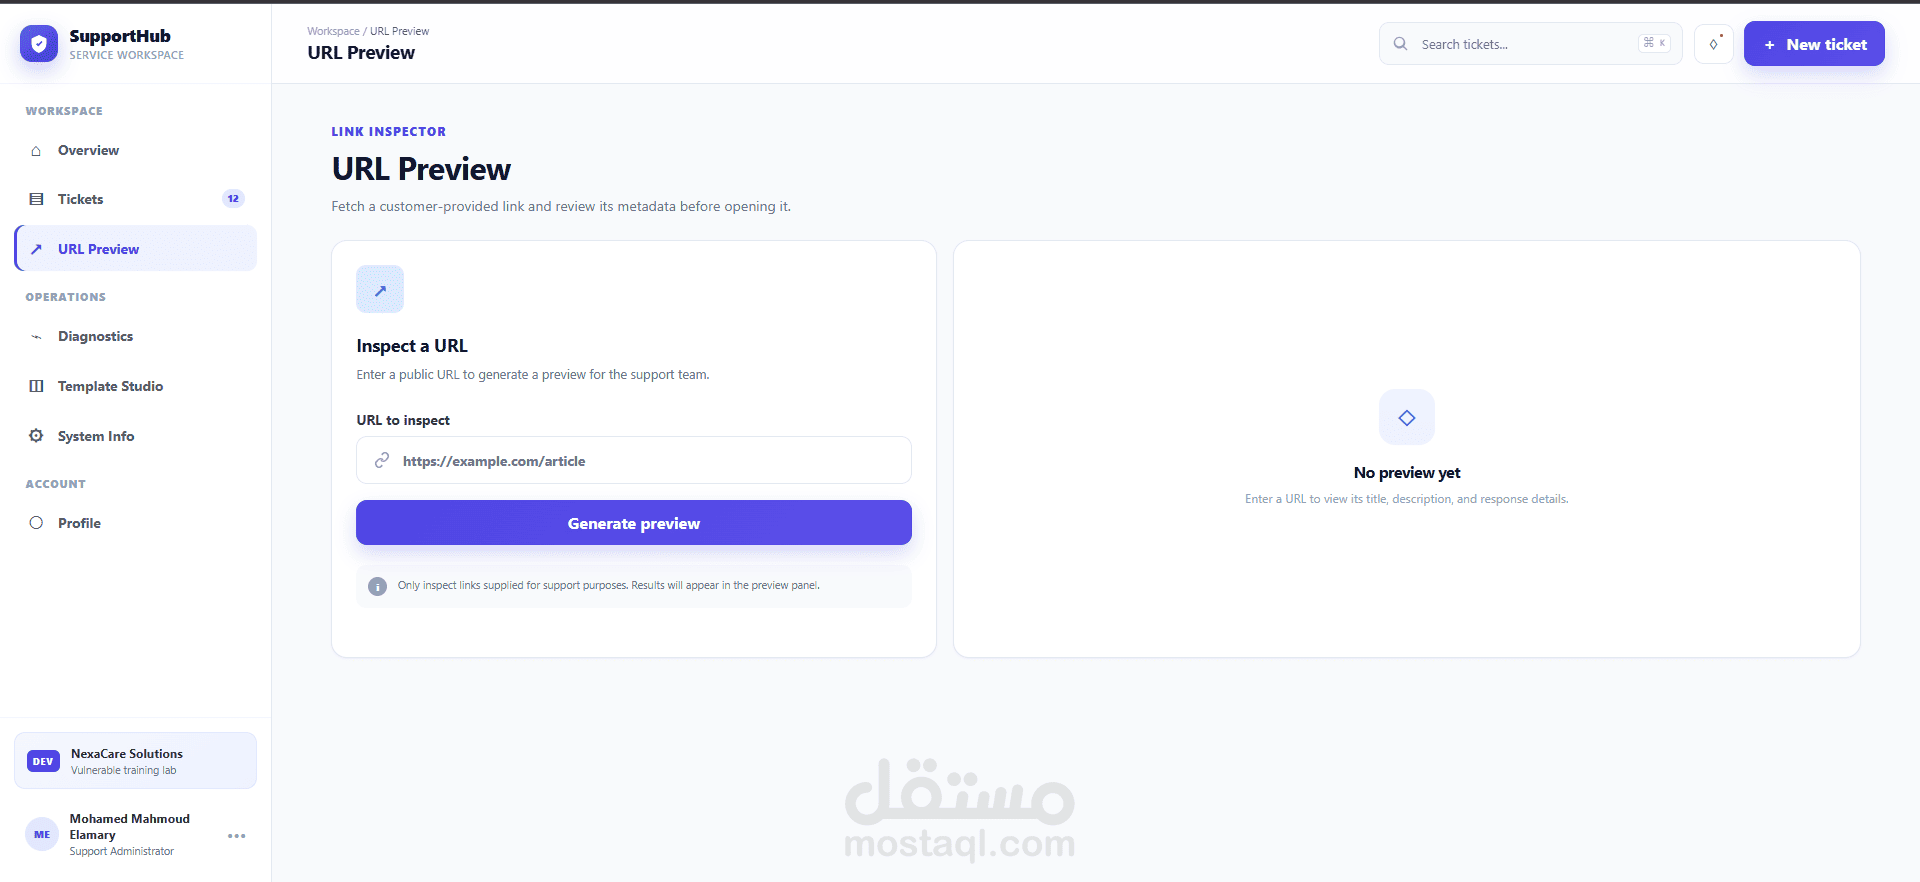
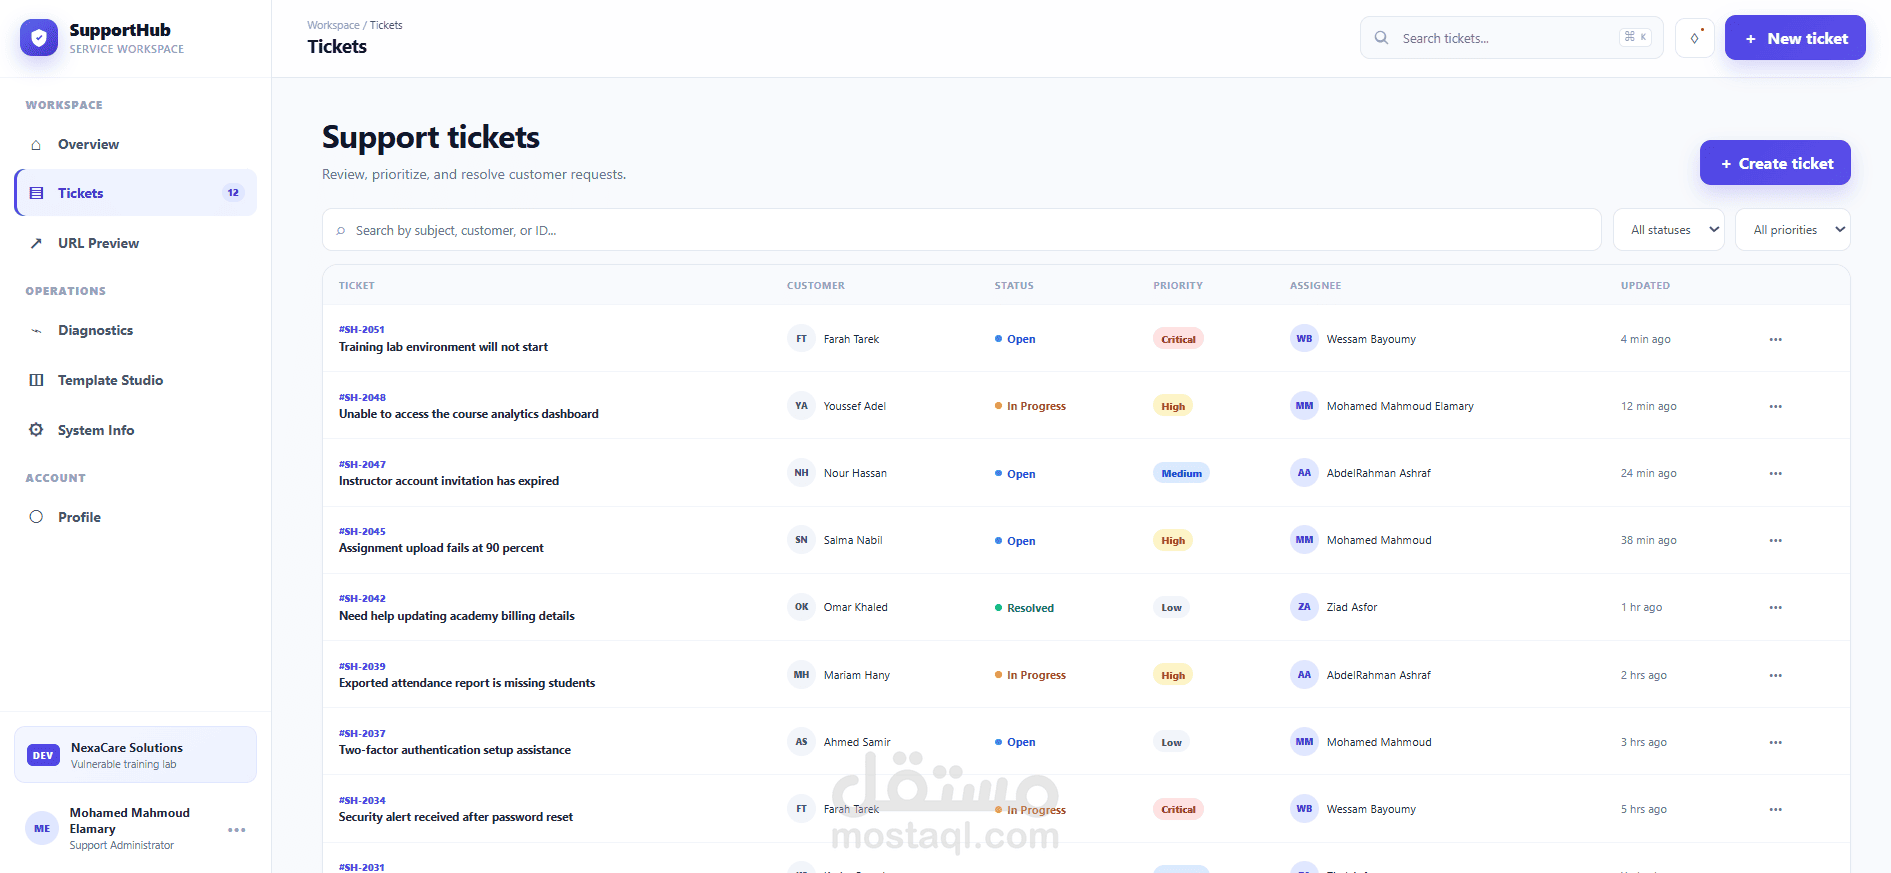
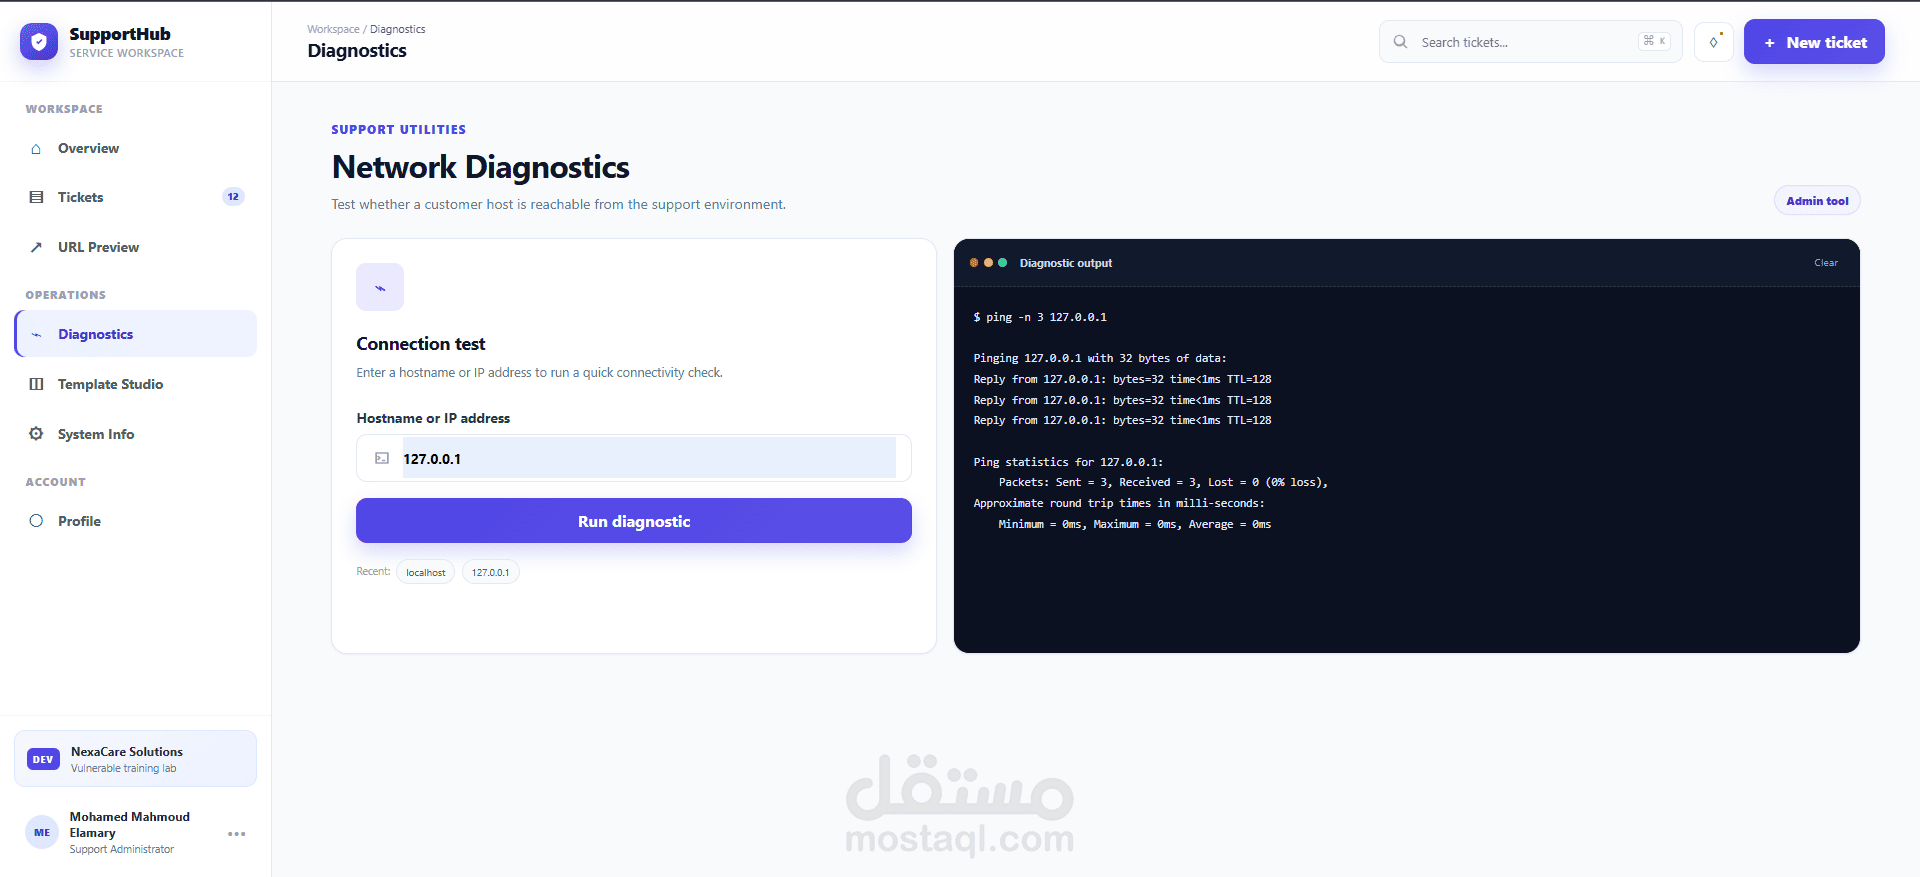
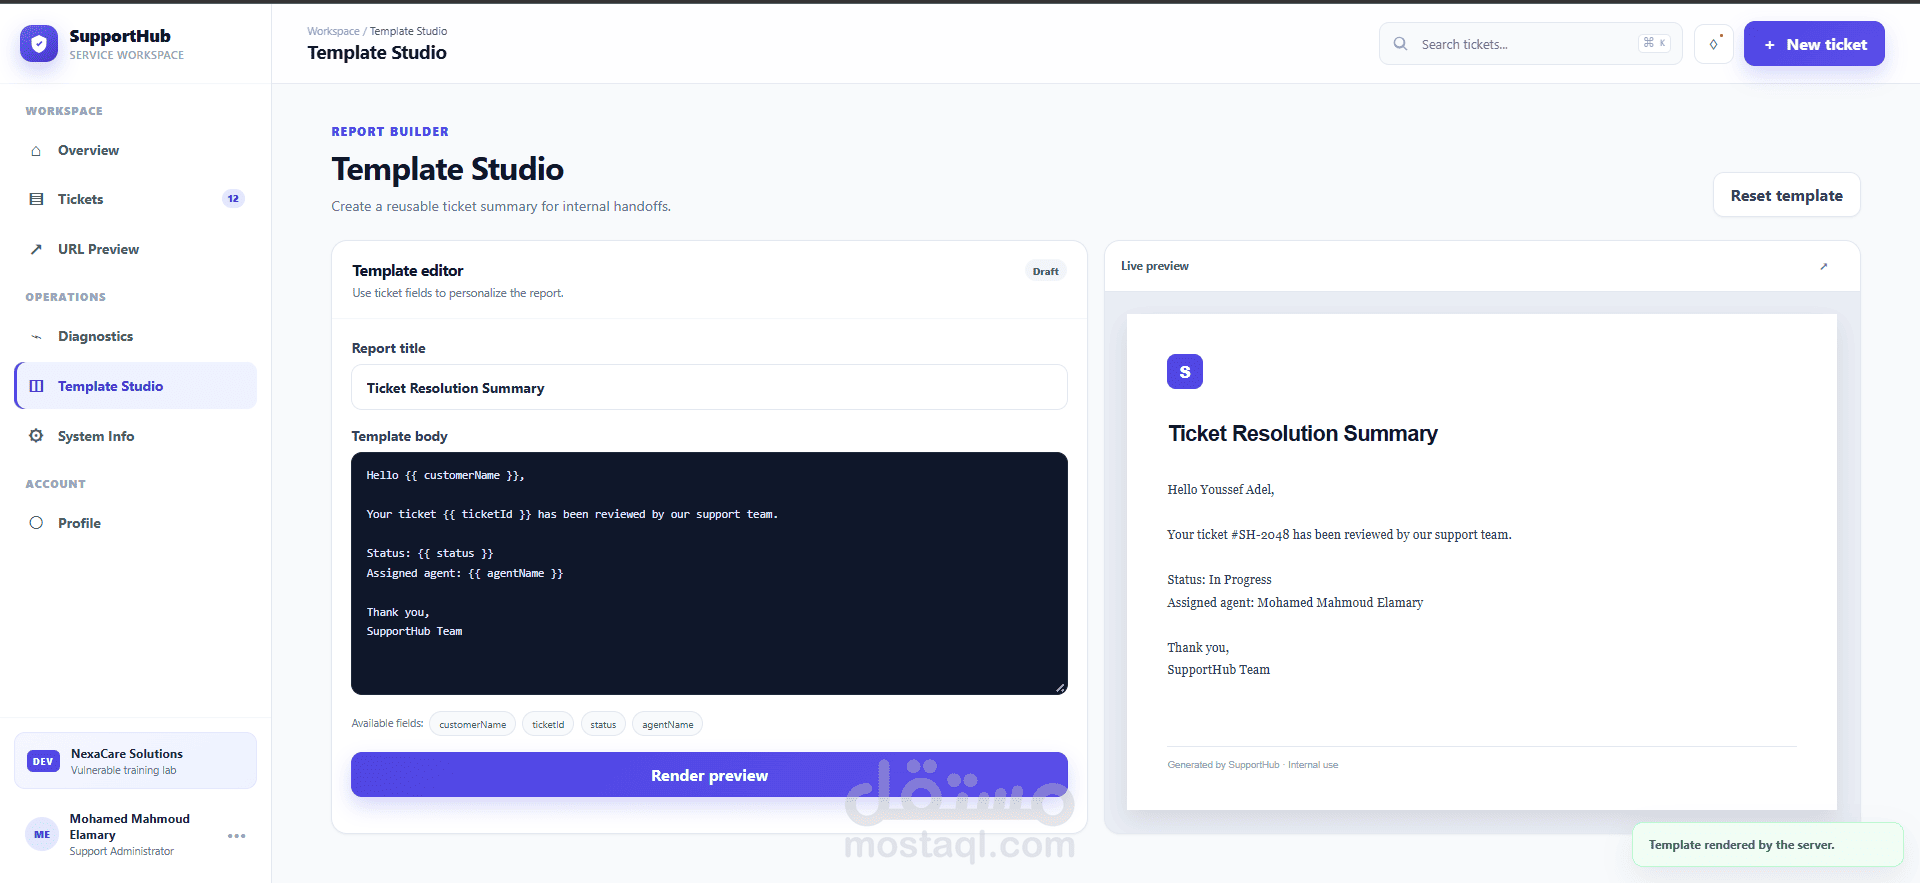
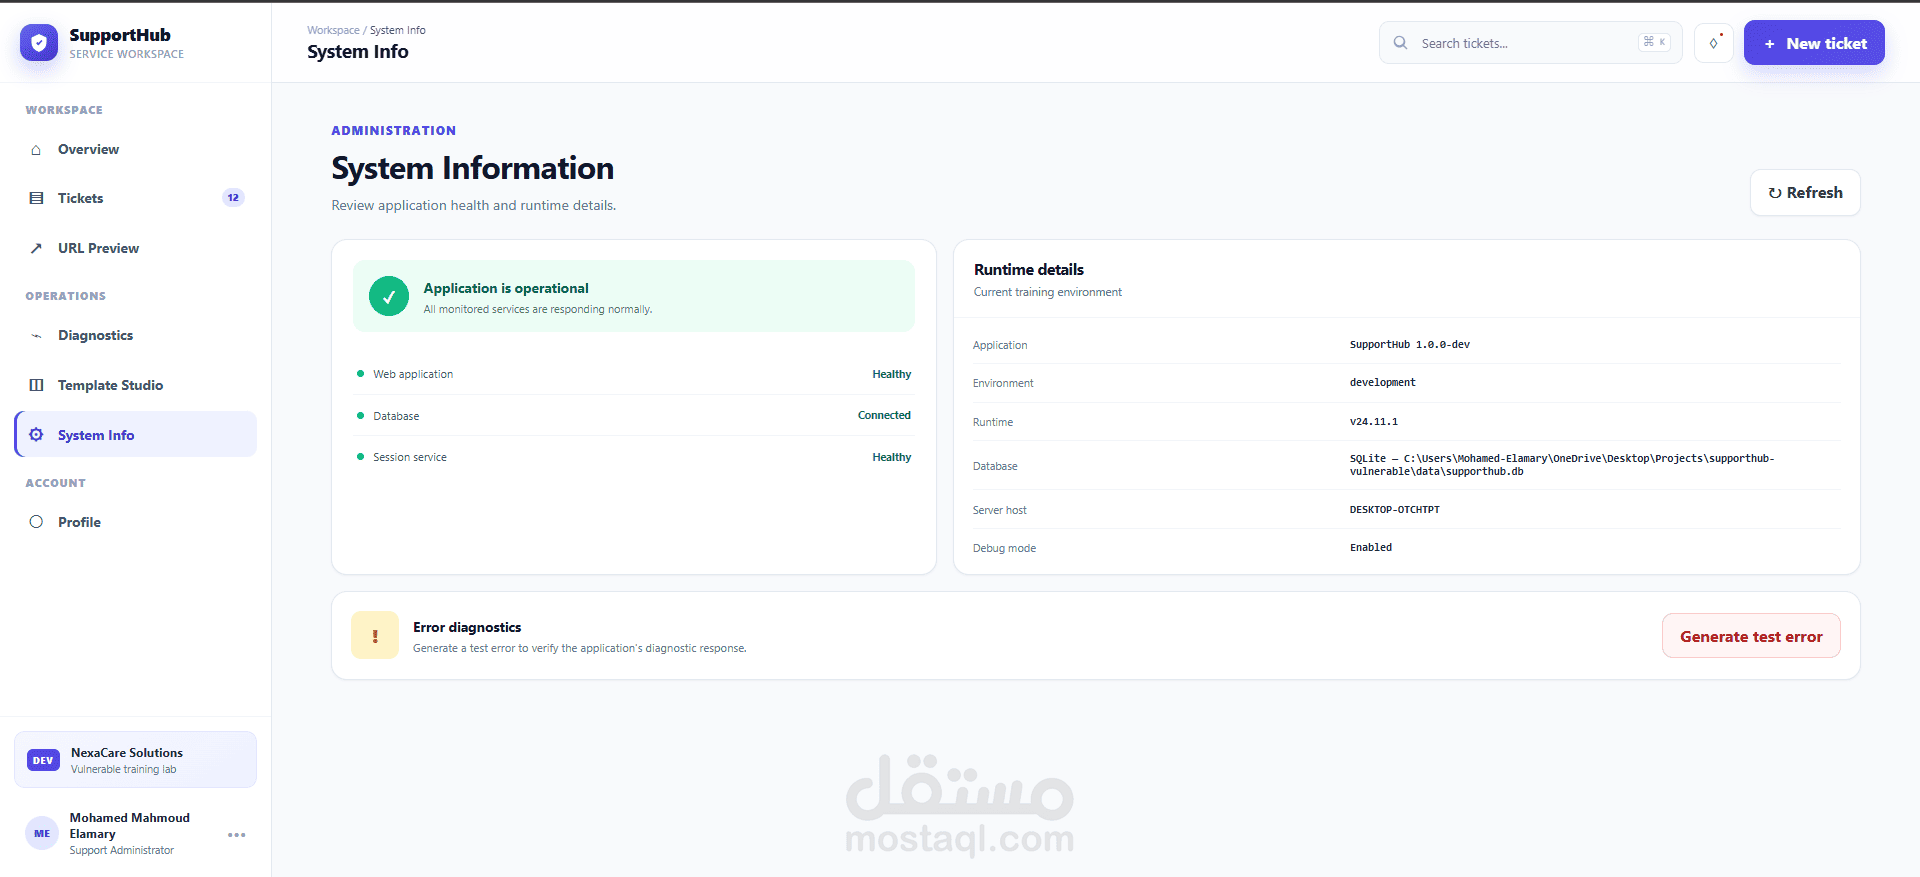
Secured an existing SupportHub web application by remediating seven demonstrated vulnerabilities while preserving its core features and user interface. This project is the remediation-focused counterpart to my vulnerable application security lab, maintained in a separate GitHub repository.
Built with Node.js, Express, SQLite, HTML, CSS, and JavaScript, the application includes authentication, a support dashboard, ticket conversations, and template-based reports.
Security improvements:
• SQL Injection: Replaced unsafe queries with parameterized statements.
• Information Disclosure: Reduced exposed internal details and improved error handling.
• OS Command Injection: Restricted command execution and validated input.
• CSRF: Added protection against forged state-changing requests.
• SSRF: Validated destination URLs and restricted access to disallowed network targets.
• SSTI: Replaced general-purpose template evaluation with allowlisted placeholder rendering.
• Stored XSS: Replaced unsafe comment rendering with safe DOM construction and textContent, supported by Content Security Policy.
Verification and deliverables:
• Retested the original proof-of-concept exploits and verified legitimate application behavior after each fix.
• Performed syntax checks and ran automated SQL Injection regression tests.
• Preserved vulnerable code as inactive, commented references explaining the original issues and their remediation.
• Documented each fix with technical explanations, verification steps, and screenshot evidence.
• Published the secured source code and remediation documentation in a dedicated GitHub repository with tracked commits.
The result is a demonstrable remediation of all seven targeted vulnerabilities, showcasing secure coding, code review, regression testing, and clear technical documentation.