SOC Alert Investigation & Incident Analysis
تفاصيل العمل
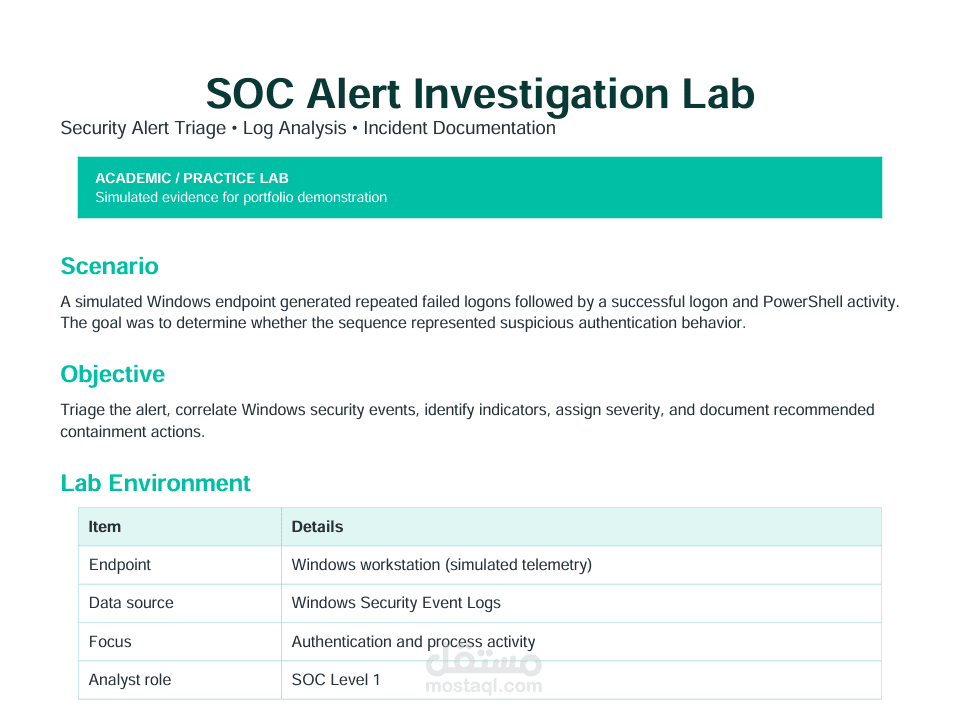
Conducted a simulated SOC investigation of suspicious authentication activity. Analyzed Windows Security Event Logs, correlated failed and successful logons, reviewed PowerShell activity, assessed severity, and documented recommended containment and response actions.