Network Security & Defense Lab
تفاصيل العمل
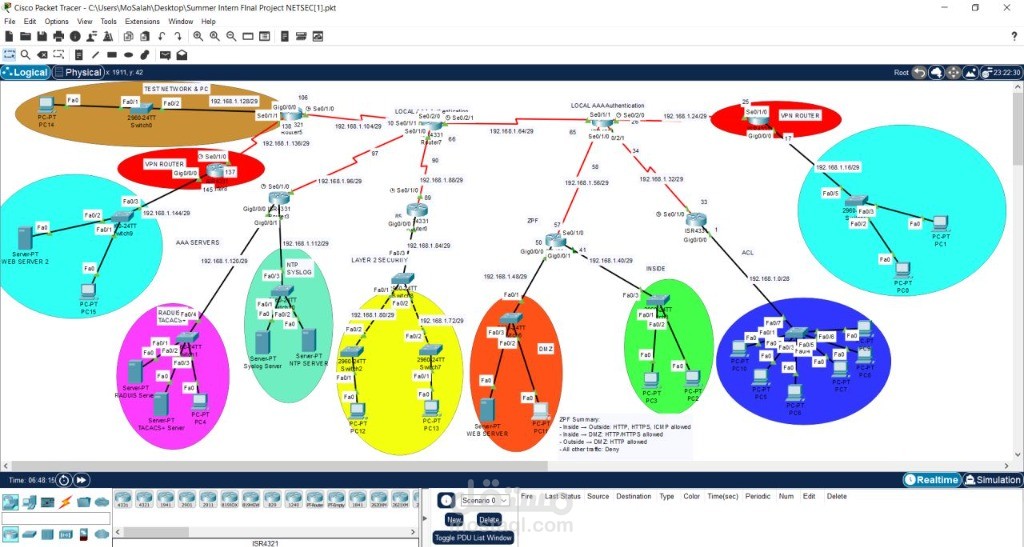
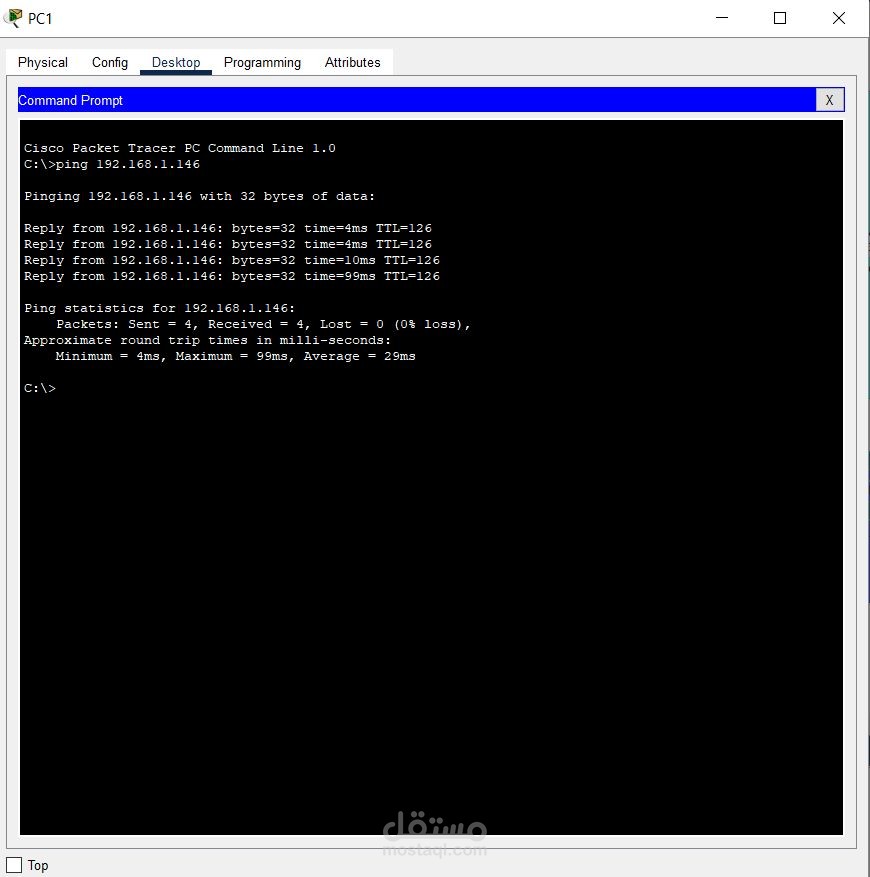
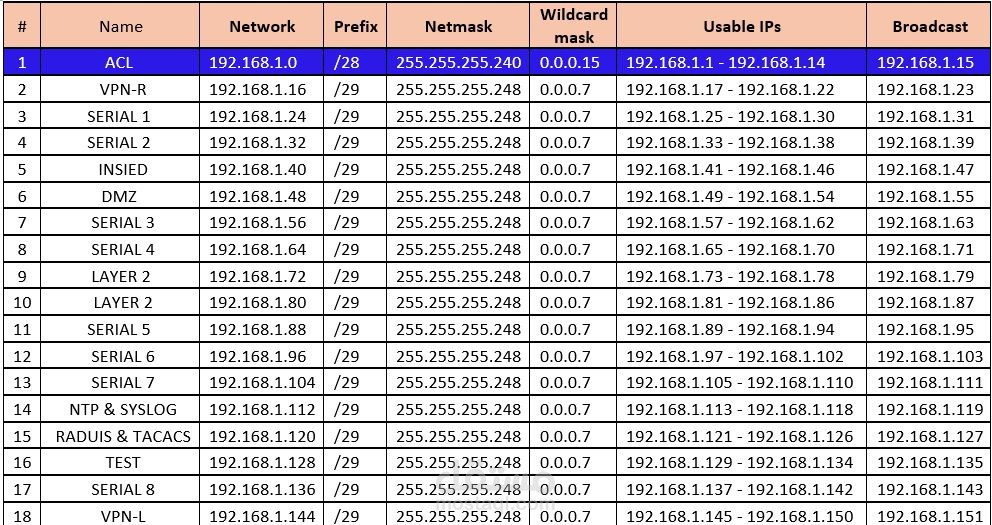
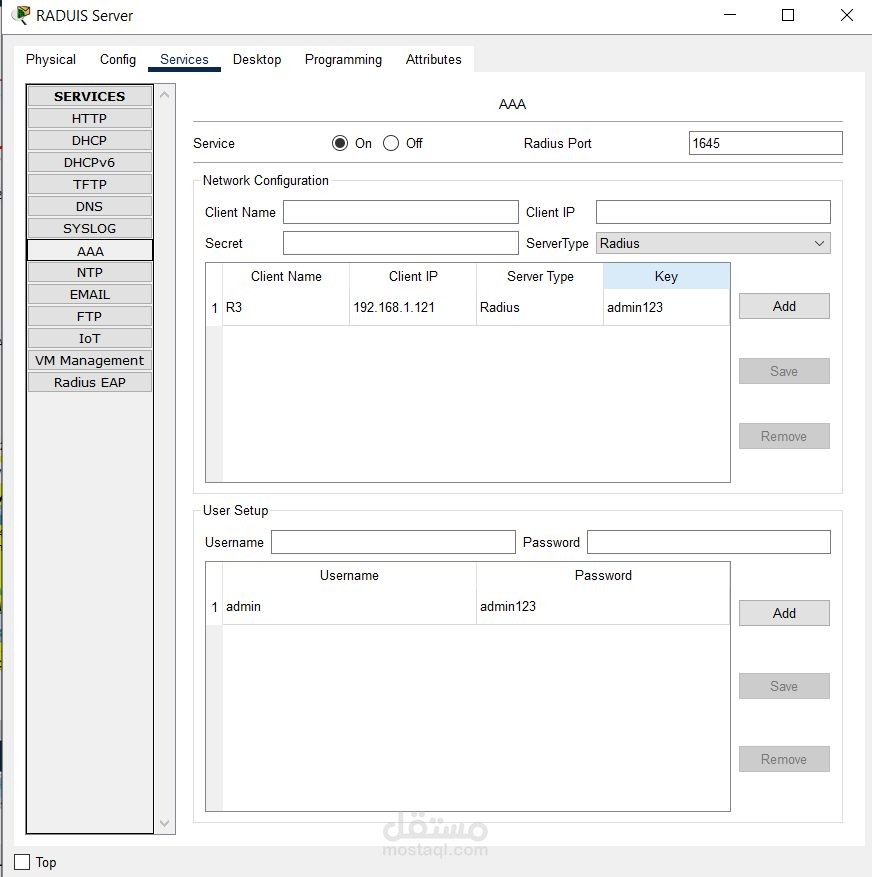
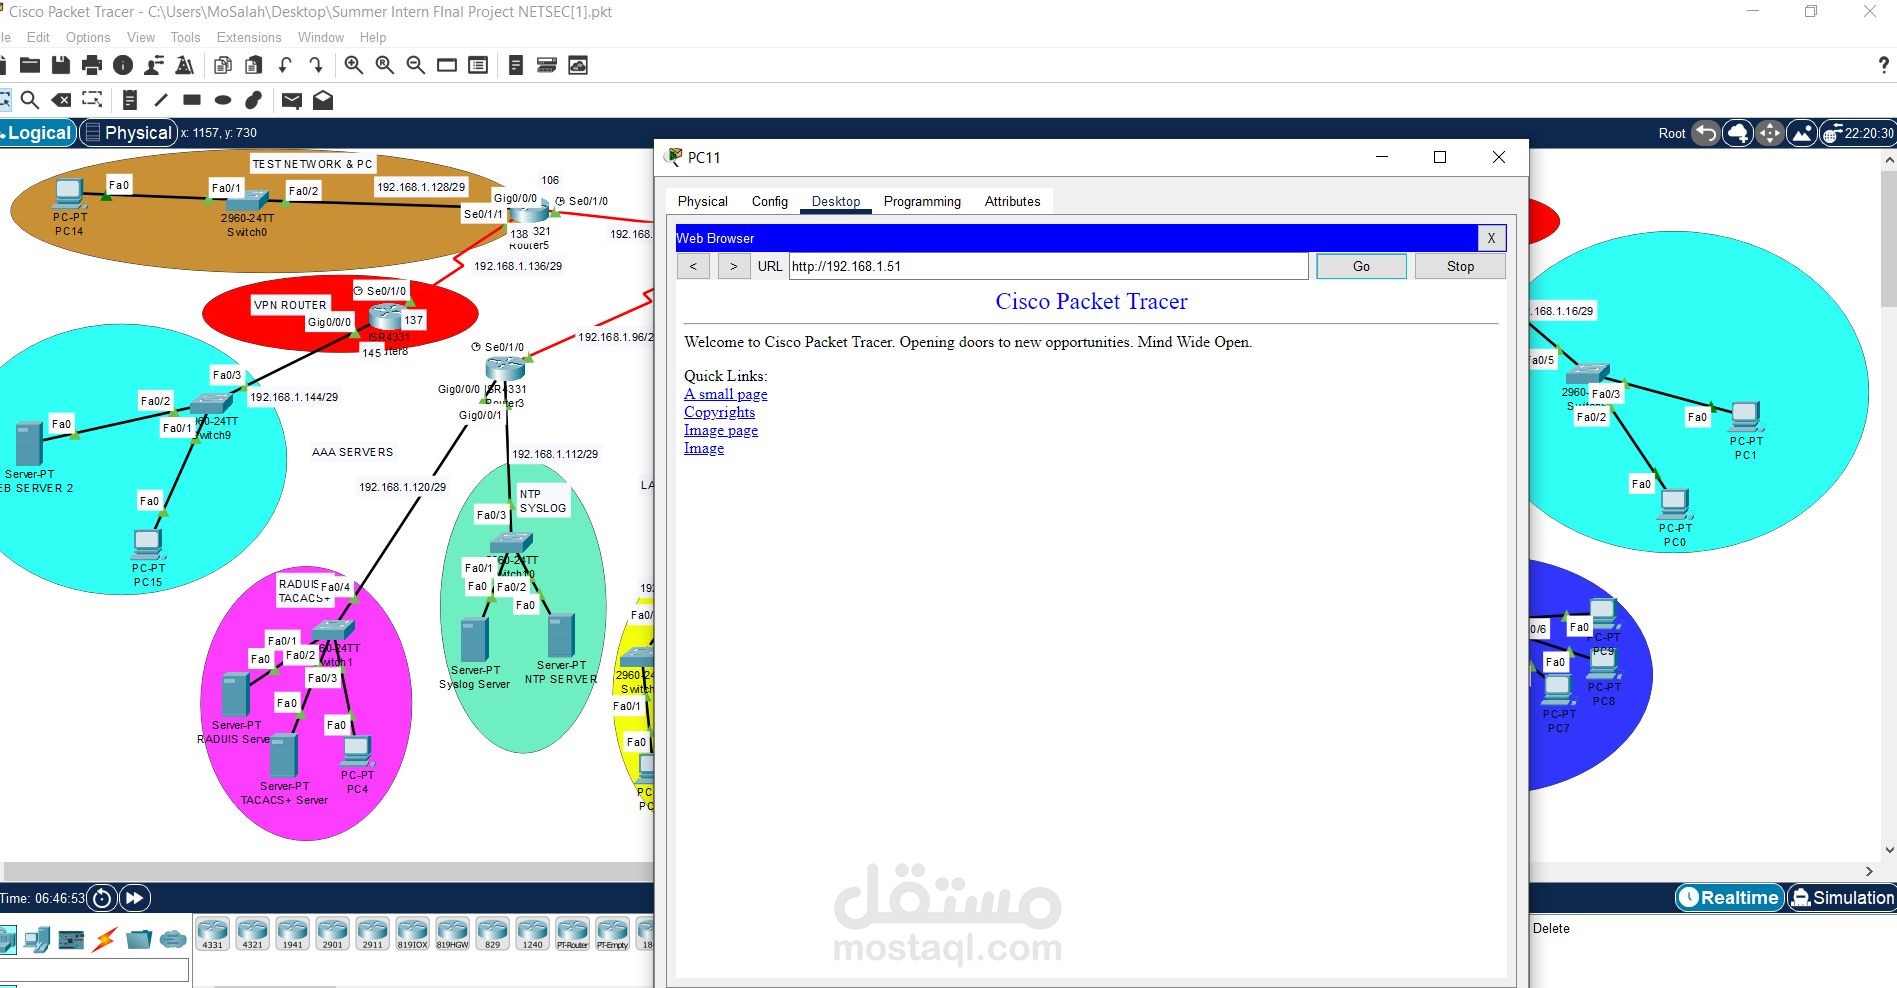
Key Areas Explored:
• تأمين إدارة أجهزة الشبكة باستخدام Cryptographic SSH وRobust Secret Keys.
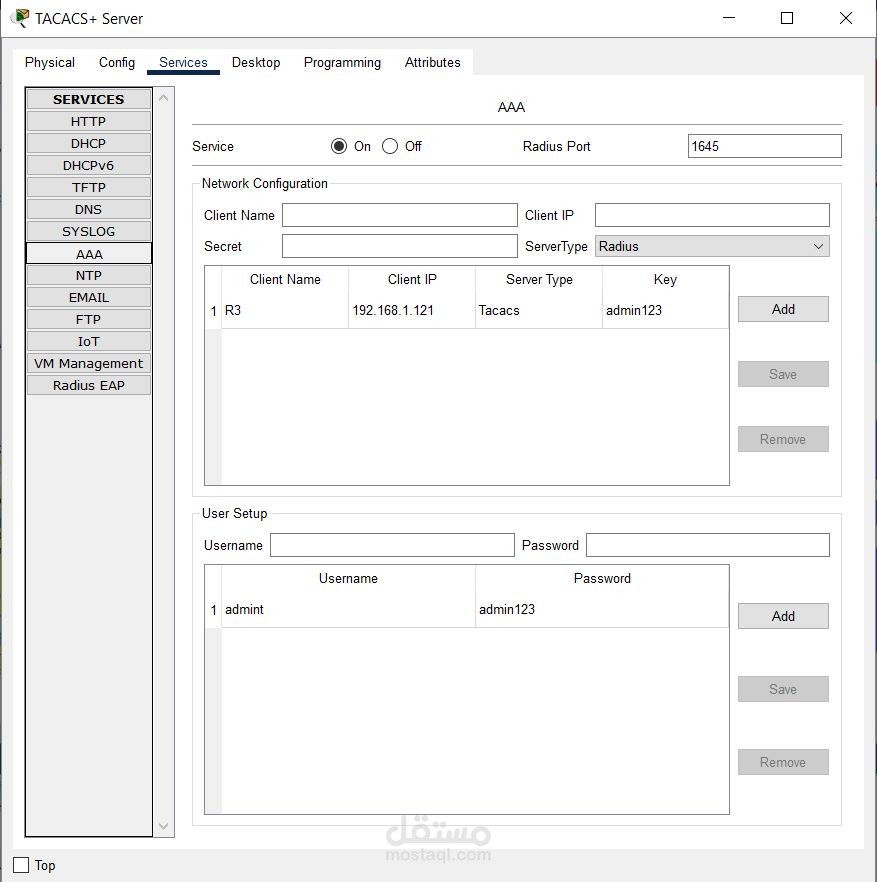
• تطبيق مفاهيم AAA (Authentication, Authorization, Accounting) Framework.
• تطبيق Standard وExtended Access Control Lists للتحكم الدقيق في Packet Filtering.
• إعداد Anti-Spoofing Controls لمنع Source Addresses غير المشروعة.
• تطبيق Granular Traffic Filtering Rules لحماية Sensitive Subnet Ranges.
• محاكاة مفاهيم IPsec VPN Site-to-Site Encrypted Tunnel.
• استكشاف Zone-Based Firewall (ZBF) Architectures وتطبيق Zone-Pair Inspection Rules.
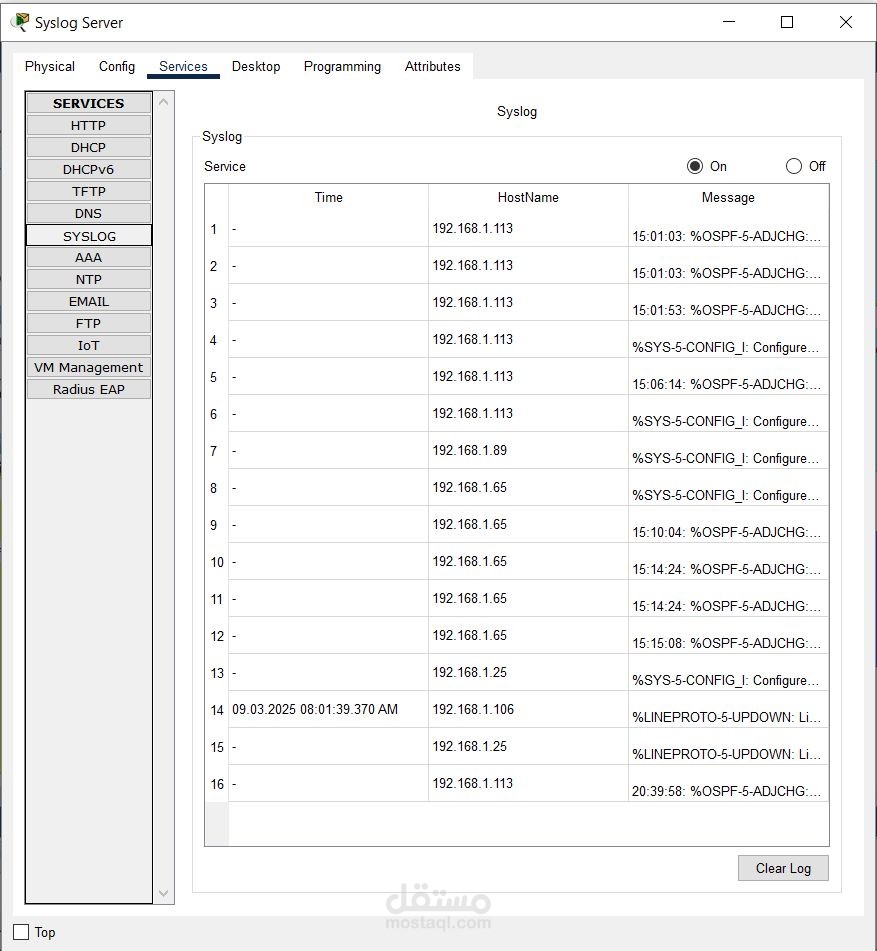
• مزامنة أجهزة الشبكة باستخدام NTP وتطبيق Centralized Syslog Logging لإنشاء Audit Trails.
• تنفيذ Security-Focused Troubleshooting وBoundary Penetration Testing.
/My Portfolio :- https://mohamedsalah11.ve...