Torma – Automated Bug Bounty Recon & Vulnerability Scanner
تفاصيل العمل
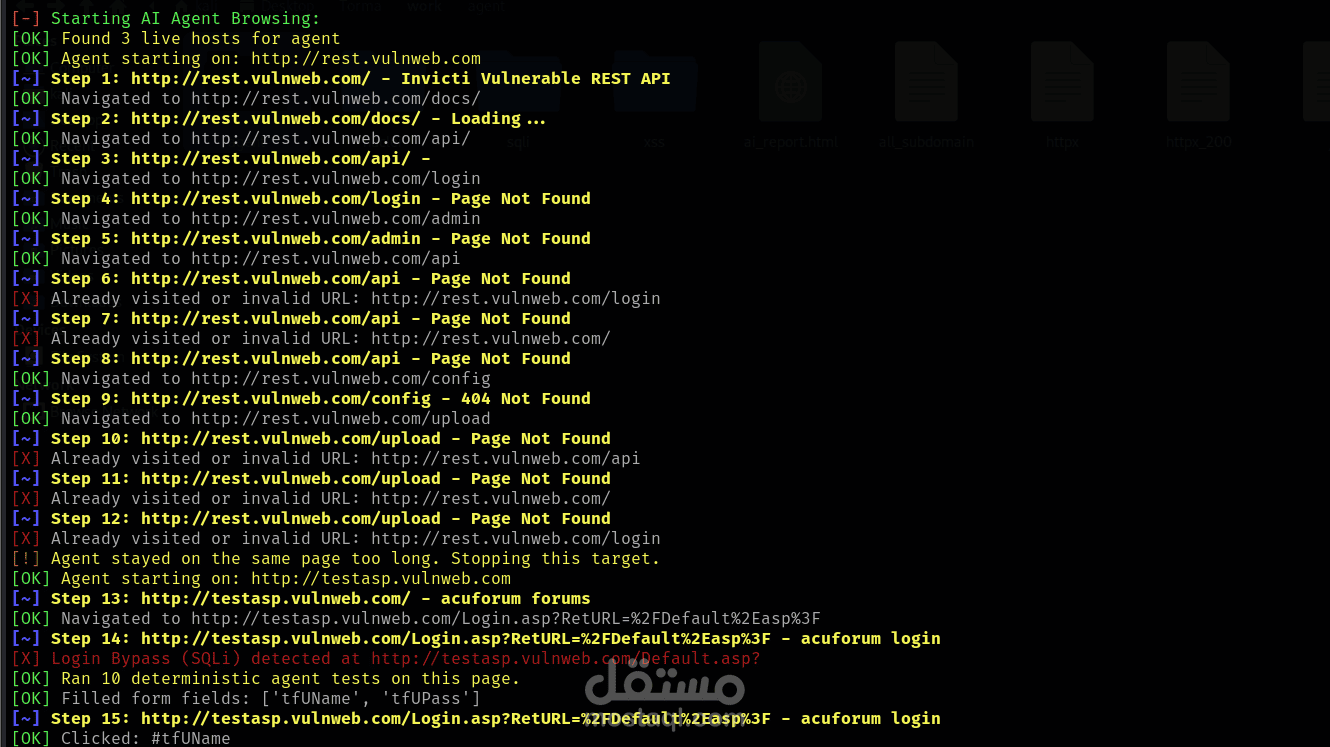
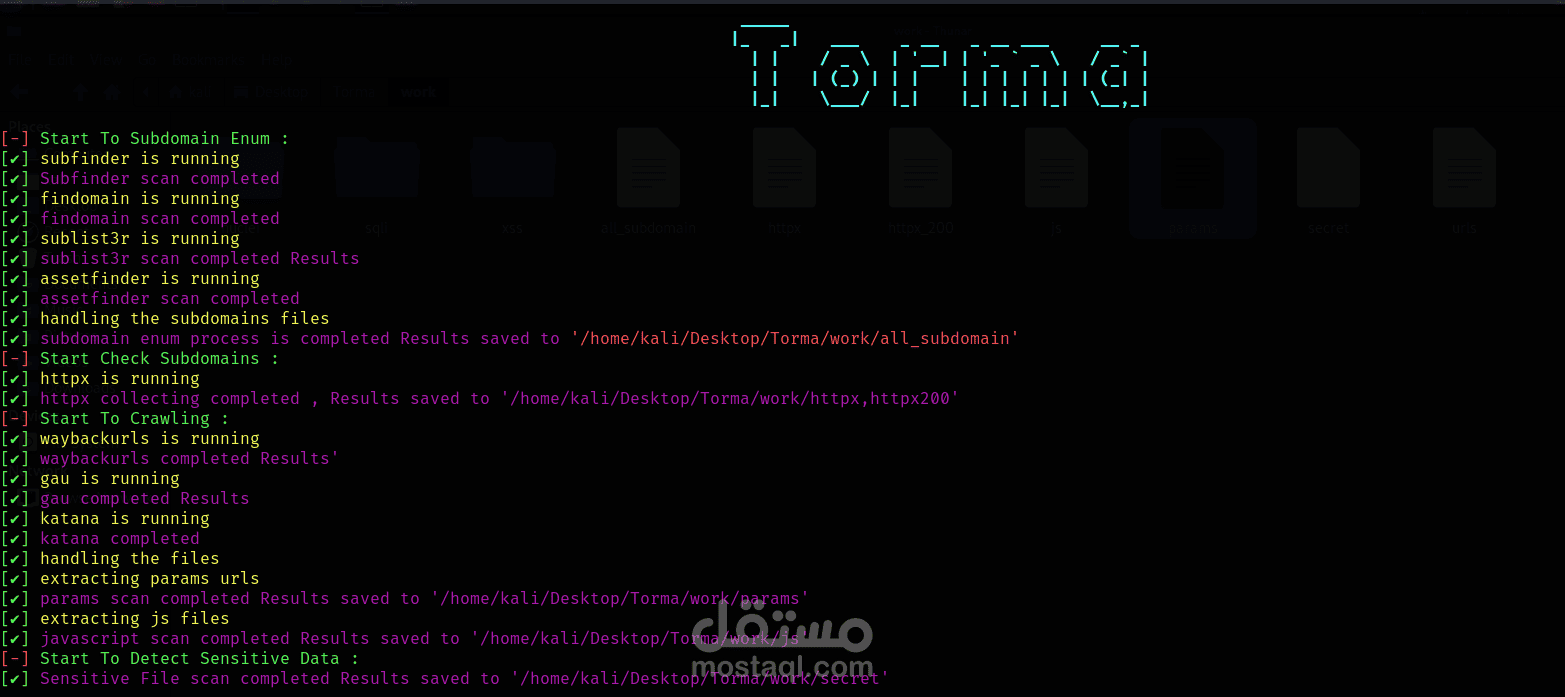
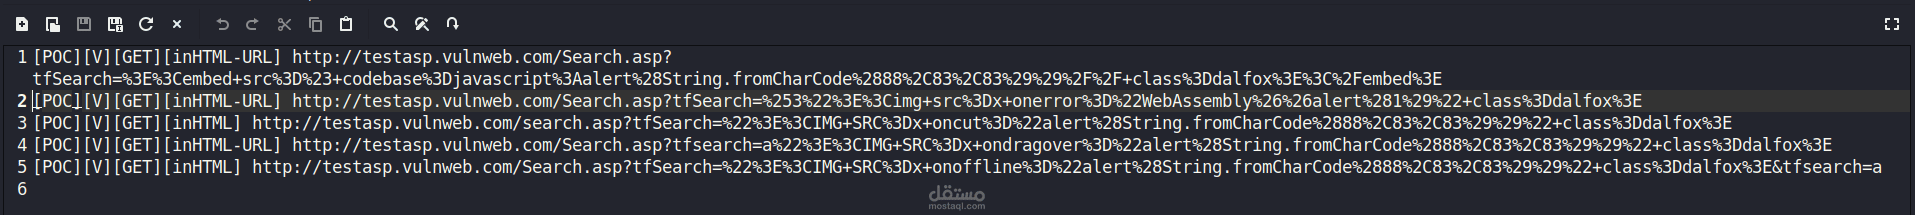
Built a modular Python security tool that automates the end-to-end bug bounty workflow — from subdomain enumeration through vulnerability scanning — reducing what's typically a manual, multi-tool process into a single-command pipeline.
Key features:
Integrated 12+ industry-standard open-source tools (Subfinder, Httpx, Katana, Dalfox, Sqlmap, Nuclei, and more) into a unified recon-to-scan pipeline
Designed and built an AI agent (powered by LLaMA 3.3 70B via Groq API) that autonomously browses target websites using Playwright, discovers hidden endpoints, fills forms with security test payloads, and performs real-time vulnerability detection (SQLi, XSS, IDOR, login bypass)
Implemented automatic tool installation/version verification, live scan progress reporting, and AI-generated HTML vulnerability reports
Validated against legally sanctioned vulnerable test applications, successfully identifying real injection points and IDOR vulnerabilities
Tech stack: Python 3, Playwright, Groq API (LLaMA 3.3 70B), Nuclei, Sqlmap, Dalfox, Kali Linux