Cybersecurity Attack Simulation & SIEM Log Analysis | Hands-on SOC Project
تفاصيل العمل
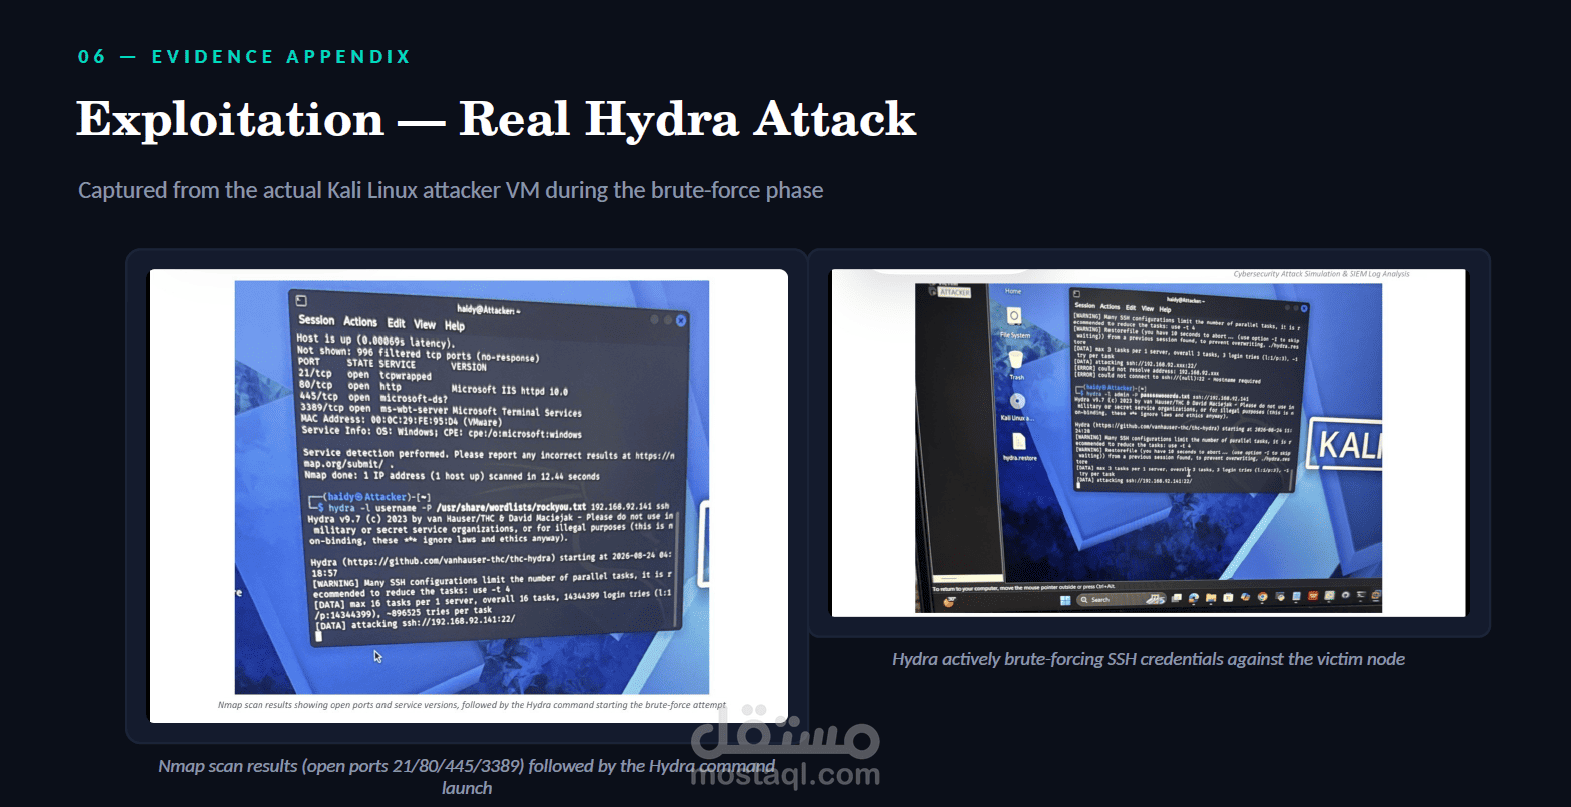
Simulated a complete cyber attack lifecycle inside an isolated lab environment using Kali Linux and Windows 10 VMs. I performed reconnaissance with Nmap, launched an SSH brute-force attack via Hydra, then shifted to the defensive side using Splunk SIEM to collect, correlate, and analyze security logs in real time — successfully identifying the exact attack window through IoC tracing and log spike analysis.