soc tier 1
تفاصيل العمل
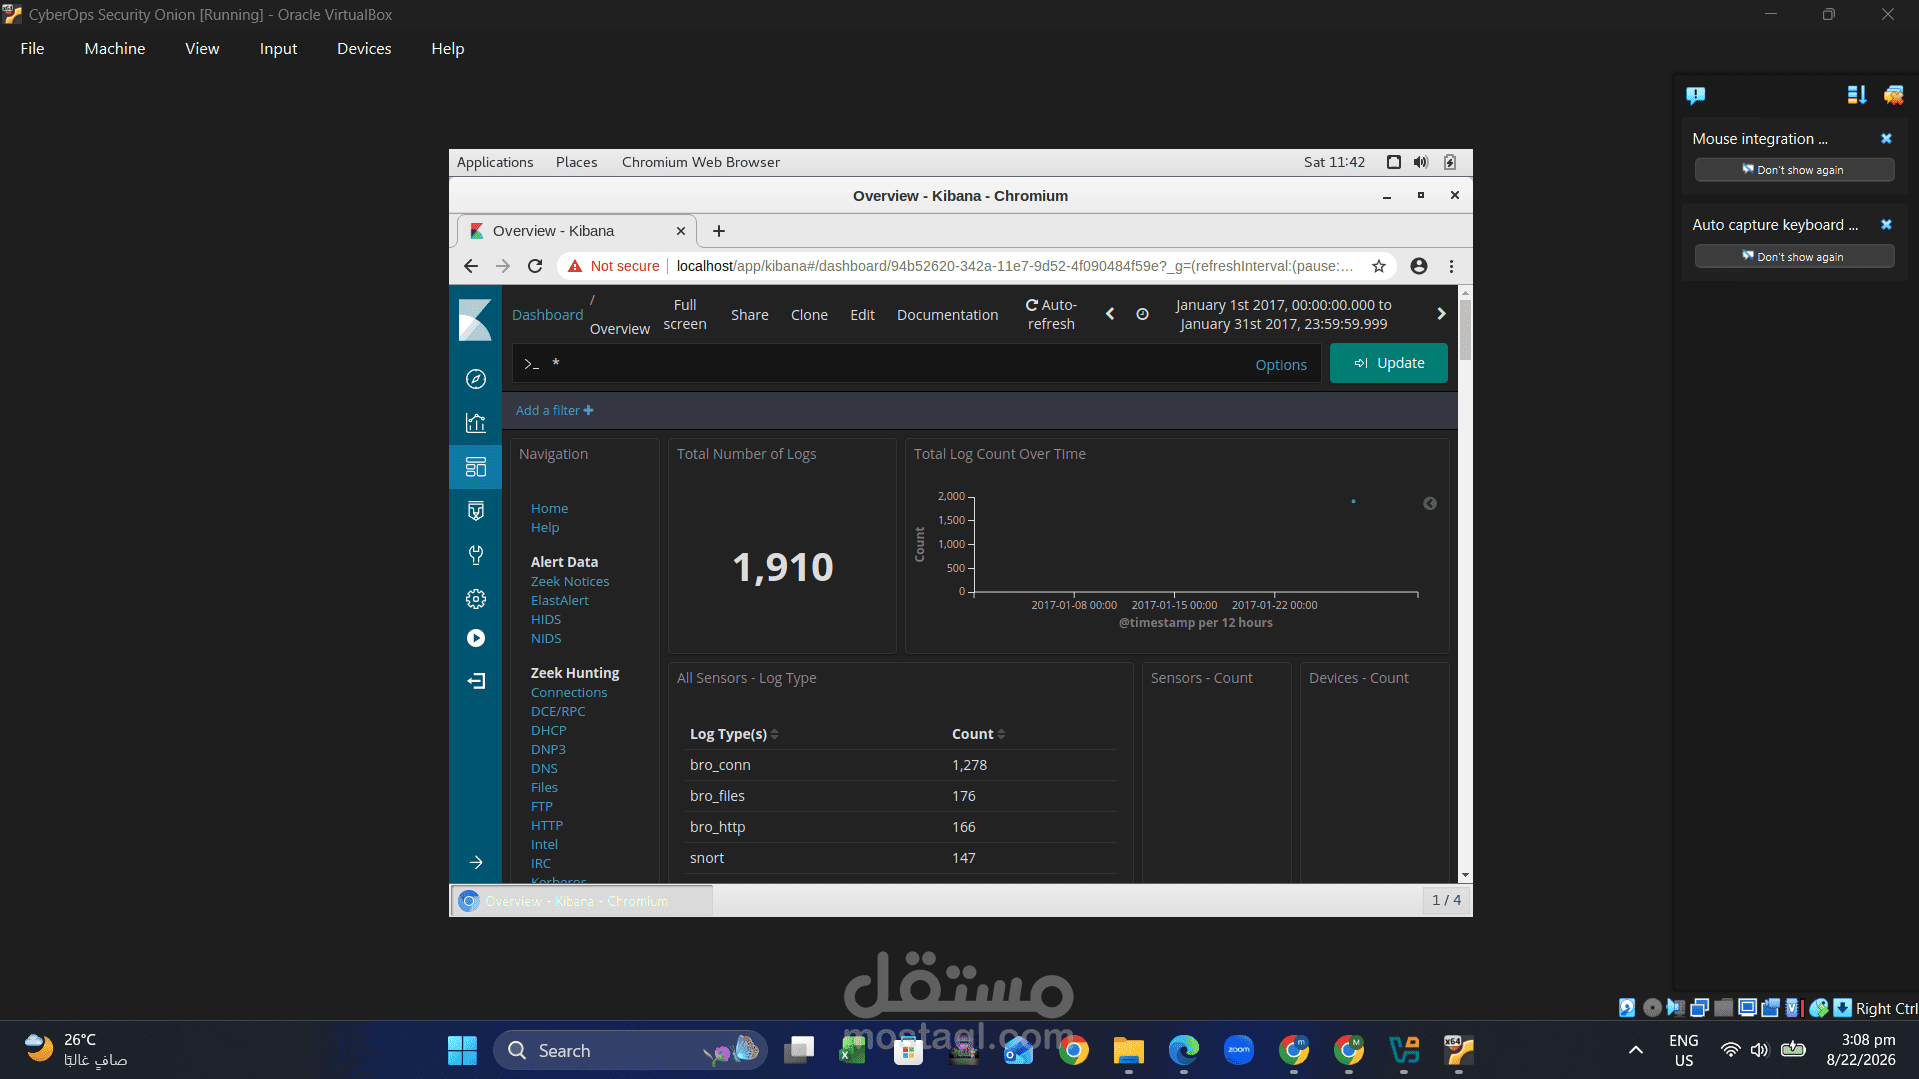
The attack started when the victim searched for “kitchen remodeling” on Bing and visited a legitimate but compromised website, homeimprovement.com. The website silently loaded a hidden script from retrotip.visionurbana.com.ve, which created a hidden iframe that redirected the victim to tyu.benme.com hosting the RIG Exploit Kit. The exploit kit then delivered a malicious Flash file called exploit.swf, which exploited CVE-2015-3105 in Adobe Flash Player on the victim’s Internet Explorer 11 and Windows 7 system. The exploit required no user interaction and resulted in the silent installation and execution of Cerber Ransomware. After execution, the ransomware attempted to communicate with its C2 server at 90.2.1.0 and also tried to resolve a backup .onion domain through internal DNS.