Security Investigation: SQL Injection & DNS Data Exfiltration
تفاصيل العمل
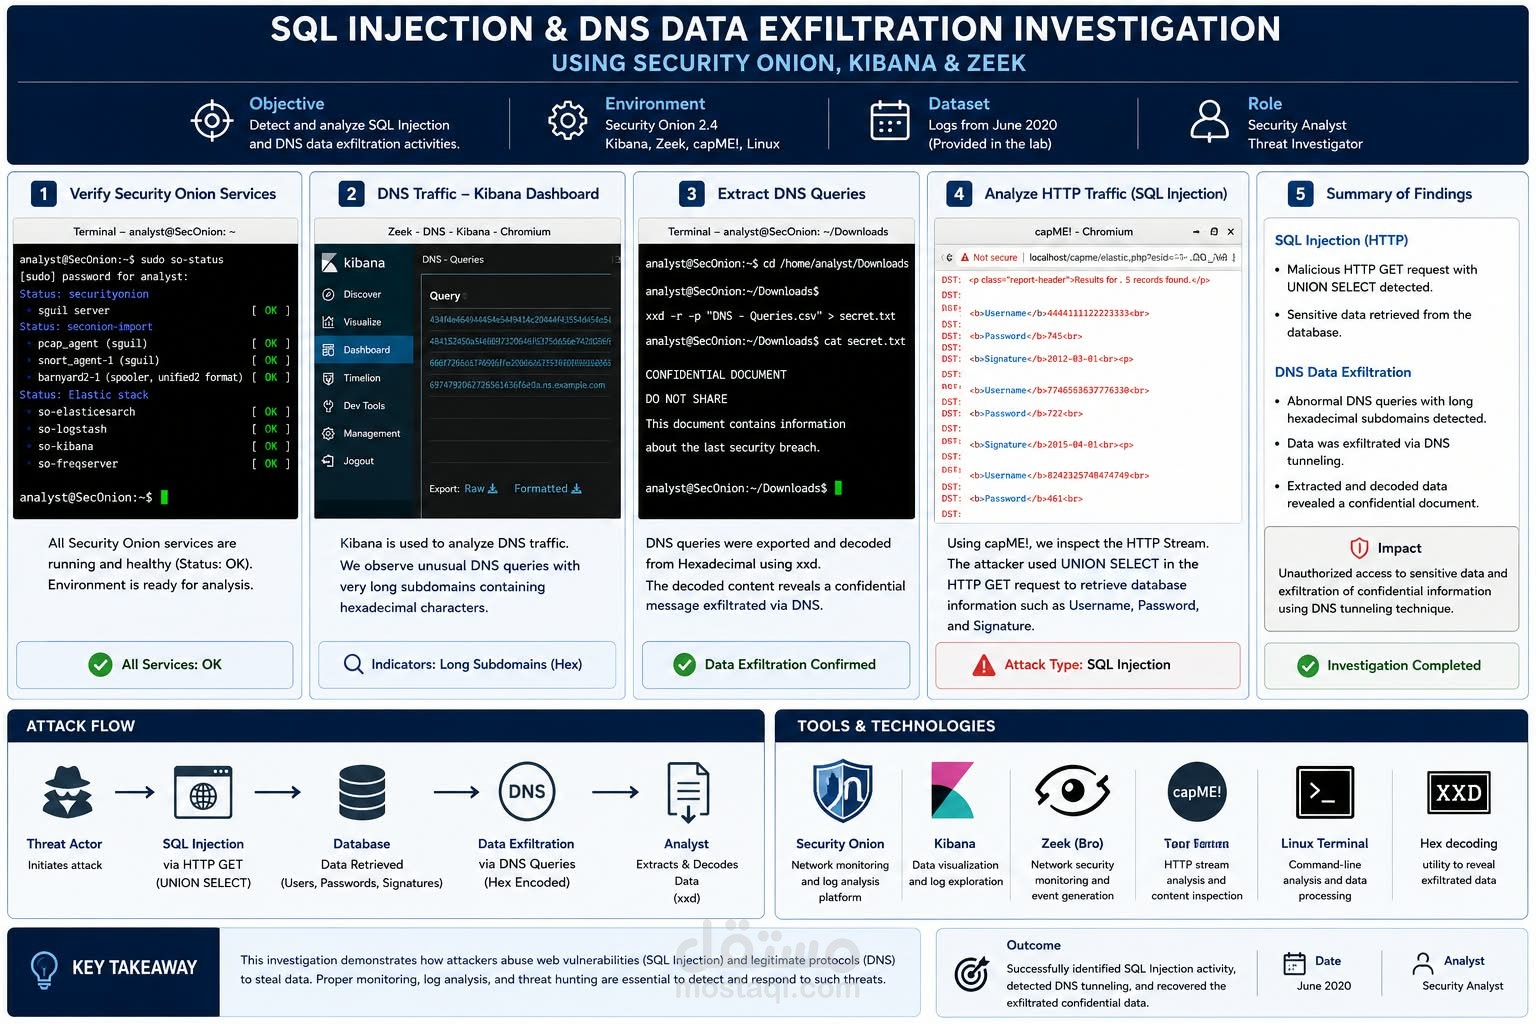
* Detection and analysis of *SQL Injection* through HTTP traffic.
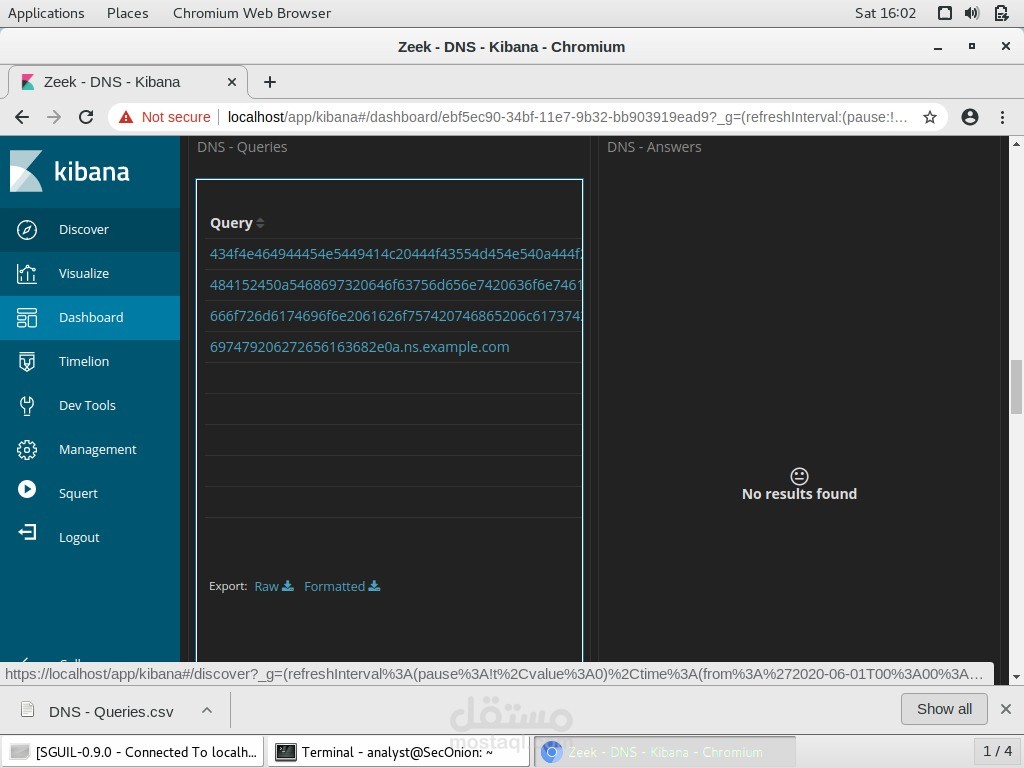
* Analysis of *DNS traffic* to identify abnormal queries.
* Detection of *DNS Data Exfiltration* through long subdomains containing hexadecimal data.
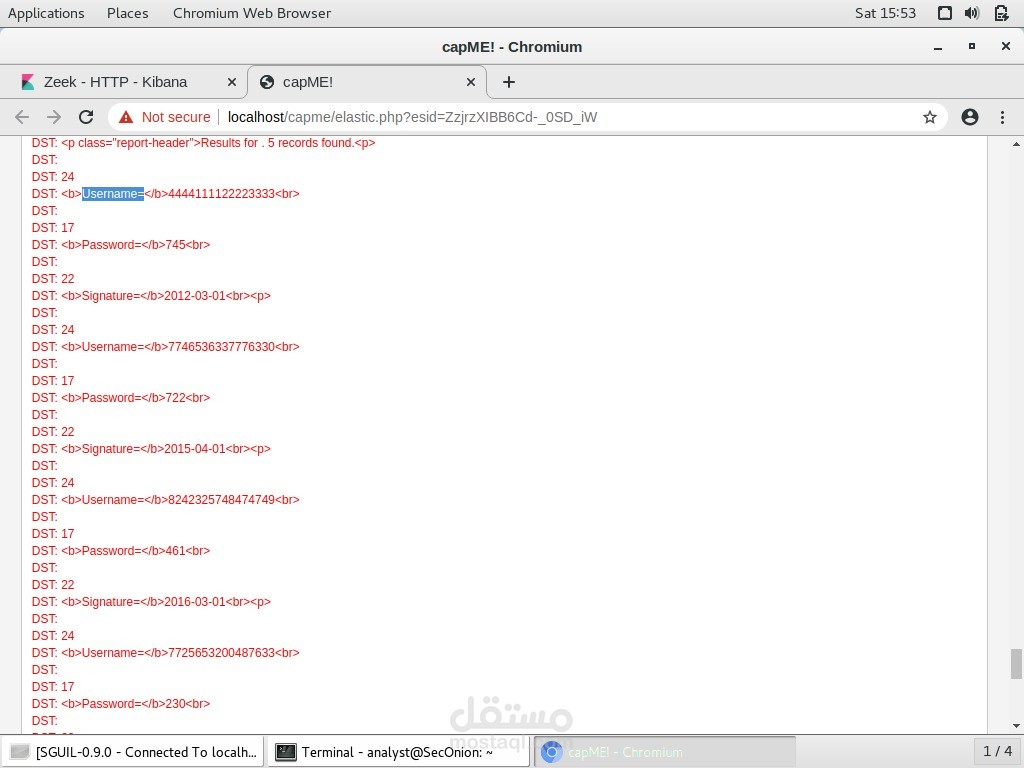
* Analysis of HTTP transcripts to determine the data accessed during the attack.
* Identification of sensitive information such as *usernames, passwords, and signatures*.
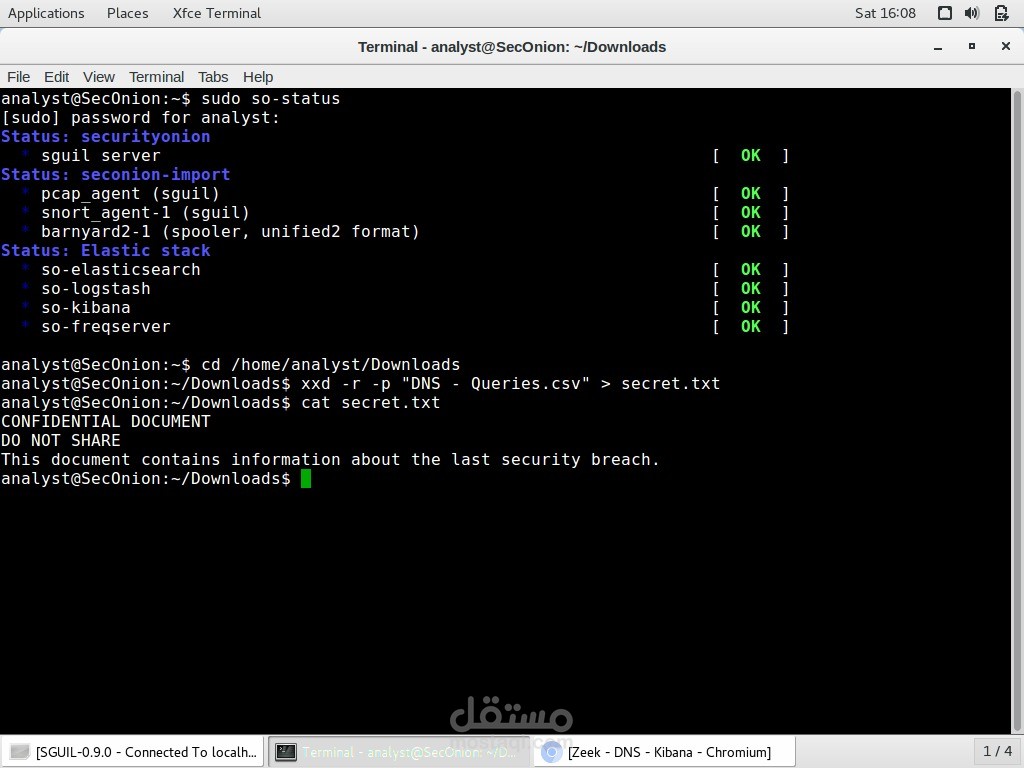
* Decoding extracted data using Linux .
* Visualization and analysis of security logs using Kibana.
* Practical application of a security investigation methodology.
### Implementation Process
1. Start *Security Onion* and verify that all services are running correctly.
2. Open *Kibana* and select the required time range.
3. Analyze *HTTP Logs* and identify activity related to SQL Injection.
4. Use *capME!* to inspect the HTTP stream and analyze requests and responses.
5. Analyze *DNS Logs* and search for abnormal DNS queries.
6. Identify long hexadecimal subdomains indicating possible data exfiltration.
7. Export and analyze the DNS queries.
8. Use to decode the hexadecimal data and recover the original content.
9. Document the findings, including the *attack type, affected data, and exfiltration method*.