Security Onion Threat Hunter
تفاصيل العمل
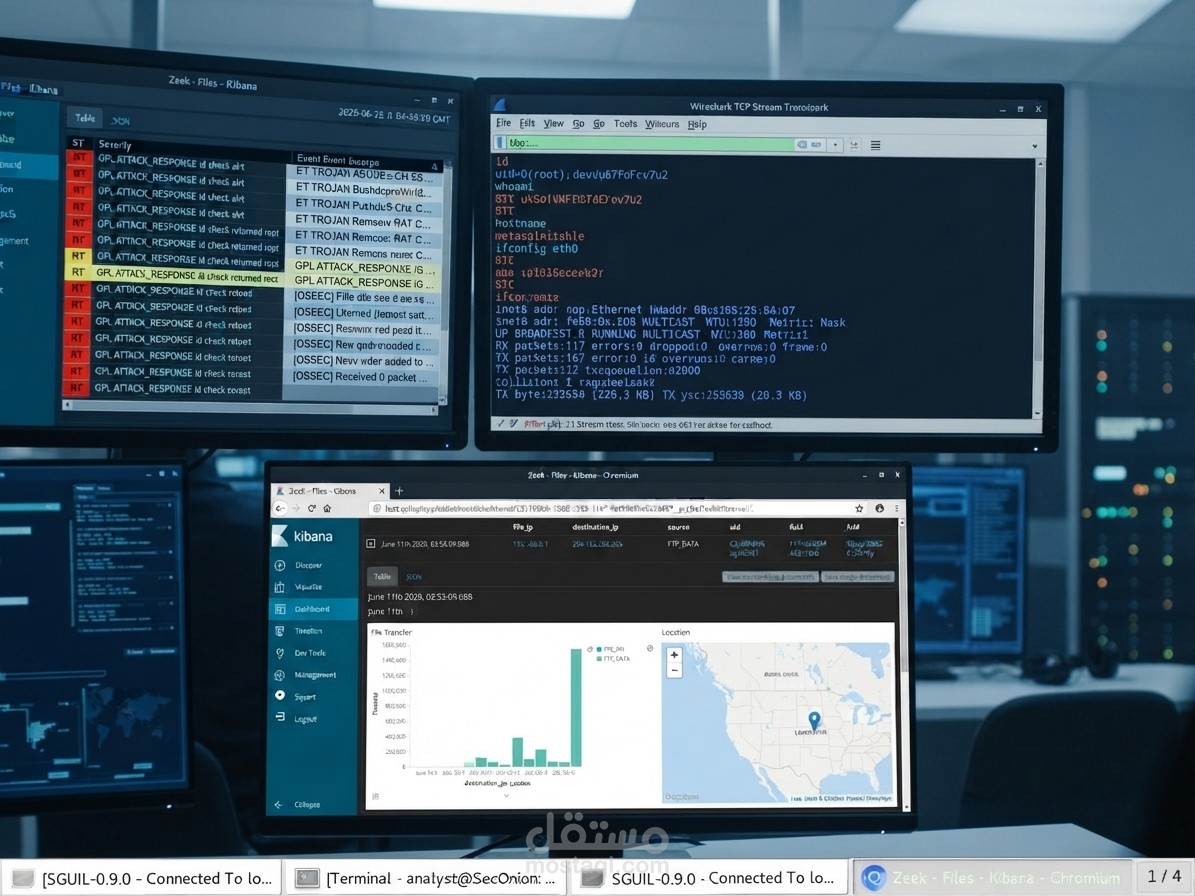
Type of Work: An applied security project in Cybersecurity Incident Response & Network Forensics, focused on detecting and investigating a network breach where a vulnerability was exploited, resulting in the exfiltration and theft of a sensitive file (confidential.txt).
Project Features:
Combines the use of leading Security Operations Center (SOC) monitoring platforms and tools, including Security Onion, Sguil, Wireshark, and Kibana.
Applies network traffic analysis standards using the 5-Tuple concept (source/destination IP addresses, port numbers, and transport protocol).
Enables the documentation of digital evidence and the writing of professional incident response reports with high accuracy.
Implementation Method:
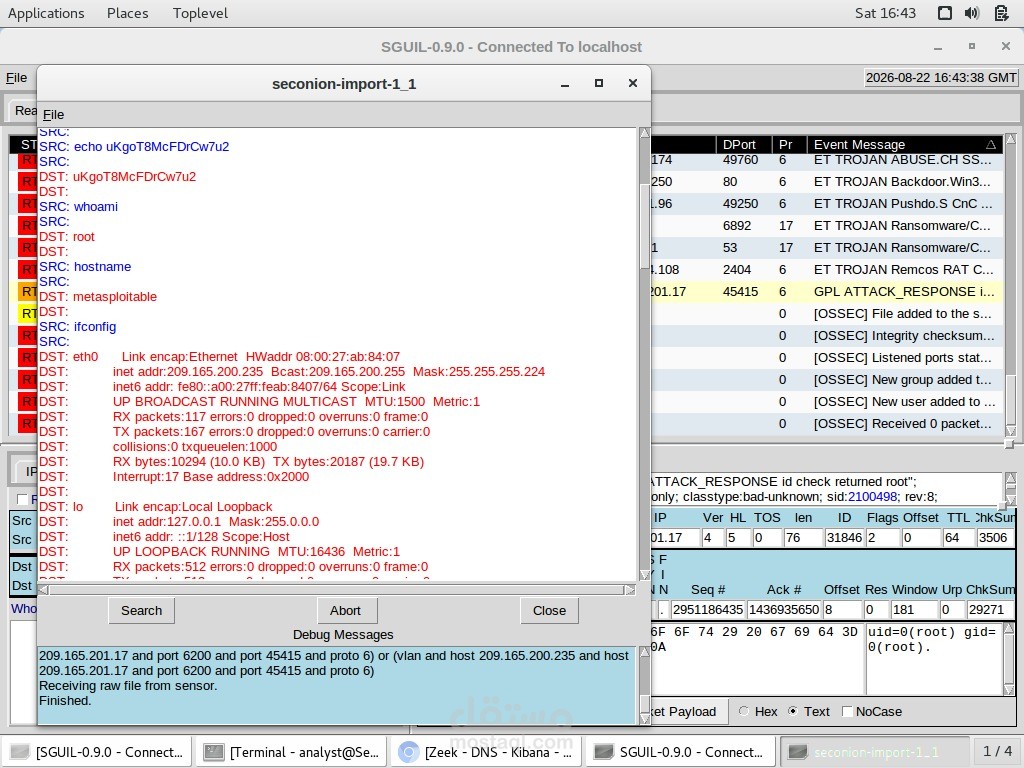
Step 1 (Sguil): Launching the Security Onion environment and monitoring critical security alerts to identify that the attacker gained root access, while tracking executed text commands.
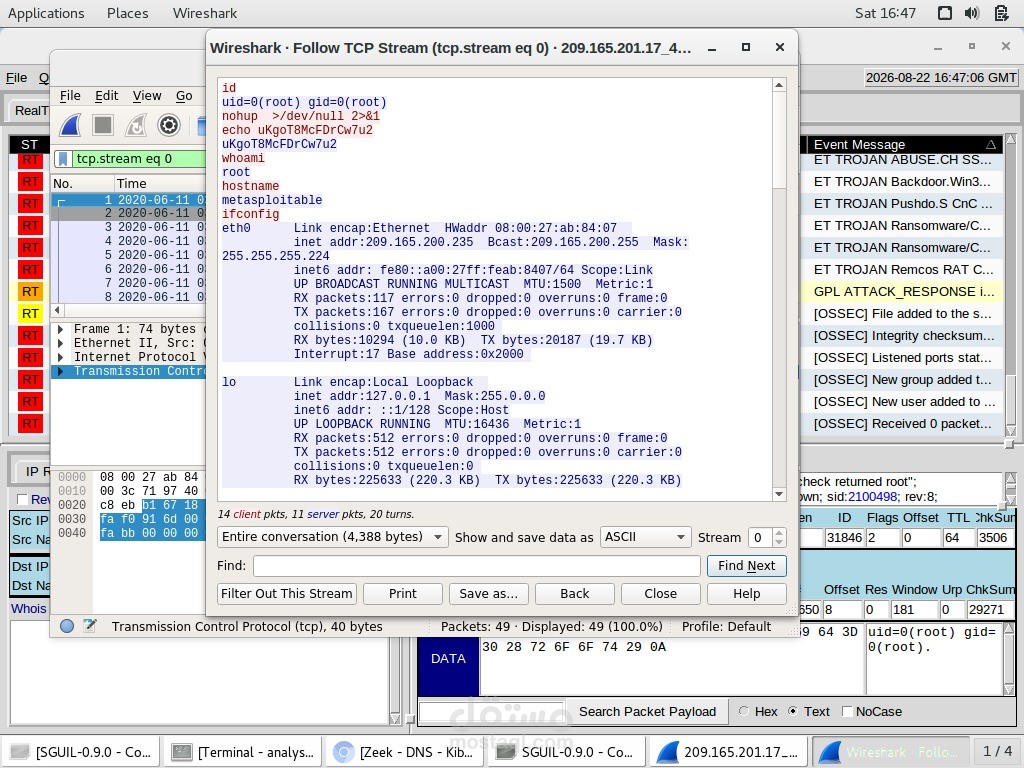
Step 2 (Wireshark): Pivoting to analyze network packet data and tracing TCP stream sessions to understand the transactions exchanged between the client and server.
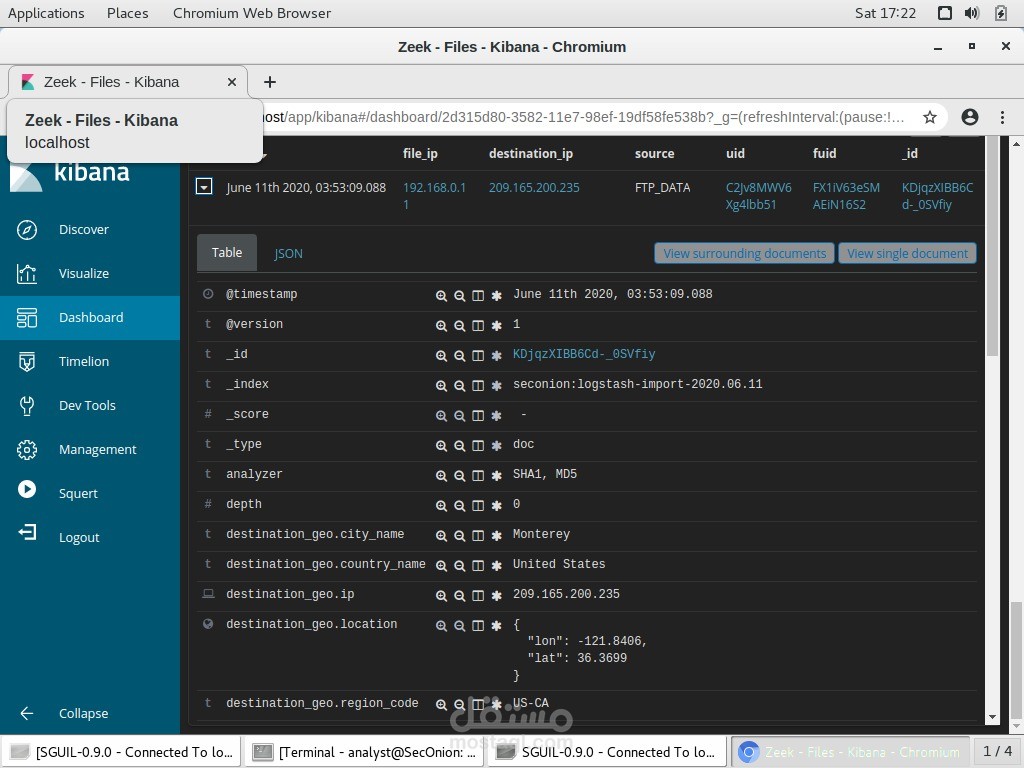
Step 3 (Kibana): Querying dashboards and inspecting file transfer protocol logs (FTP and FTP_DATA) to uncover how the sensitive file was copied, exfiltrated, and deleted from the compromised host.