SIEM Use Case Documentation
تفاصيل العمل
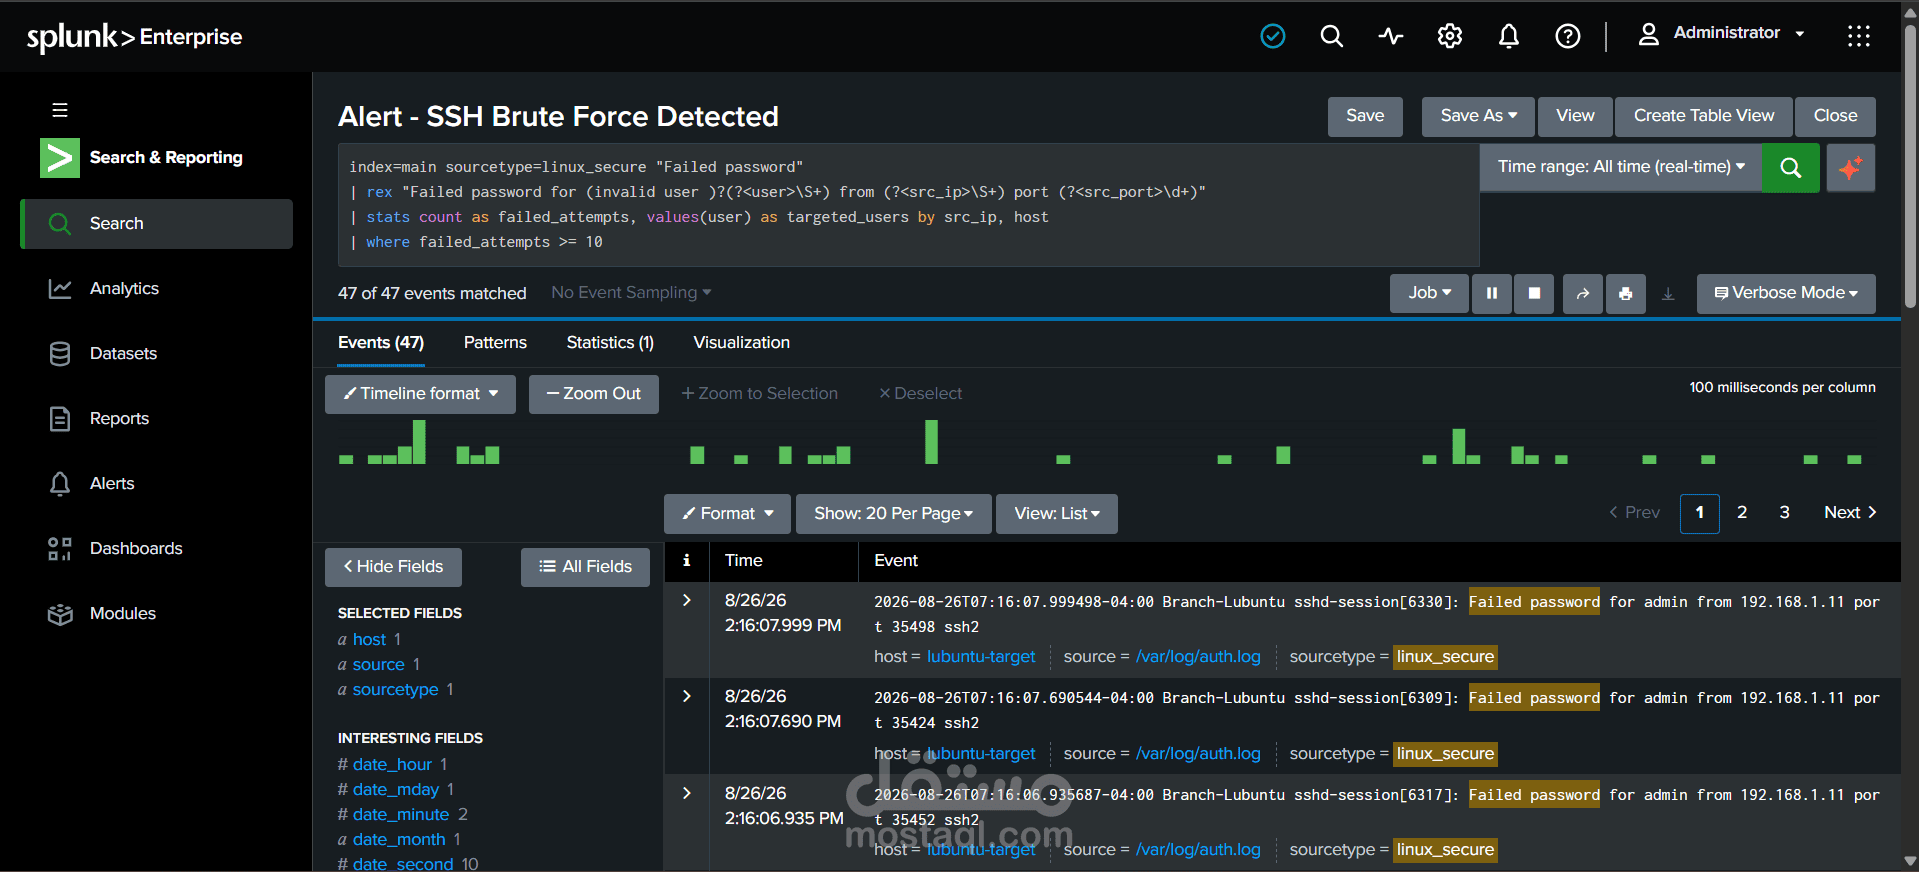
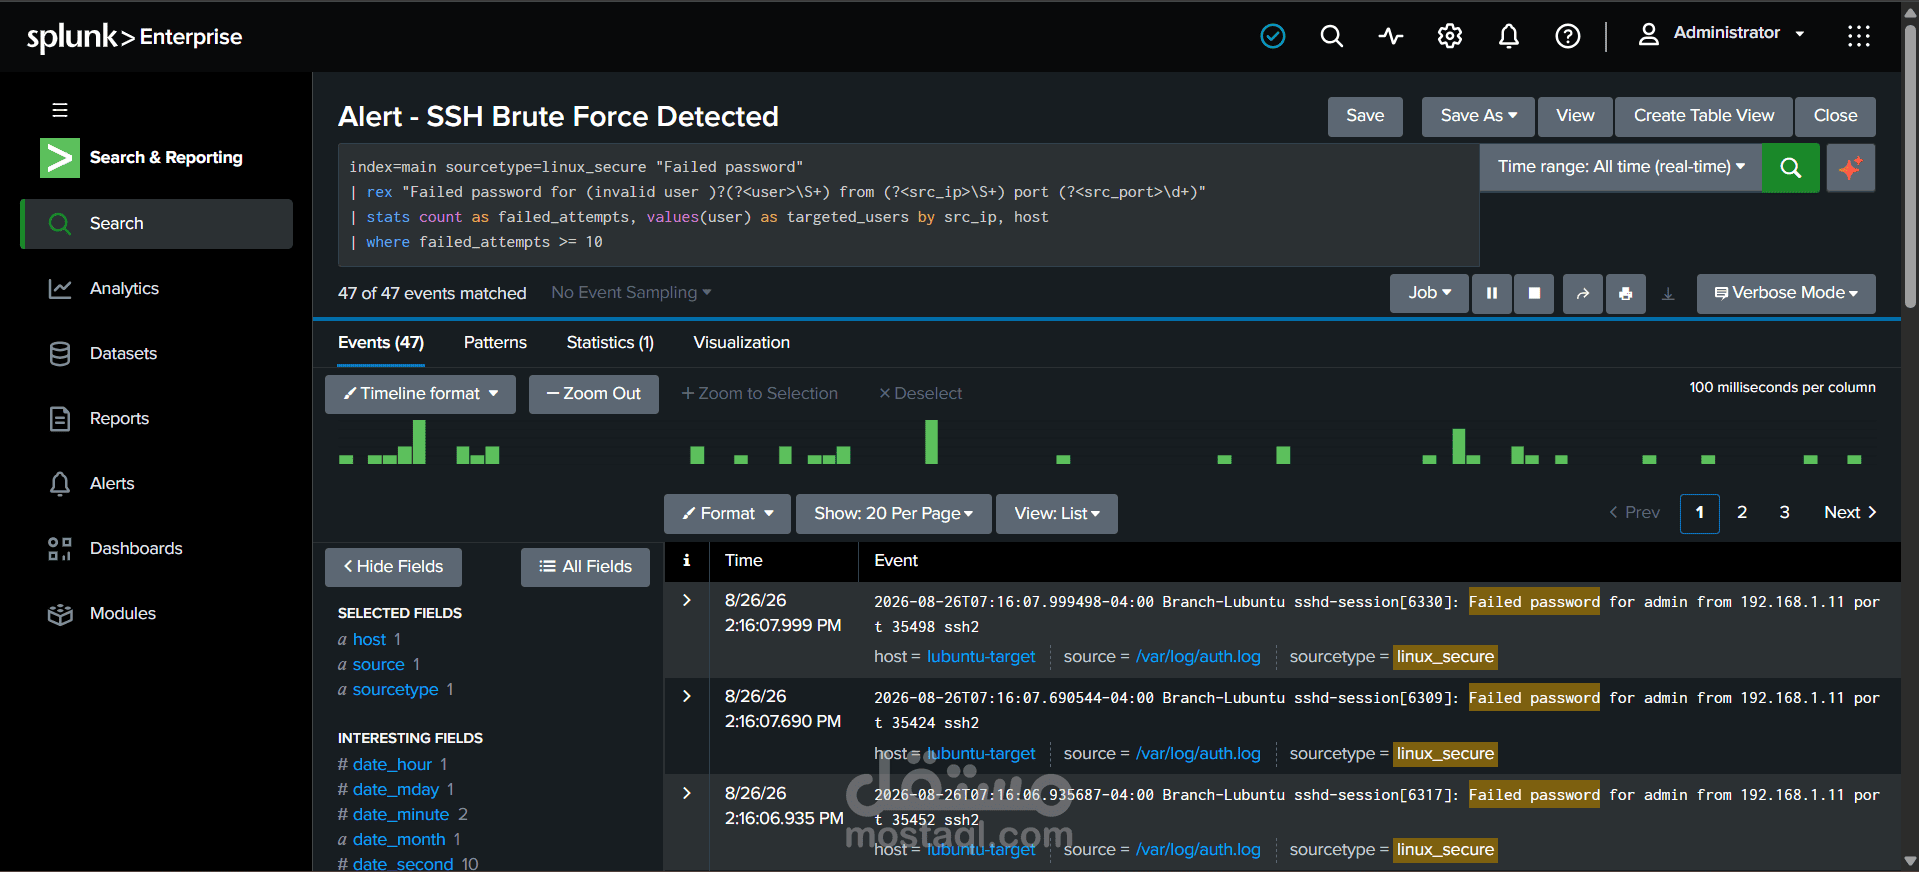
Developed SIEM use case documentation for detecting suspicious SSH brute-force activity using Splunk. The work included defining the detection logic, analyzing relevant security events and logs, identifying indicators of suspicious activity, and documenting the alert findings and investigation process in a structured format.