File Path Traversal – Non-Recursive Traversal Filtering
تفاصيل العمل
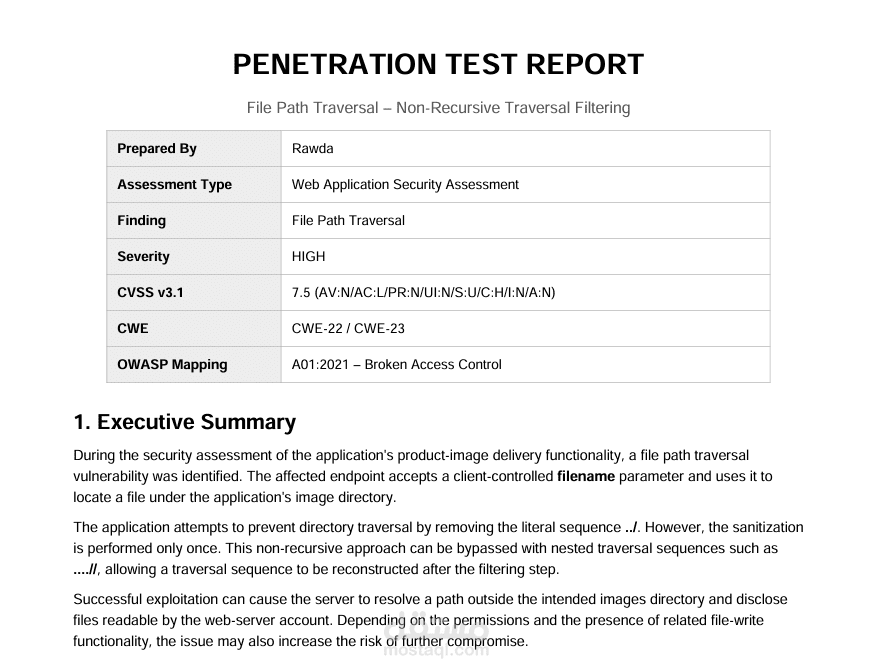
During the security assessment of the application's product-image delivery functionality, a file path traversal
vulnerability was identified. The affected endpoint accepts a client-controlled filename parameter and uses it to
locate a file under the application's image directory.
The application attempts to prevent directory traversal by removing the literal sequence ../. However, the sanitization
is performed only once. This non-recursive approach can be bypassed with nested traversal sequences such as
....//, allowing a traversal sequence to be reconstructed after the filtering step.
Successful exploitation can cause the server to resolve a path outside the intended images directory and disclose
files readable by the web-server account. Depending on the permissions and the presence of related file-write
functionality, the issue may also increase the risk of further compromise