الجيزه مصر
تفاصيل العمل
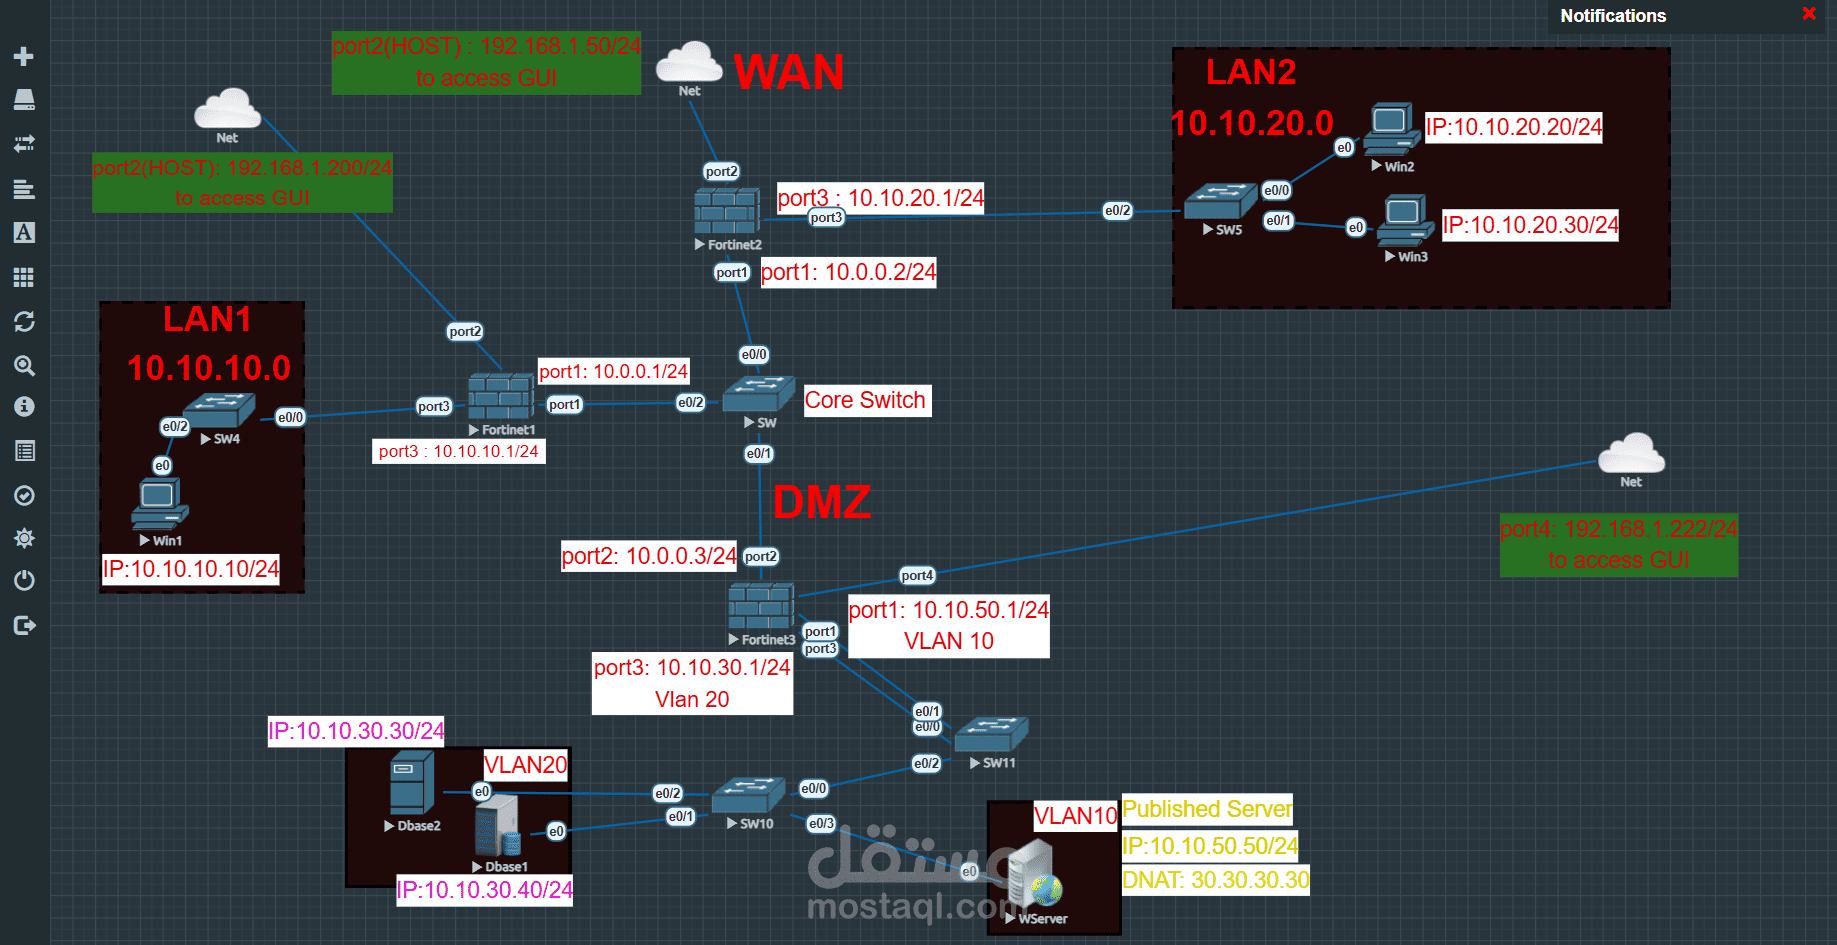
1. Network Security Project
This project represents a network infrastructure designed to provide secure communication between different network segments. The topology contains two internal LANs, LAN1 (10.10.10.0/24) and LAN2 (10.10.20.0/24), which are connected through firewalls and a core switch. The DMZ is used to host servers and is divided into VLAN 10 and VLAN 20 to separate and organize network traffic. The firewalls control traffic between the internal networks, the DMZ, and the WAN, providing security and controlled access. A published web server is located in the DMZ with the private IP 10.10.50.50/24, and DNAT is configured to allow external users to access the server securely.