Security misconfiguration vulnerability finding
تفاصيل العمل
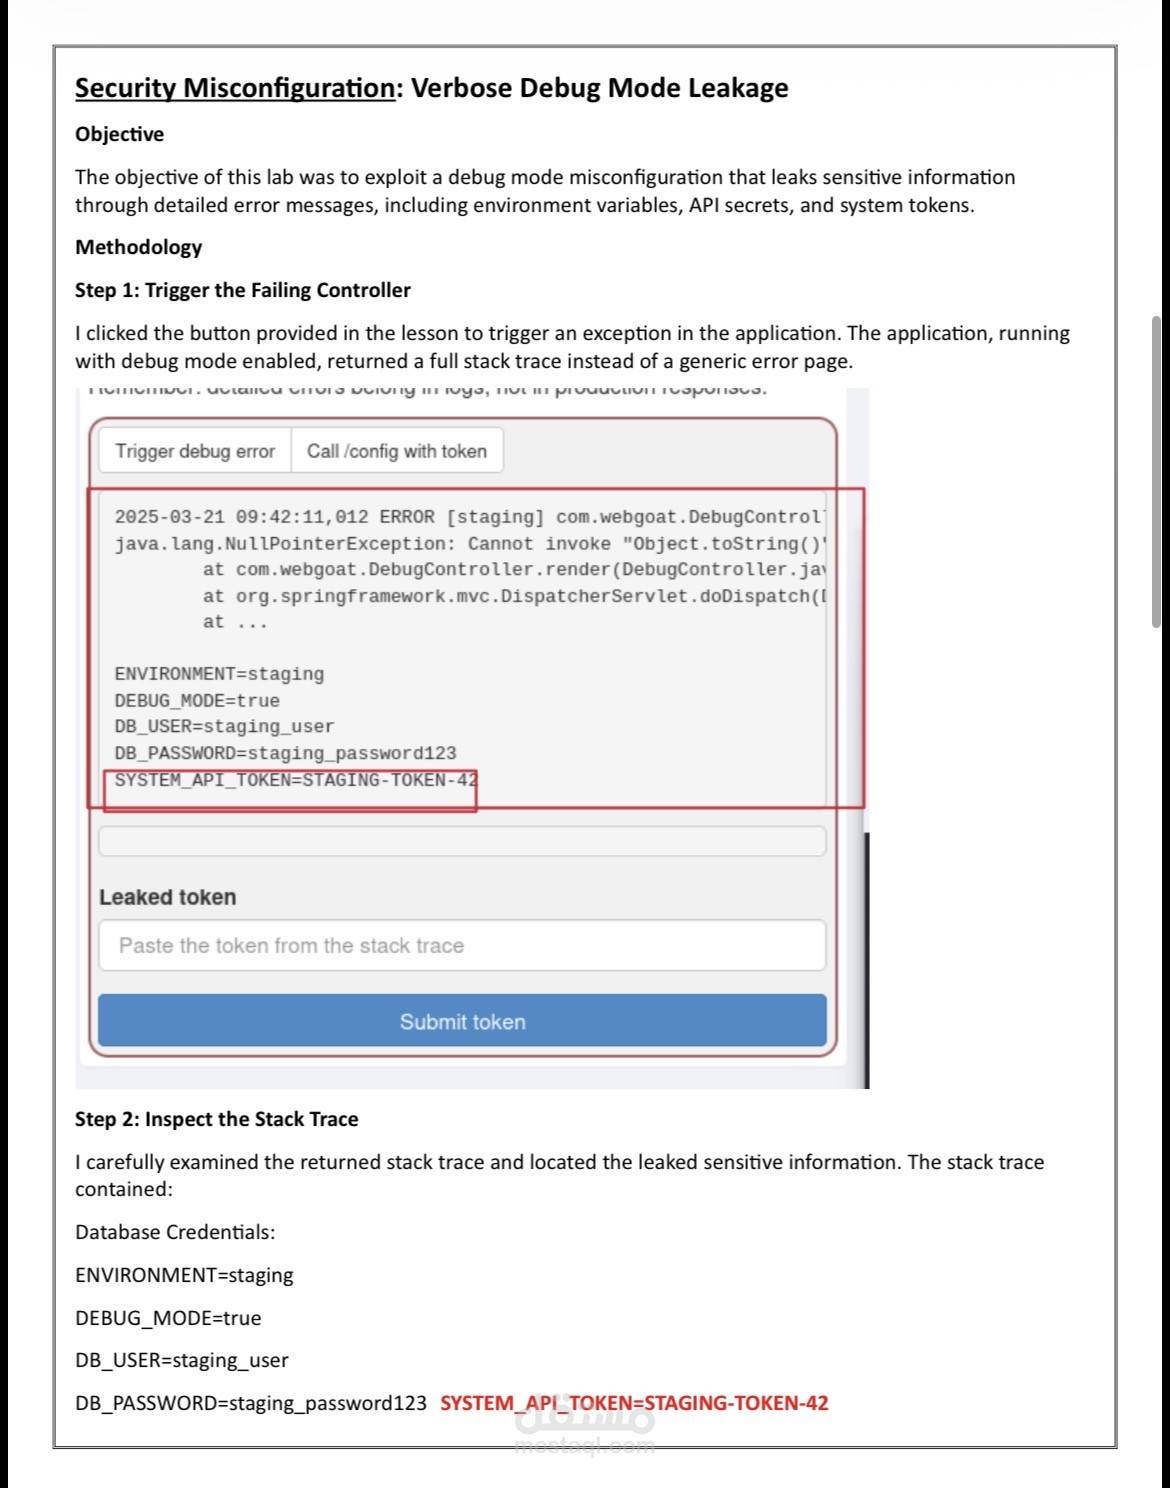
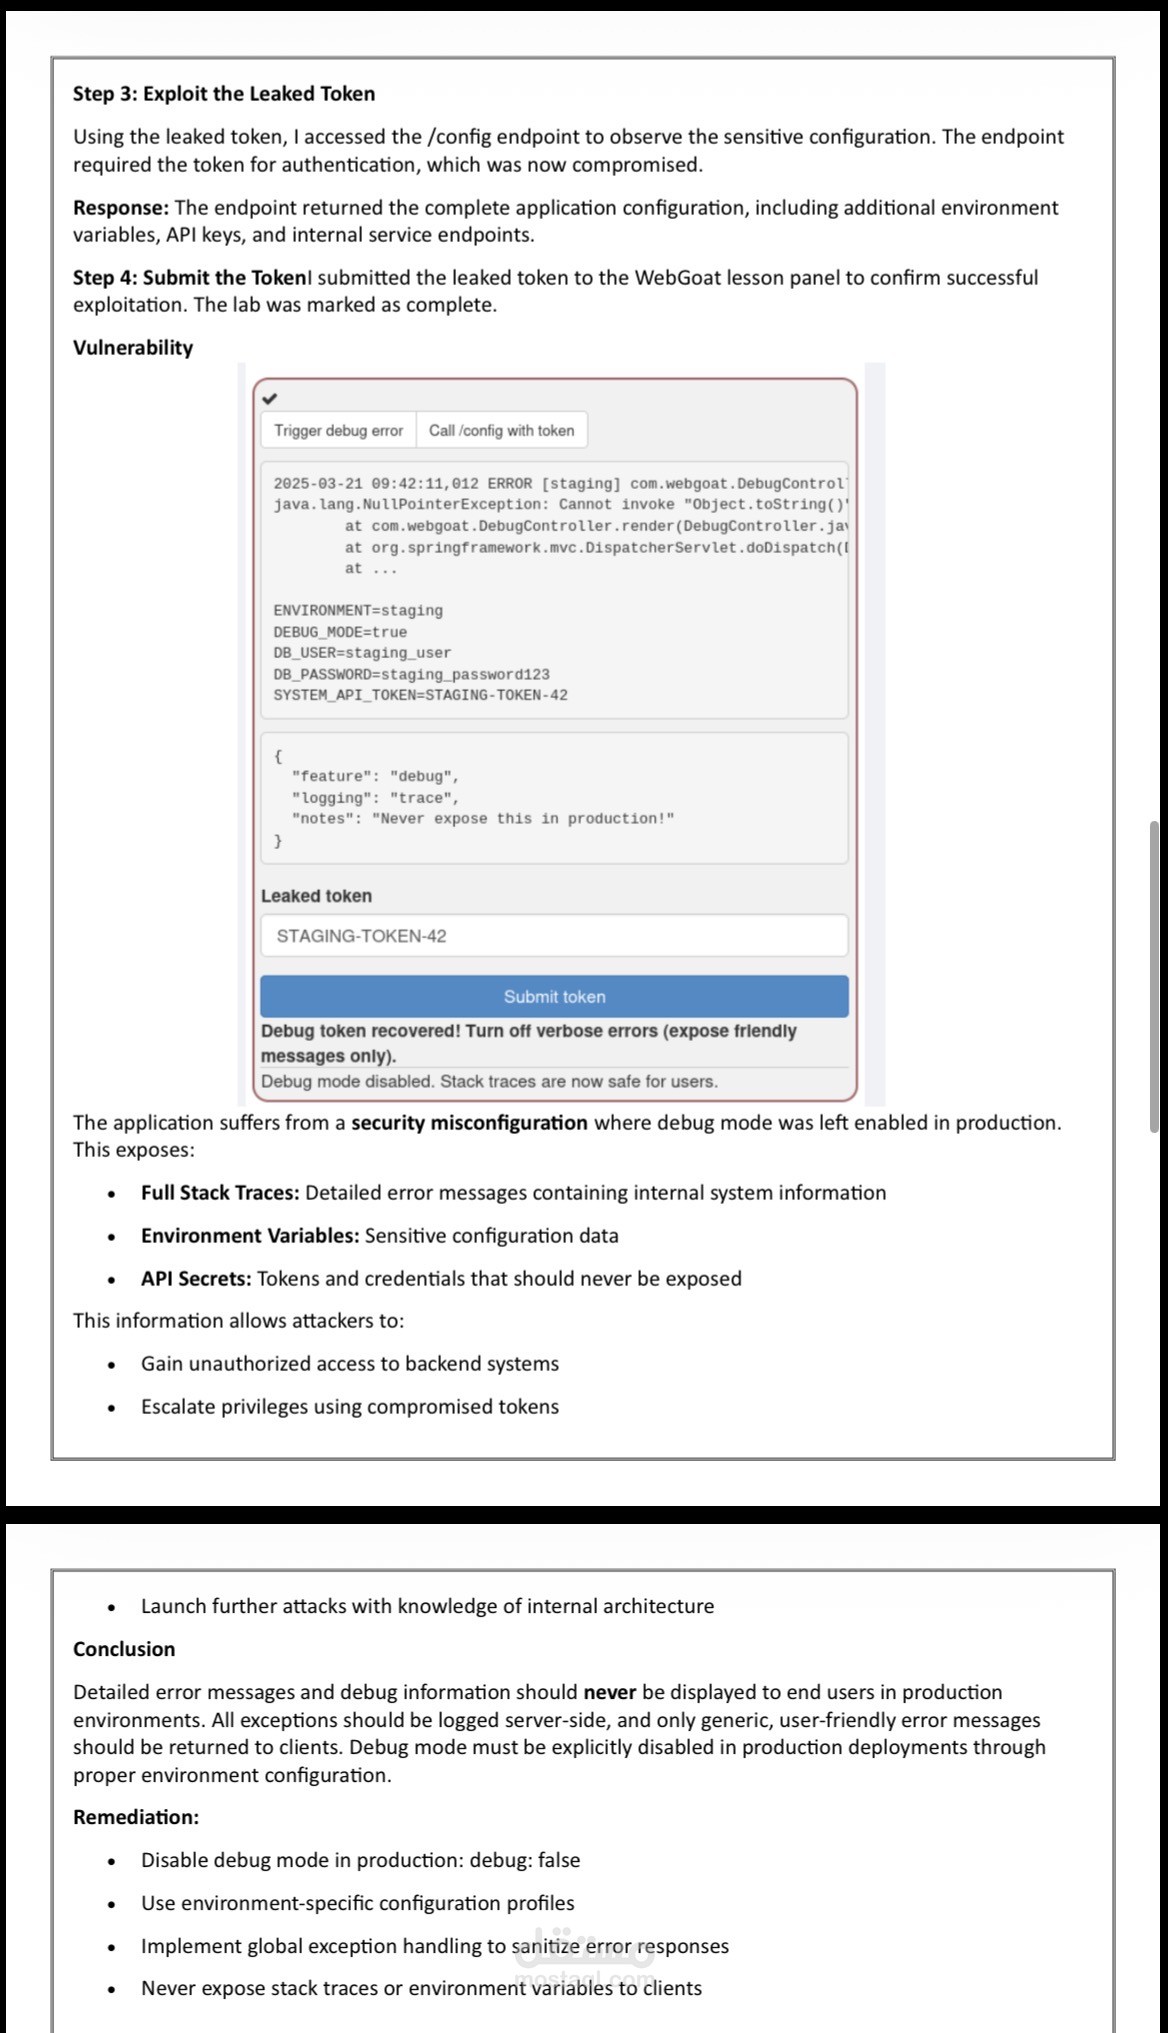
Security Misconfiguration – Lab 1
Objective
The objective of this lab was to identify and exploit a security misconfiguration in the web application.
Steps Performed
1. Opened the Security Misconfiguration lab in WebGoat.
2. Inspected the application and its available functionality.
3. Identified a misconfigured security setting that exposed functionality that should not be accessible to normal users.
4. Accessed the exposed functionality.
5. The application revealed the expected information and the lab was successfully completed.
Vulnerability
The application contained an insecure configuration that exposed sensitive functionality or information to users who should not have access to it.
Impact
Security misconfigurations can allow attackers to access sensitive information, administrative functionality, or other resources that should be restricted.
Remediation
* Disable unnecessary features and services.
* Restrict access to administrative functionality.
* Use secure default configurations.
* Remove debugging and unnecessary information disclosure from production environments.
* Regularly review and update security configurations.
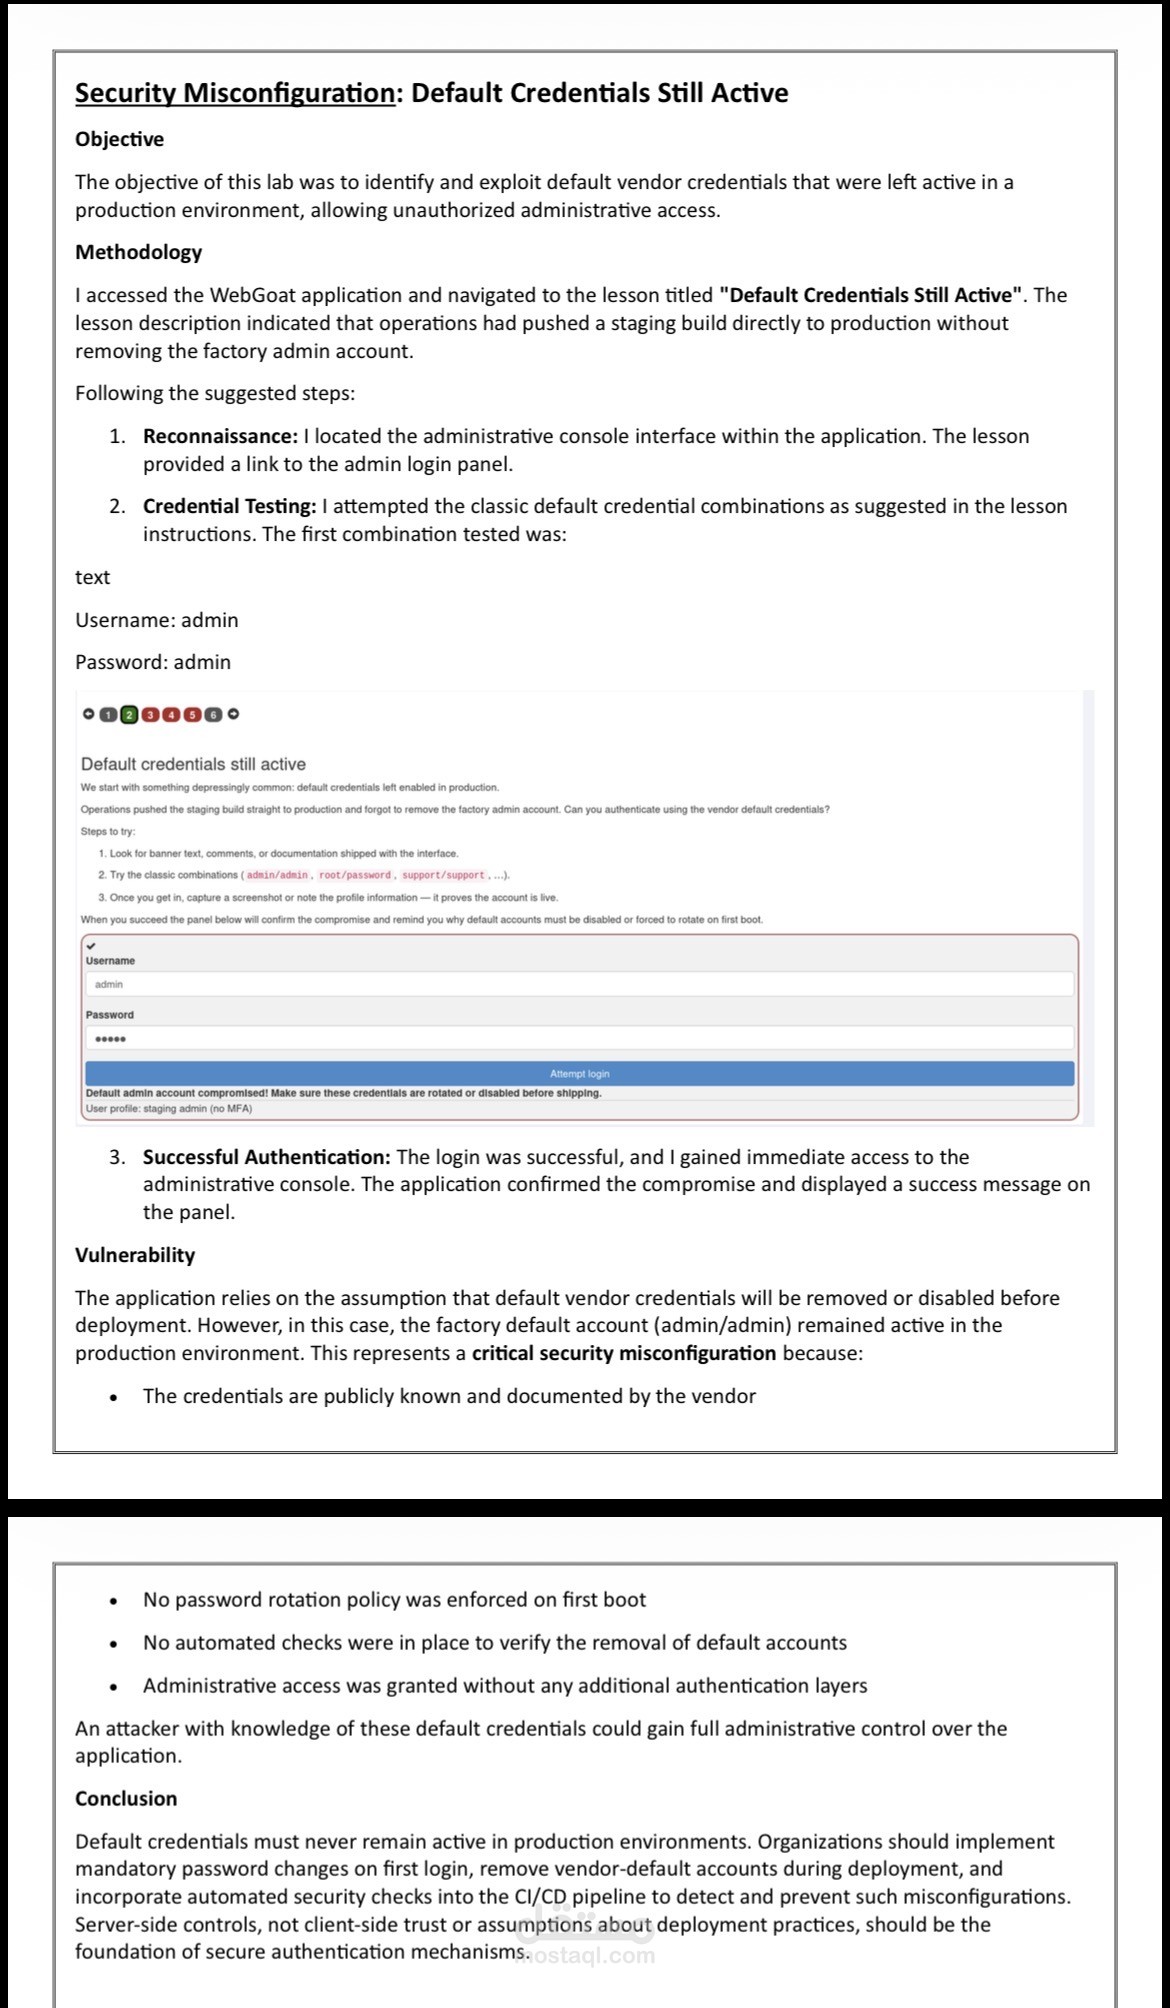
Security Misconfiguration – Lab 2
Objective
The objective of this lab was to identify a misconfiguration in the application’s security settings and demonstrate its impact.
Steps Performed
1. Opened the second Security Misconfiguration exercise.
2. Examined the application’s behavior and available resources.
3. Identified an improperly configured resource/functionality.
4. Accessed the resource by taking advantage of the insecure configuration.
5. The application provided the expected result and the lab was successfully completed.
Vulnerability
The application was improperly configured, allowing access to functionality or information that should have been restricted.
Impact
An attacker could take advantage of the misconfiguration to obtain information or access functionality that was not intended to be publicly available.
Remediation
* Follow secure configuration standards.
* Restrict sensitive resources using proper server-side access controls.
* Disable unnecessary endpoints and services.
* Avoid exposing sensitive information through error messages or configuration files.
* Perform regular security configuration reviews.