Client side vulnerability finding
تفاصيل العمل
WebGoat – Client-Side Validation / Field Restrictions
Objective
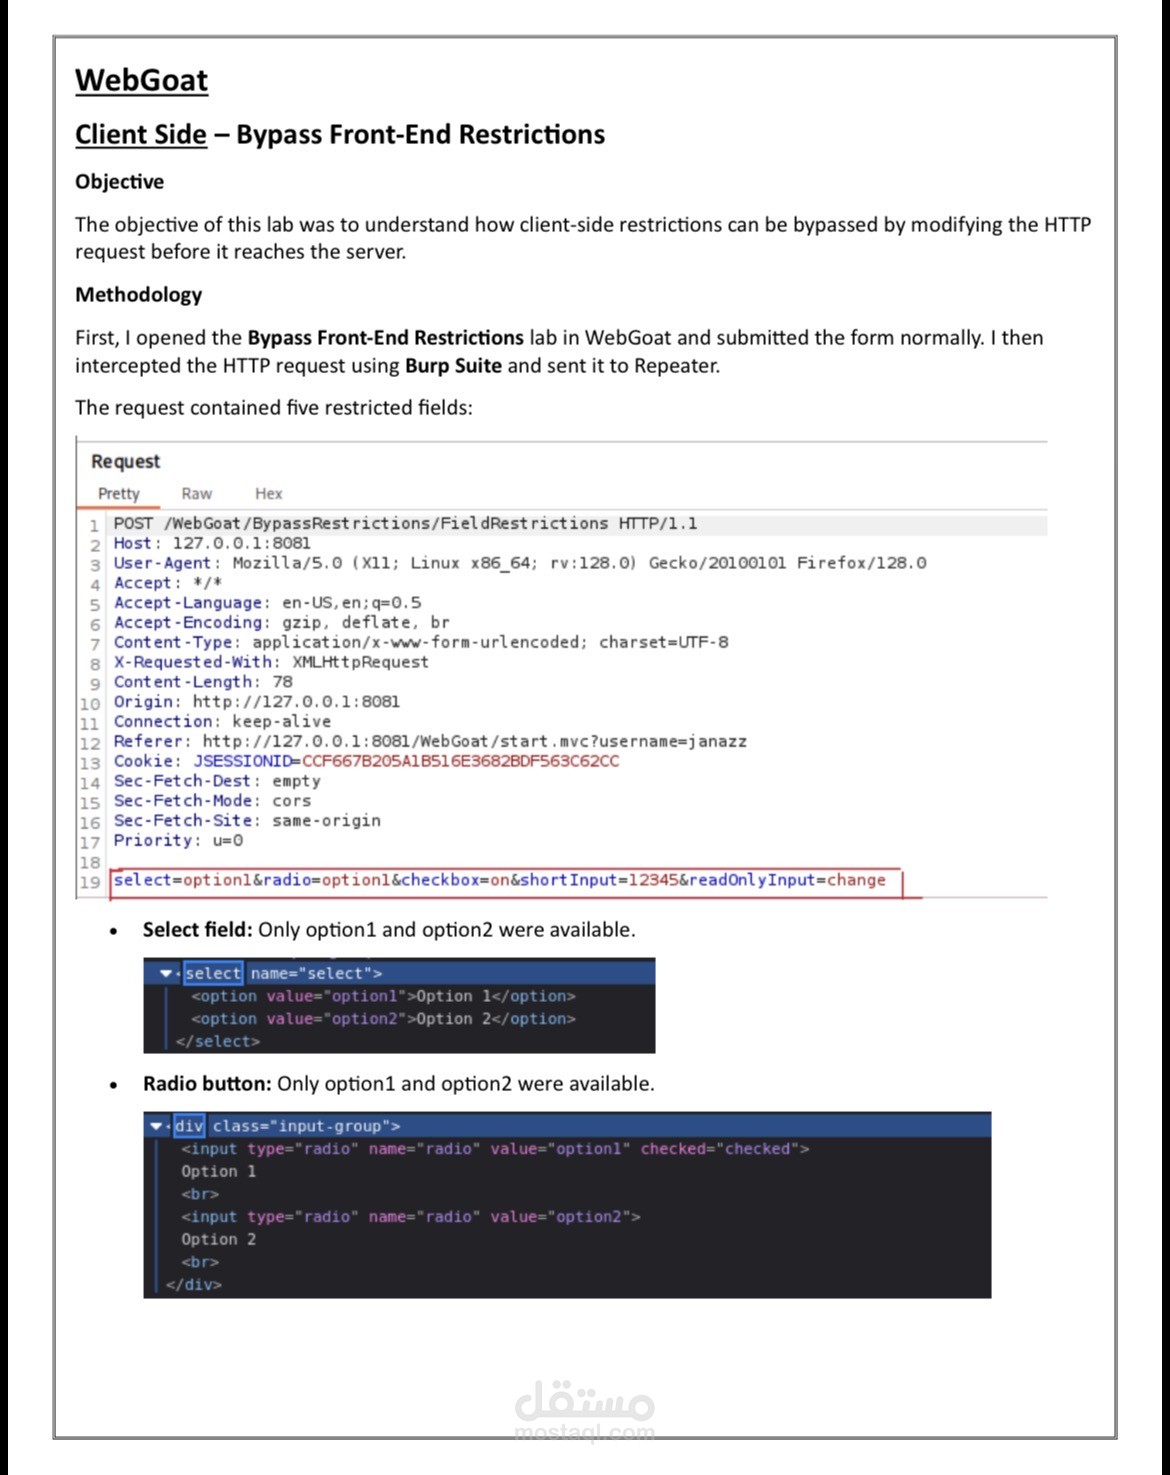
The objective of this lab was to understand how client-side restrictions can be bypassed because validation performed in the browser can be modified by the user.
Steps Performed
1. Opened the vulnerable WebGoat exercise.
2. Inspected the page and identified the restriction applied to the input field.
3. The restriction was implemented on the client side using HTML/JavaScript.
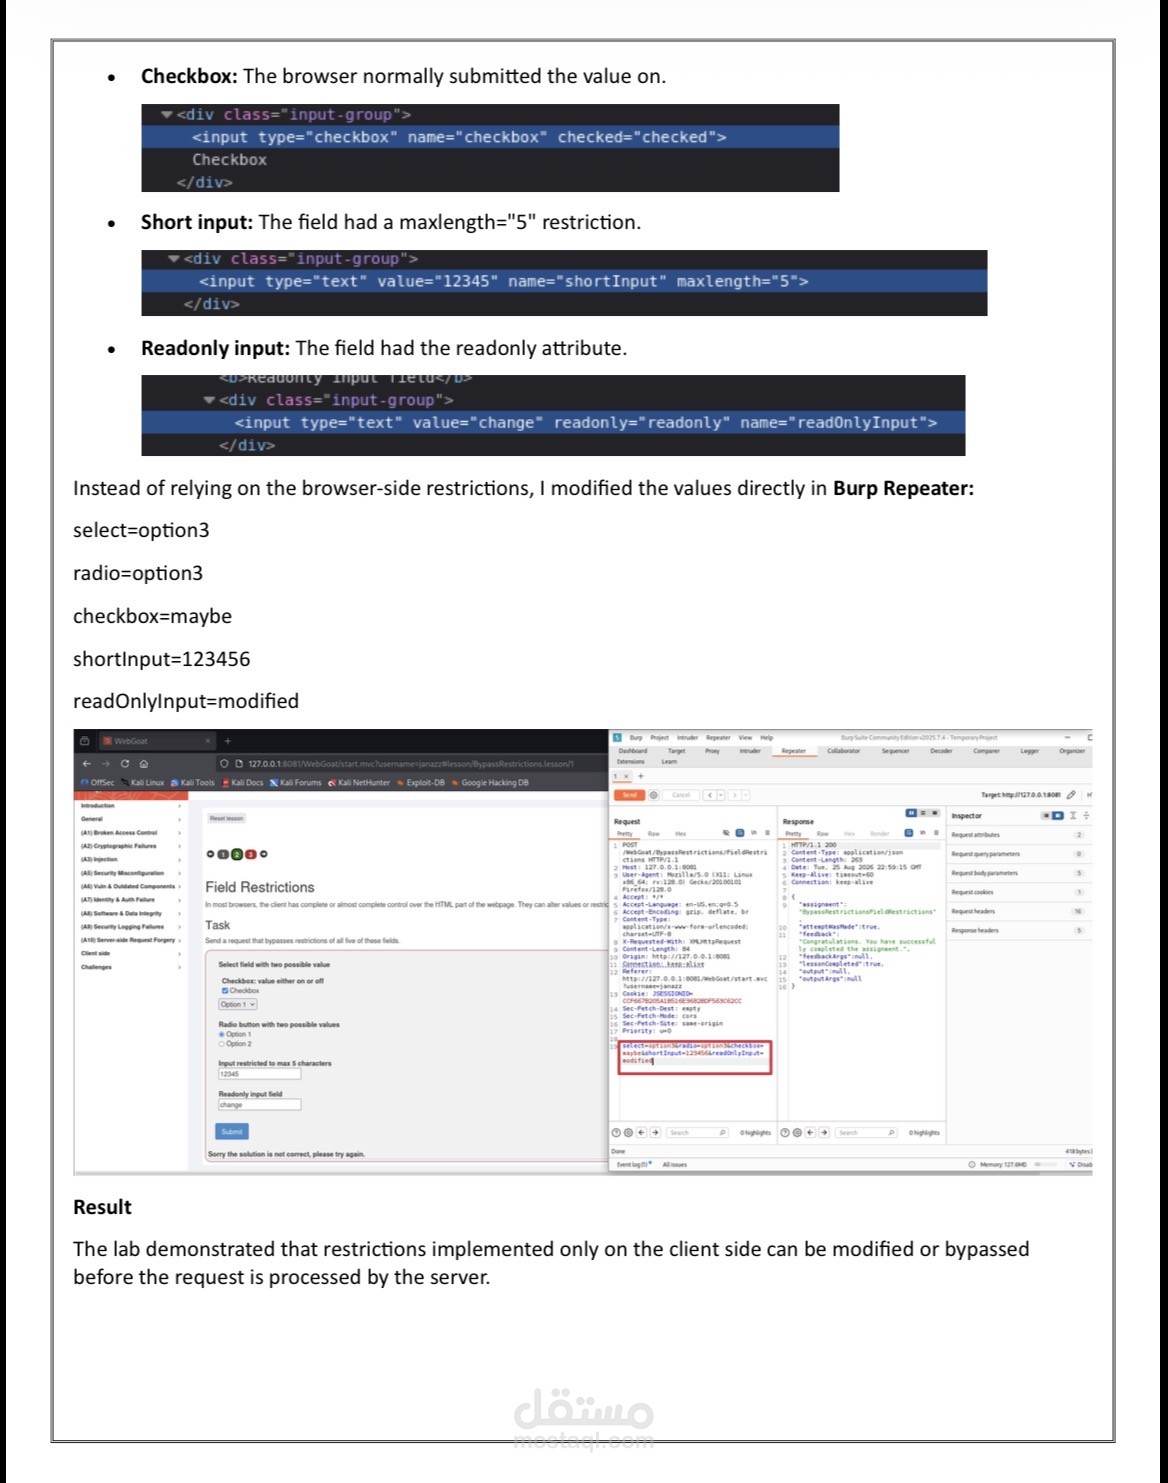
4. Modified the request/input to bypass the restriction.
5. Submitted the modified value to the server.
6. The application accepted the modified input and the lab was successfully completed.
Vulnerability
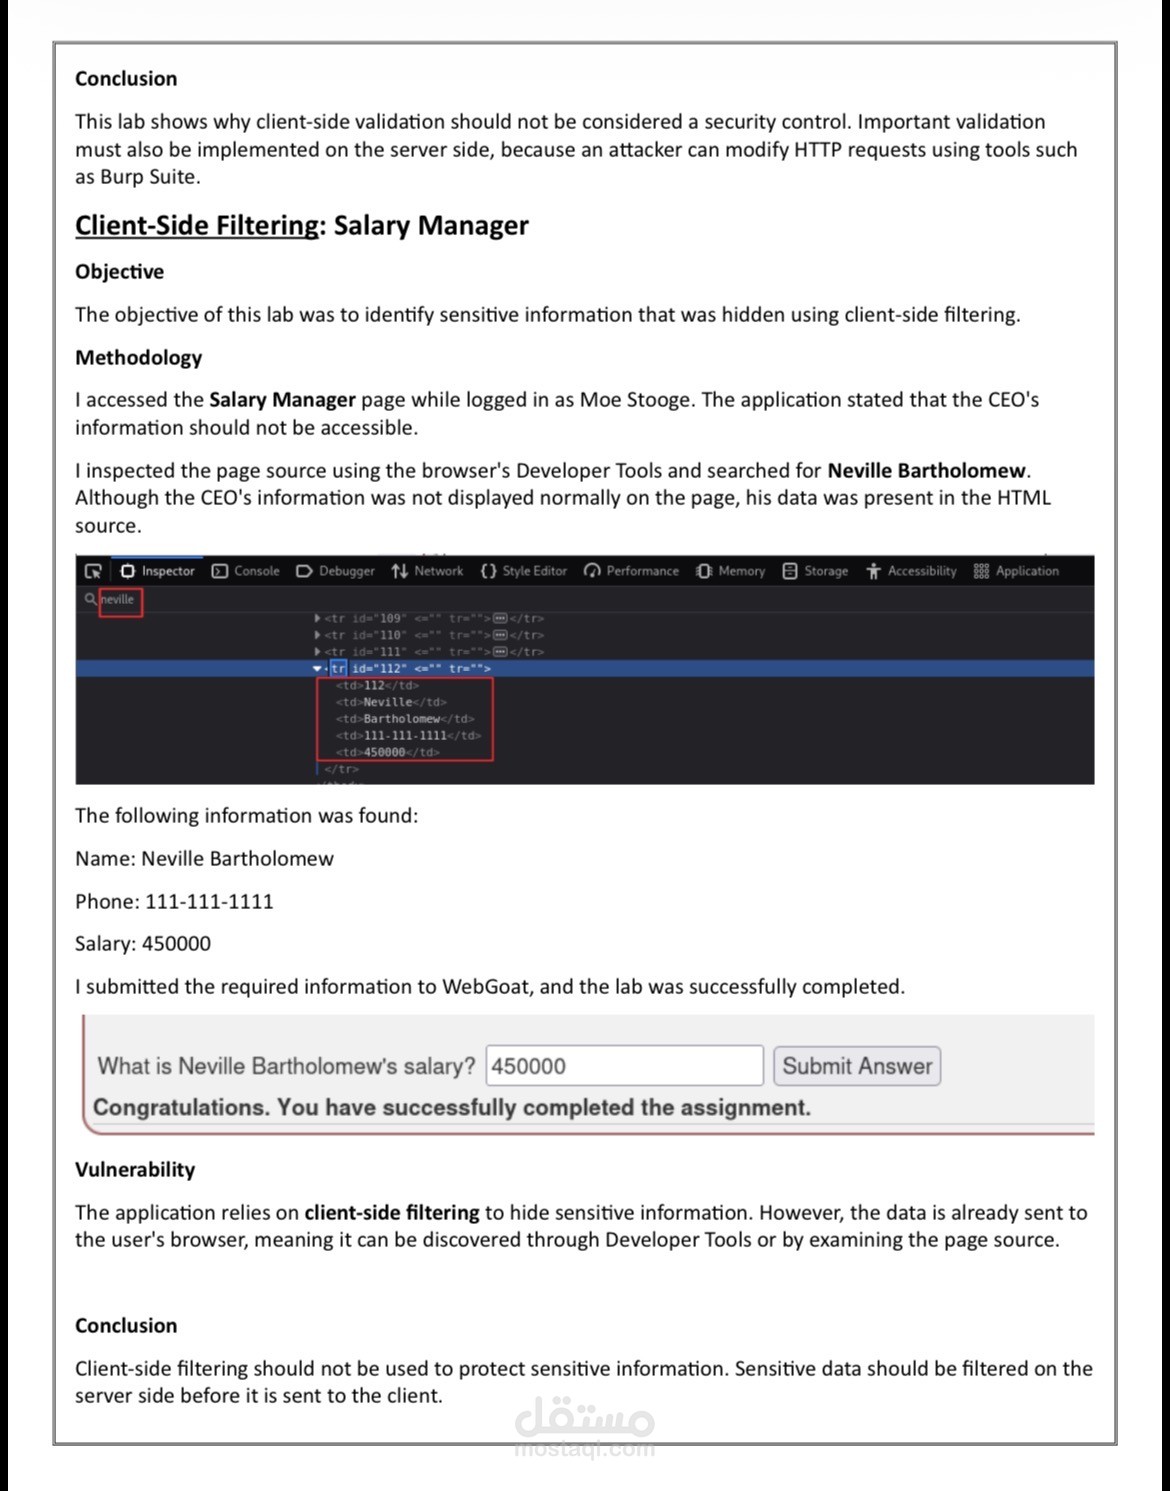
The application relied on client-side validation to restrict the user’s input. Since client-side code runs in the user’s browser, it can be modified or bypassed.
Impact
An attacker can manipulate the client-side restrictions and send values that the application intended to prevent.
Mitigation
* Do not rely on client-side validation for security.
* Validate and sanitize all user input on the server side.
* Apply authorization and business rules on the server.
* Treat all data received from the client as untrusted.