Building a Segmented Enterprise Network with FortiGate
تفاصيل العمل
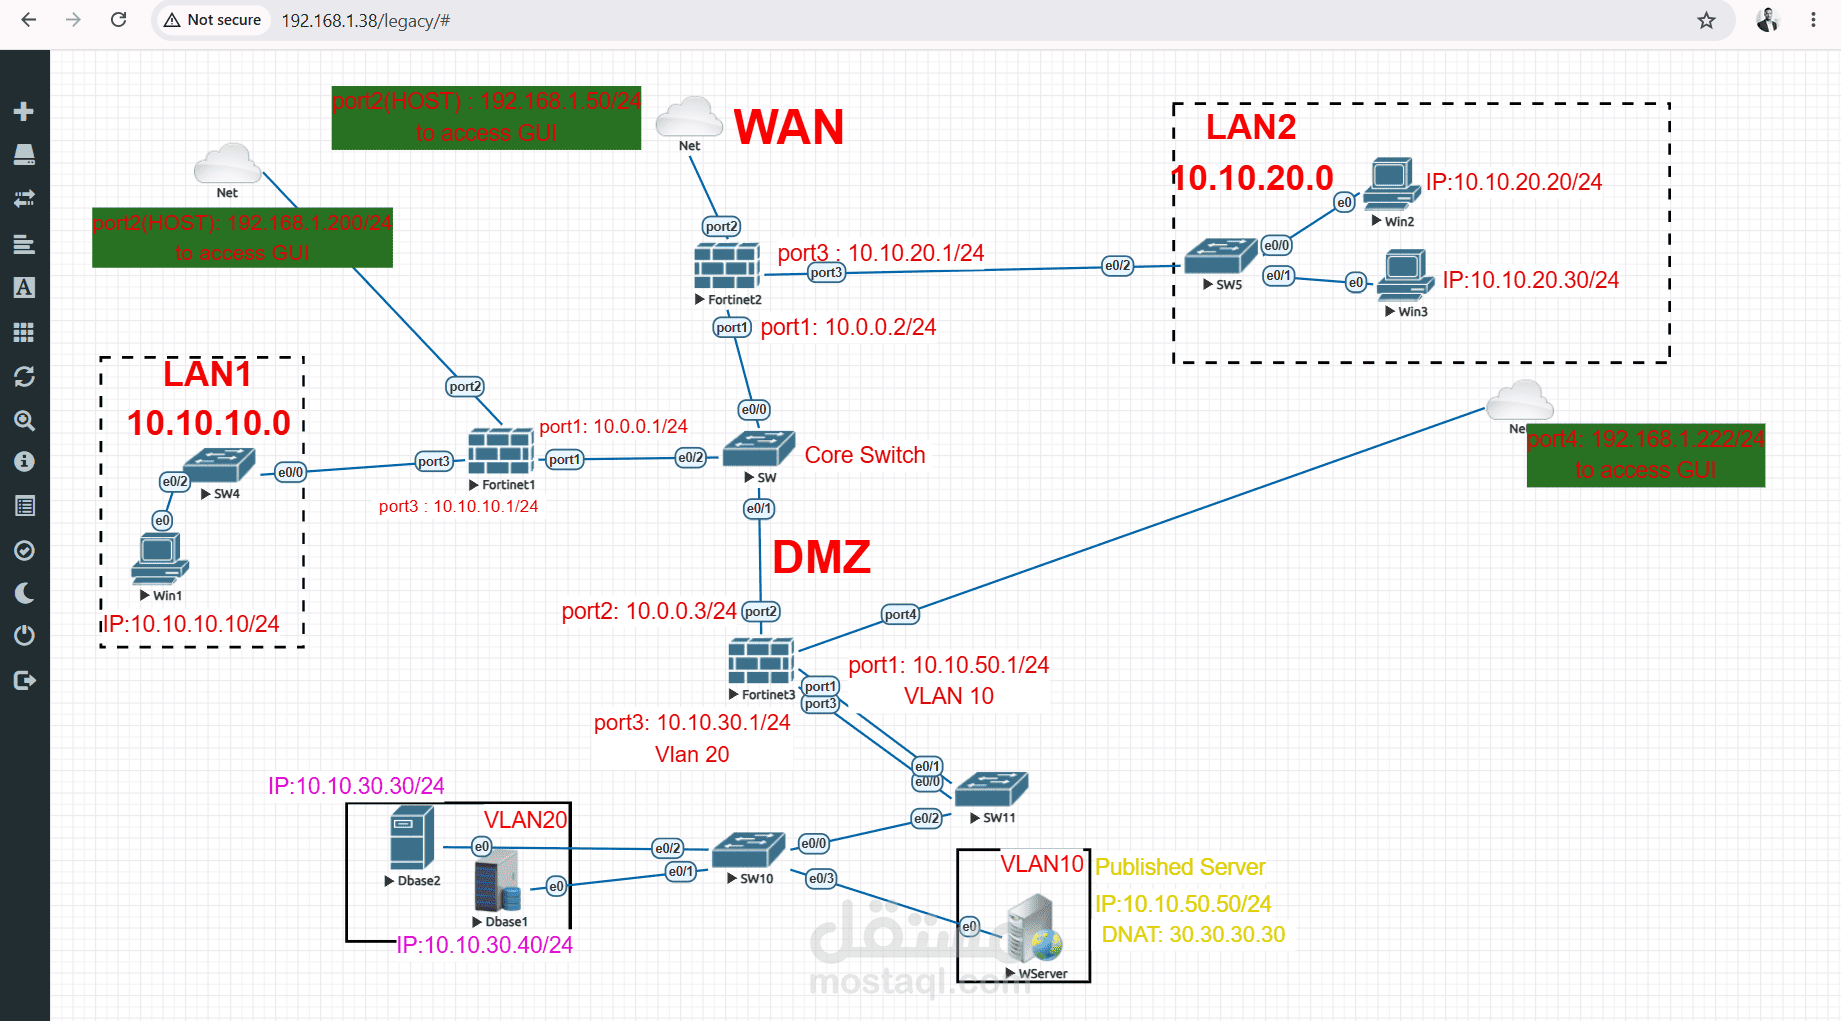
Building a Segmented Enterprise Network with FortiGate Firewalls
A hands-on cybersecurity lab project — designed, deployed & tested in EVE-NG
Project Details & Features
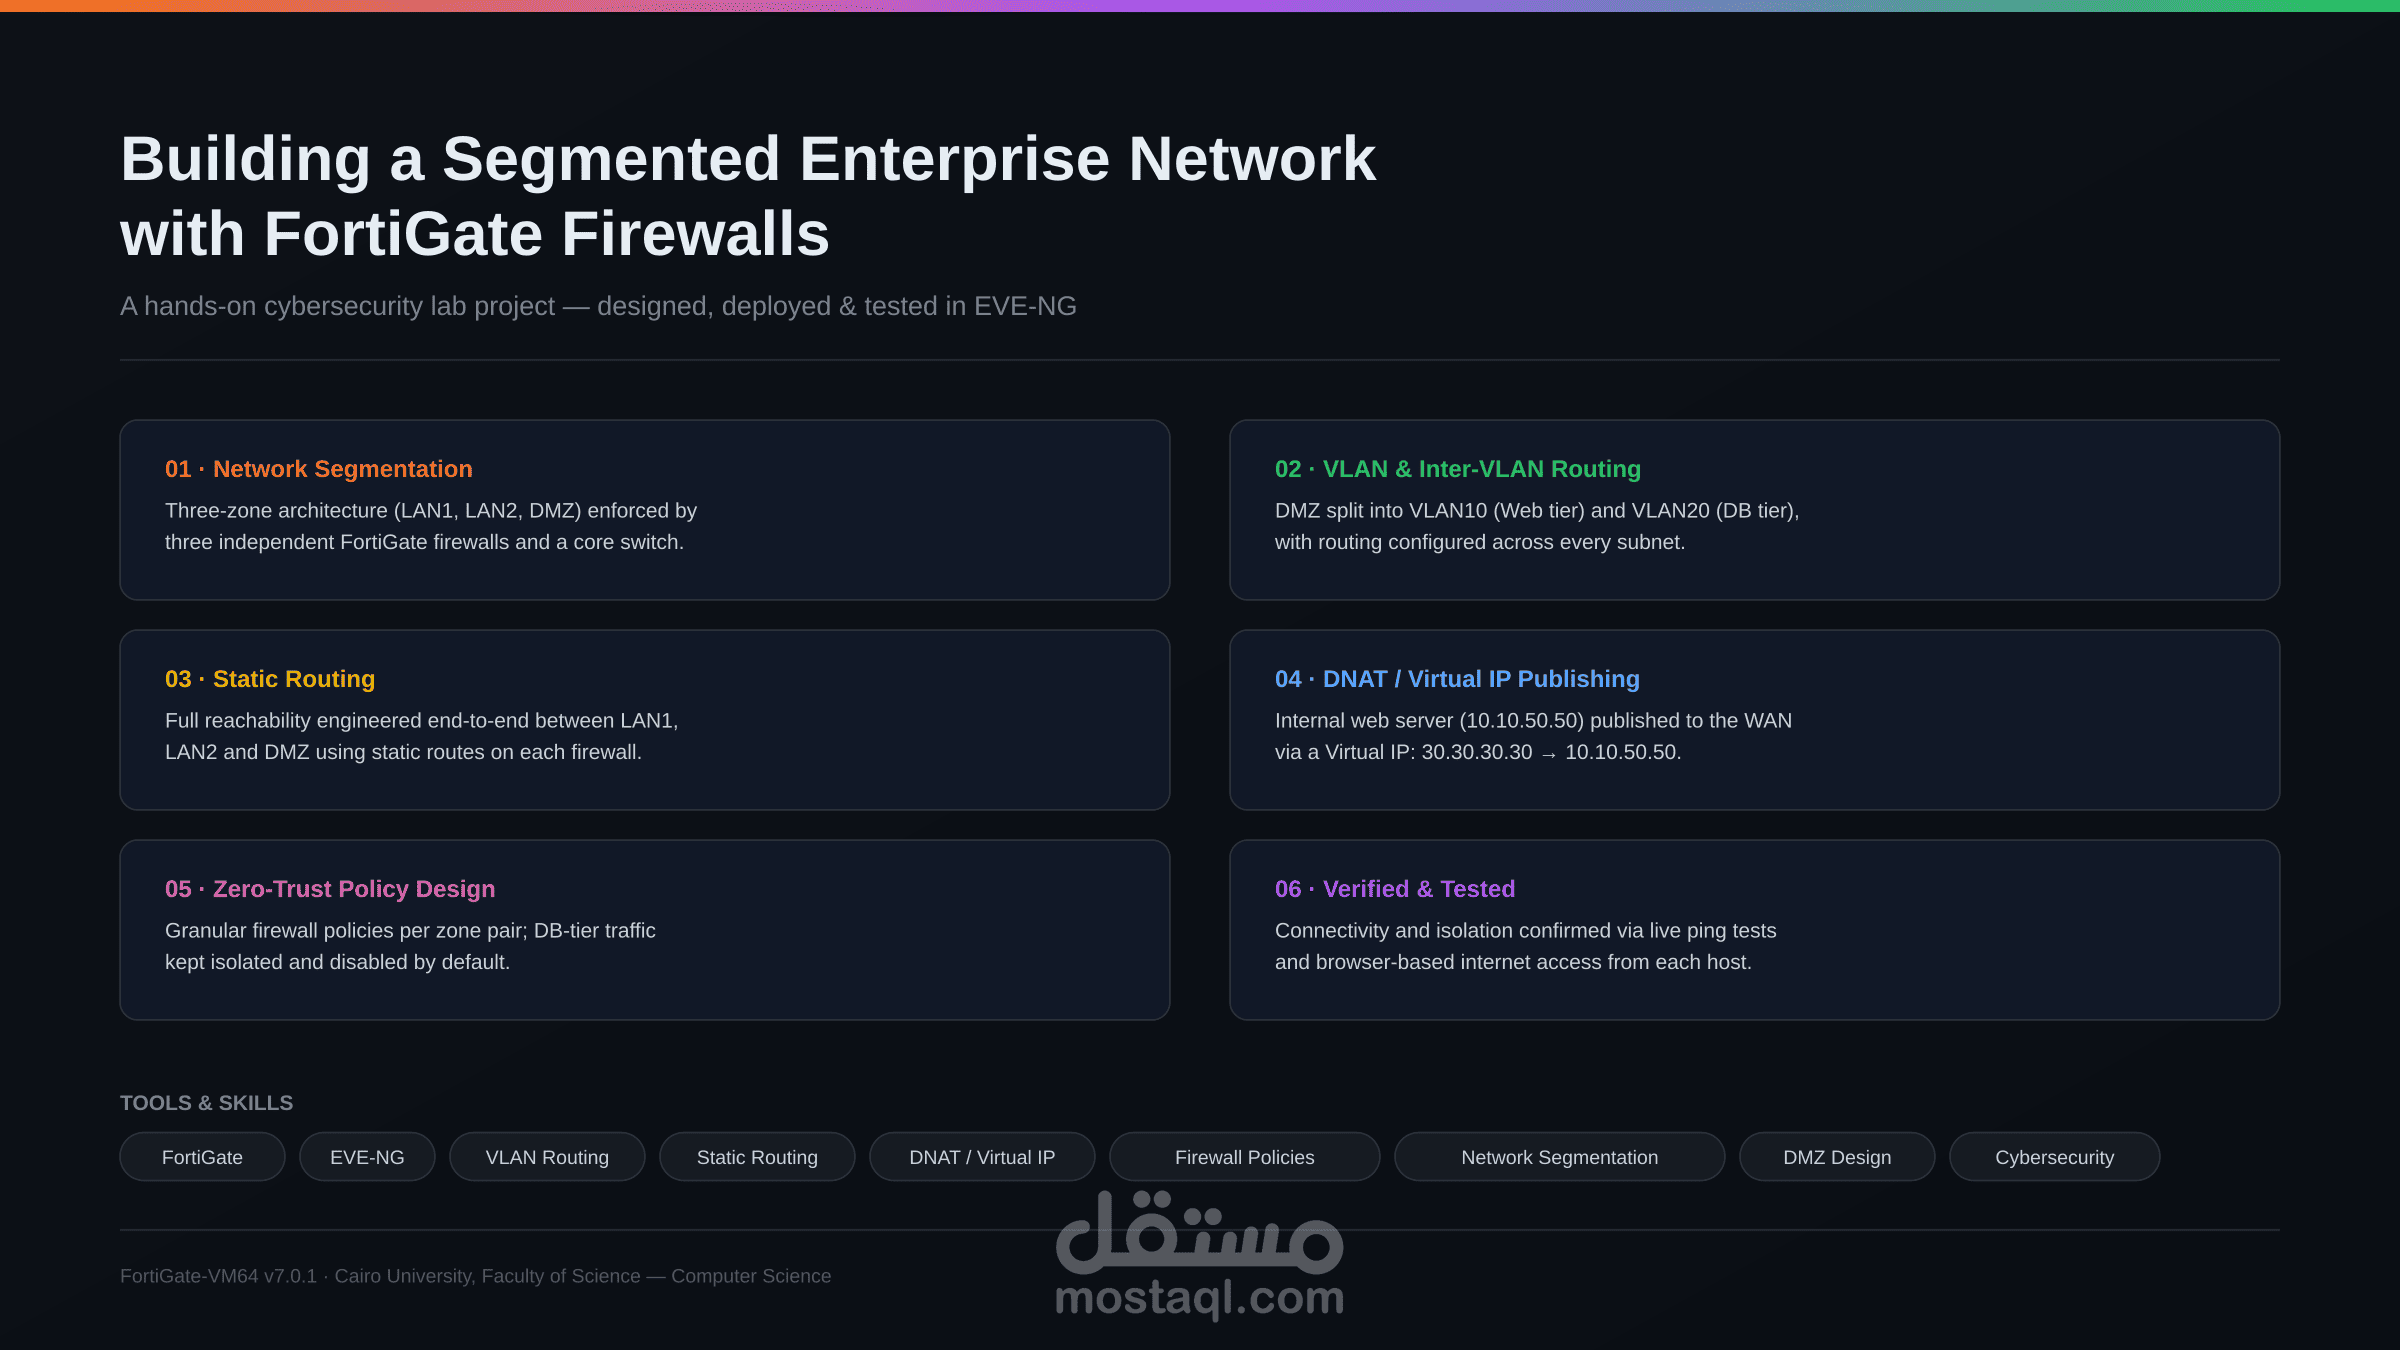
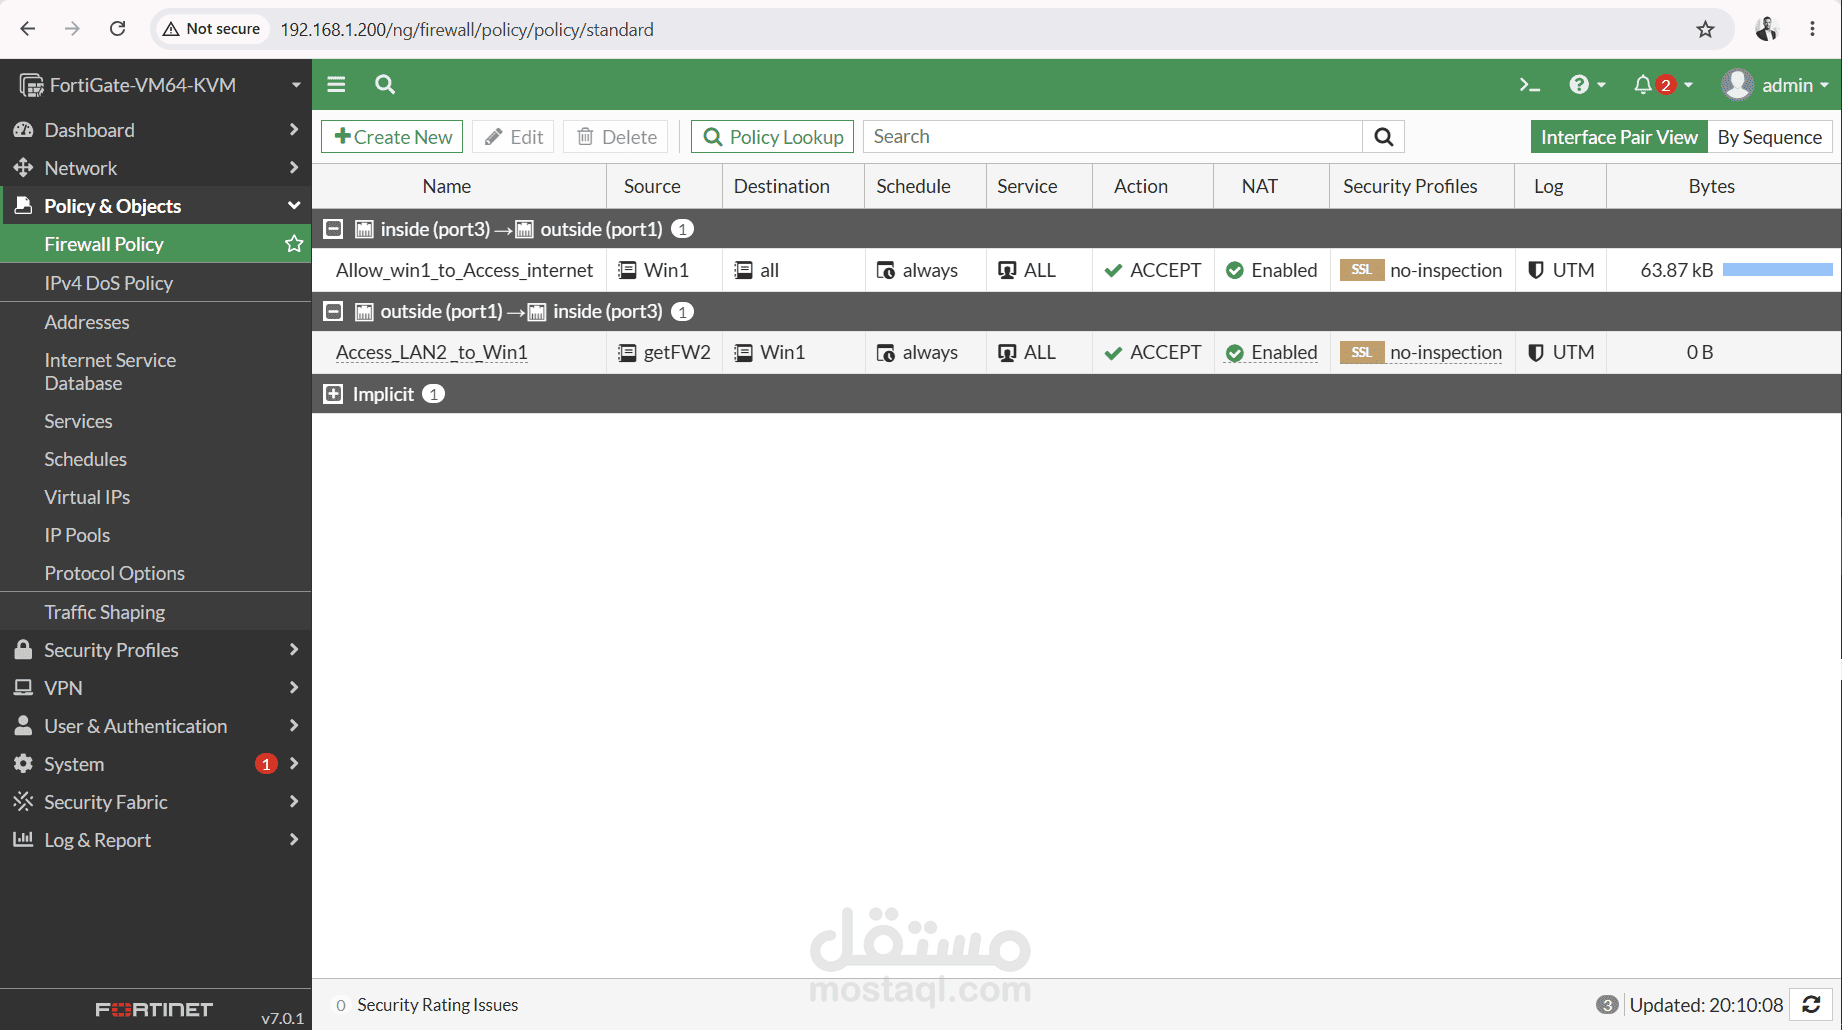
01 · Network Segmentation
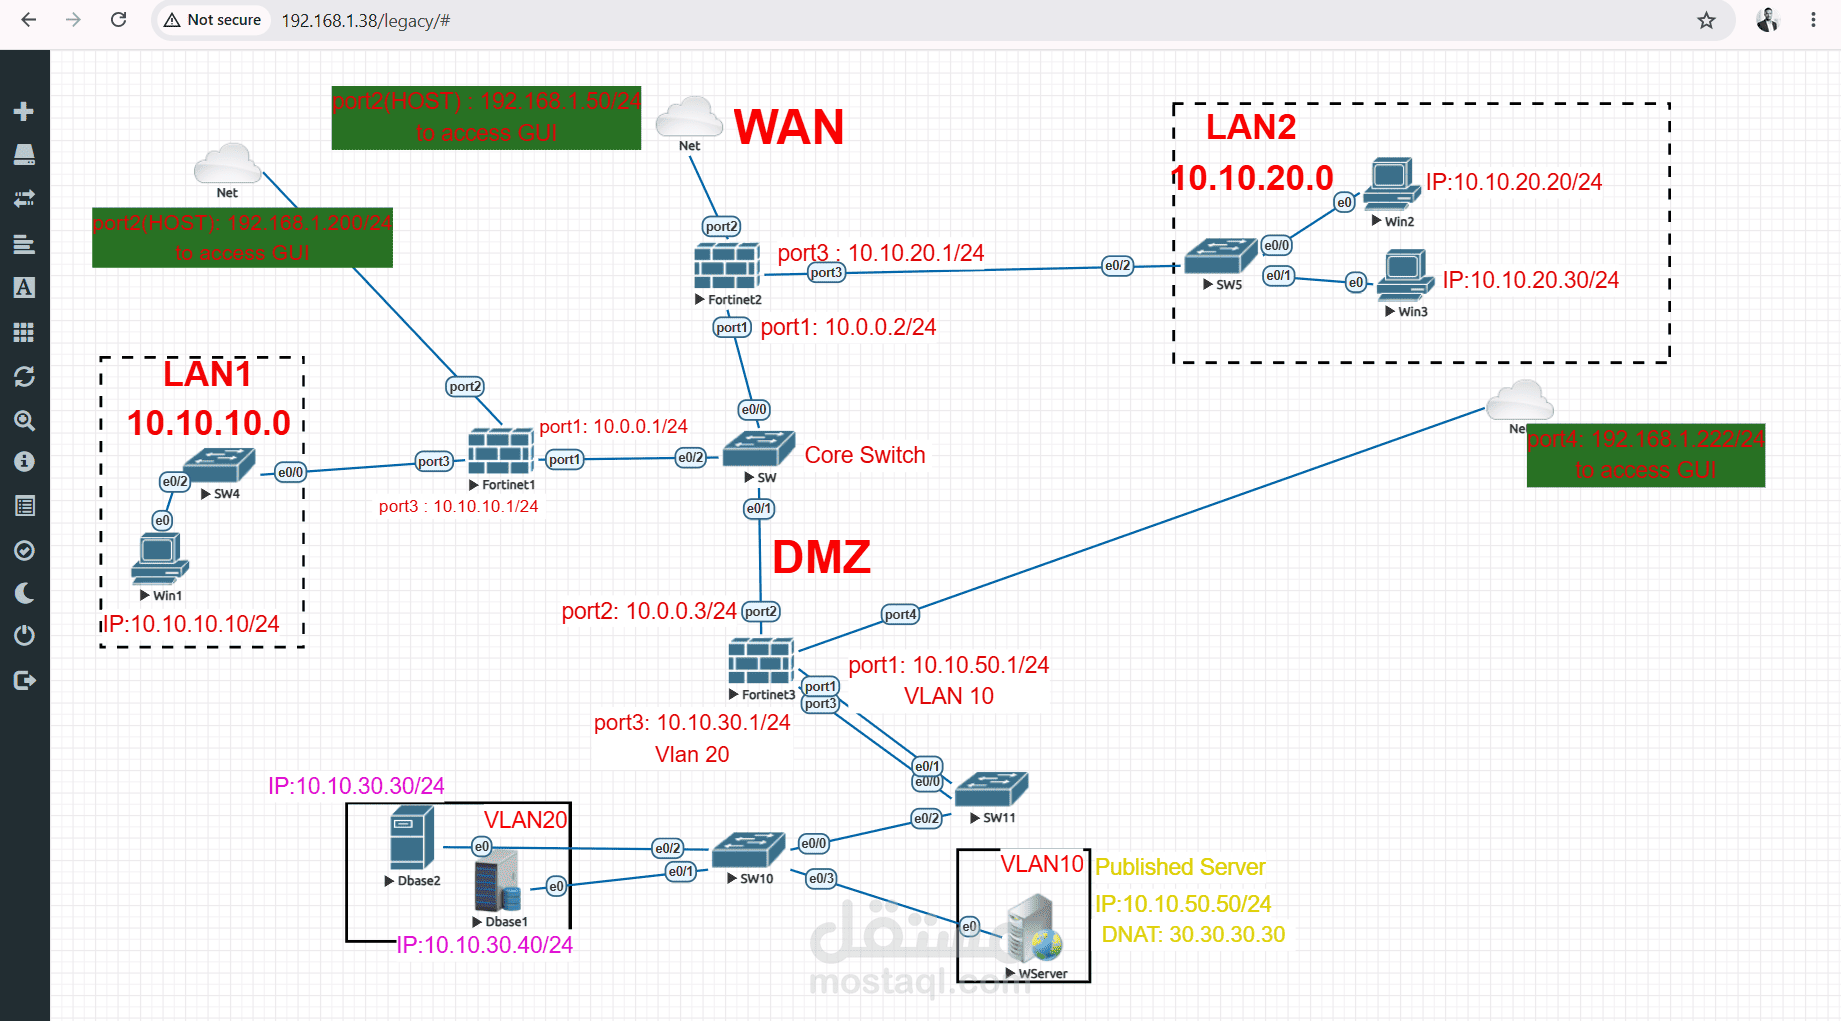
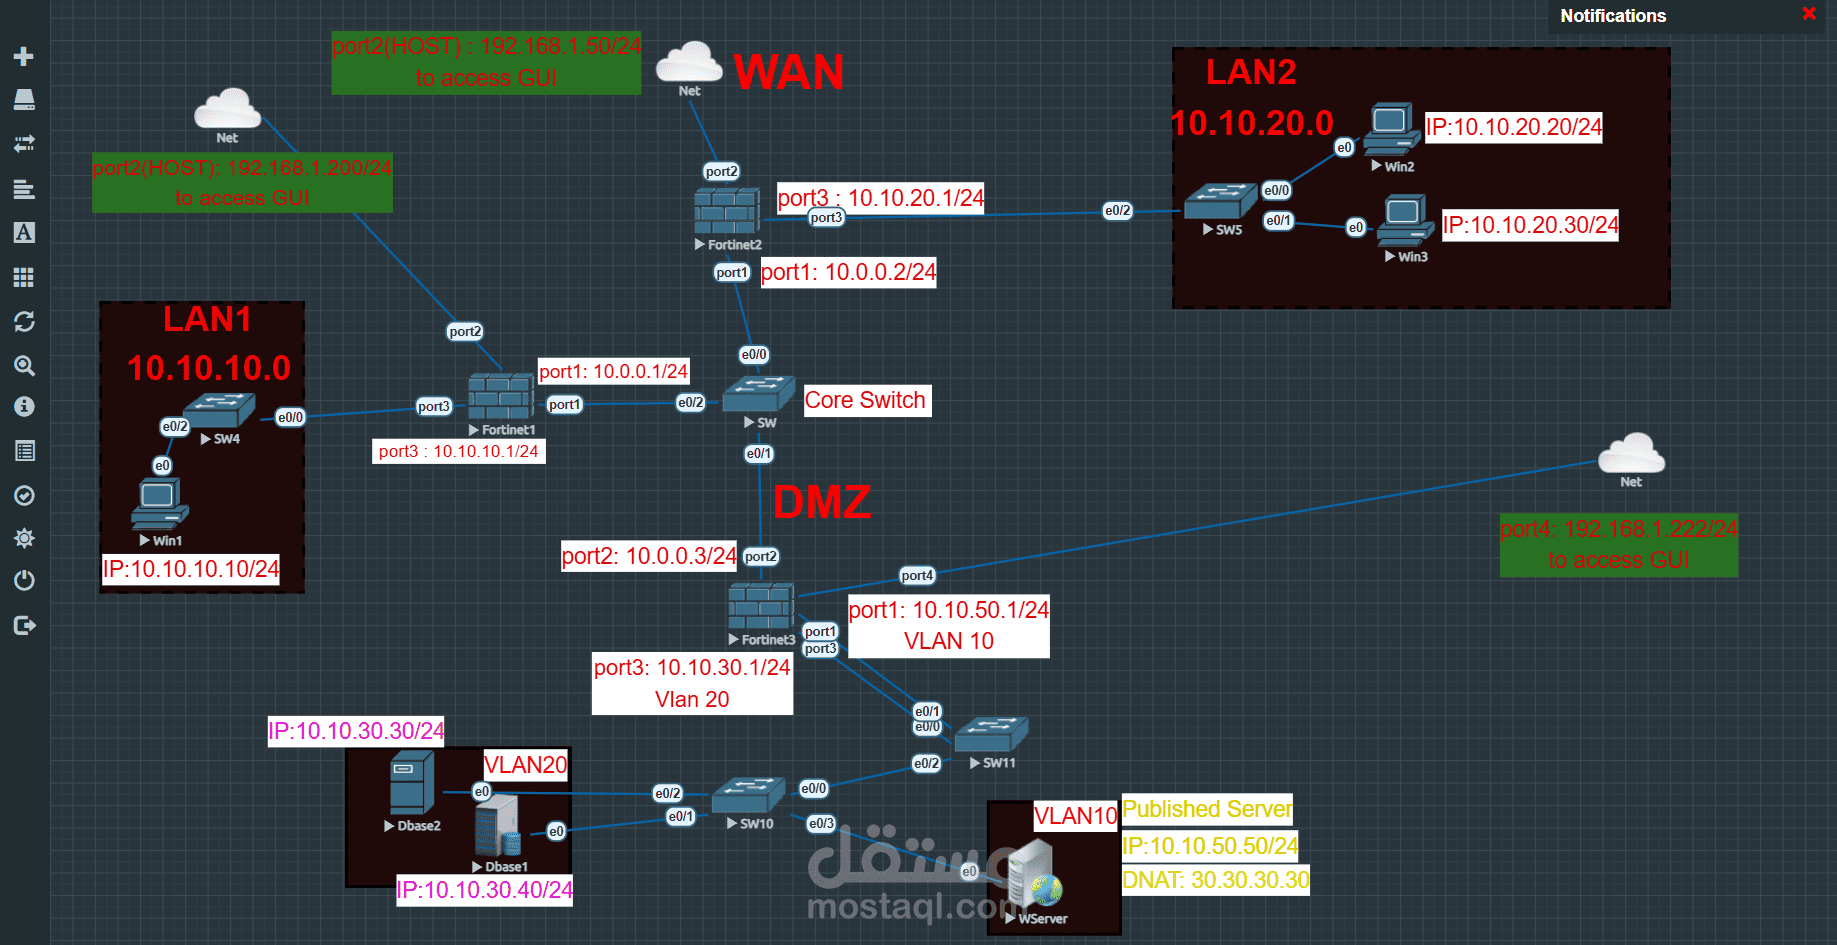
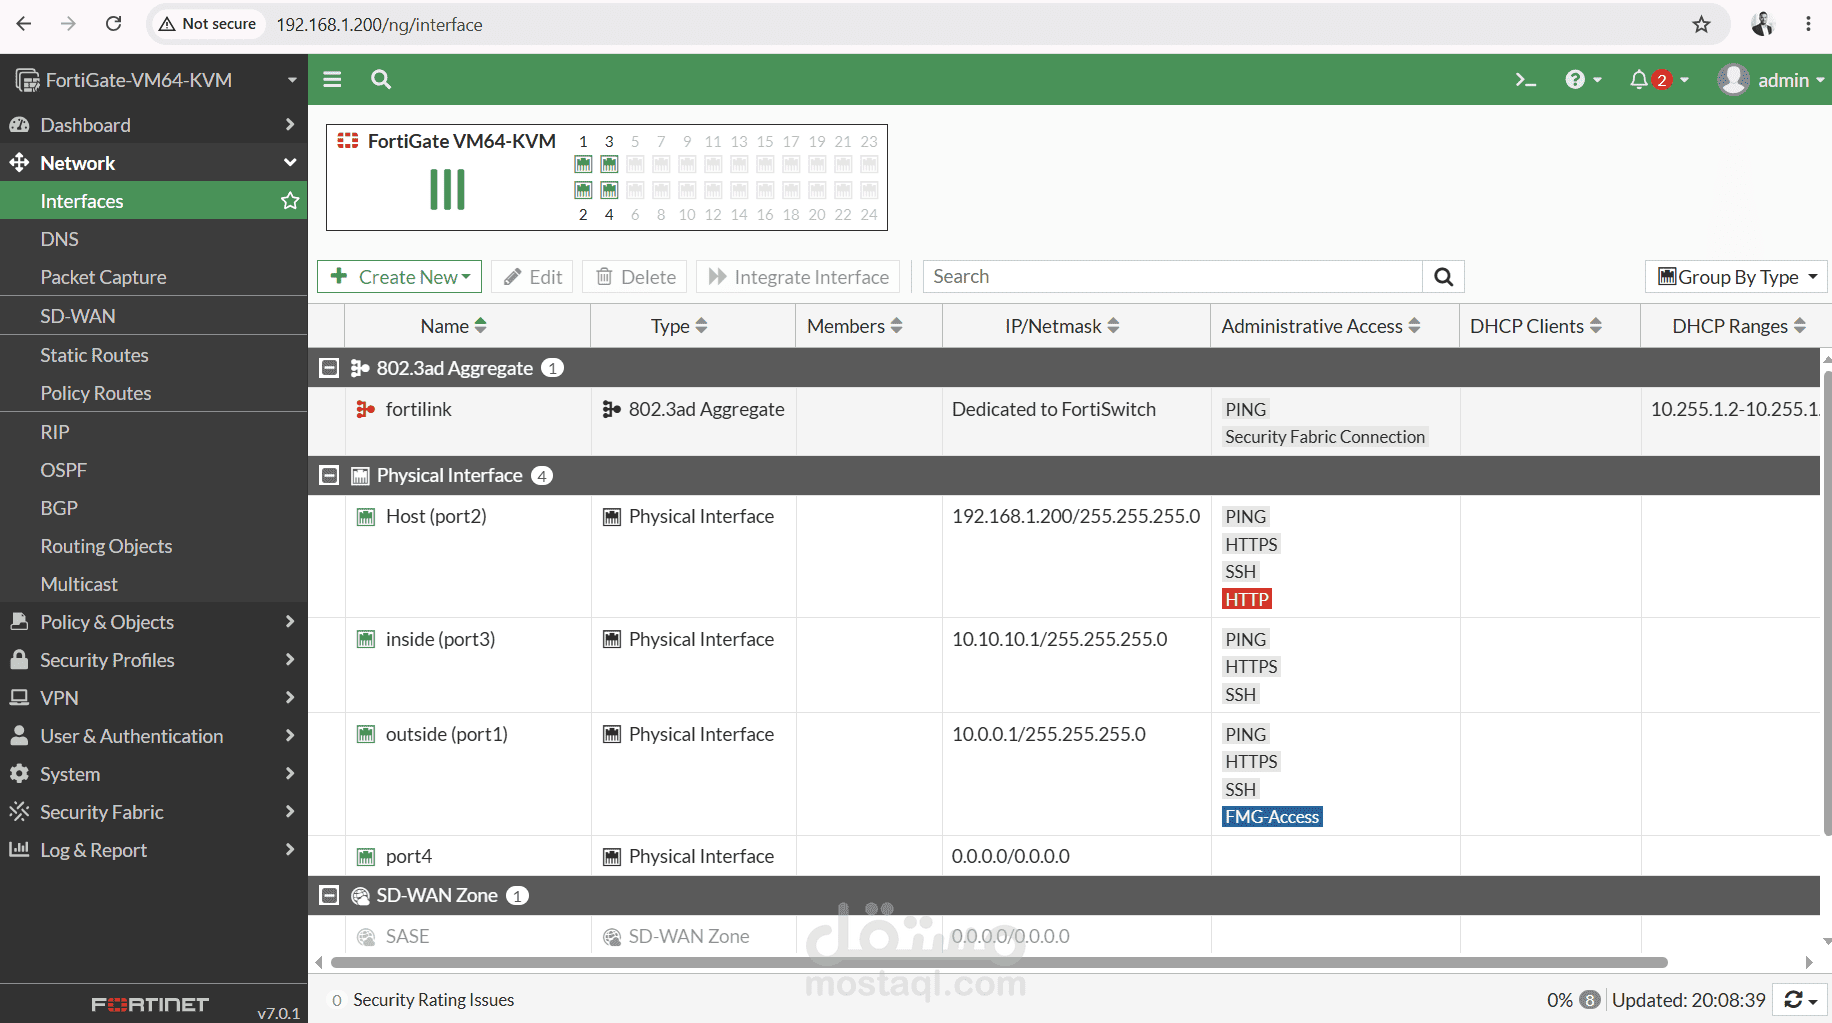
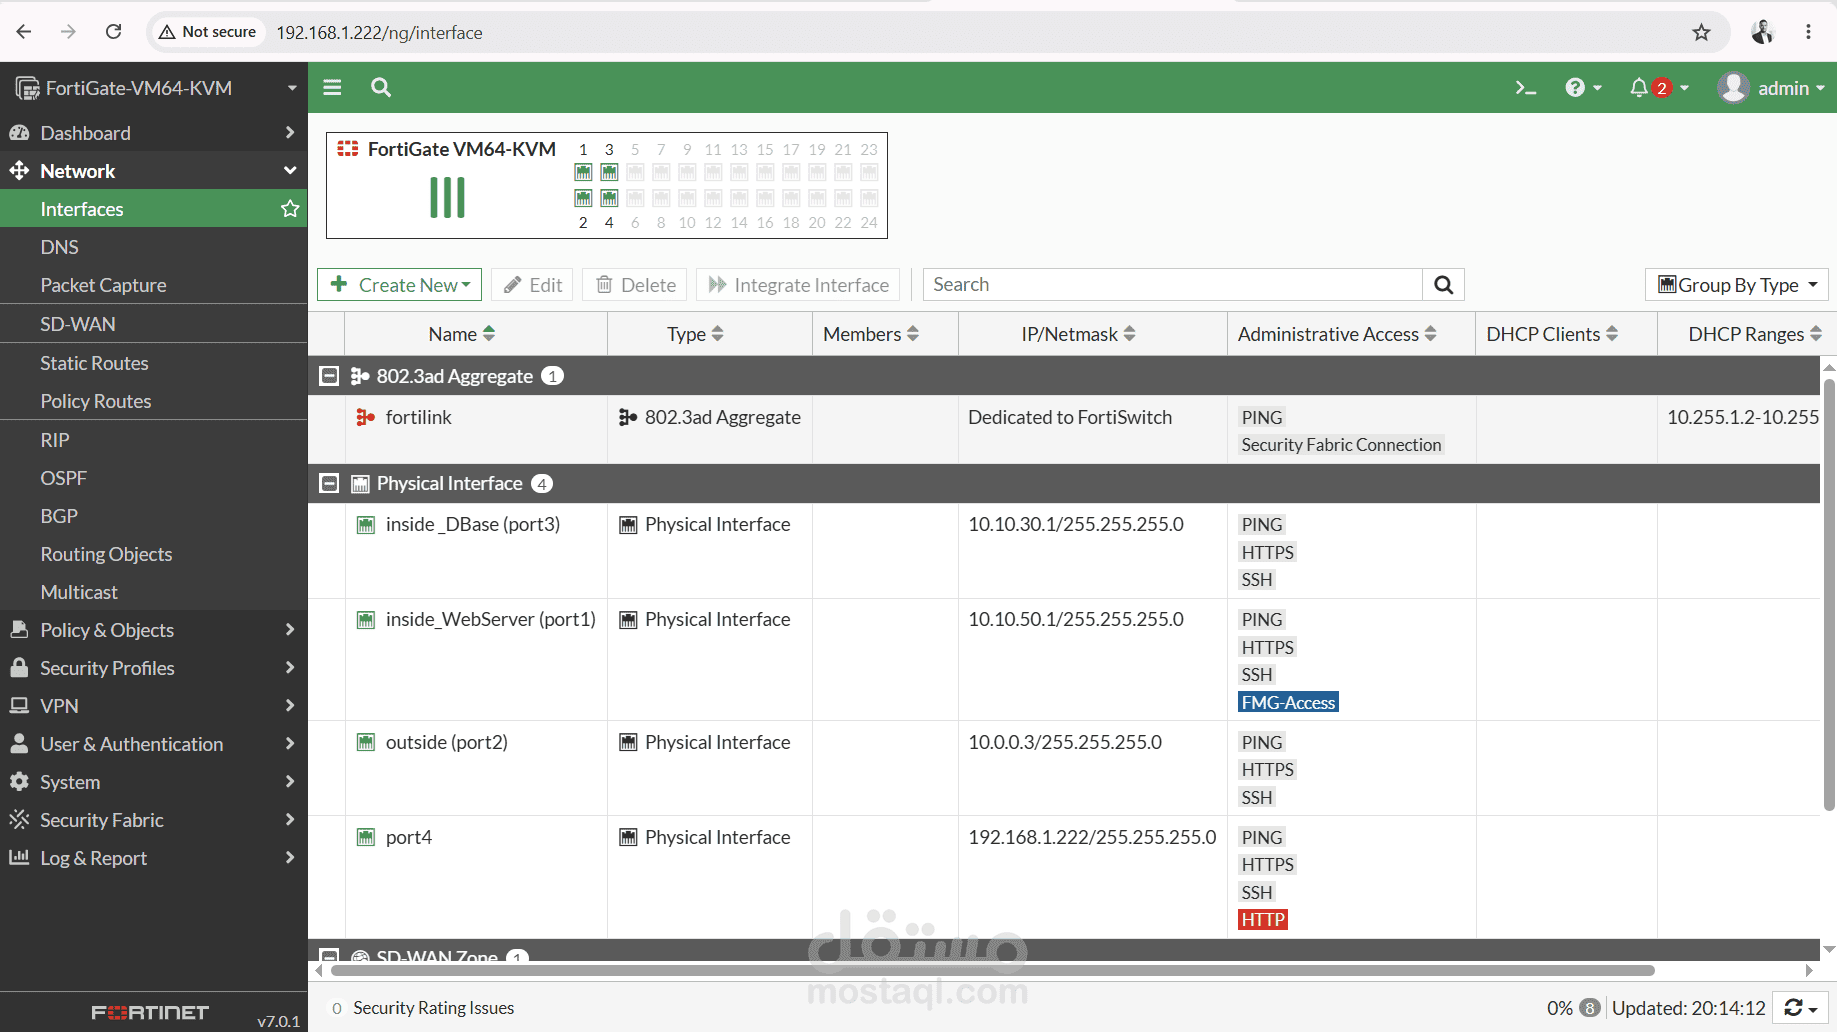
Three-zone architecture (LAN1, LAN2, DMZ) enforced by three independent FortiGate firewalls and a core switch.
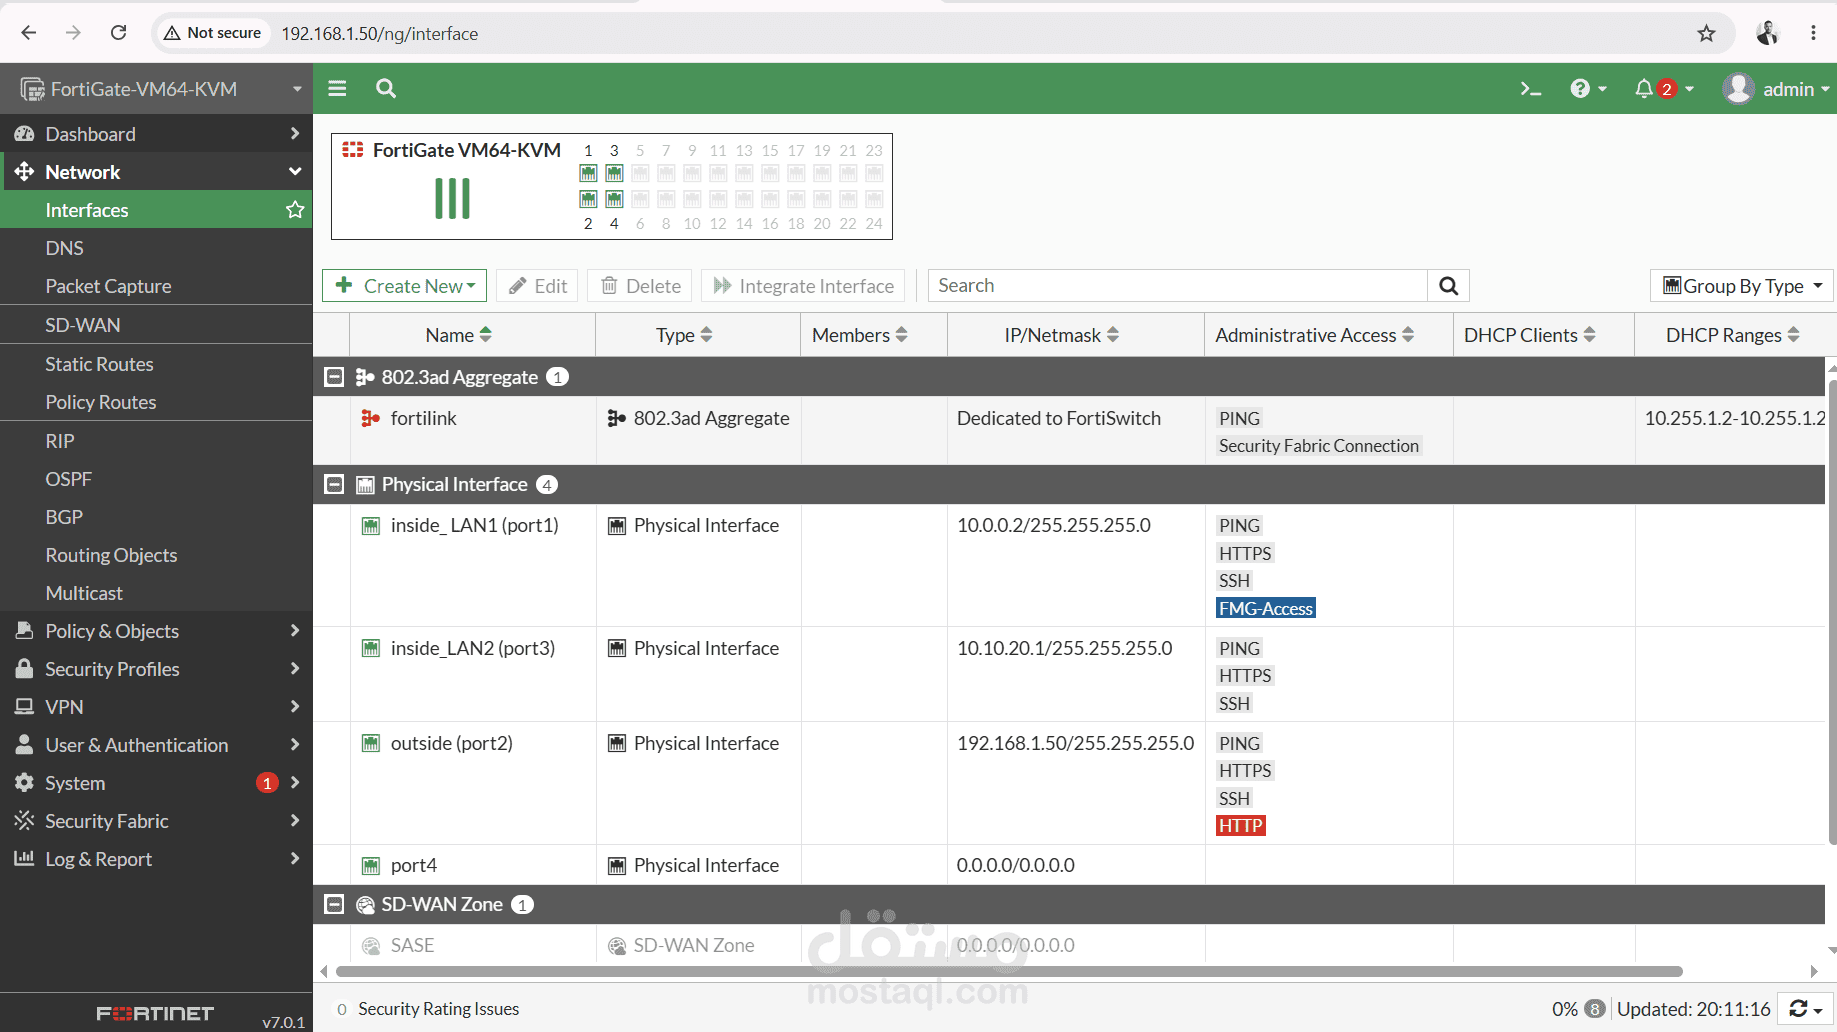
02 · VLAN & Inter-VLAN Routing
DMZ split into VLAN10 (Web tier) and VLAN20 (DB tier), with routing configured across every subnet.
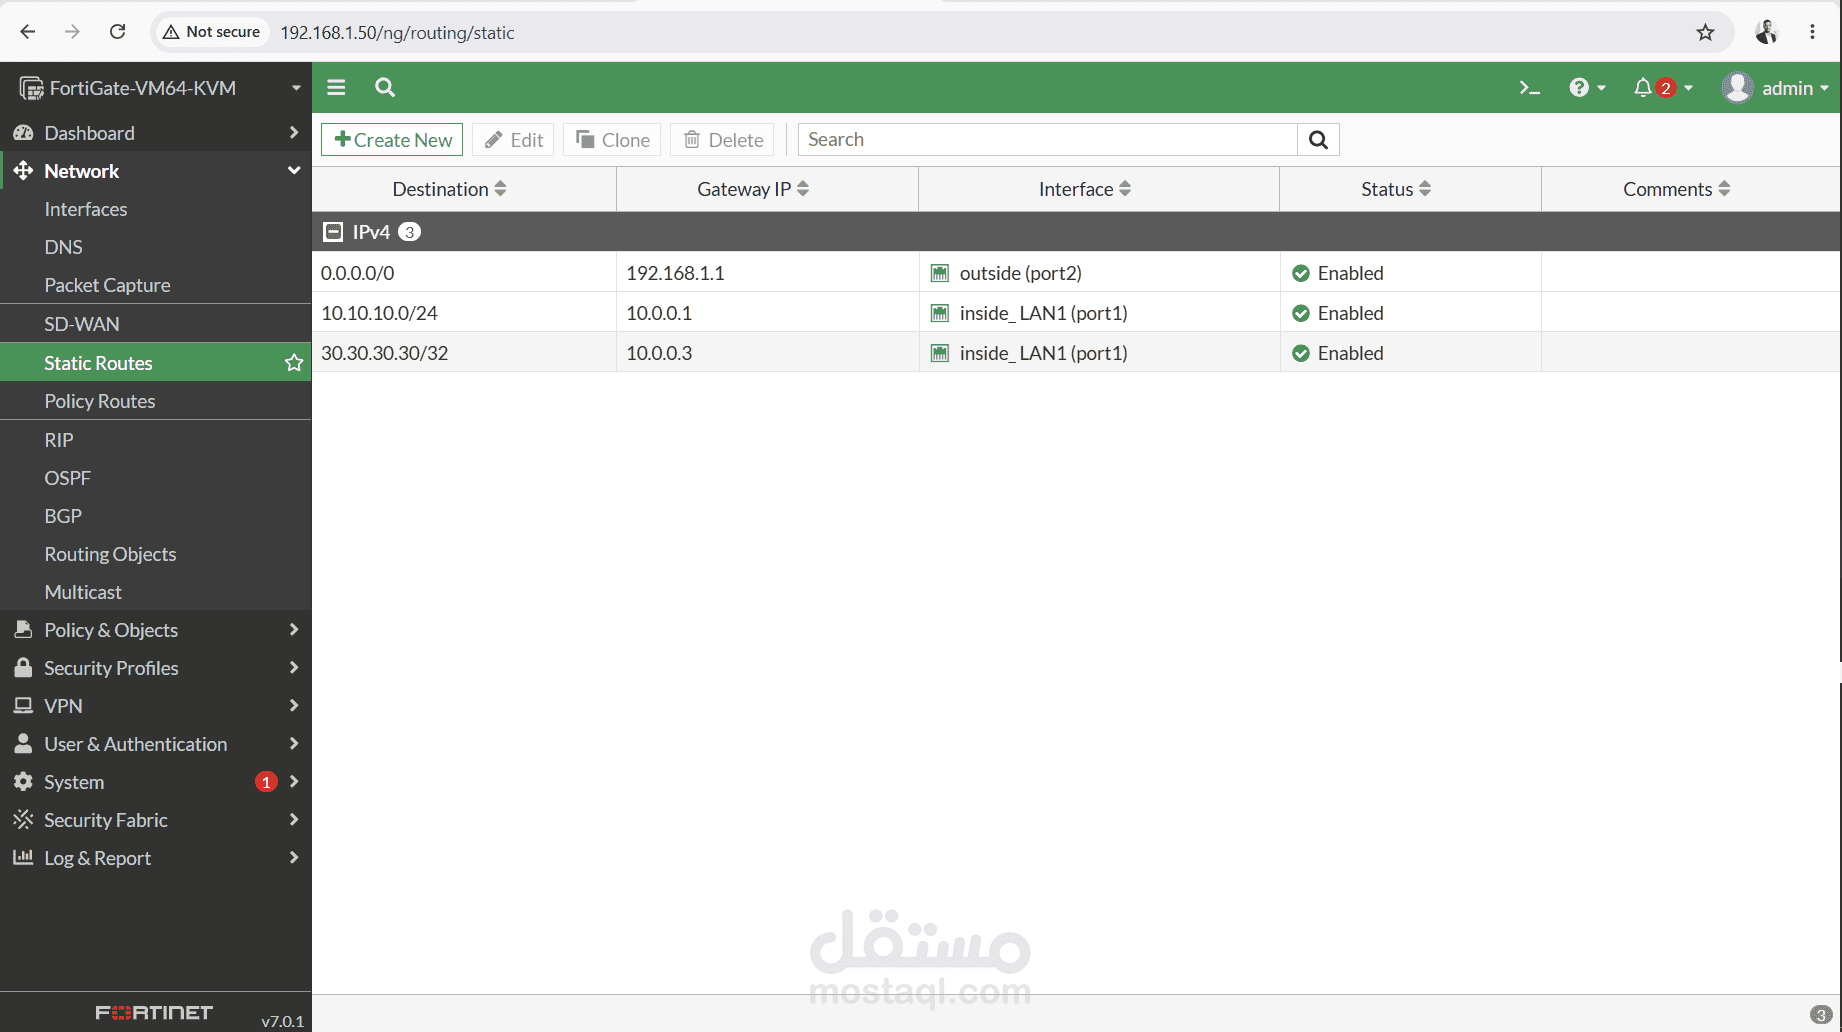
03 · Static Routing
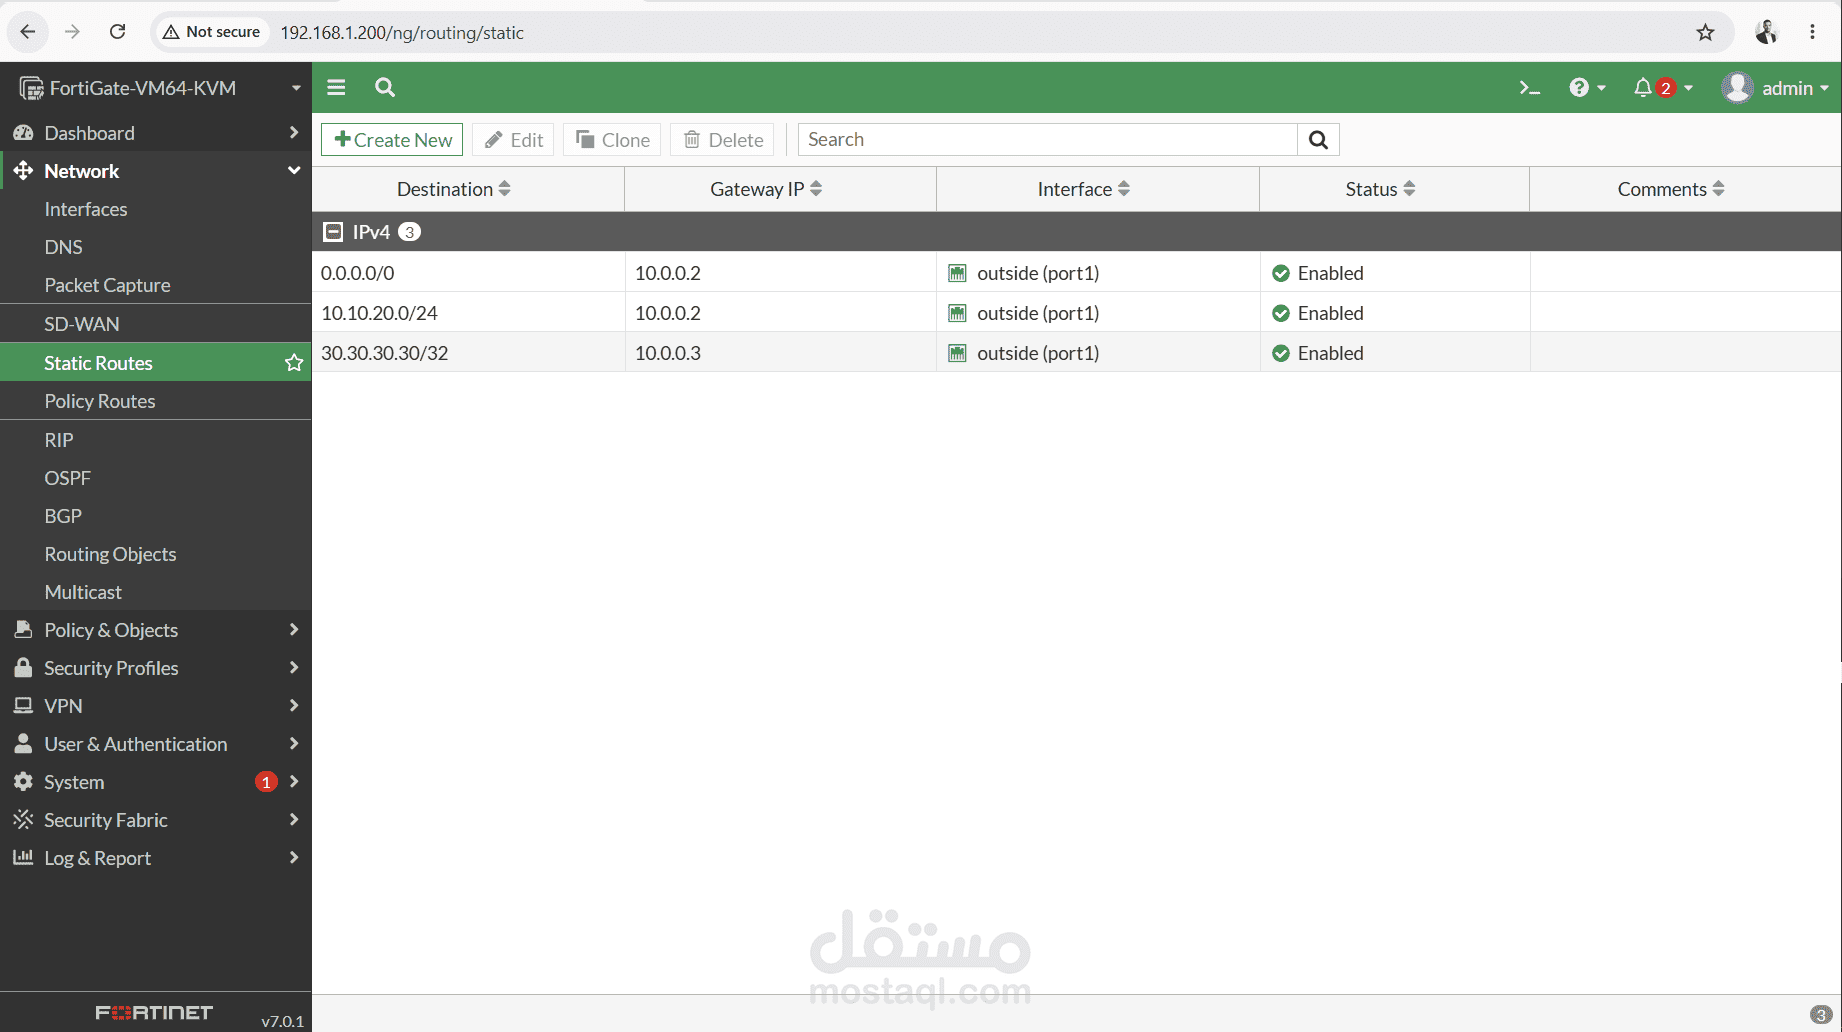
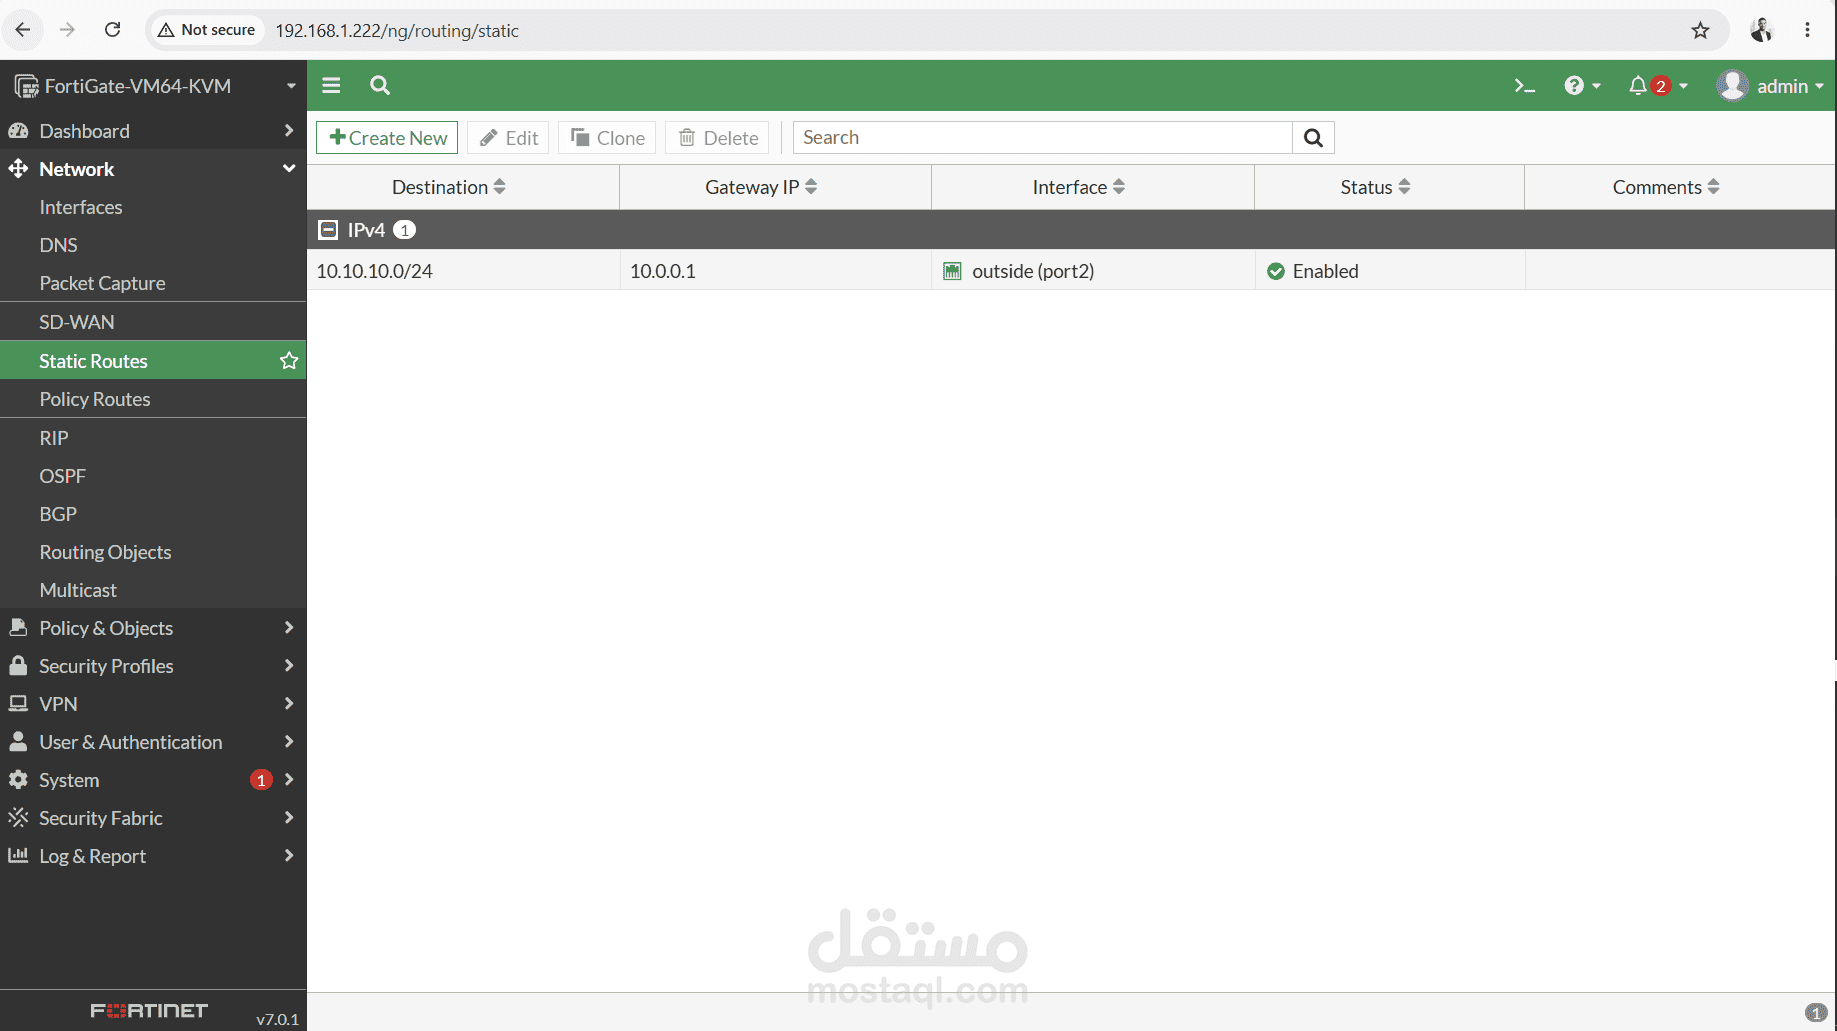
Full reachability engineered end-to-end between LAN1, LAN2 and DMZ using static routes on each firewall.
04 · DNAT / Virtual IP Publishing
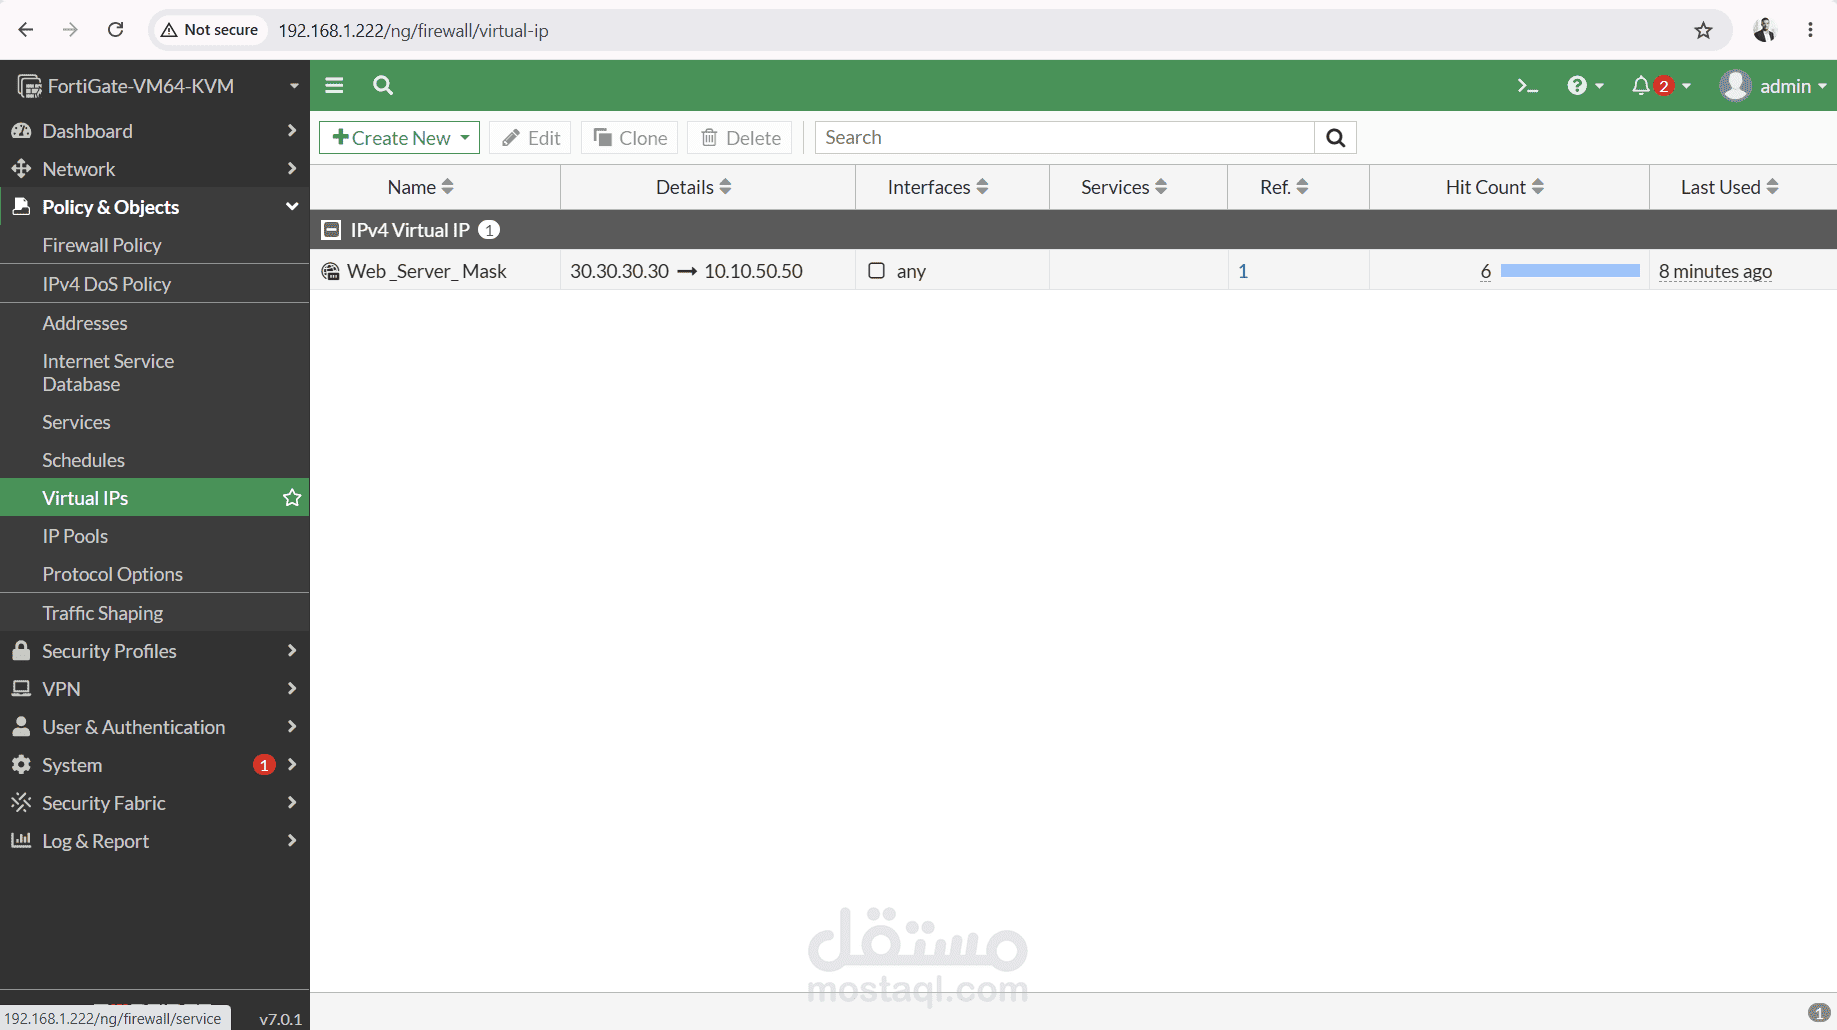
Internal web server (10.10.50.50) published to the WAN via a Virtual IP: 30.30.30.30 -> 10.10.50.50.
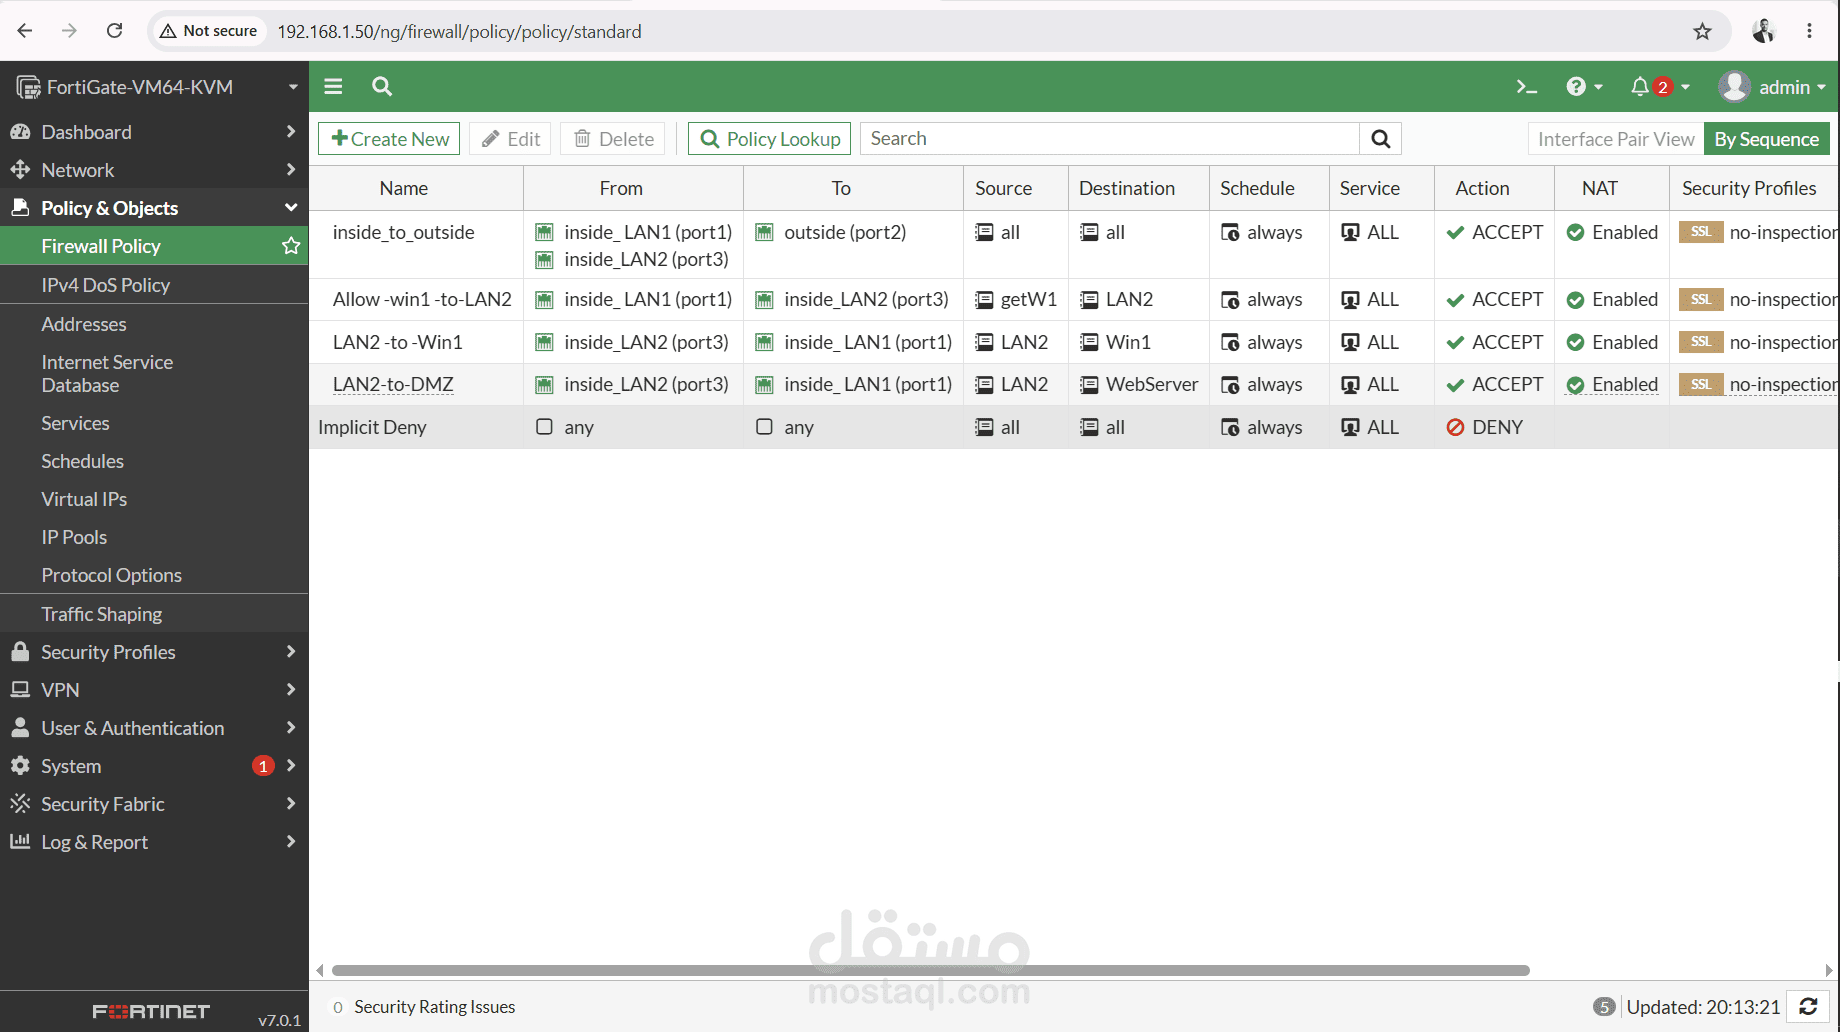
05 · Zero-Trust Policy Design
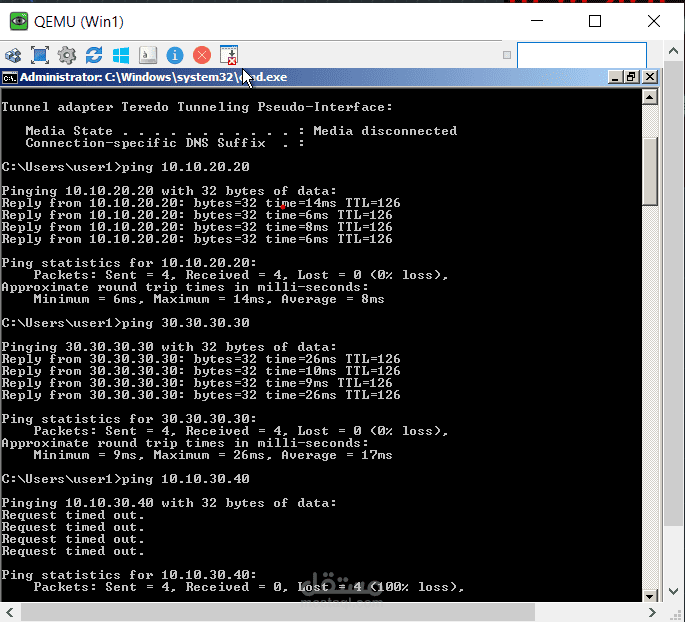
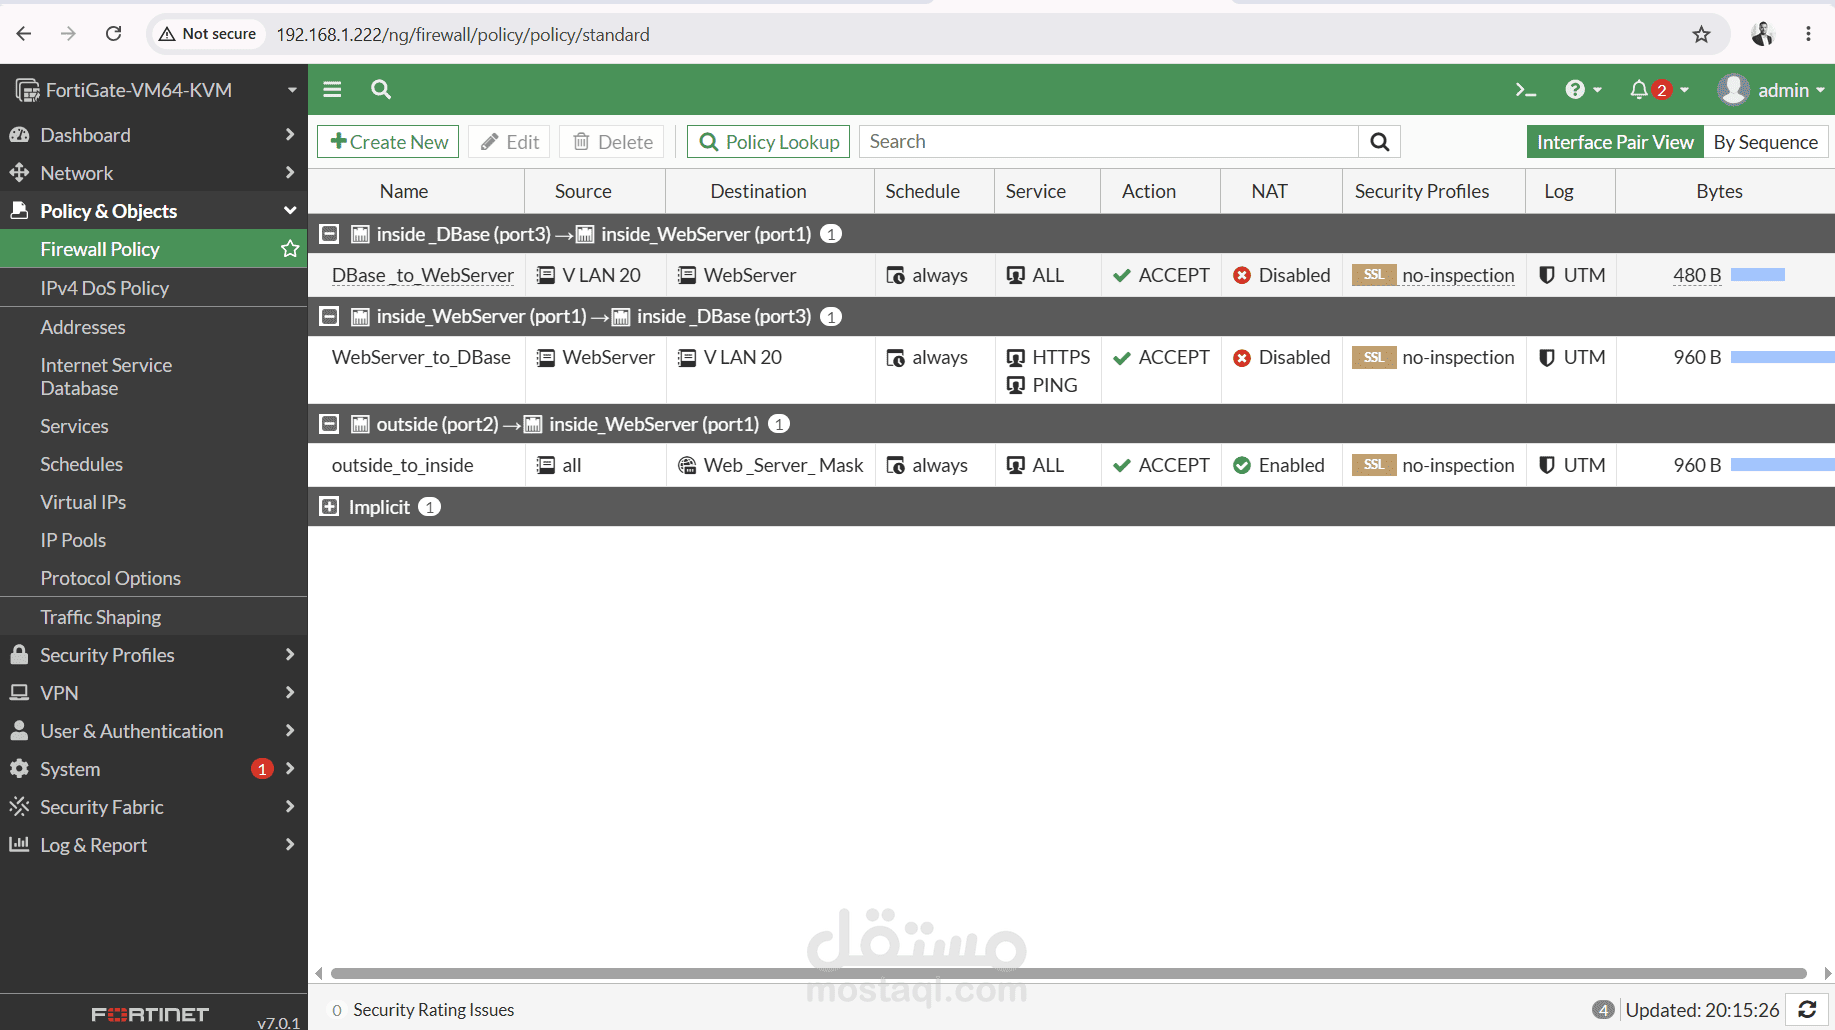
Granular firewall policies per zone pair; DB-tier traffic kept isolated and disabled by default.
06 · Verified & Tested
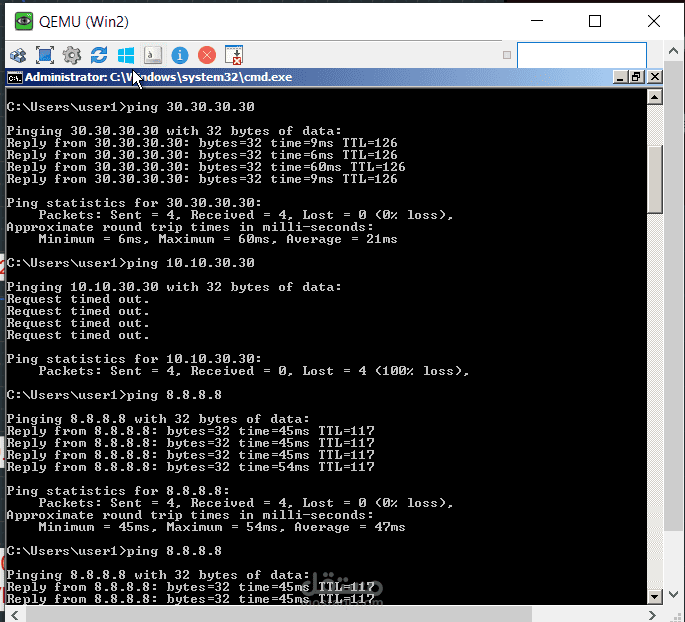
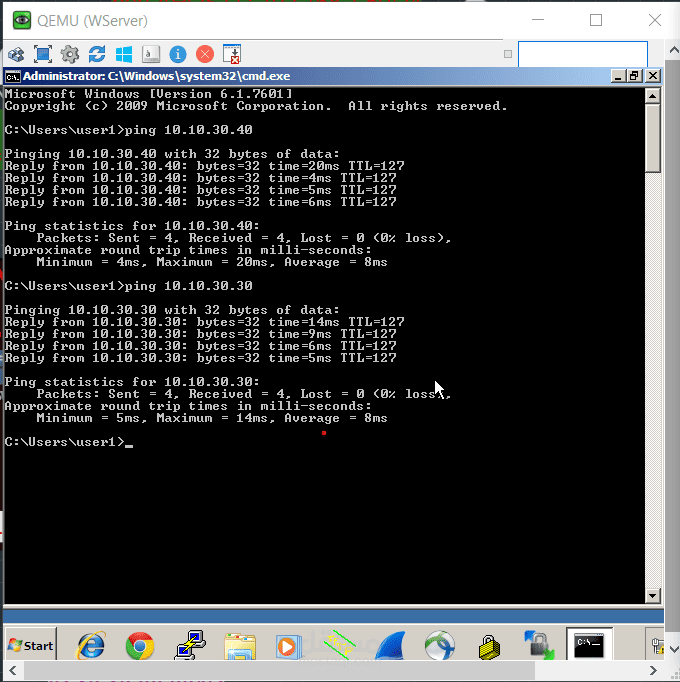
Connectivity and isolation confirmed via live ping tests and browser-based internet access from each host.