Security Monitoring and Threat Detection Using SIEM (SOC Lab Project)
تفاصيل العمل
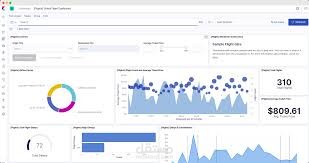
This project demonstrates my practical experience as a Junior SOC Analyst in monitoring, detecting, and analyzing security incidents within a simulated Security Operations Center (SOC) environment.
In this lab, I performed real-world security analysis tasks including log monitoring, alert triage, and incident investigation using SIEM-based techniques. The project focused on identifying potential threats such as phishing attempts, malware activity, and suspicious network behavior.
I analyzed system and network logs to detect anomalies, investigate alerts, and determine the severity and impact of security incidents. Additionally, I applied incident response procedures including initial investigation, evidence collection, and threat classification.
Technical skills applied in this project include:
* SIEM Monitoring and Alert Analysis
* Log Analysis and Threat Detection
* Incident Response (IR) Fundamentals
* Networking Concepts (CCNA Level)
* Basic Malware Analysis
* Windows and Linux Security Analysis
This project reflects my hands-on training in cybersecurity operations and my ability to support Level 1 SOC tasks such as continuous monitoring, alert investigation, and escalation support.